
CVE-2026-34990-poc
Proof-of-concept exploit for CVE-2026-34990, a CUPS 2.4.16 local privilege escalation via arbitrary file write through CUPS_CREATE_LOCAL_PRINTER and…

Proof-of-concept exploit for CVE-2026-34990, a CUPS 2.4.16 local privilege escalation via arbitrary file write through CUPS_CREATE_LOCAL_PRINTER and…

Mythic C2 agent targeting Linux and Windows hosts written in Rust

Proof-of-concept exploit for Firefox BrowsingContext authorization bypass (CVE-2026-4692), demonstrating forged IPC messages to set InRDMPane and…

OSCP-focused toolkit for read-only network, SMB, AD, DNS, web, and database enumeration; privesc scanning, hash identification, and…

GEF (GDB Enhanced Features) - a modern experience for GDB with advanced debugging capabilities for exploit devs & reverse engineers on Linux

The User Registration & Membership WordPress plugin before 4.1.2 does not prevent users to set their account role when the Membership Addon is…

Toolkit to weaponize Chromium vulnerabilities into reliable, cross-platform, full-chain exploits

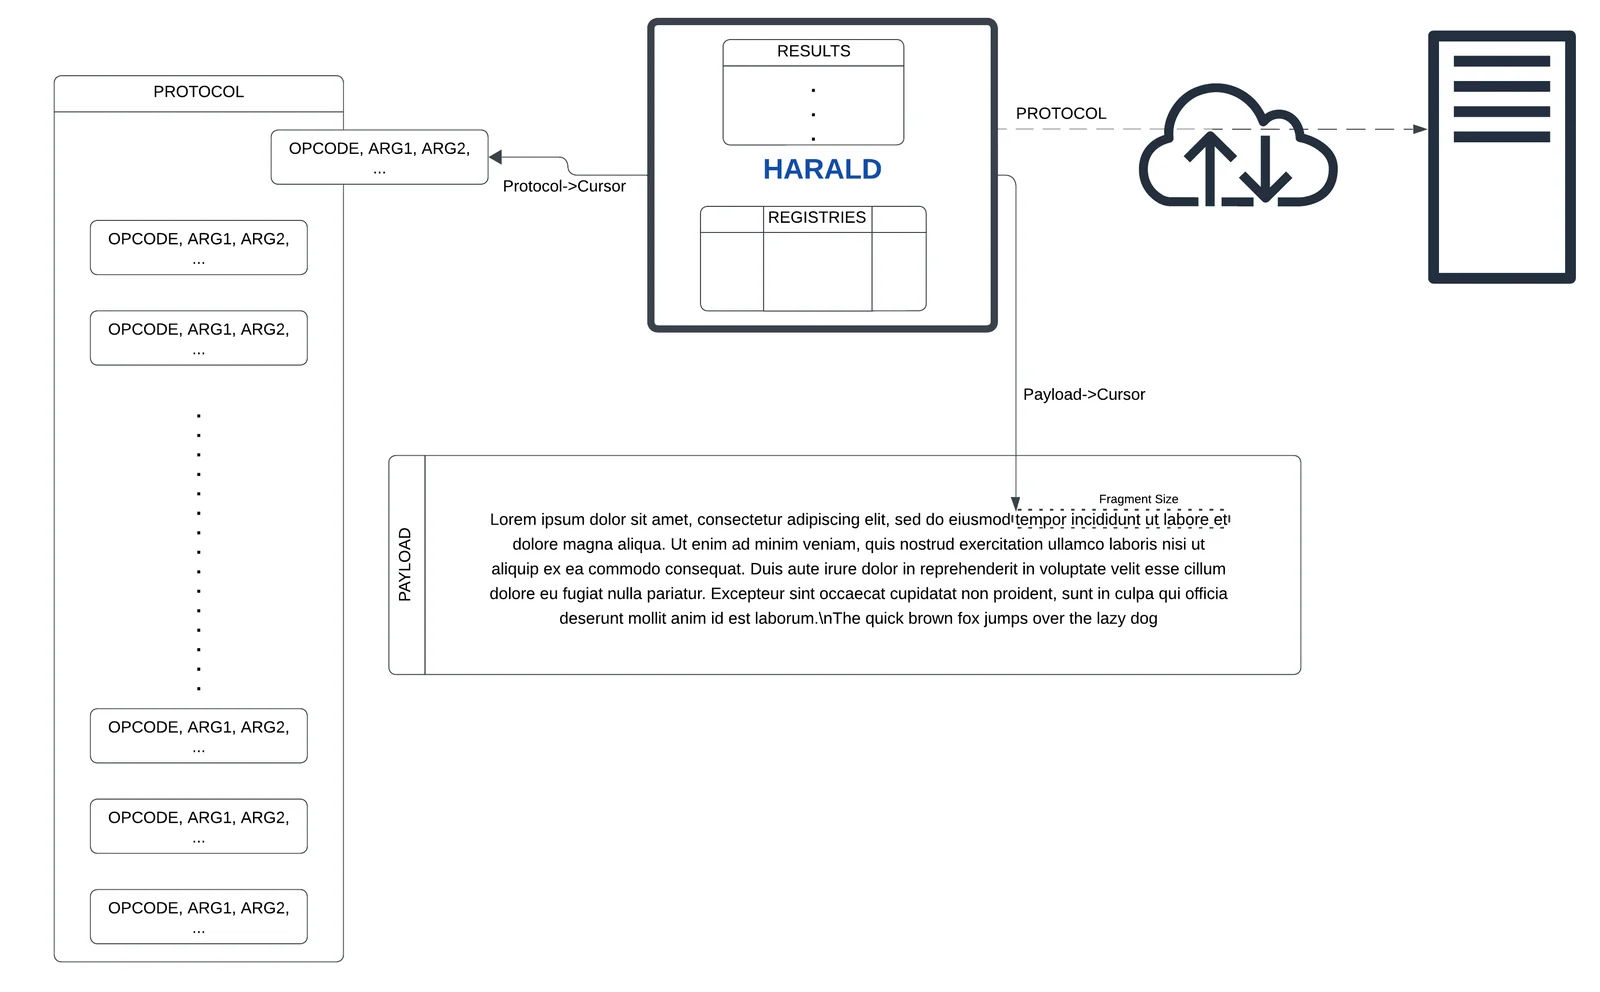
An in-memory minimal CPU for agnostic on-the-fly protocols creation

Proof-of-concept exploit for CVE-2024-10793 targeting WordPress wp-security-audit-log plugin. Demonstrates account takeover, privileged user…

Proof of concept python script for regreSSHion exploit.

PoC of CVE-2024-33883, RCE vulnerability of ejs.

Windows SmartScreen Security Feature Bypass Vulnerability

A set of fully-undetectable process injection techniques abusing Windows Thread Pools

Win32 and Kernel abusing techniques for pentesters

Image Payload Creating/Injecting tools

PoC for triggering buffer overflow via CVE-2020-0796

Exploit implementation for Android Stagefright vulnerability CVE-2015-3864, enabling remote code execution and privilege escalation on Android 5.1.1…

C++ library that retrieves and spoofs Windows syscall arguments using hardware breakpoints and exception handlers to subvert EDR telemetry.