ghostlock-cve-2026-43499

CVE-2026-43499 (GhostLock) — Linux kernel futex PI rt_mutex UAF ARM32 privilege escalation research targeting Huawei Watch 4 Pro (kernel 5.4.210)
binary-exploitationembedded-systems-securityexploitation+5
6
CVE-2026-43499 (GhostLock) — Linux kernel futex PI rt_mutex UAF ARM32 privilege escalation research targeting Huawei Watch 4 Pro (kernel 5.4.210)

ARM32 Linux kernel privilege escalation exploit for CVE-2026-43499 (GhostLock futex UAF) targeting Huawei Watch 4 Pro with multiple exploitation…

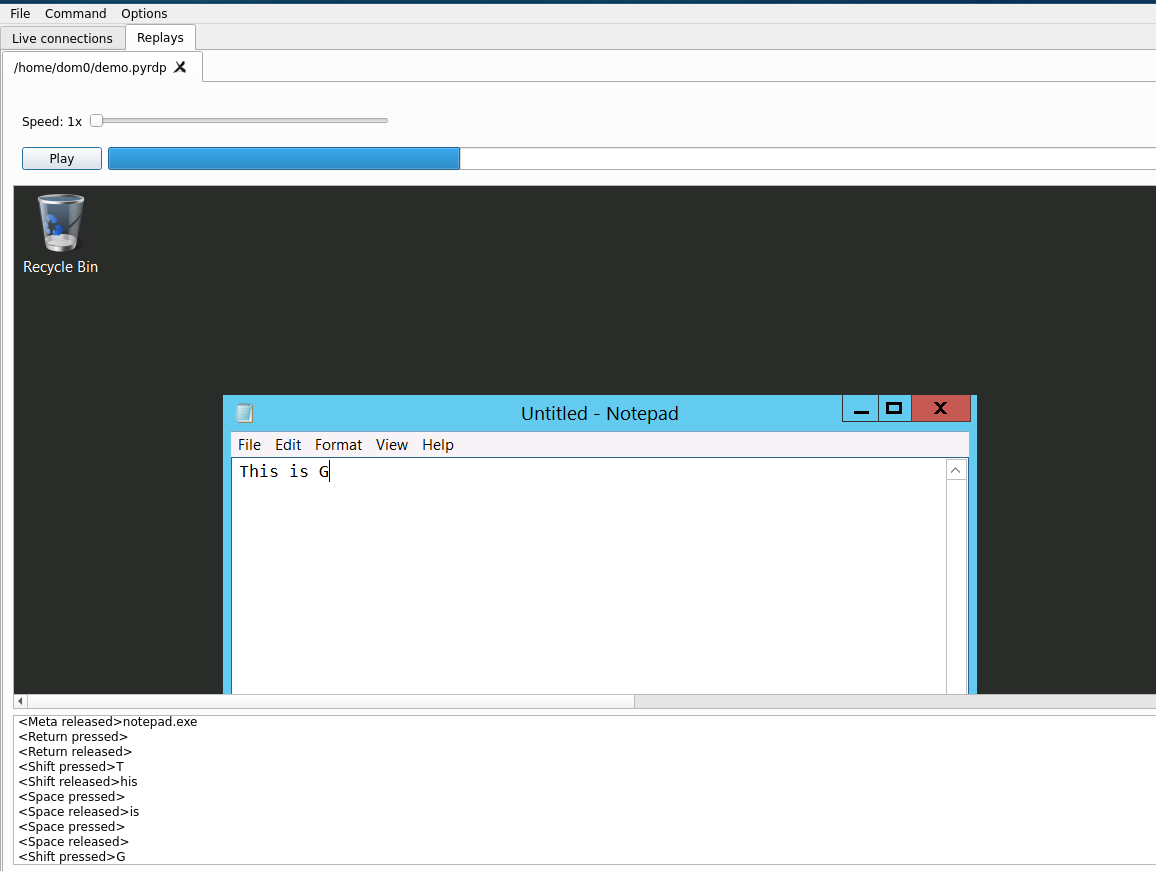
RDP monster-in-the-middle (mitm) and library for Python with the ability to watch connections live or after the fact

Exploit for CVE-2026-41940 providing direct shell access via websocket and persistence through root API key injection.