

sliver
 bishopfox/sliver
Adversary Emulation Framework
adversarial-attackcommand-and-controldata-exfiltration+16
11.8k1 day ago
bishopfox/sliverAdversary Emulation Framework
 vanivamshi/cve-2013-2028-exploit
Docker-based lab and Python exploit for CVE-2013-2028, an Nginx 1.3.9 chunked-parser integer overflow, covering canary recovery, mprotect, and…
 s3n4t0r-0x0/bear-c2
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 e4zyy/project-cve-2026-33017
CVE-2026-33017 - Langflow Unauthenticated RCE Exploit
 lulztigre/cve-2026-41042
Exploits unauthenticated RCE in Apache Gravitino < 1.2.1 via H2 JDBC INIT; hosts SQL/Java payloads, executes commands, and exfiltrates output over…
 debajyoti0-0/cve-2026-27654-poc
Proof-of-Concept and technical analysis for CVE-2026-27654, a heap-based buffer overflow vulnerability in the NGINX HTTP WebDAV module, including…
 depthfirstdisclosures/nginx-rift
NGINX RCE exploits
 razureink/cve-2025-43564-tomcat_put_rce_reproduction
Reproduction of cve-2025-43564-tomcat_put_rce_reproduction
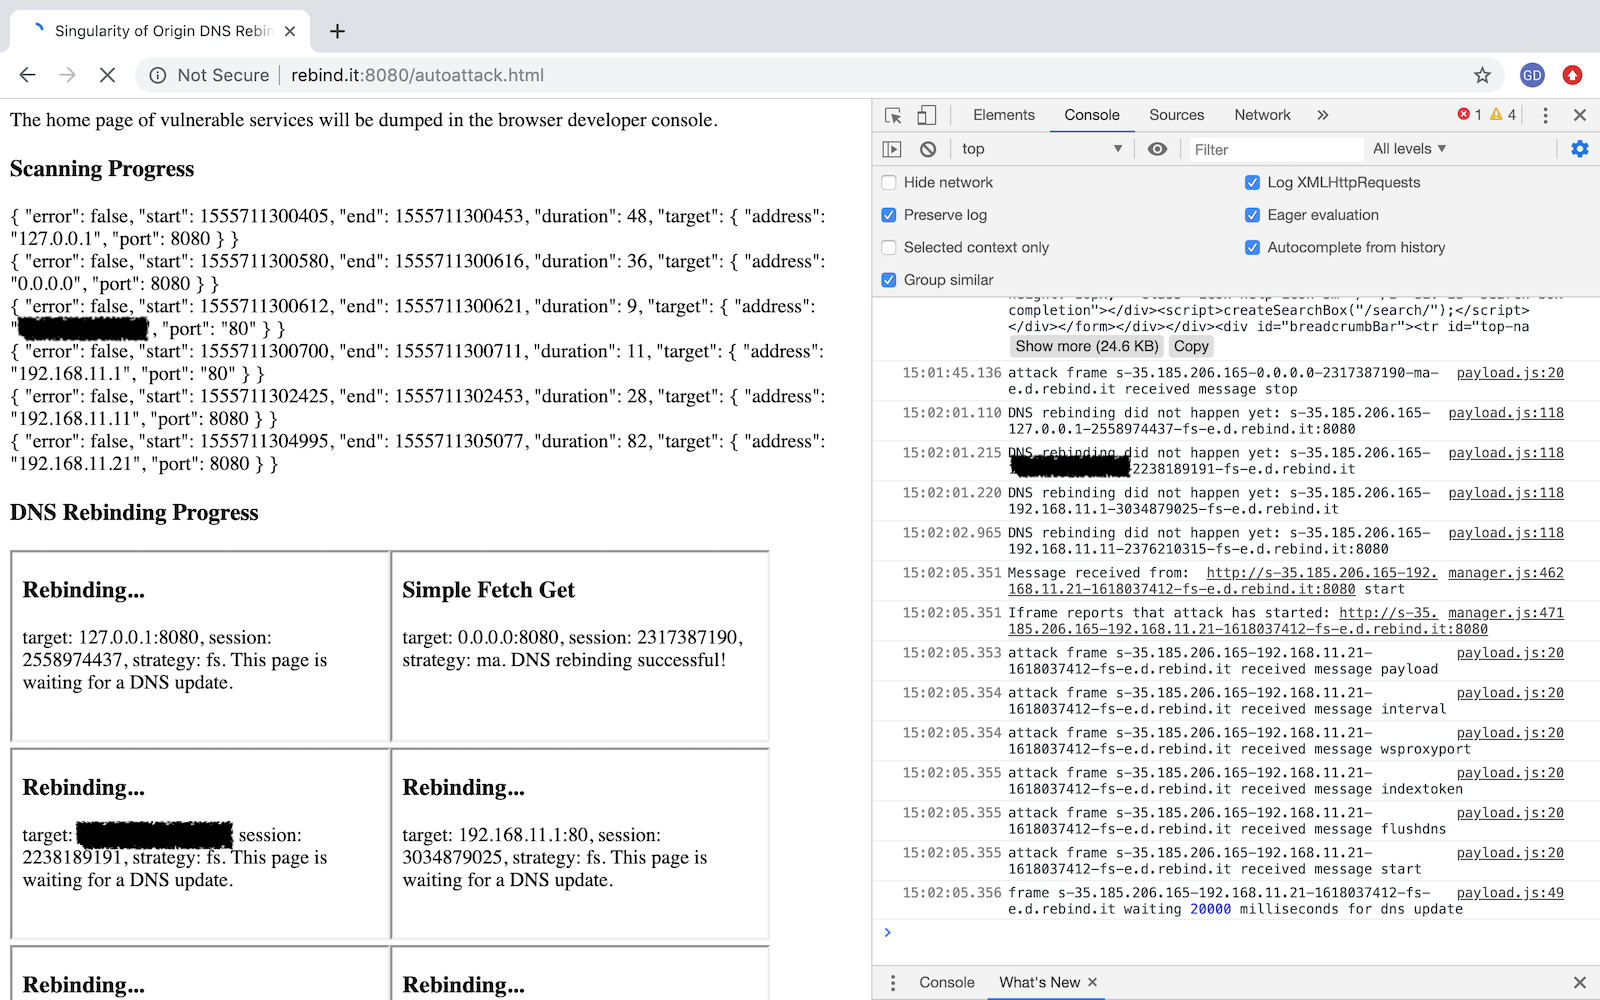 nccgroup/singularity
A DNS rebinding attack framework.
 oscerd/cve-2026-40859
Reproducer for CVE-2026-40859 — Apache Camel camel-netty-http / camel-vertx-http producer-side unsafe deserialization of HTTP response bodies (RCE)
 george1-adel/cve-2026-41940_exploit
Python exploit for CVE-2026-41940, a critical CRLF injection in cPanel/WHM cpsrvd that bypasses authentication and 2FA, granting root-level access…
 aratane/cve-2026-42945
A flaw was found in NGINX, specifically within the ngx_http_rewrite_module. An unauthenticated attacker can exploit this vulnerability by sending…
 biitts/cve-2026-44789-n8n-prototypepollution-rce
CVE-2026-44789 — n8n <1.123.43 HTTP Request pagination prototype pollution to RCE (NODE_OPTIONS runner-spawn gadget). Lab + automated PoC, verified…
 kuri119/cve-2022-22965-spring4shell
Exploit for CVE-2022-22965 (Spring4Shell) enabling remote code execution on unpatched Spring Framework applications via crafted HTTP requests.
 gagaltotal/cve-2026-23918-double-free-apache-httpd-mod_http2
Go-based proof-of-concept exploit for CVE-2026-23918 targeting a double-free vulnerability in Apache httpd mod_http2, enabling pre-auth remote code…
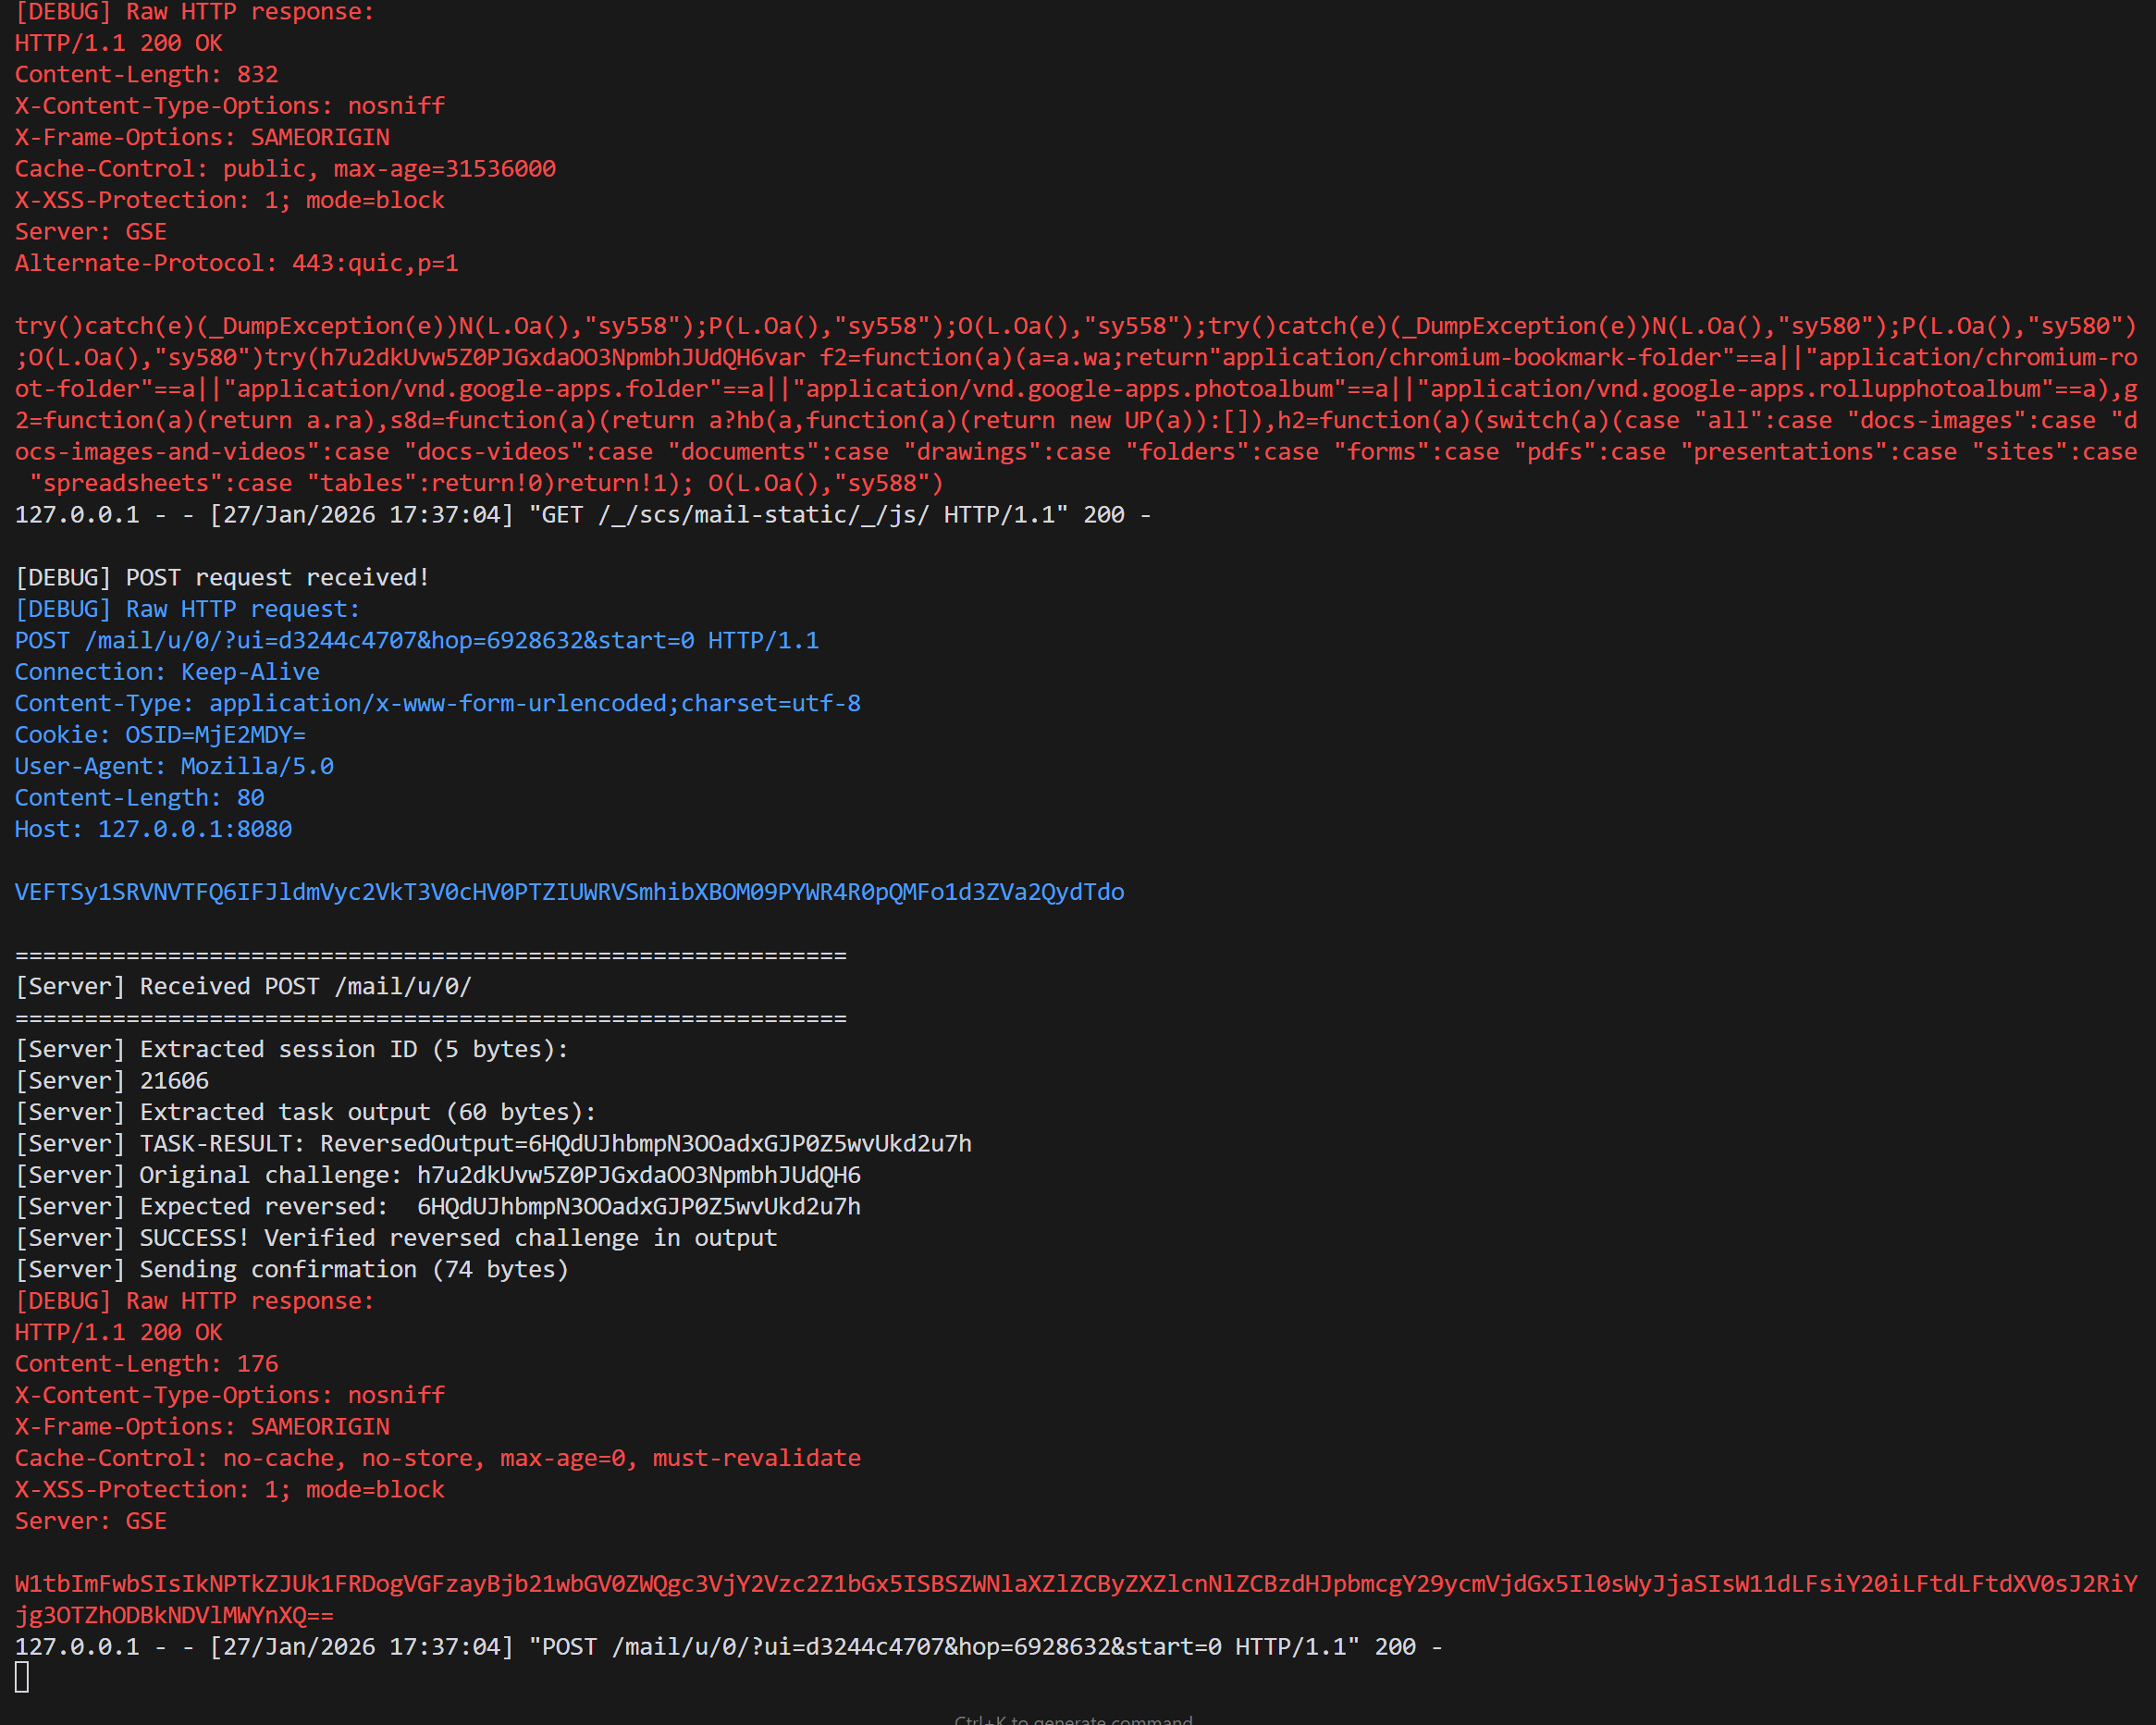 codextf2/openmalleablec2
Open Source Implementation of Cobalt Strike's Malleable C2
 offseckit/cve-2026-24207
CVE-2026-24207 — NVIDIA Triton SageMaker auth bypass to unauth RCE. Detection script, bypass demo, RCE-chain PoC, and IDS rules.
 liaoziqi-gzfls/cve-2026-42945
CVE-2026-42945 Nginx Rift