
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
99 results
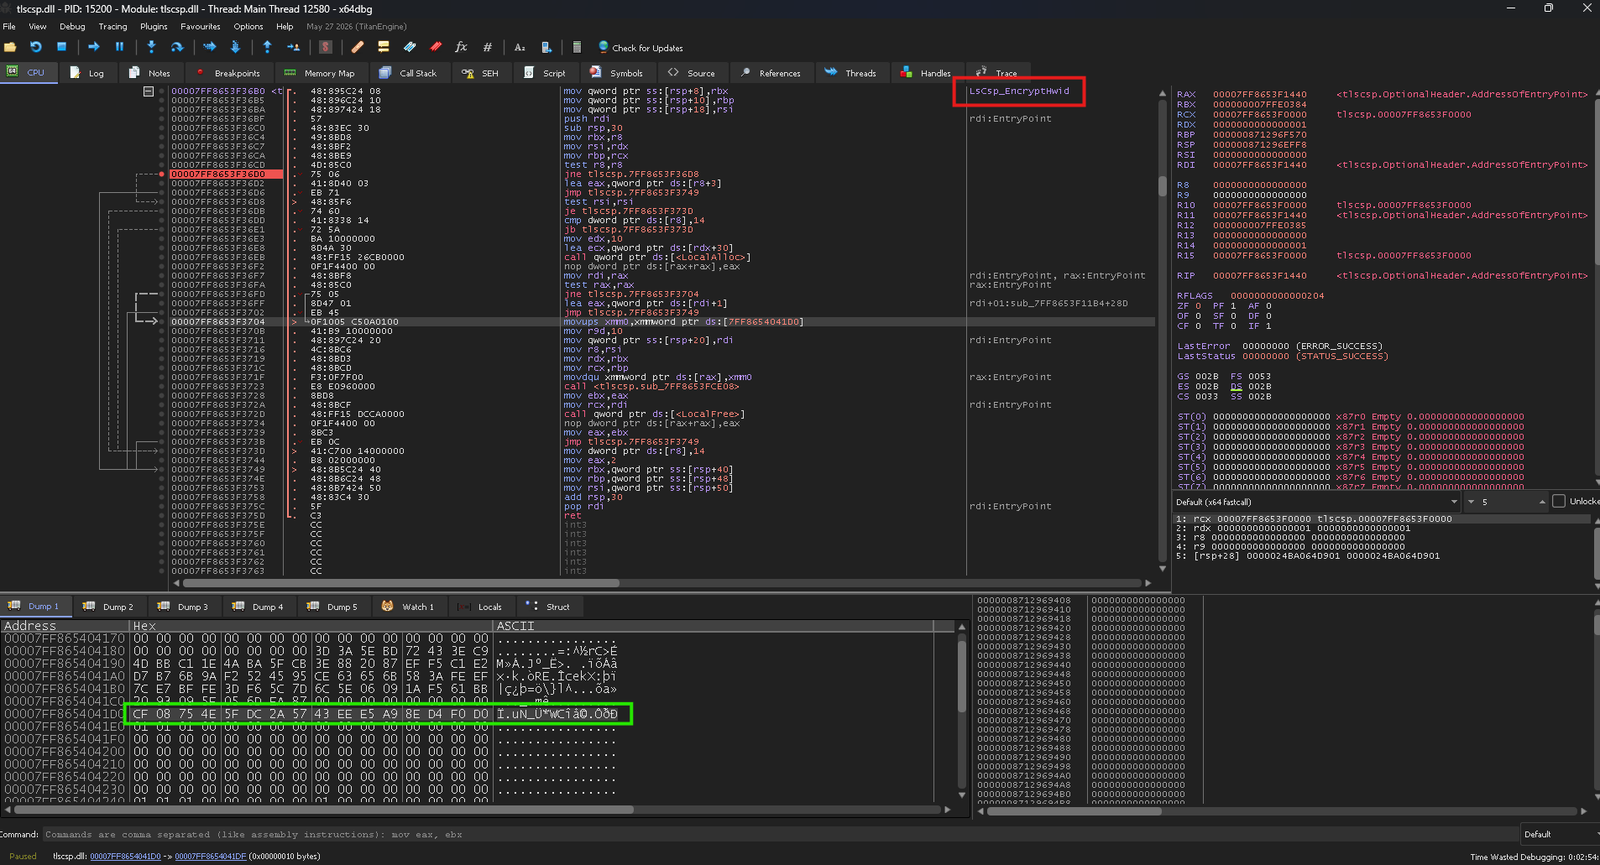
RC4Decryption preview

RC4Decryption

GitHubweedhashpeddler/rc4decryption

Abuses the Microsoft-signed tlscsp.dll LOLBin to run RC4 encrypt/decrypt via LsCsp_EncryptHwid, patching the hardcoded key in memory for BYOK…

binary-analysiscryptographydefensive-tools+6
37
1 month ago
EternalBlueC preview

EternalBlueC

GitHubbhassani/eternalbluec

EternalBlue suite remade in C/C++ which includes: MS17-010 Exploit, EternalBlue vulnerability detector, DoublePulsar detector and DoublePulsar…
binary-exploitationeducationexploitation+7
6131 month ago
SCCM-CVE-2026-47301-Remote-Code-Execution-Exploit preview

SCCM-CVE-2026-47301-Remote-Code-Execution-Exploit

GitHubomribaso/sccm-cve-2026-47301-remote-code-execution-exploit

Proof-of-concept exploit chain (CVE-2026-47301) for Microsoft Configuration Manager (SCCM), combining a broken access, CAB arbitrary-write path…
exploitationpayload-developmentpenetration-testing+3
1082 months ago
PrintSpoofer-ReflectiveDLL preview

PrintSpoofer-ReflectiveDLL

GitHubjonyfilc/printspoofer-reflectivedll

The Windows Print Spooler privilege escalation vulnerability (CVE-2019-1040/CVE-2019-1019) has been implemented as a Reflective DLL for penetration…

exploitationlateral-movementpayload-development+4
22 months ago
POC-CVE-2017-8464-OpenCalculator preview

POC-CVE-2017-8464-OpenCalculator

GitHubplayboisk8/poc-cve-2017-8464-opencalculator

Exploiting the .lnk vulnerability and operating system handling mechanisms regarding explorer.exe and USB drives.
binary-analysisbinary-exploitationexploitation+2
2 months ago
Fritter preview

Fritter

GitHub0xrootpls/fritter

Polymorphic shellcode generator for in-memory execution of EXE, DLL, .NET, VBScript, and JScript with per-output and per-build randomization for…
binary-exploitationexploitationpayload-development+5
2482 months ago
QuickAssist_UAC_Bypass preview

QuickAssist_UAC_Bypass

GitHubr41n3rzuf477/quickassist_uac_bypass

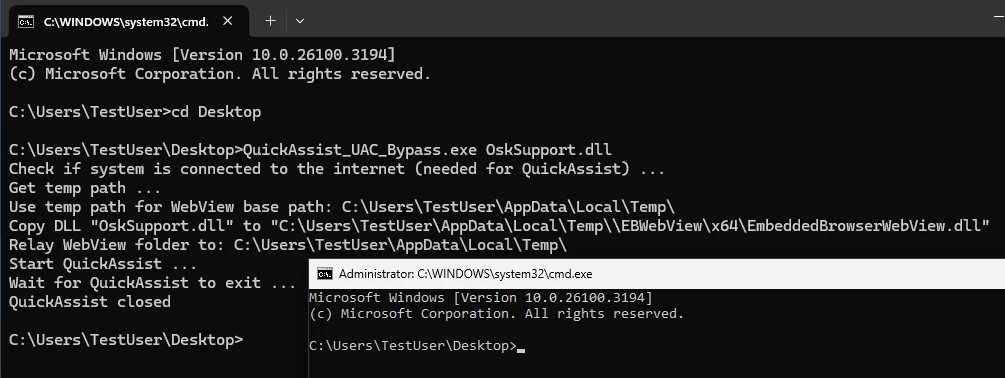
UAC bypass PoC abusing the UIAccess QuickAssist binary to load an attacker-controlled DLL via WebView2 BrowserExecutableFolder, then hijack elevated…
defensive-toolsexploitationpayload-development+4
2443 months ago
CVE-2026-50343-InstallService-EoP preview

CVE-2026-50343-InstallService-EoP

GitHubrat5ak/cve-2026-50343-installservice-eop

CVE-2026-50343 InstallService StaticPluginMap EoP - standard user to SYSTEM
binary-exploitationeducationexploitation+3
483 months ago
chimera preview

chimera

GitHub1neptune/chimera

Rust-based DLL hijacking loader for MobaXterm (CVE-2026-6421) with persistence
binary-exploitationexploitationpayload-development+4
3 months ago
PhantomCtx preview

PhantomCtx

GitHubr3xmax/phantomctx

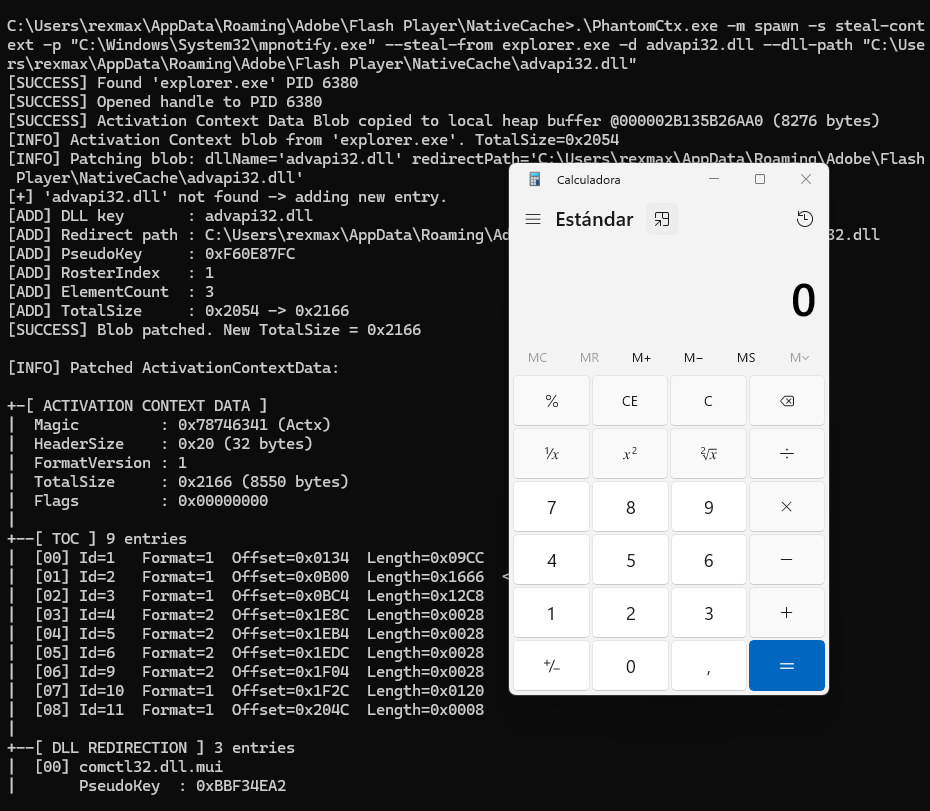
Activation Context Hijacking Evasion Tool
binary-exploitationexploitationpayload-development+3
3064 months ago
rustdllproxy preview

rustdllproxy

GitHubjohnswiftc/rustdllproxy

Generate Proxy DLLs in Rust
payload-developmentpayload-generationpenetration-testing+3
564 months ago
staged-DLL-Injection-SMB- preview

staged-DLL-Injection-SMB-

GitHubkasturixbm5/staged-dll-injection-smb-

Staged DLL injection proof-of-concept built in C using Win32 APIs — developed in an isolated lab environment for red team certification study (CRTO).
educationexploitationlabs-practice+5
425 months ago
ExportHider preview

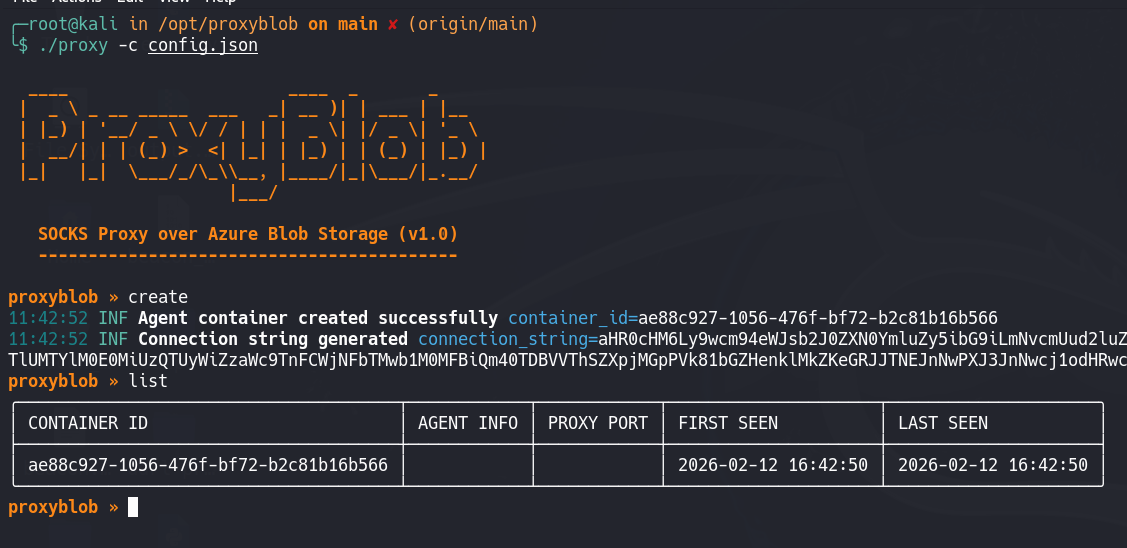
ExportHider

GitHubfrkngksl/exporthider

ExportHider: Generating Export Table during Runtime to Hide the Exported Functions from the DLL File.
binary-analysisdynamic-code-analysisexploitation+4
336 months ago
ClickOnceBlobber preview

ClickOnceBlobber

GitHubdazzyddos/clickonceblobber

Weaponize signed .NET ClickOnce applications for initial access by hijacking a dependency DLL via AppDomainManager injection and loading a C# port of…
command-and-controlpayload-developmentred-teaming+1
1688 months ago
CVE-2026-21508_POC preview

CVE-2026-21508_POC

GitHub0xc4r/cve-2026-21508_poc

Proof-of-concept for CVE-2026-21508, demonstrating a DLL hijacking attack on Windows 11 that escalates privileges by loading a crafted DLL into…
binary-exploitationexploitationpayload-development+2
298 months ago
NoFaxGiven preview

NoFaxGiven

GitHubhackerhouse-opensource/nofaxgiven

Code Execution & Persistence in NETWORK SERVICE FAX Service

exploitationpayload-developmentpersistence-mechanisms+3
379 months ago
iscsicpl_bypassUAC preview

iscsicpl_bypassUAC

GitHubhackerhouse-opensource/iscsicpl_bypassuac

UAC bypass for x64 Windows 7 - 11

exploitationpayload-developmentpost-exploitation+2
8489 months ago
cve-2021-34527 preview

cve-2021-34527

GitHubhackerhouse-opensource/cve-2021-34527

CVE-2021-34527 AddPrinterDriverEx() Privilege Escalation

binary-exploitationexploitationpayload-development+3
239 months ago
Previous123456Next