
CVE-2022-22077
 grisuno/cve-2022-22077
BYOVD exploitation framework for CVE-2022-22077 targeting RTCore64.sys. Demonstrates kernel token theft, privilege escalation to SYSTEM, and C2…
binary-exploitationcommand-and-controleducation+5
7
grisuno/cve-2022-22077BYOVD exploitation framework for CVE-2022-22077 targeting RTCore64.sys. Demonstrates kernel token theft, privilege escalation to SYSTEM, and C2…
 eqstlab/cve-2026-6951
Proof-of-concept exploit for CVE-2026-6951, a simple-git --config filter bypass enabling RCE via the Git ext protocol, with a Docker lab and reverse…
 themalwareguardian/cve-2022-34302
Demonstrates CVE-2022-34302, a Secure Boot bypass via the New Horizon Datasys signed bootloader whose built-in custom PE/COFF loader executes…
 themalwareguardian/cve-2022-34303
Demonstrates CVE-2022-34303 Secure Boot bypass via CryptoPro signed UEFI Shell, using the mm command to nullify gSecurity2 and load unsigned UEFI…
 princeh4k/spring4shell-poc
Proof of Concept for exploiting the CVE-2022-22965 (Spring4Shell) vulnerability in an isolated environment, with Remote Code Execution (RCE)…
 atici/imagemagick-cve-2022-44268-poc
A bash script for easyly exploiting ImageMagick Arbitrary File Read Vulnerability CVE-2022-44268
 winstxnhdw/cve-2022-30190
A proof of concept for CVE-2022-30190 (Follina).
 seal-sec-demo-2/yaml-payload-2
SnakeYAML CVE-2022-1471 exploit payload for Seal Security demos
 catherines77/activemq-exptools
Apache ActiveMQ漏洞综合利用工具(CVE-2015-5254,CVE-2016-3088,CVE-2022-41678,CVE-2023-46604,CVE-2024-32114,CVE-2026-34197,CVE-2026-40466, CVE-2026-42588)
 shndnth/cve-2022-30190
Educational Proof-of-Concept for the CVE-2022-30190 (Follina) vulnerability.
 danielhallbro/cve-2022-36804-bitbucket-rce-analysis
Full-chain reproduction of CVE-2022-36804 (Bitbucket RCE). Includes a Dockerized laboratory, pspy64 monitoring for null-byte injection verification,…
 seal-sec-demo-2/yaml-payload
SnakeYAML CVE-2022-1471 exploit payload for demo
 developerfred/cve-2022-31199
Proof-of-concept exploits for CVE-2022-31199, a critical .NET deserialization RCE in Netwrix Auditor. Includes Python and PowerShell scripts, payload…
 krill-x7/cve-2022-25226
Python exploit script for ThinVNC 1.0b1 authentication bypass (CVE-2022-25226) that chains unauthenticated /cmd endpoint access with AMSI bypass and…
 tdawg506/mailenable-cve-2022-36934
Metasploit module for MailEnable CVE-2022-36934 authentication bypass RCE
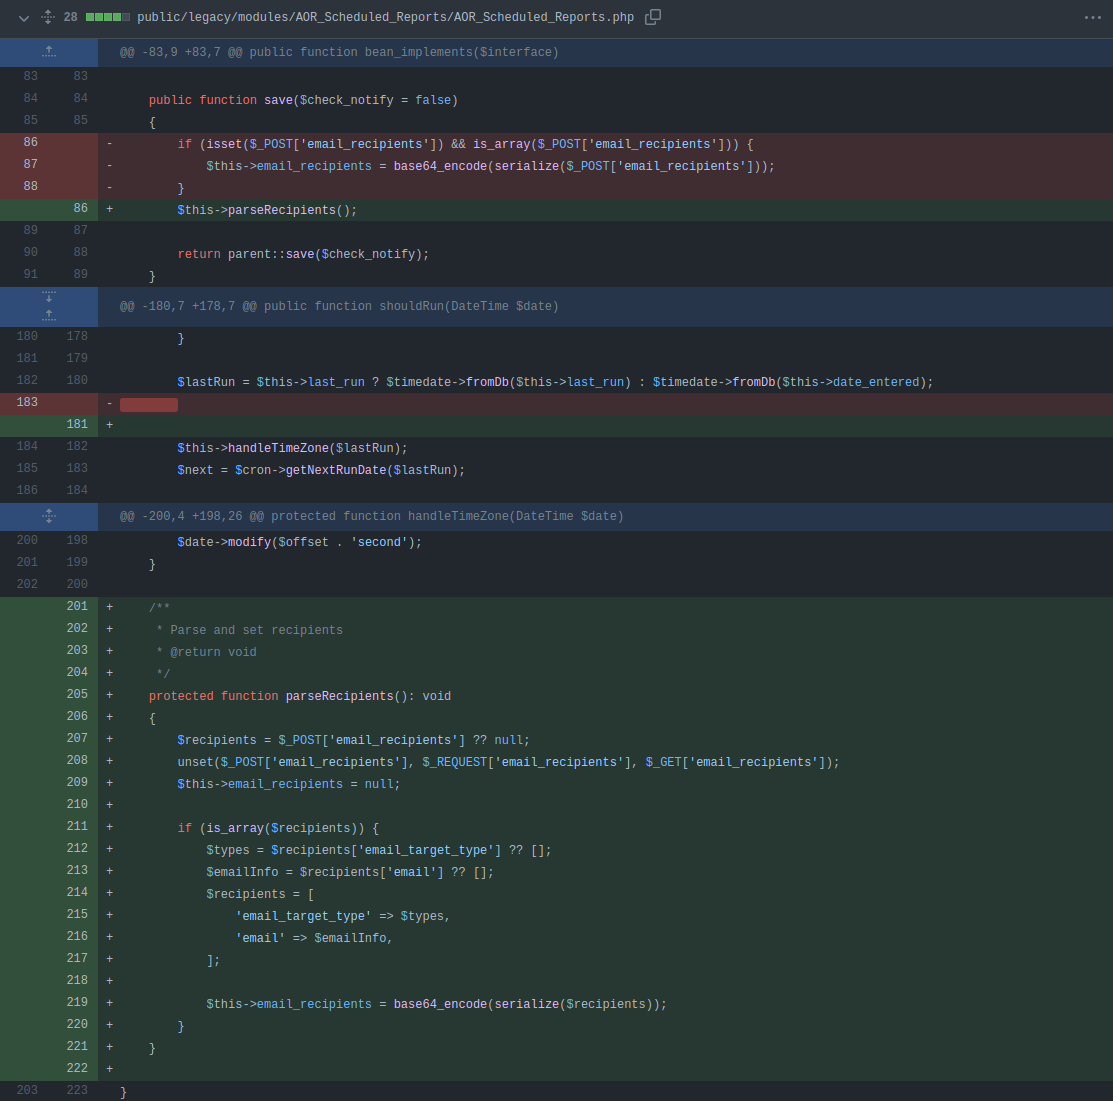 manuelz120/cve-2022-23940
PoC for CVE-2022-23940
 bytereaper77/dirty-pipe
Proof-of-concept exploit for CVE-2022-0847 (Dirty Pipe) enabling local privilege escalation on Linux kernels 5.8–5.16 via pipe buffer manipulation…
 mbadanoiu/cve-2025-26865
CVE-2025-26865: FreeMarker Server-Side Template Injection via the "ecommerce" plugin in Apache OfBiz