
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
70 results
AdaptixC2 preview

AdaptixC2

GitHubadaptix-framework/adaptixc2

AdaptixC2 is a highly modular advanced redteam toolkit
command-and-controlencryption-decryption-toolsexploit-frameworks+9
3.7k
16 days ago
CS-Remote-OPs-BOF preview

CS-Remote-OPs-BOF

GitHubtrustedsec/cs-remote-ops-bof

Remote operations commands implemented using Beacon Object Files

authenticationencryption-decryption-toolslateral-movement+6
1.2k16 days ago
mythic_telegram_profile preview

mythic_telegram_profile

GitHubdavidcarliez/mythic_telegram_profile

Mythic C2 profile that tunnels Athena and Apollo agent traffic through Telegram bot-to-bot messages, bridging encrypted payloads to Mythic via its…
command-and-controlencryption-decryption-toolsexploit-frameworks+5
417 days ago
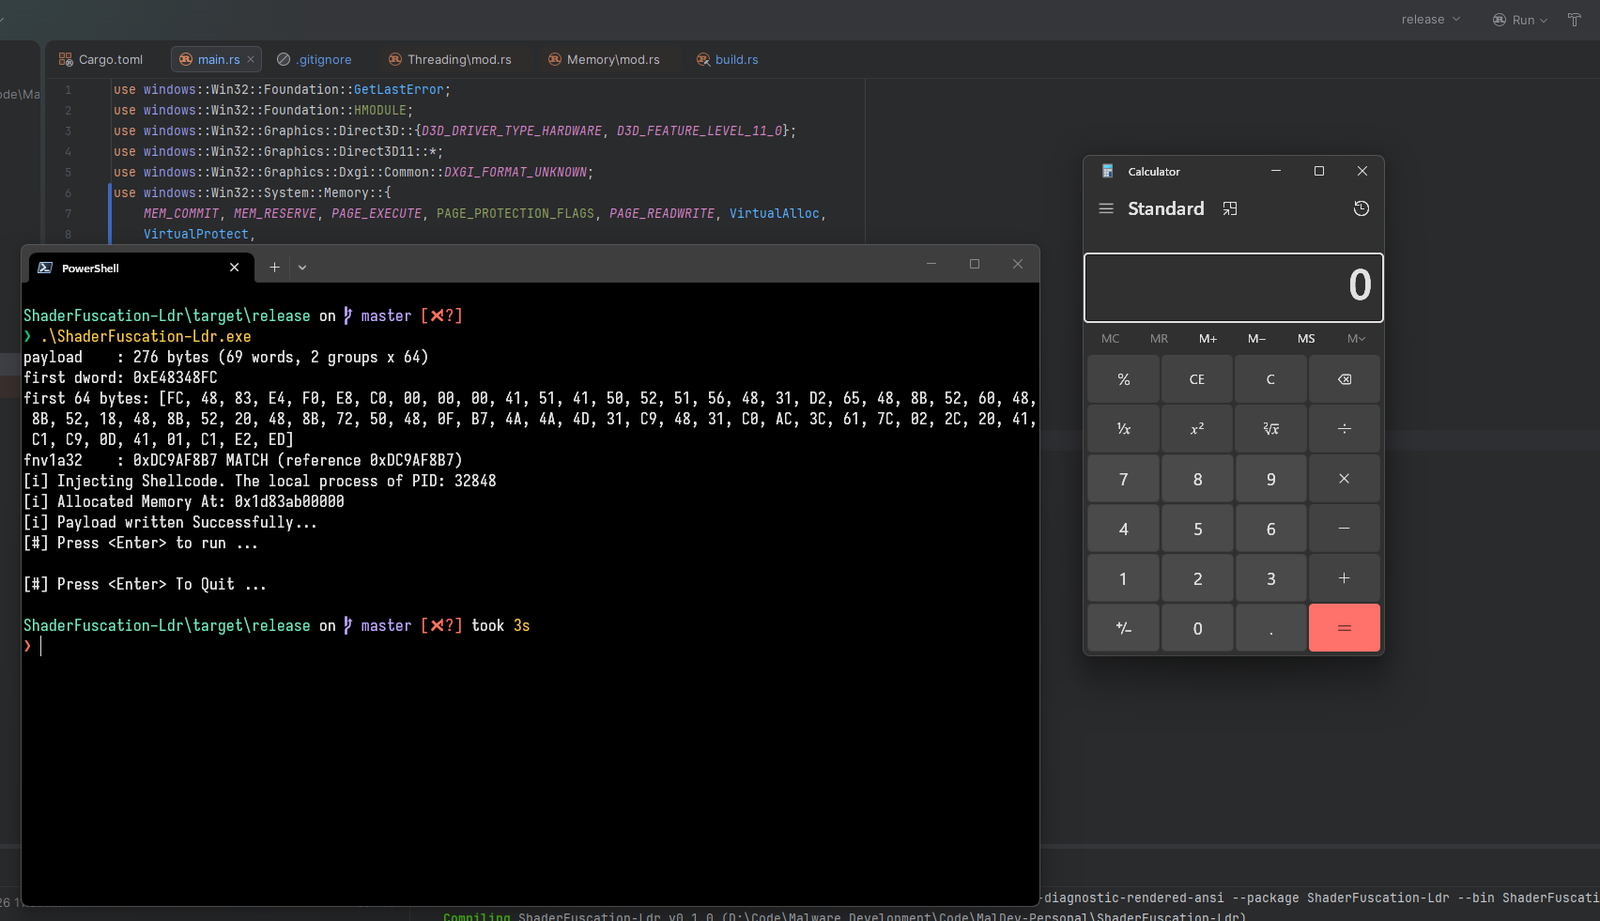
polychrome-rs preview

polychrome-rs

GitHubdovelus/polychrome-rs

A PoC on how to use a Compute Shader as Payload
defensive-toolsencryption-decryption-toolsexploitation+5
719 days ago
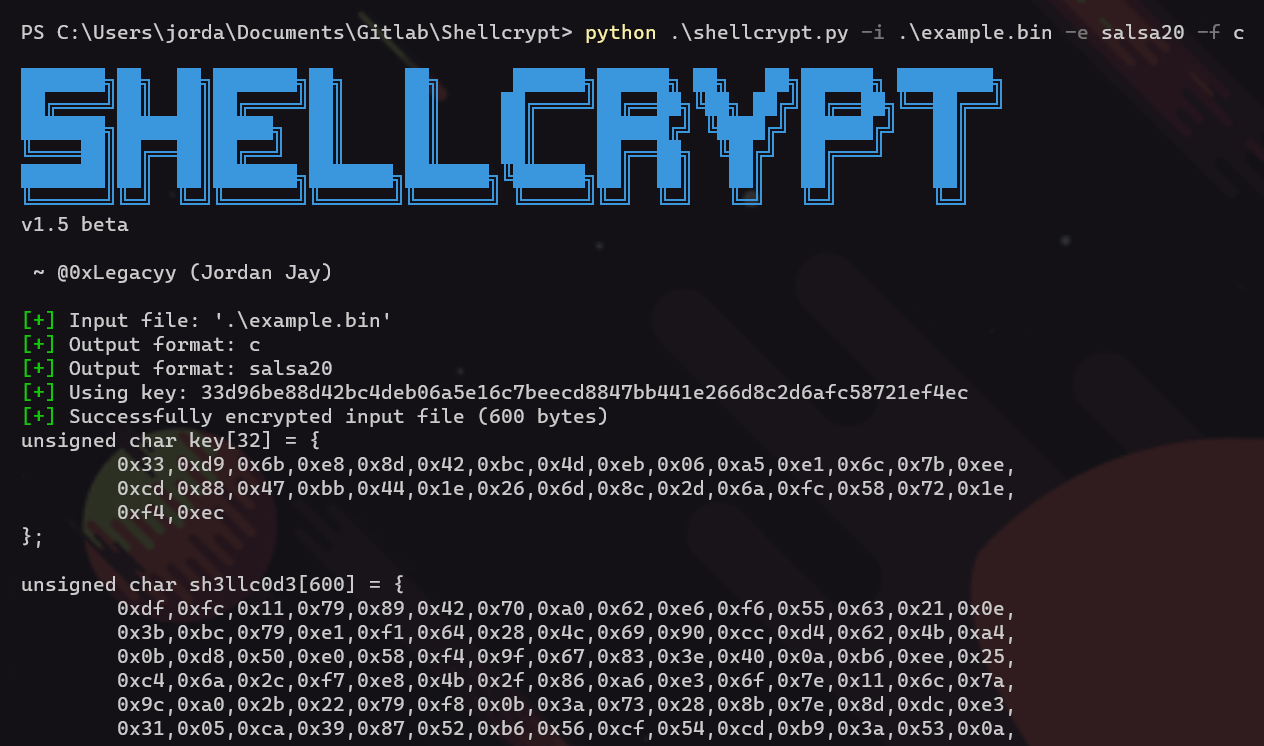
Shellcrypt preview

Shellcrypt

GitHubiilegacyyii/shellcrypt

A QoL tool to obfuscate shellcode. In the future will be able to chain encoding/encryption/compression methods.
cryptographyencryption-decryption-toolspayload-development+3
21822 days ago
msteams preview

msteams

GitHubwhispergate/msteams

Mythic C2 profile that tunnels agent traffic through Microsoft Teams channels using the Microsoft Graph API, with AES256 encryption, jitter, kill…

command-and-controldefensive-toolsencryption-decryption-tools+5
3927 days ago
voidsyscall preview

voidsyscall

GitHubvoidsecsoftwares/voidsyscall

Cross-platform syscall-powered implant & C2 — direct syscalls (Win), raw syscalls (Linux), HTTPS/DNS/ICMP channels. No winapi layer.

command-and-controlencryption-decryption-toolsids-ips-evasion+9
641 month ago
stratum-c2 preview

stratum-c2

GitHublame-projects/stratum-c2

Cloud dead-drop C2 framework — RSA-4096 + AES-256-GCM, 5 cloud providers, Rust-only agents, P2P mesh, persistence engine, credential harvesting
cloud-securitycommand-and-controlencryption-decryption-tools+6
431 month ago
ransomwhere preview

ransomwhere

GitHubhazcod/ransomwhere

A PoC ransomware sample to test out your ransomware response strategy.

adversarial-attackencryption-decryption-toolsincident-response+3
2192 months ago
httpx preview

httpx

GitHubmythicc2profiles/httpx

Configurable, Community driven, HTTP C2 Profile
command-and-controldefensive-toolsencryption-decryption-tools+5
312 months ago
voron-crypto preview

voron-crypto

GitHubsoftdeadlock/voron-crypto

Voron messenger crypto/protocol library (X3DH-lite + Double Ratchet, group sender-keys, onion transport) — external review requested
command-and-controlcryptographyencryption-decryption-tools+3
12 months ago
nimcrypt preview

nimcrypt

GitHubchaelsoo/nimcrypt

Nim-based encryption tool for obfuscating shellcode and payloads for evading Windows Defender.

anti-botcommand-and-controlencryption-decryption-tools+6
282 months ago
Hollow preview

Hollow

GitHubchaelsoo/hollow

A shellcode loader generator with support for multiple injection techniques, built for red team engagements.
binary-exploitationencryption-decryption-toolsexploitation+7
1023 months ago
DirtyClone preview

DirtyClone

GitHubgl1tch0x1/dirtyclone

Proof-of-concept local privilege escalation tool exploiting a kernel XFRM/ESP vulnerability (CVE-2026-43503) via crafted AES-CBC encrypted payloads…

binary-exploitationcryptographyexploitation+3
23 months ago
Maverick preview

Maverick

GitHubblacksnufkin/maverick

Adaptix C2 agent using Crystal Palace PIC linker and PICO module system

binary-analysiscommand-and-controlencryption-decryption-tools+5
1194 months ago
CVE-2026-23744 preview

CVE-2026-23744

GitHuboryk0/cve-2026-23744

CVE-2026-23744 Reverse shell

exploitationpayload-developmentpenetration-testing+3
4 months ago
FUD-C2-Framework preview

FUD-C2-Framework

GitHubx3r0day/fud-c2-framework

A fileless reverse shell and C2 framework leveraging direct syscalls, proxy tunneling, and ChaCha20 encryption for AV evasion.
command-and-controlencryption-decryption-toolsids-ips-evasion+9
75 months ago
Huan preview

Huan

GitHubfrkngksl/huan

Encrypted PE Loader Generator

binary-exploitationencryption-decryption-toolsexploit-frameworks+5
5486 months ago
Previous1234Next