metasploit-framework

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

XSS2Shell: WordPress Preauth XSS to RCE Chain (CVE-2026-64638)

Python PoC for CVE-2026-92247, an authenticated RCE in SynaptikCMS file manager via PHP upload and rename validation bypass.

Bash proof-of-concept exploit for CVE-2026-33017 in Langflow, triggering a reverse shell callback to a netcat listener.

Drag and Drop File Upload for Elementor Forms - Unauthenticated Arbitrary File Upload to RCE.🔥

Exploits CVE-2026-57811, an unauthenticated RCE in Realtyna Organic IDX + WPL Real Estate WordPress plugin, enabling shell upload and command…

Proof-of-concept exploit for CVE-2026-32475, an unauthenticated arbitrary file upload in Elementor Pro leading to remote code execution. Includes…

Proof-of-concept exploit for CVE-2026-27475, an authenticated insecure deserialization vulnerability in SPIP 4.4.8 leading to remote code execution.

PoC and detection templates for pre-auth RCE and payment tampering in Balbooa Forms (Joomla), including Python exploit and Nuclei detection template.

Proof-of-concept exploit for arbitrary code execution through eval() injection in a ham radio programming application, including malicious .itm/.img…

Pre-auth RCE via FilteredObjectInputStream MarshalledObject bypass in Apache Log4j 2

PoC for CVE-2026-32475: Elementor Pro <=4.2.1 unauthenticated file upload to RCE. Stdlib-only Python.

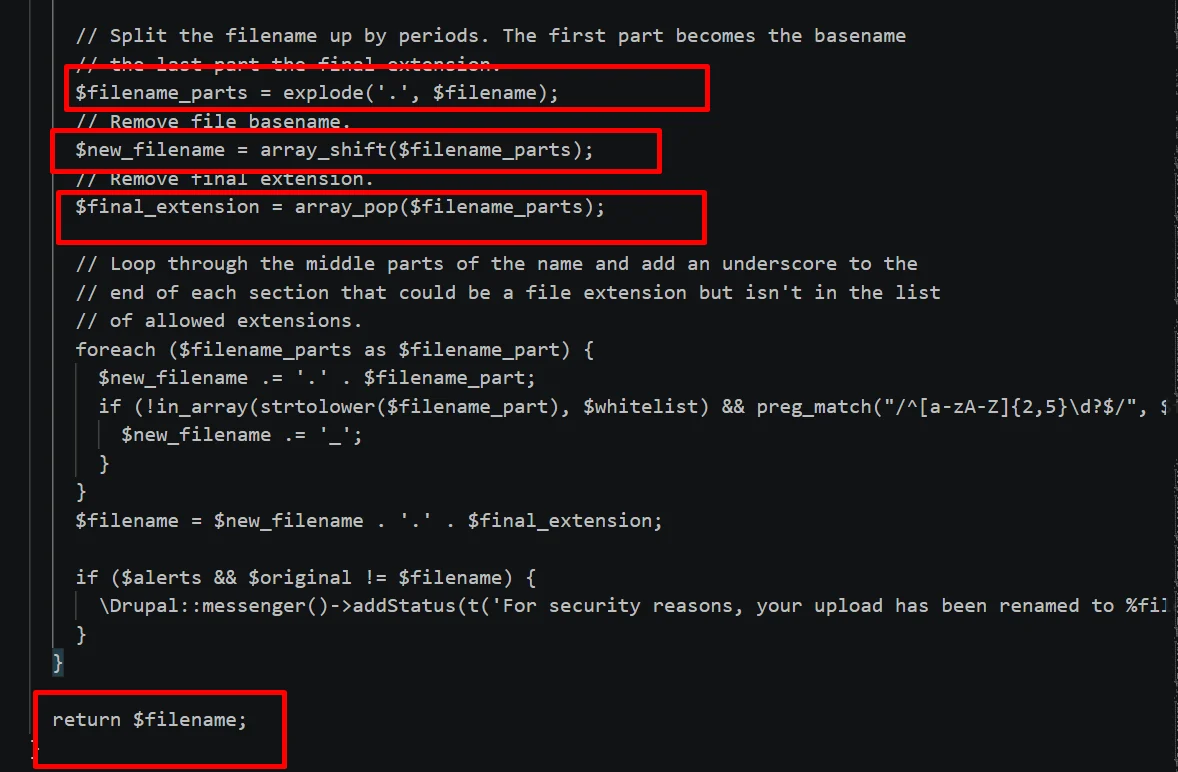
CVE-2020-13671 - Drupal RCE via File Upload Vulnerability Analysis and PoC

Proof-of-concept exploit for CVE-2026-62911: pre-auth RCE on Microsoft Exchange via NTLM relay to MRSProxy, writing an ASPX webshell for SYSTEM…

Practical study notes and walkthroughs for PortSwigger Academy labs, covering web vulnerabilities, payloads, enumeration, and BSCP exam strategies.

Technical analysis and clean Java Thread Echo PoC for Oracle WebLogic Server vulnerability chain.

Exploits unauthenticated RCE in Apache Gravitino < 1.2.1 via H2 JDBC INIT; hosts SQL/Java payloads, executes commands, and exfiltrates output over…

CVE-2026-73034 — DB-GPT v0.8.1 unauth path traversal → arbitrary file write as root via user-id header. Verified + fix diff