metasploit-framework

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Proof-of-concept exploit for Apache Tomcat deserialization RCE (CVE-2025-24813). Uploads a crafted session file via PUT request and triggers…

Android app that checks a supported Vivo X200 Ultra, then uses Shizuku to attempt temporary root with CVE-2026-98260 and load KernelSU. Optional boot…

Android front end for CVE-2026-98260: root shell + KernelSU late-load through Shizuku

All-in-one penetration testing platform with MITM proxy, web fuzzer, reverse connection handler, and plugin system for automated security testing and…

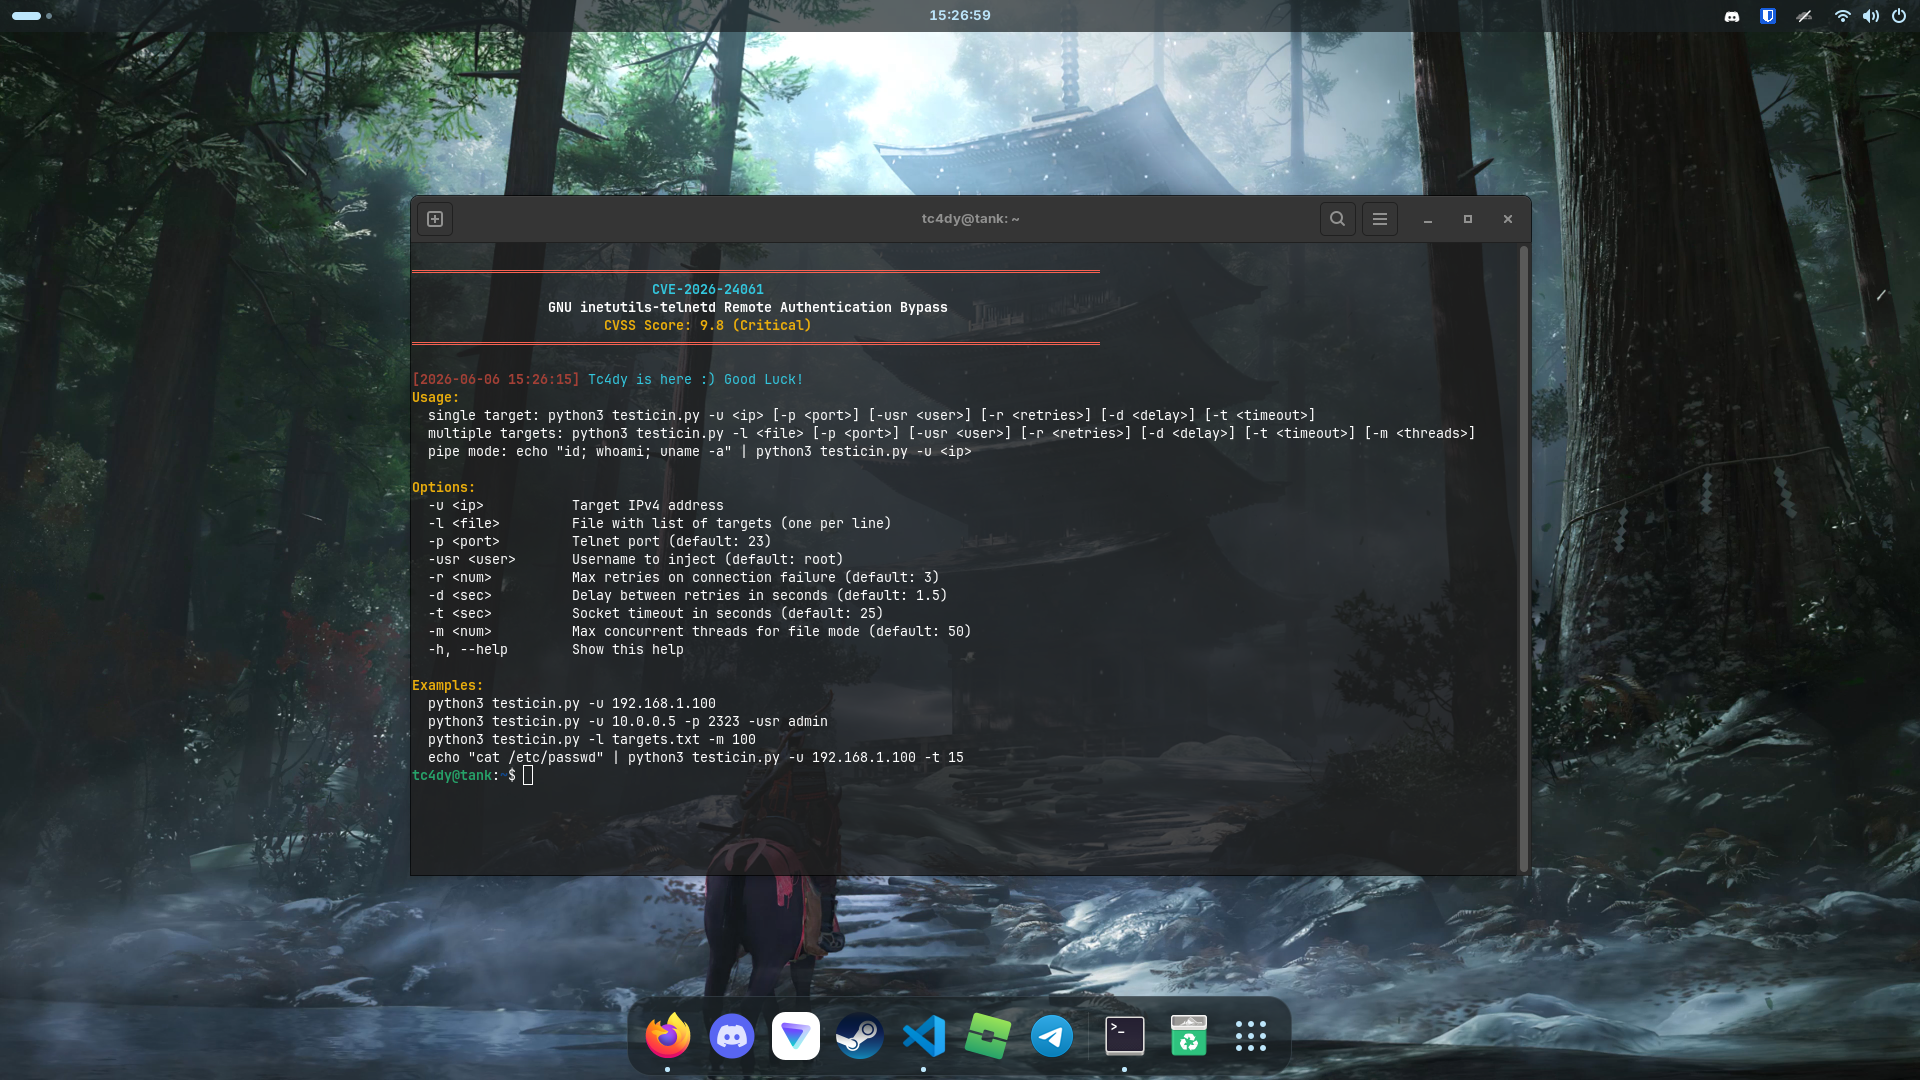
Remote authentication bypass exploit for GNU inetutils-telnetd (CVE-2026-24061) using CRLF injection to gain instant root shell. Supports single/mass…

Shizuku-driven CVE-2026-98260 root + KernelSU runtime LKM loader for Xiaomi yingtian / lhasa (kernel 6.18.21)

Android kernel PoC for CVE-2026-98260: POSIX CPU timer use-after-free achieving uid-0 root and KernelSU late-load on vivo S60, with BTF-based offset…

One-click root for vivo/iQOO devices on locked bootloader | CVE-2026-43499 + KernelSU

Proof-of-concept exploit for CVE-2021-44967 enabling remote code execution in LimeSurvey 5.2.4 via malicious plugin upload, with reverse shell…

A method for CVE-2025-31710 and to connect to cmd_skt to obtain a root shell on unisoc unpatched models

Android kernel LPE exploit for CVE-2026-98260 (POSIX CPU timer UAF), ported to OPPO Pad Air 5 / MT6878, gaining temporary root and loading KernelSU.

Android kernel LPE research for CVE-2026-98260 (posix-cpu-timers UAF): trigger PoC, fake-cred and real-cred uid-0 shell chains, plus a…

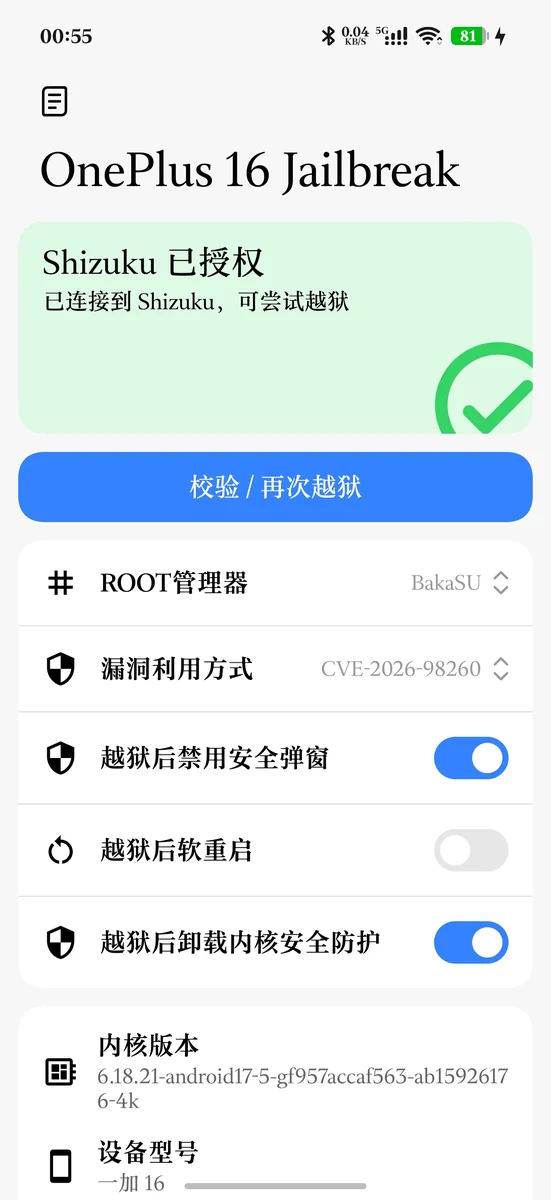
OnePlus 16 (PYB110) jailbreak: CVE-2026-98260 + KernelSU / KernelSU Next / BakaSU / SukiSU Ultra LKM

One-tap Android root for Samsung Galaxy devices, built around the CVE-2026-98260 timer exploit.

REDMI K90 Max在OS4.0.5.0.XAACNXM利用CVE-2026-98260获取ROOT权限并加载KSU模块。

Android local privilege-escalation payload exploiting a POSIX CPU timer use-after-free (CVE-2026-98260) on iQOO Neo11 kernel 6.6.89 to obtain a uid=0…

CVE-2026-98260 一键 root | 玄戒 O1 家族:Xiaomi Pad 7S Pro 12.5 (violin) / Pad 7 Ultra (jinghu) / 15S Pro (dijun),内核 6.18.21 | 可选加载 KernelSU / SukiSU /…