
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
701 results
CoercedPotato preview

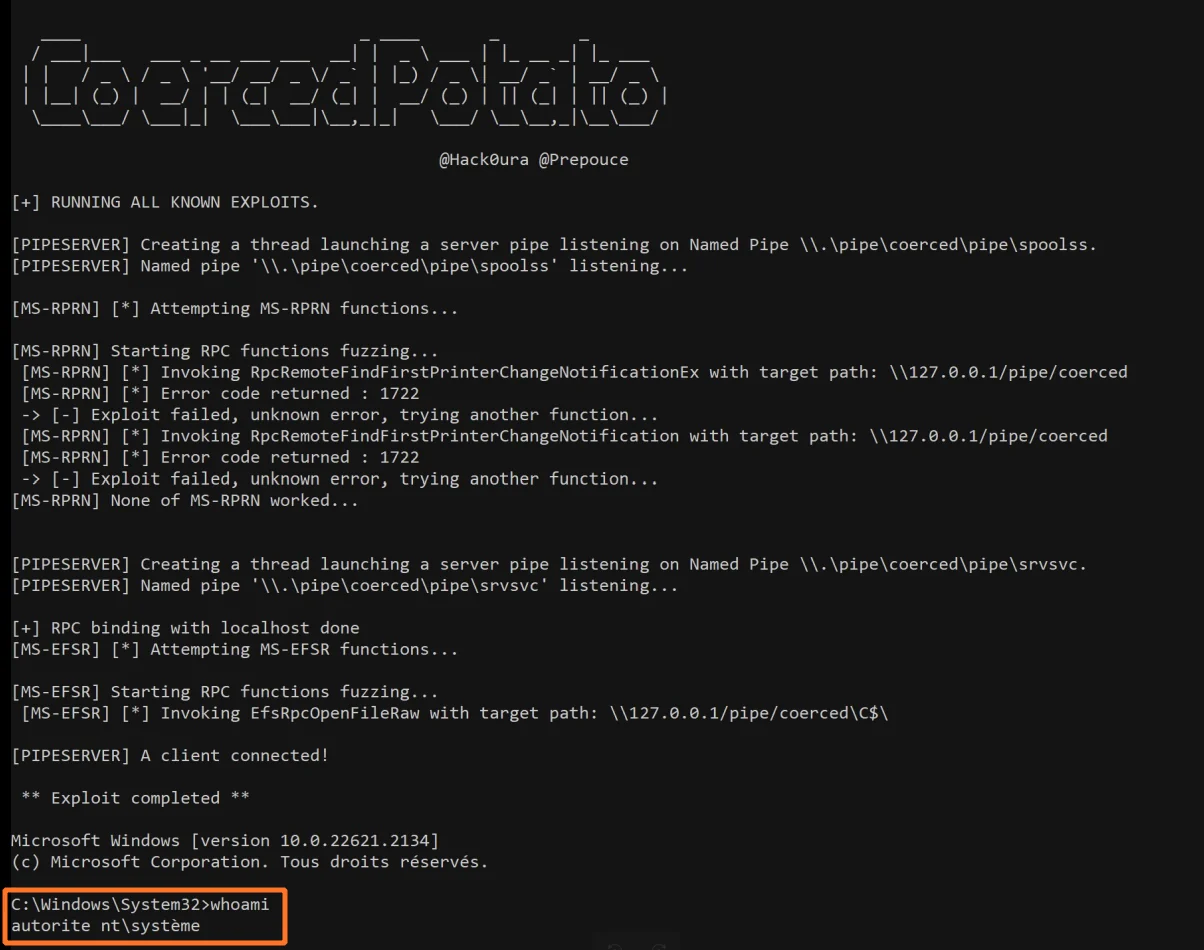
CoercedPotato

GitHubprepouce/coercedpotato

Windows local privilege escalation tool that abuses SeImpersonatePrivilege via MS-RPRN and MS-EFSR RPC coercion to execute commands as SYSTEM.

exploitationpayload-developmentpenetration-testing+3
401
2 months ago
php2shell-poc preview

php2shell-poc

GitHubikow/php2shell-poc

CVE-2026-109618/109619 PHP session.upload_progress Exploit Research — POC & Analysis

exploitationlabs-practicememory-forensics+5
1341 day ago
CVE-2026-0006-step-2 preview

CVE-2026-0006-step-2

GitHubr3n3r0/cve-2026-0006-step-2

Research package demonstrating a leak-assisted ROP chain in Android media.swcodec via the CVE-2026-0006 APV decoder heap overflow, with payload…

android-securitybinary-exploitationexploitation+5
2 days ago
SyscallRevenant preview

SyscallRevenant

GitHubsilentisvox/syscallrevenant

Clean Indirect Syscalls with Syscall Tampering.

binary-exploitationexploitationids-ips-evasion+6
13 days ago
TornadoC2 preview

TornadoC2

GitHubkamalx06/tornadoc2

Pull-based C2 framework with ten native transports, concurrent multi-profile handlers, ECDSA-signed tasking, and a multi-operator team server with…

command-and-controlcryptographyids-ips-evasion+9
26 days ago
memory-relocalloc preview

memory-relocalloc

GitHubgmh5225/memory-relocalloc

C proof-of-concept that locates code caves in the .reloc section of mapped DLLs to allocate and execute small shellcode, replacing typical memory…

binary-exploitationexploitationmalware-analysis+6
24 years ago
Decepticon preview

Decepticon

GitHubbittersecurity/decepticon

Autonomous LLM red team agent that plans and executes full attack chains—recon, exploitation, privilege escalation, lateral movement and C2—inside an…

ai-securitycommand-and-controlexploitation+9
6.4k11h 32m ago
InjectSetConsole preview

InjectSetConsole

GitHubtwosevenonet/injectsetconsole

Proof of Concept for Process Code Injection Without Using WriteProcessMemory

command-and-controlexploitationids-ips-evasion+7
15225 days ago
NTDLL-reconstruction preview

NTDLL-reconstruction

GitHubsk4r4b/ntdll-reconstruction

A technique that mixes NTDLL unhooking and hellsgate gate varients

binary-exploitationdefensive-toolsids-ips-evasion+6
336 days ago
Overthrone preview

Overthrone

GitHubkarmanya03/overthrone

All-Rust Active Directory exploitation framework: LDAP/SMB/Kerberos enumeration, attack-graph pathfinding, Kerberoasting, NTLM relay, ticket forging,…

command-and-controlexploit-frameworksinformation-gathering+8
301 month ago
Chimay-Red preview

Chimay-Red

GitHubbignerd95/chimay-red

Working POC of Mikrotik exploit from Vault 7 CIA Leaks

binary-exploitationembedded-systems-securityexploitation+8
6684 years ago
glimmer preview

glimmer

GitHublinnemanlabs/glimmer

Adversary emulation and C2 framework for security research

command-and-controlcryptographydata-exfiltration+8
55 months ago
ultrasploiter preview

ultrasploiter

GitLabvqkro/ultrasploiter

A single binary that folds a port scanner, the full Exploit-DB index (47k entries) and runnable exploit modules into one tool. Written in Rust, runs…

command-and-controlexploitationexploit-frameworks+9
11 days ago
veneficus-implant-public preview

veneficus-implant-public

GitHubabraxas/veneficus-implant-public

Spicy malware 0day. Full kill-chain malware: exploit, pivot, c2, persistence. Rust converted to pseudo-code - if you're smart you can build it…
command-and-controldata-exfiltrationexploitation+9
1 month ago
Nginx-chain-Rift-Poolslip preview

Nginx-chain-Rift-Poolslip

GitHuby198nt/nginx-chain-rift-poolslip

ASLR-independent nginx RCE chain PoC combining the PoolSlip heap over-read leak (CVE-2026-9256) with the rift overflow (CVE-2026-42945) to reach…

binary-exploitationeducationexploitation+7
144 months ago
veneficus preview

veneficus

GitHubabraxas/veneficus

Super elite end-to-end implant 0day. Full kill-chain. Exploit, escalate, pivot, poison, persistence.

command-and-controldata-exfiltrationids-ips-evasion+8
21 month ago
lockjaw preview

lockjaw

GitHubg13net/lockjaw

Modular Windows C2 framework with a Rust teamserver, Zig implant, indirect syscalls, AMSI bypass, reflective/PoolParty injection, in-memory BOF…

command-and-controldns-analysisexploit-frameworks+9
3322 days ago
evil-winrm-py preview

evil-winrm-py

GitHubadityatelange/evil-winrm-py

Execute commands interactively on remote Windows machines using the WinRM protocol (just faster)

authenticationcommand-and-controllateral-movement+7
41211 days ago
Previous12…39Next
