
CnaEmulator
 iterat0r/cnaemulator
Standalone emulation and testing harness for Cobalt Strike Aggressor Scripts (.cna) that validates syntax, mocks Beacon APIs, and executes BOFs via…
command-and-controldynamic-analysis-sandboxingeducation+7
22
iterat0r/cnaemulatorStandalone emulation and testing harness for Cobalt Strike Aggressor Scripts (.cna) that validates syntax, mocks Beacon APIs, and executes BOFs via…
 vsvalinx/cve-2025-5548
Educational repository documenting the full exploitation lifecycle of a stack buffer overflow in FreeFloat FTP Server 1.0, including fuzzing, EIP…
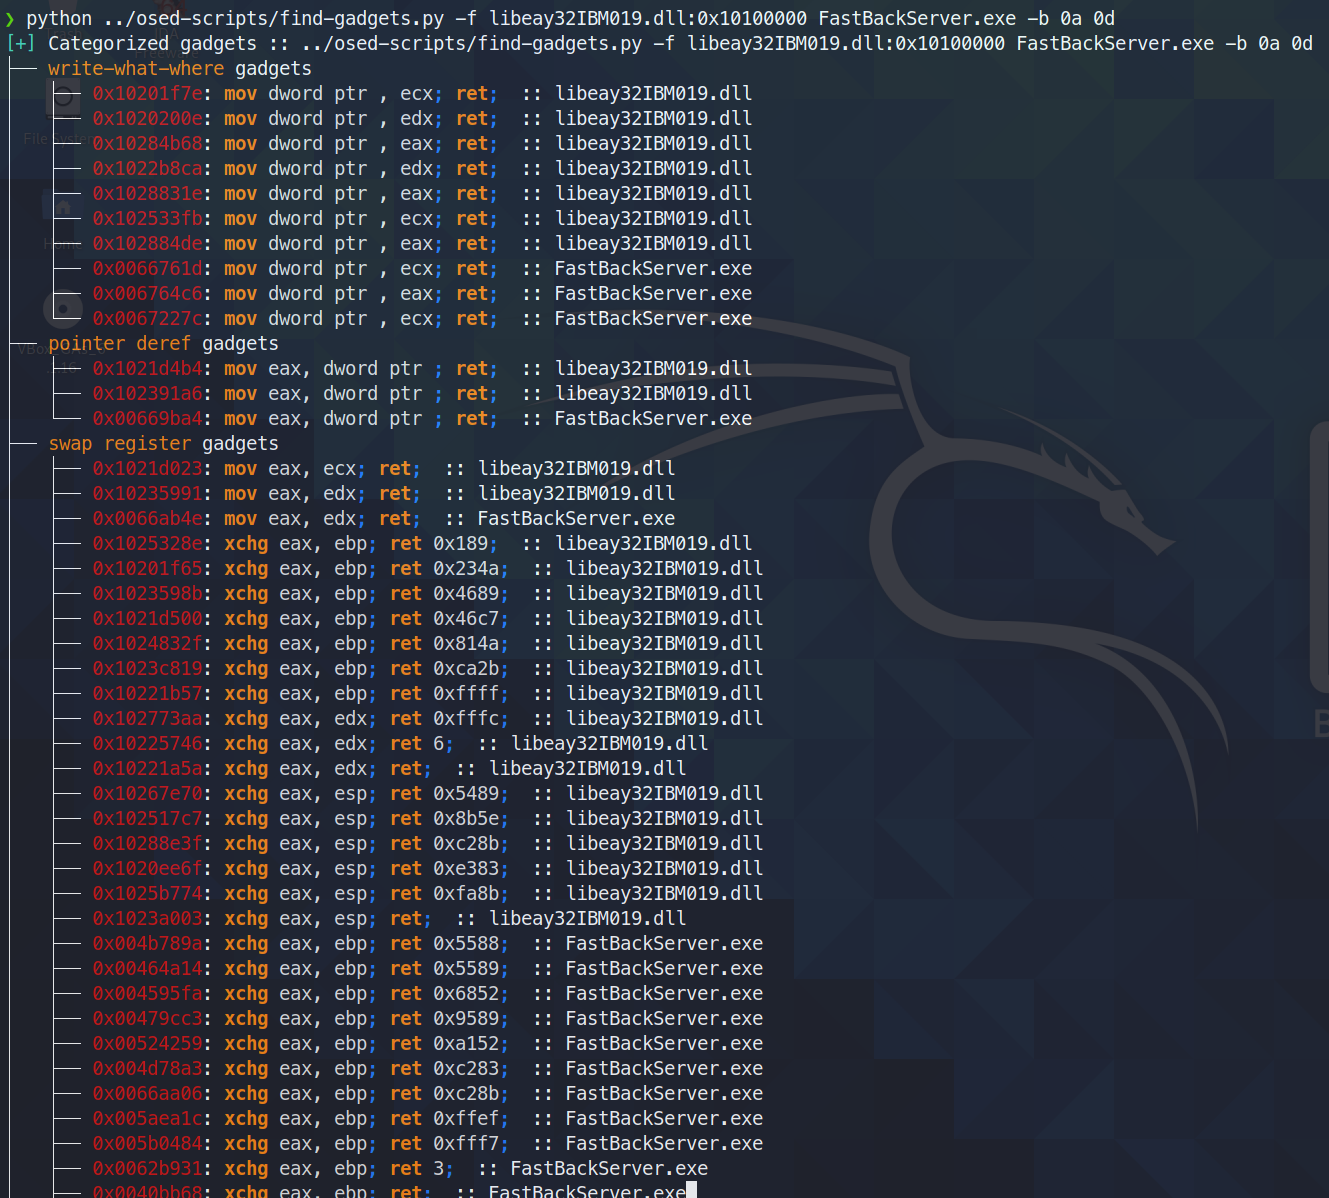 epi052/osed-scripts
bespoke tooling for offensive security's Windows Usermode Exploit Dev course (OSED)
 diego57709/cve-2025-5548
Structured lab for controlled exploitation of CVE-2025-5548 (FreeFloat FTP Server). Includes environment setup, fuzzing, EIP control, badchars…

 blacksnufkin/litterbox
A self-hosted sandbox for red teams to test payloads against modern detection before deployment. MCP integration lets an LLM agent drive analysis end…
 vrikodar/cve-2003-0264_exploit
Buffer Overflow in Seattle Lab Mail (SLmail) 5.5 - POP3
 raulsineiro/cve-2025-5548
Binary exploitation laboratory: Environment setup and step-by-step walkthrough for exploiting CVE-2025-5548 using Ghidra, Immunity Debugger, and…
 popclom/cve-2025-5548
Step-by-step guide to exploit a buffer overflow in FreeFloat FTP Server using Python fuzzing, Immunity Debugger with mona.py, and IDA Free for binary…
 fkshield/cve-2025-5548
End-to-end exploitation lab for CVE-2025-5548 (FreeFloat FTP Server stack buffer overflow). Includes static analysis with IDA/Ghidra, binary fuzzing,…
 elrajiii/cve-2025-5548
Buffer overflow in FreeFloat FTP Server 1.0
 charlyrr/cve-2025-5548
Educational lab documenting step-by-step exploitation of CVE-2025-5548 (Stack Buffer Overflow) on Windows 11, from fuzzing and crash analysis to…
 javyan05/cve-2025-5548
Entorno y explotación de la vulnerabilidad CVE-2025-5548
 iamescri/cve-2025-5548-freefloat-ftp-buffer-overflow
Laboratorio de análisis y explotación de la vulnerabilidad CVE-2025-5548 en FreeFloat FTP Server 1.0
 anasrami12/cve-2025-5548
Methodology for vulnerability analysis and exploit development, covering static/dynamic analysis, fuzzing, patch diffing, and 0-day research with…
 alberto-galindo/cve-2025-5548
Security research and reproduction of CVE-2025-5548: A stack-based buffer overflow in FreeFloat FTP Server 1.0. Includes binary analysis, crash…
 biitts/cve-2026-53753-crawl4ai-rce
CVE-2026-53753 — Crawl4AI <0.8.7 unauthenticated RCE (AST sandbox escape via gi_frame.f_back). Lab + PoC, verified e2e.