
CVE-2026-29053
 k3ystr0k3r/cve-2026-29053
Python PoC and version scanner for CVE-2026-29053, an authenticated RCE in Ghost CMS below 6.19.1 via malicious Handlebars theme templates.
exploitationpayload-developmentpenetration-testing+5
1
k3ystr0k3r/cve-2026-29053Python PoC and version scanner for CVE-2026-29053, an authenticated RCE in Ghost CMS below 6.19.1 via malicious Handlebars theme templates.
 arensballiu/cve-2026-33017-langflow-rce
Proof-of-concept for CVE-2026-33017, demonstrating unauthenticated remote code execution in vulnerable Langflow versions through malicious…
 arensballiu/flowise-rce-cve-2025-59528
Python PoC exploit for CVE-2025-59528, achieving authenticated RCE on Flowise AI <= 3.0.4 via the customMCP endpoint and Node.js…
 d3ext/cve-2024-25641
Proof-of-concept exploit for CVE-2024-25641, an authenticated RCE in Cacti 1.2.26 via the Package Import feature, enabling arbitrary PHP code…
 cr4sh/smmbackdoor
First open source and publicly available System Management Mode backdoor for UEFI based platforms. Good as general purpose playground for various SMM…
 3gstudent/homework-of-python
Python codes of my blog.
 kaanaryoverflow/ipfire-2-25-auth-rce
ipfire 2.25 authenticated remote code execution
 secretsquirrel/the-backdoor-factory
Patch PE, ELF, Mach-O binaries with shellcode new version in development, available only to sponsors
 u0pattern/cve-2018-1000117-exploit
Buffer Overflow Vulnerability that can result ACE
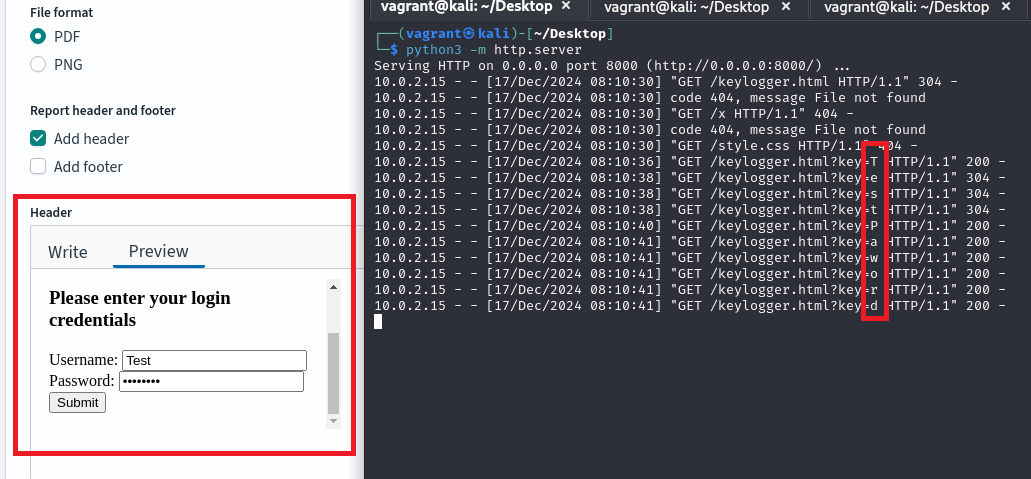 jflye/cve-2024-54160-opensearch-html-and-injection-stored-xss
Proof-of-concept exploit for CVE-2024-54160 demonstrating stored XSS and HTML injection in OpenSearch Reports plugin via malicious iframe payload in…
 lucaspdiniz/cve-2021-44228
Log4j Vulnerability RCE - CVE-2021-44228
 princeaikinsbaidoo/cve-2022-41840-poc
This is the PoC exploit for CVE-2022-41840, running Zenario
 themiddleblue/cve-2019-11043
(PoC) Python version of CVE-2019-11043 exploit by neex
 fran-cics/exploittensorflowcve-2021-37678
TP Seguridad Informática UTN FRBA 2021
 darrynb89/cve-2004-1561
Python port of a Metasploit exploit targeting CVE-2004-1561 for remote code execution. Designed for penetration testing and vulnerability validation…
 josemlwdf/cve-2019-13272
This is a Python 3 version of this exploit. Hope it works!!!
 cybersecplayground/cve-2025-24016-wazuh-remote-code-execution-rce-poc
A critical RCE vulnerability has been identified in the Wazuh server due to unsafe deserialization in the wazuh-manager package. This bug affects…
 cowsecurity/cve-2022-23935
Python exploit PoC for CVE-2022-23935 targeting exiftool 12.37, enabling remote code execution via crafted image files.