
CVE-2026-40003
 rva3/cve-2026-40003
Exploit for CVE-2026-40003, an arbitrary memory write vulnerability in ZXIC/Sanechips ZX297520V3 SoC BootROM, enabling code execution via USB…
binary-exploitationembedded-systems-securityexploitation+4
16
rva3/cve-2026-40003Exploit for CVE-2026-40003, an arbitrary memory write vulnerability in ZXIC/Sanechips ZX297520V3 SoC BootROM, enabling code execution via USB…
 mbanyamer/cve-2026-27180-majordomo-unauthenticated-rce
Proof-of-concept exploit for CVE-2026-27180, an unauthenticated RCE in MajorDoMo via update URL poisoning, delivering a webshell to the web root.
 defhacks/cve-2021-4034
Rust implementation of the CVE-2021-4034 pkexec privilege escalation exploit, with scripts to download and unpack a vulnerable pkexec for testing.
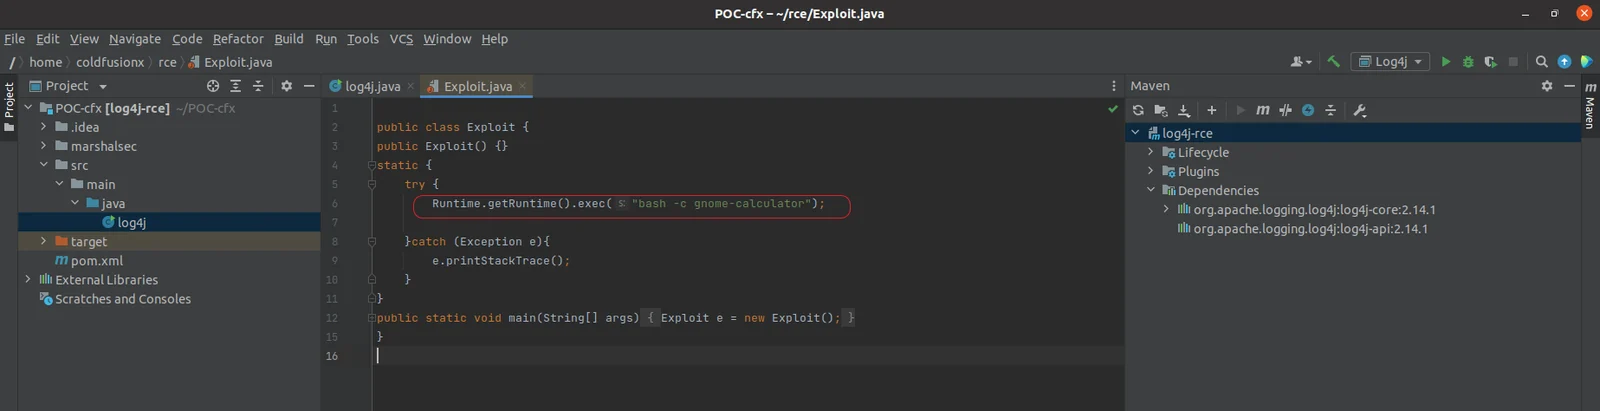 coldfusionx/cve-2021-44228-log4shell-poc
Proof-of-concept for Log4Shell (CVE-2021-44228) demonstrating JNDI-based remote code execution via LDAP and HTTP servers.
 gmh5225/aether-c2-framework
🛠️ Explore custom C2 TTPs with Aether-C2-Framework, focusing on lightweight Rust implants and stealthy transport stacks to reduce forensic…
 virtualalllocex/payload-download-cradles
This are different types of download cradles which should be an inspiration to play and create new download cradles to bypass AV/EPP/EDR in context…
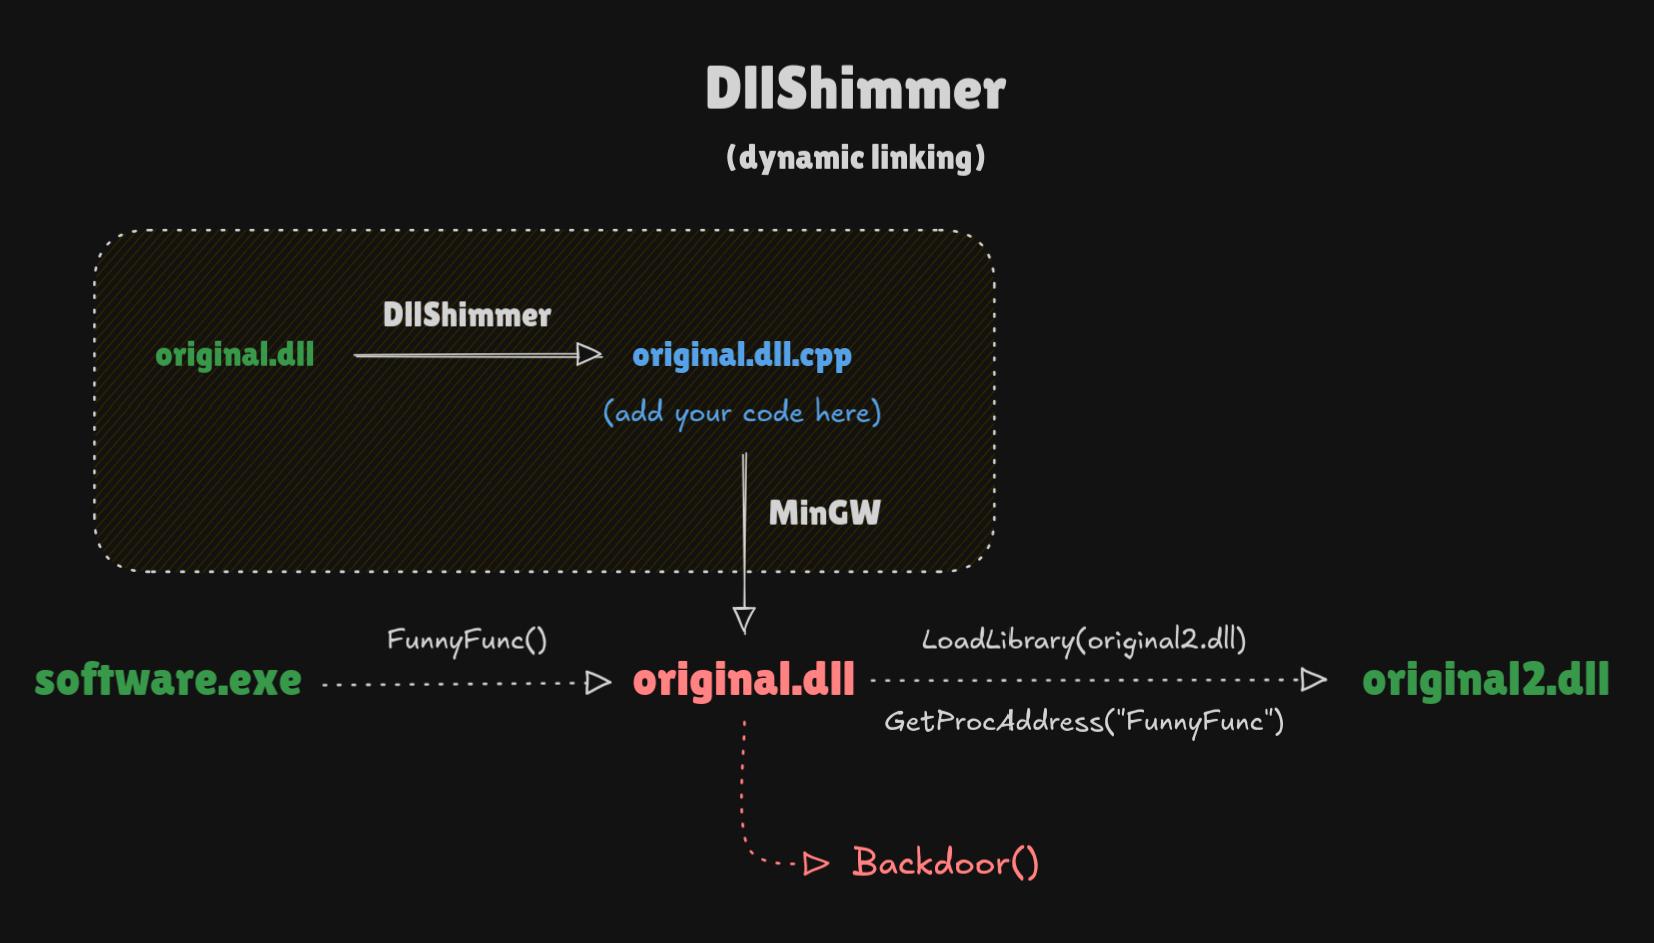 print3m/dllshimmer
Weaponize DLL hijacking easily. Backdoor any function in any DLL.
 george0papasotiriou/cve-2026-22004-git-lfs-pointer-poisoning-supply-chain-
Proof-of-concept for Git LFS pointer poisoning, with Bash and Python scripts that create a malicious repository, simulate a rogue LFS server, and…
 edubr2020/rp_import_rce
Proof-of-concept exploit for RealPlayer arbitrary file download and directory traversal leading to remote code execution via Import() method.
 jonstratton/selenium-node-takeover-kit
A collection of selenium tests that might aid it takeover of a selenium node
 wooluo/cve-2022-25581
Python exploit script for CVE-2022-25581 (ClassCMS 2.4 arbitrary file download) that automates login, CSRF token extraction, malicious zip upload…
 tinopreter/docviewerexploitapp
This is an Exploit App I made when solving the DocumentViewer challenge (CVE-2021-40724) from MobileHackingLab. It will download a libdocviewe_pro.so…
 orf53975/rig-exploit-for-cve-2018-8174
Rig Exploit for CVE-2018-8174 As with its previous campaigns, Rig’s Seamless campaign uses malvertising. In this case, the malvertisements have a…
 joebeeton/cve-2024-4701-poc
POC for CVE-2024-4701
 r00t4dm/cve-2018-14667
about CVE-2018-14667 from RichFaces Framework 3.3.4
 bo0l3an/cve-2024-49112-poc
CVE-2024-49112 LDAP RCE PoC and Metasploit Module
 w01fh4cker/cve-2025-30406
Exploit for CVE-2025-30406