

glimmer
 linnemanlabs/glimmer
Adversary emulation and C2 framework for security research
command-and-controlcryptographydata-exfiltration+8
55 months ago
linnemanlabs/glimmerAdversary emulation and C2 framework for security research
 snailsploit/claude-red
Curated library of 78 offensive security SKILL.md modules that prime Claude with expert red team methodology across web, AD, wireless, cloud, and…
 zimawhit3/bitmancer
Nim Library for Offensive Security Development
 lsecqt/offensivecpp
This repo contains C/C++ snippets that can be handy in specific offensive scenarios.
 flangvik/obfuscatedsharpcollection
Attempt at Obfuscated version of SharpCollection
 yo-yo-yo-jbo/macos_app_structure
Educational deep dive into macOS app bundles, plist files, and launchd process behavior, with offensive security notes on packaging payloads as .app…
 hackerhouse-opensource/offensivelua
Offensive Lua.
 luemmelsec/pentest-tools-collection
Curated collection of offensive security tools and commands for Active Directory attacks, C2, privilege escalation, obfuscation, and web pentesting.
 agampreet-singh/redroot
RedRoot is a Python-based, CLI-driven offensive security framework that brings essential red teaming tools into one unified terminal environment.…
 0x00pf/0x00sec_code
Educational repository of offensive security source code: remote shells, ELF injectors, crypters, memory injection, and droppers for Linux,…
 reverseclabs/c3
Custom Command and Control (C3). A framework for rapid prototyping of custom C2 channels, while still providing integration with existing offensive…
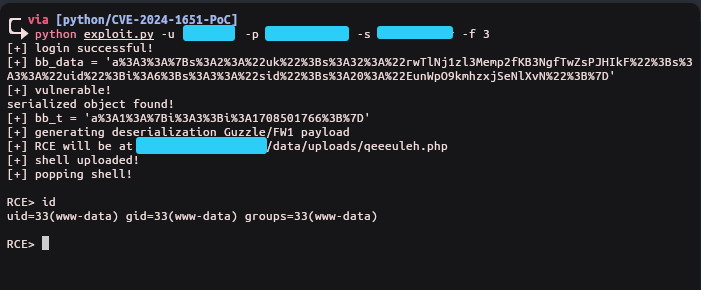 sharpicx/cve-2024-1651-poc
Torrentpier v2.4.1. CVE-2024-1651. Remote Code Execution (RCE). Exploit.
 baktistr/cve-2025-62726-poc
This is a proof-of-concept demonstration for CVE-2025-62726, created for educational purposes as part of a class project. Part of CMU Course : 18-739…
 whiteh4twolf/cve-2024-1651-poc
Proof-of-concept exploit for CVE-2024-1651, demonstrating insecure deserialization to achieve remote code execution. Provides a fast, easy-to-use…
 zeop-cybersec/word_mshtml
Contains the offensive (exploit and auxiliary) modules for the CVE-2021-40444.
 sia-iotechnology/kittysploit-framework
Python Exploitation Framework, V8 Engine Debugger, Proxy interceptor, marketplace, post-exploitation, backdoor generator,....
 brucedevices/firmware
Predatory ESP32 Firmware
 samratashok/kautilya
Kautilya - Tool for easy use of Human Interface Devices for offensive security and penetration testing.