external-c2-experiments

Go external C2 module for go-exploit that catches reverse SSH shells, providing a server listener and payload client for integrating custom C2…

Go external C2 module for go-exploit that catches reverse SSH shells, providing a server listener and payload client for integrating custom C2…

Python proof-of-concept for CVE-2026-67401, an authenticated SQL injection in cPanel EmailTrack that allows arbitrary file write as root via SQLite…

Python exploit for Serv-U SSH vulnerability (CVE-2021-35211) with multiple payload modes: stage, exec, and download-execute, enabling shellcode…

SSH RCE PoC CVE-2024-6387

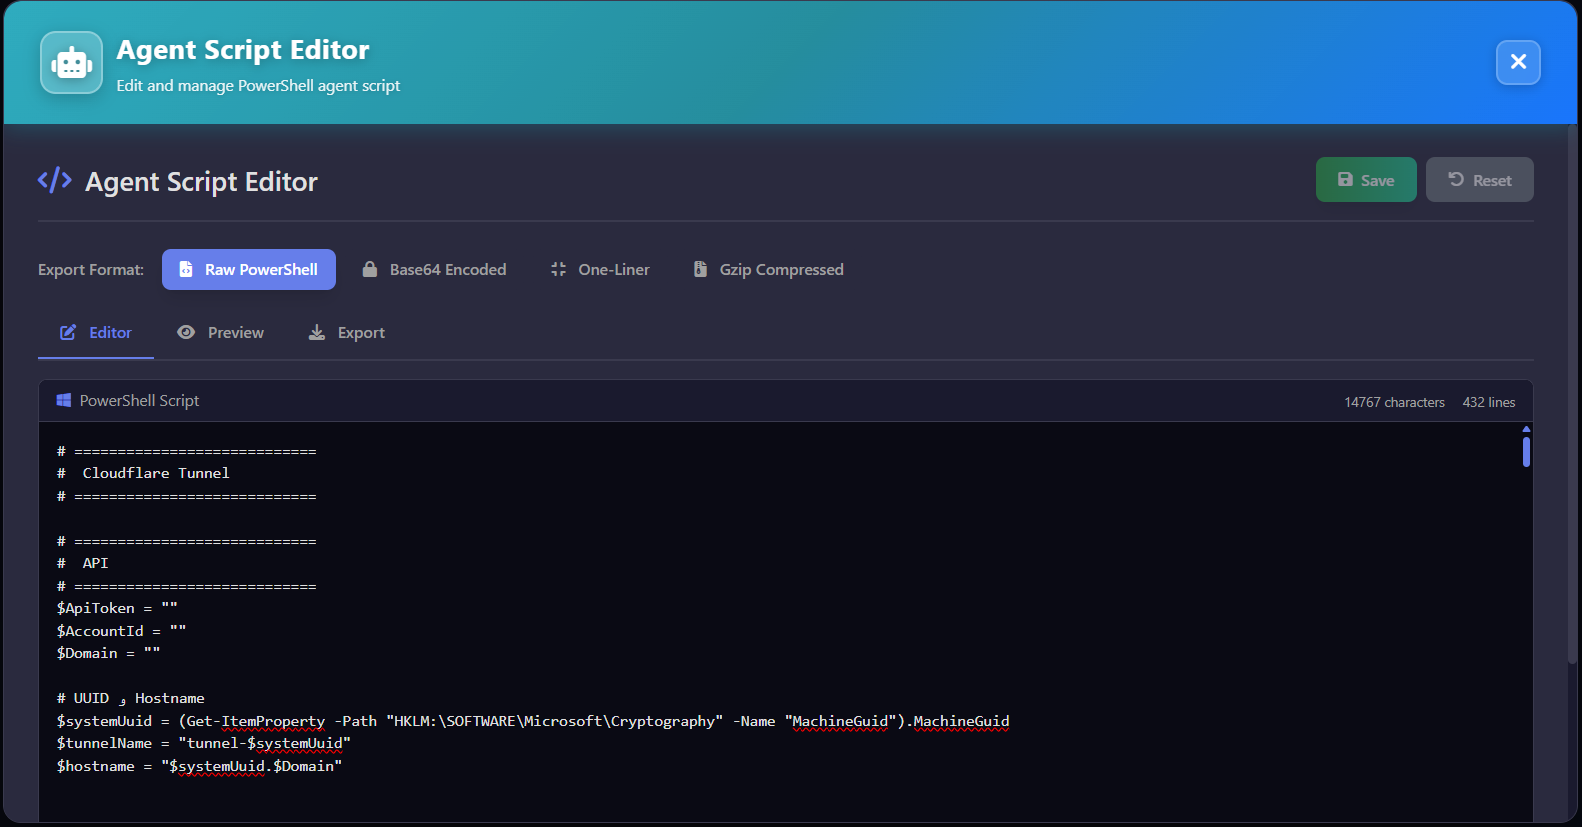
🔒 Modern C2 Platform with Cloudflare Tunnel Integration | WinRM & SSH Remote Management | Real-time Terminal & Remote Desktop | Built with FastAPI &…

A Simple Python Program that uses gets a Remote Root Shell on the Target Device by exploiting a Vulnerability (CVE-2011-2523) present in vsFTP 2.3.4

Missing Authentication for Critical Function (CWE-306)-Exploit

Proof-of-concept exploit for CVE-2025-32433, a pre-authentication RCE in Erlang/OTP SSH daemon. Includes Python script to send crafted SSH channel…

Proof-of-concept exploit for CVE-2024-6387 targeting vulnerable OpenSSH servers via heap manipulation and race condition to achieve remote code…

Proof of concept (POC) for CVE-2024-45337

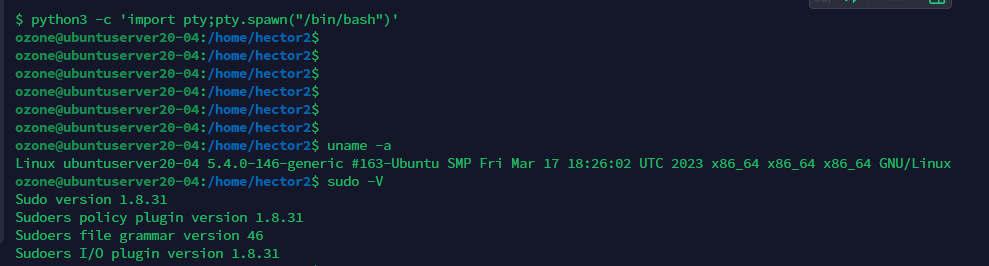
Exploit for Ubuntu 20.04 using CVE-2021-3156 enhanced with post-exploitation scripts

Python-based exploit for CVE-2018-15473, enabling SSH user enumeration via OpenSSH username validation timing attack. Updated from Python 2 to 3 for…

Proof-of-concept exploit for CVE-2017-1000117: remote code execution via malicious git submodule SSH URL, enabling reverse shell payload delivery…

This repository contains alternative payload approaches for the InvokeAI RCE vulnerability (CVE-2024-12029) when SSH key injection fails. The…

Proof of concept python script for regreSSHion exploit.

Proof-of-concept exploit for CVE-2022-40684 authentication bypass in Fortinet FortiOS, FortiProxy, and FortiSwitchManager. Injects SSH keys via…

Exploit for CVE-2014-4210 targeting WebLogic deserialization, with post-exploitation features including ransomware deployment, C2 integration, and…

SSH Exploit for CVE-2024-6387 : RCE in OpenSSH's server, on glibc-based Linux systems