CVE-2022-34302
Demonstrates CVE-2022-34302, a Secure Boot bypass via the New Horizon Datasys signed bootloader whose built-in custom PE/COFF loader executes…

Demonstrates CVE-2022-34302, a Secure Boot bypass via the New Horizon Datasys signed bootloader whose built-in custom PE/COFF loader executes…

Demonstrates CVE-2022-34303 Secure Boot bypass via CryptoPro signed UEFI Shell, using the mm command to nullify gSecurity2 and load unsigned UEFI…

Windows privilege escalation tool that abuses SeImpersonatePrivilege via indirect syscalls, patching ETW and AMSI to elevate from service account or…

Header-only Windows x64 indirect syscall library. Zero CRT, zero IAT, VEH anti-BP, AMSI/ETW bypass, W^X memory, per-call dynamic stubs.

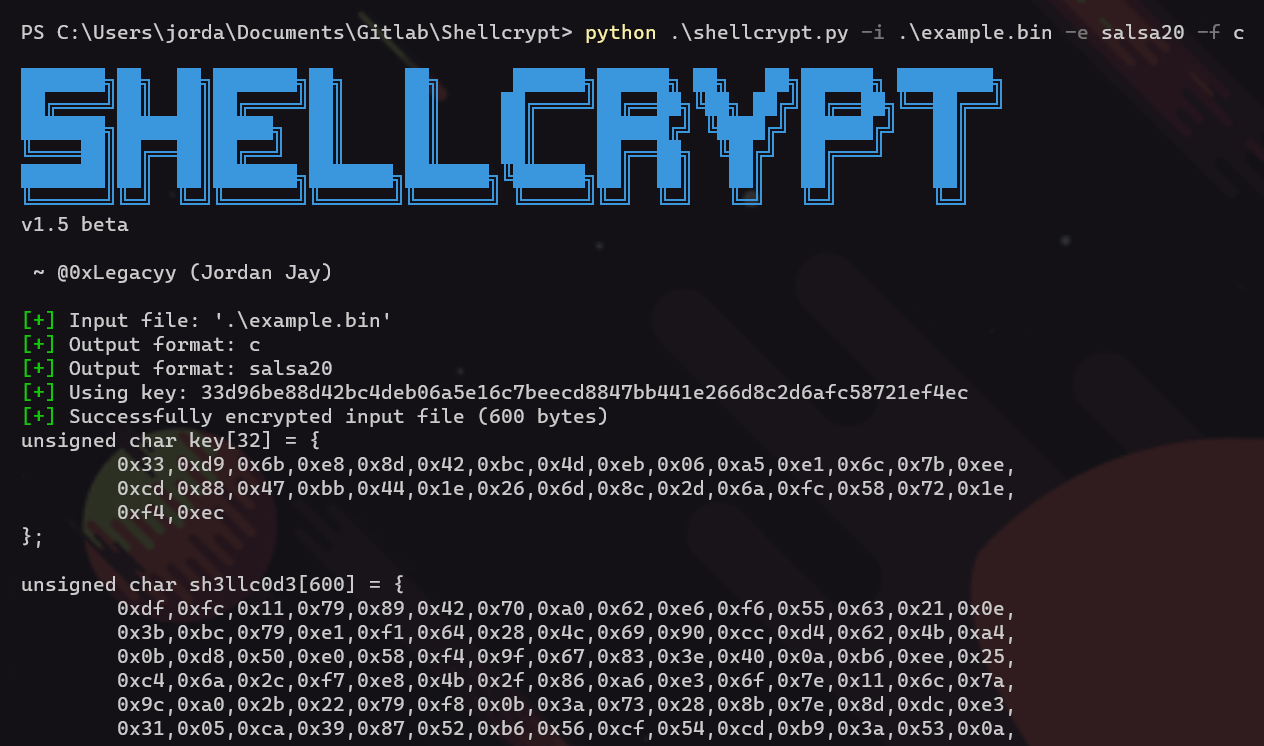
Python-based crypter that obfuscates payloads to bypass antivirus and EDR, generating FUD stubs for red team operations.

Exploit for CVE-2021-4034, a local privilege escalation in polkit's pkexec, providing a root shell via a shared library and GCONV path manipulation.

Proof-of-concept exploit for CVE-2026-30345, an arbitrary file write in CTFd backup import, enabling persistent backdoor via .bashrc.

Exploit for CVE-2021-4034, a local privilege escalation in polkit's pkexec, providing a root shell via a shared library and GCONV_PATH manipulation.

Educational demonstration of the Log4Shell vulnerability (CVE-2021-44228) with JNDI LDAP payloads for experimental testing on your own systems.

Exploit for CVE-2019-2215 to gain temporary root on Xiaomi MIUI devices, enabling bootloader unlock and system modifications.

A QoL tool to obfuscate shellcode. In the future will be able to chain encoding/encryption/compression methods.

Root your Galaxy using CVE-2026-43499

Customizable Stage0 C2 framework with C and Rust agent templates, a Flask backend, and a React dashboard for building and operating your own C2…

Hide your payload into .jpg file

For when DLLMain is the only way

Indirect syscalls + DInvoke made simple.

Toolkit to weaponize Chromium vulnerabilities into reliable, cross-platform, full-chain exploits

All the materials for Gareth Heyes' Black Hat talk: CSS: the bomb inside your inbox.