
CVE-2026-34990-poc
Proof-of-concept exploit for CVE-2026-34990, a CUPS 2.4.16 local privilege escalation via arbitrary file write through CUPS_CREATE_LOCAL_PRINTER and…

Proof-of-concept exploit for CVE-2026-34990, a CUPS 2.4.16 local privilege escalation via arbitrary file write through CUPS_CREATE_LOCAL_PRINTER and…

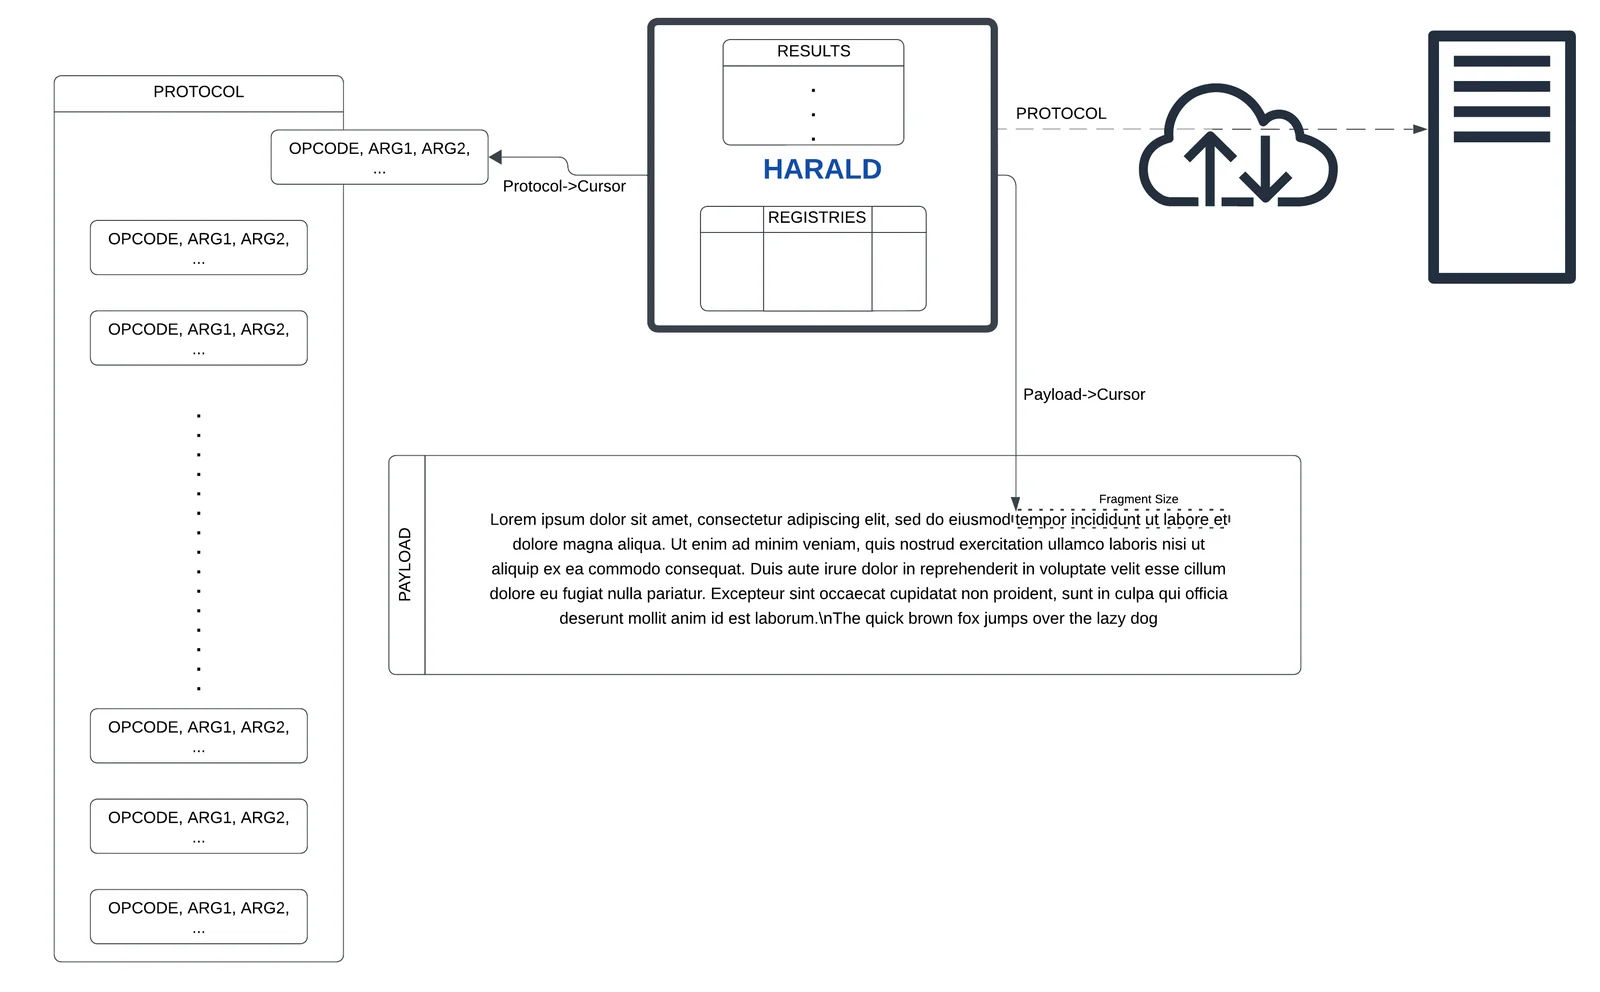
An in-memory minimal CPU for agnostic on-the-fly protocols creation

Proof-of-concept exploit for Firefox BrowsingContext authorization bypass (CVE-2026-4692), demonstrating forged IPC messages to set InRDMPane and…

OSCP-focused toolkit for read-only network, SMB, AD, DNS, web, and database enumeration; privesc scanning, hash identification, and…

C++ library that retrieves and spoofs Windows syscall arguments using hardware breakpoints and exception handlers to subvert EDR telemetry.

Win32 and Kernel abusing techniques for pentesters

Toolkit to weaponize Chromium vulnerabilities into reliable, cross-platform, full-chain exploits

Some codes for bypassing Oracle WebLogic CVE-2018-2628 patch

Git Web Hook Tunnel for C2

PoC of CVE-2024-33883, RCE vulnerability of ejs.

Proof-of-concept exploit for CVE-2024-10793 targeting WordPress wp-security-audit-log plugin. Demonstrates account takeover, privileged user…

The User Registration & Membership WordPress plugin before 4.1.2 does not prevent users to set their account role when the Membership Addon is…

Atlassian Jira unauthen template injection

exp for CVE-2019-0887

CVE-2017-7269 to webshell or shellcode loader

GEF (GDB Enhanced Features) - a modern experience for GDB with advanced debugging capabilities for exploit devs & reverse engineers on Linux

Proof of concept python script for regreSSHion exploit.

PoC for triggering buffer overflow via CVE-2020-0796