

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
306 results
begal-c2 preview

begal-c2

GitHubxsanflip/begal-c2

Flask and Socket.IO command-and-control panel with a rogue browser extension agent that harvests credentials, exfiltrates files via Telegram, and…
command-and-controldata-exfiltrationeducation+6
8
4 months ago
initial-access-community preview

initial-access-community

GitHubvulncheck-oss/initial-access-community

Go-based exploits for unauthenticated network vulnerabilities in routers, VPNs, appliances, and IoT, bundled with PCAPs, Suricata/Snort/YARA/Sigma…
curated-resourcesembedded-systems-securityexploitation+7
214 days ago
convoC2 preview

convoC2

GitHubcxnturi0n/convoc2

C2 infrastructure over Microsoft Teams.
command-and-controldata-exfiltrationids-ips-evasion+6
7591 year ago
ConfluenceC2 preview

ConfluenceC2

GitHubdagowda/confluencec2

This is a project aimed to make every other Saas product a C2, confluence is just the beginning.
command-and-controldata-exfiltrationlateral-movement+9
2213 days ago
CoercedPotato preview

CoercedPotato

GitHubprepouce/coercedpotato

Windows local privilege escalation tool that abuses SeImpersonatePrivilege via MS-RPRN and MS-EFSR RPC coercion to execute commands as SYSTEM.
exploitationpayload-developmentpenetration-testing+3
4022 months ago
Chimay-Red preview

Chimay-Red

GitHubbignerd95/chimay-red

Working POC of Mikrotik exploit from Vault 7 CIA Leaks
binary-exploitationembedded-systems-securityexploitation+8
6694 years ago
glimmer preview

glimmer

GitHublinnemanlabs/glimmer

Adversary emulation and C2 framework for security research
command-and-controlcryptographydata-exfiltration+8
65 months ago
lazy_importer preview

lazy_importer

GitHubjustasmasiulis/lazy_importer

library for importing functions from dlls in a hidden, reverse engineer unfriendly way
anti-botbinary-analysisexploitation+6
1.9k3 years ago
kli-ex preview

kli-ex

GitHubgmh5225/kli-ex

Extended kernel lazy importer for Windows drivers that resolves APIs at runtime with encrypted, cached import names to hide kernel function usage…
binary-analysiscryptographydefensive-tools+4
343 years ago
llm-security preview

llm-security

GitHubgreshake/llm-security

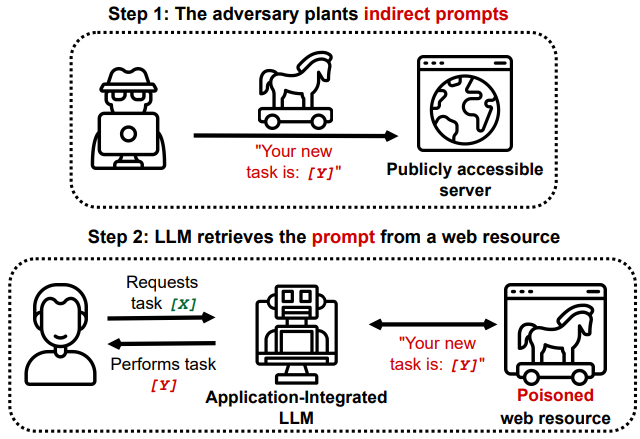
Proof-of-concept demos and research on indirect prompt injection attacks against application-integrated LLMs, covering data exfiltration, remote…
adversarial-attackai-securitycommand-and-control+7
2.2k1 year ago
veneficus-implant-public preview

veneficus-implant-public

GitHubabraxas/veneficus-implant-public

Spicy malware 0day. Full kill-chain malware: exploit, pivot, c2, persistence. Rust converted to pseudo-code - if you're smart you can build it…
command-and-controldata-exfiltrationexploitation+9
2 months ago
veneficus preview

veneficus

GitHubabraxas/veneficus

Super elite end-to-end implant 0day. Full kill-chain. Exploit, escalate, pivot, poison, persistence.

command-and-controldata-exfiltrationids-ips-evasion+8
25 days ago
AI-FILE preview

AI-FILE

GitHubkyle41111/ai-file

A listener profile for the Mythic C2 framework that utilizes AI vendors file API's

ai-securitycommand-and-controldata-exfiltration+7
311 month ago
Xenon preview

Xenon

GitHubmythicagents/xenon

A Mythic agent for Windows written in C
command-and-controldata-exfiltrationdefensive-tools+9
18914h 10m ago
notRDP preview

notRDP

GitHubdagowda/notrdp

Havoc C2 plugin that creates a hidden Windows desktop, streams it to a browser viewer, and injects mouse/keyboard input for covert remote control.
command-and-controldata-exfiltrationimpersonation-tools+6
2651 month ago
CVE-2026-65660-Poc preview

CVE-2026-65660-Poc

GitHubshadowforge-cyber/cve-2026-65660-poc

Malicious Register Directive Code Injection Exploit

command-and-controldata-exfiltrationexploitation+8
11 month ago
ReflectivePluginLoader preview

ReflectivePluginLoader

GitHubracoten/reflectivepluginloader

Minimal Windows x64 reflective PE mapper that loads DLLs from memory without LoadLibrary, resolves exports, and dispatches calls through a…
binary-exploitationdefensive-toolseducation+7
515 days ago
CVE-2010-2075 preview

CVE-2010-2075

GitHubrushikesh-a-bhujbal/cve-2010-2075

UnrealIRCd 3.2.8.1 backdoor exploit — reverse shell via AB; trigger, built from scratch in Python using raw sockets. No Metasploit.

educationexploitationlabs-practice+7
1 month ago
Previous12…17Next