
esp8266-injection-example
 pulkin/esp8266-injection-example
Example project to demonstrate packet injection / sniffer capabilities of ESP8266 IC.
embedded-systems-securityexploitationhardware-hacking+6
368
pulkin/esp8266-injection-exampleExample project to demonstrate packet injection / sniffer capabilities of ESP8266 IC.
 baguette168/nmg
Generates parameterized .NET memory-shell payloads (VPP, MVC route, HttpListener) compatible with Godzilla, Behinder, and AntSword clients for red…
 proviesec/xss-payload-list
Curated collection of cross-site scripting payloads, polyglots, and injection test rules for web application penetration testing and bug bounty…
 1llu50ry/mcp-gamehacking
MCP server exposing a 4,100+ skill game-hacking and reverse-engineering knowledge base with source archives, specialized agents, subagents, plugins…
 r3n3r0/cve-2026-0006-step-2
Research package demonstrating a leak-assisted ROP chain in Android media.swcodec via the CVE-2026-0006 APV decoder heap overflow, with payload…
 bittersecurity/decepticon
Autonomous LLM red team agent that plans and executes full attack chains—recon, exploitation, privilege escalation, lateral movement and C2—inside an…
 karmanya03/overthrone
All-Rust Active Directory exploitation framework: LDAP/SMB/Kerberos enumeration, attack-graph pathfinding, Kerberoasting, NTLM relay, ticket forging,…
 bignerd95/chimay-red
Working POC of Mikrotik exploit from Vault 7 CIA Leaks
 justasmasiulis/lazy_importer
library for importing functions from dlls in a hidden, reverse engineer unfriendly way

 vqkro/ultrasploiter
A single binary that folds a port scanner, the full Exploit-DB index (47k entries) and runnable exploit modules into one tool. Written in Rust, runs…
 abraxas/veneficus-implant-public
Spicy malware 0day. Full kill-chain malware: exploit, pivot, c2, persistence. Rust converted to pseudo-code - if you're smart you can build it…
 si13nttt/cve-2025-32432
Python PoC exploiting CVE-2025-32432, an unauthenticated RCE in Craft CMS via Yii DI gadget injection, with assetId scanning, reverse shell, and…
 murrez/cve-2026-102425
Python PoC for CVE-2026-102425: unauthenticated RCE in Joomla Balbooa Forms (com_baforms) via field shortcode injection in post-submission PHP…
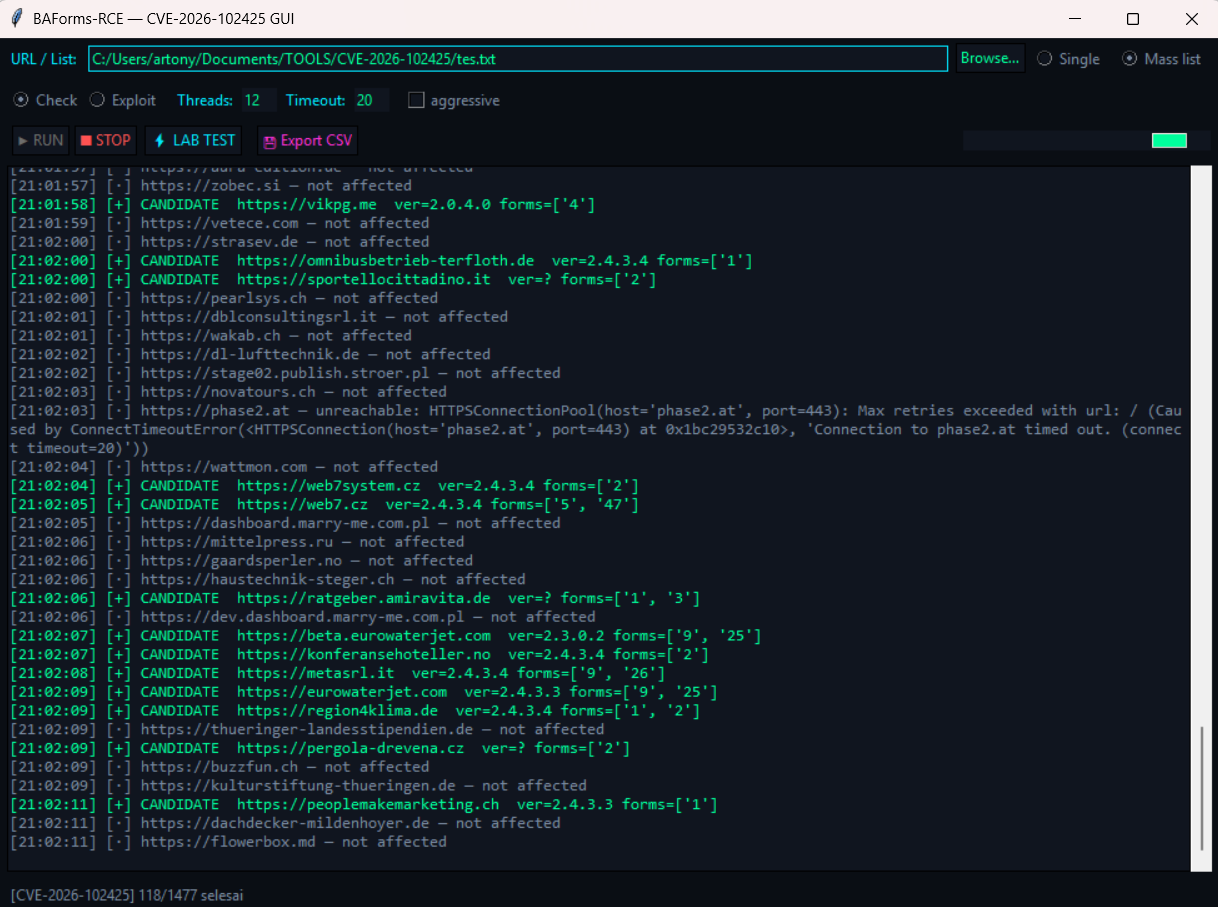 tonydelouvre/cve-2026-102425
GUI scanner and exploit for CVE-2026-102425, an unauthenticated RCE in Balbooa Forms (com_baforms) via PHP shortcode injection, with mass scanning…
 x86byte/adm-zip_lpe-poc
CVE-2026-102282: Local Privilege Escalation via SUID/SGID preservation during archive extraction
 murrez/cve-2026-100721
Python PoC for CVE-2026-100721: detects and exploits vm2 <3.12.2 NodeVM external allowlist bypass, achieving sandbox escape and host RCE via local…
 wuyou6956-glitch/cve-2026-1668-poc
Proof-of-concept exploit for CVE-2026-1668 in TP-Link switch firmware, delivering a MIPS payload that yields a root shell on vulnerable devices.
 murrez/cve-2026-18143
Python PoC that checks and exploits CVE-2026-18143, an unauthenticated arbitrary file upload in Addify Request a Quote for WooCommerce ≤ 2.9.2 via…