

Harald
 gmh5225/harald
An in-memory minimal CPU for agnostic on-the-fly protocols creation
command-and-controlexploitationids-ips-evasion+6
gmh5225/haraldAn in-memory minimal CPU for agnostic on-the-fly protocols creation
 hhesenjan/cve-2023-27163-and-mailtrail-v0.53
Python exploit chaining CVE-2023-27163 SSRF in Requests Baskets with Mailtrail v0.53 to forward internal services and execute a reverse shell.
 lyravoid/folkpatch
Root access to the kernel can be achieved simply by patching the Boot partition for reflashing. This solution is based on a non-parallel extended…
 lunasec-io/spring4shell-poc
This is a dockerized application that is vulnerable to the Spring4Shell vulnerability (CVE-2022-22965).
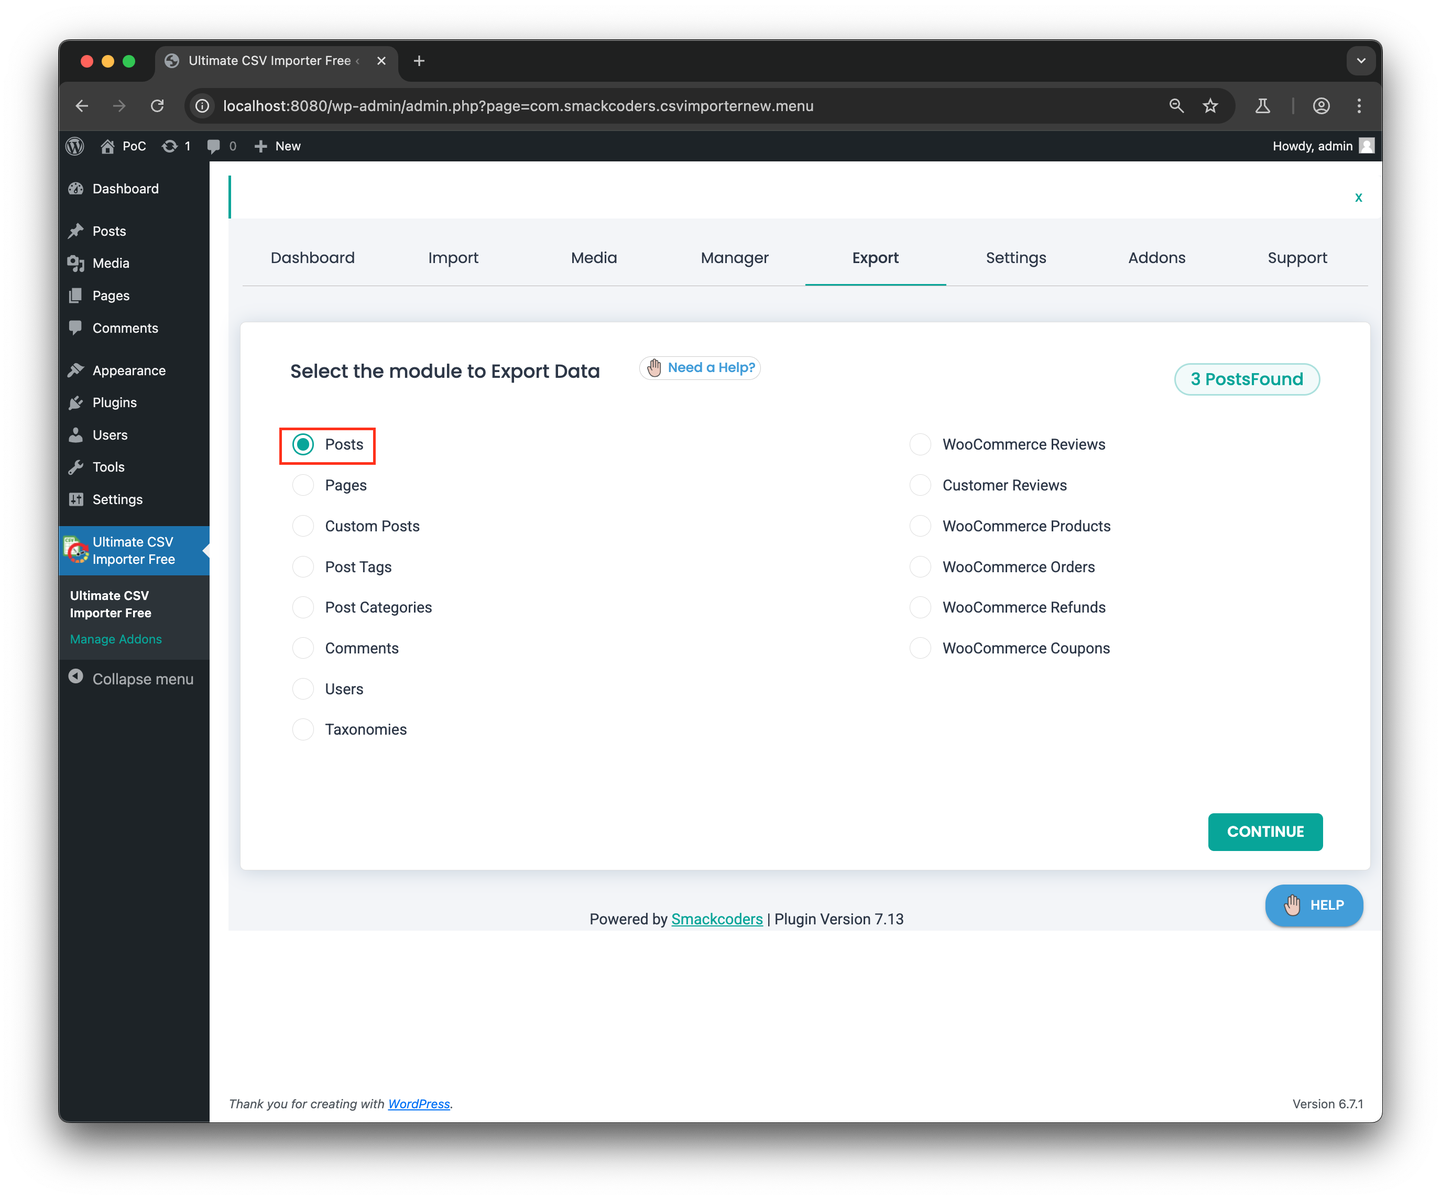 dottak/cve-2024-56278
Proof-of-concept exploit for CVE-2024-56278, a remote code execution vulnerability in the WP Ultimate Exporter WordPress plugin, demonstrating file…
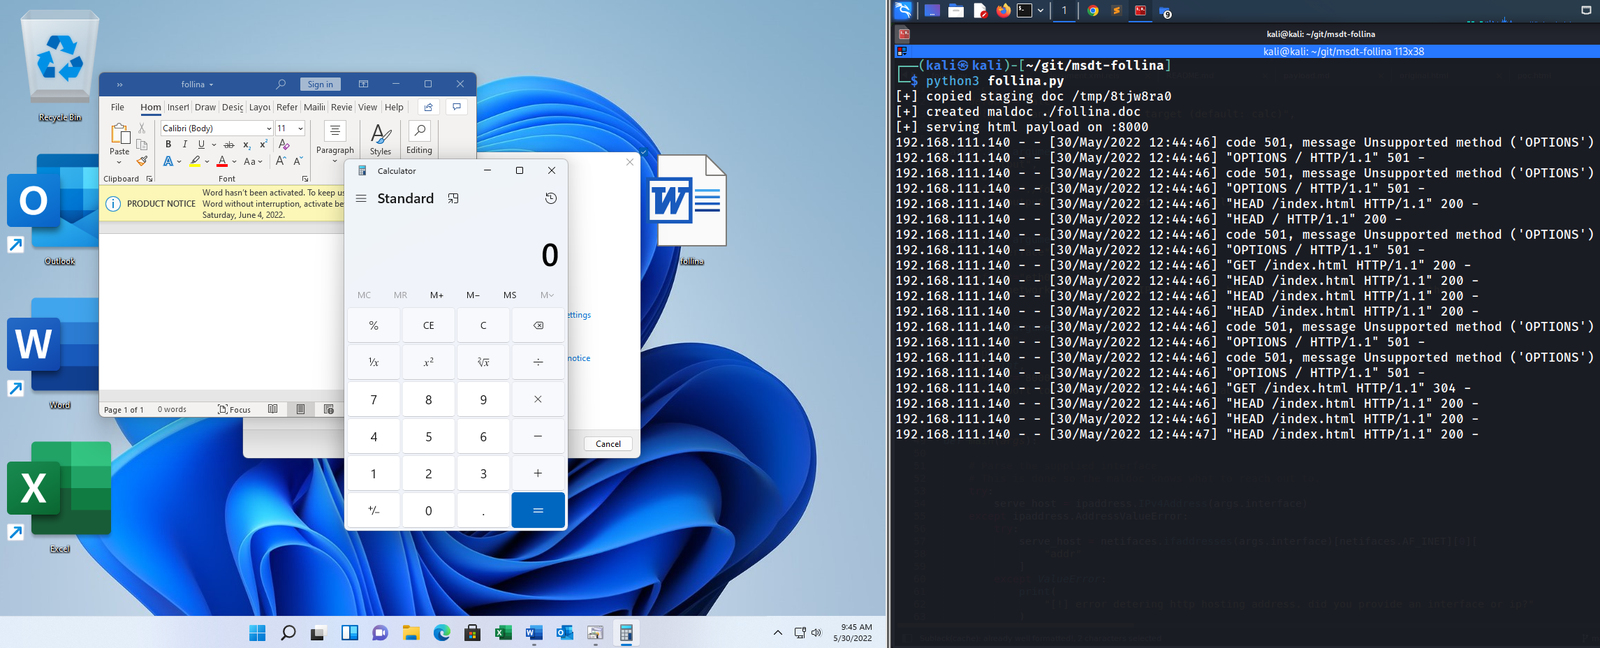 johnhammond/msdt-follina
Generates a malicious Microsoft Word document exploiting the MS-MSDT 'Follina' vulnerability to execute arbitrary commands or stage payloads via an…
 shubham0d/cve-2021-30853
Proof-of-concept script that demonstrates bypassing macOS Gatekeeper, notarization, and XProtect checks by exploiting CVE-2021-30853, allowing…
 azefzafyoussef/cve-2026-33229
Proof-of-concept exploit for CVE-2026-33229, an XWiki RCE via Apache Velocity sandbox bypass, with technical details and a working payload.
 absholi7ly/jspdf-object-injection
CVE-2026-25755 A critical PDF Object Injection vulnerability in jsPDF allows attackers to inject arbitrary PDF objects through the addJS() function,…
 simoesctt/-ctt-nsp-convergent-time-theory---network-stack-projection-cve-2026-24858-
A Proof-of-Concept demonstrating the application of 3D Navier-Stokes CTT formulations to packet flow optimization and defensive bypass.
 cduram/chirp-codeexecution_via_malicious_imagefile
Proof-of-concept exploit for arbitrary code execution through eval() injection in a ham radio programming application, including malicious .itm/.img…
 randomrobbiebf/cve-2026-28134
JetEngine <= 3.7.2 - Authenticated (Contributor+) Remote Code Execution
 velessecurity/cve-2020-14882-weblogic-analysis
Technical analysis and clean Java Thread Echo PoC for Oracle WebLogic Server vulnerability chain.
 sangsenimanwartefak/cve-2026-45034
PoC exploit for PHPSpreadsheet's phar:// deserialization vulnerability, bypassing prohibitWrappers to achieve remote code execution on vulnerable PHP…
 boreas37/cve-2026-64638-poc-xss2shell-
XSS2Shell (CVE-2026-64638) WordPress pre-auth XSS to RCE chain — PoC exploit + defensive audit tool + nuclei template
 waf-bypass-maker/waf-community-bypasses
Curated CSV collection of community-sourced Web Application Firewall bypass payloads for testing and validating WAF protections.
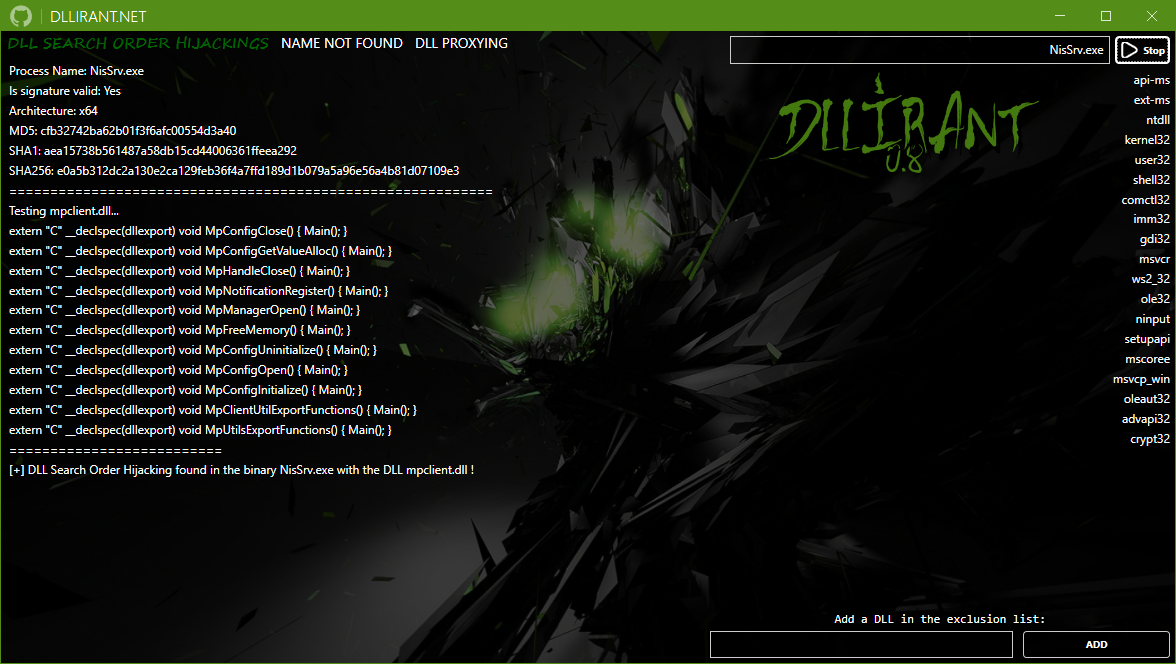 redteamsocietegenerale/dllirant
DLLirant is a tool to automatize the DLL Hijacking researches on a specified binary.
 orwagodfather/xss-payloads