
ip-camera-research
 amiraliuks/ip-camera-research
Security research on a consumer IP camera built on the Fullhan FH8626V100 SoC (model AJL30PG0803).
embedded-systems-securityexploitationexploit-frameworks+6
1
amiraliuks/ip-camera-researchSecurity research on a consumer IP camera built on the Fullhan FH8626V100 SoC (model AJL30PG0803).
 0x656565/cve-2023-48022
Exploit for CVE-2023-48022, adapted from Bishop Fox research. Configure IP, port, and payload to execute against vulnerable Ray instances.
 nettitude/runpe
C# Reflective loader for unmanaged binaries.
 jiahong-guan/log4j-shell-poc
A Proof-Of-Concept for the CVE-2021-44228 vulnerability.
 laskdjlaskdj12/cve-2024-35106-poc
Proof-of-concept exploit for CVE-2024-35106, a stack buffer overflow in NEXTU FLETA AX1500 Wi-Fi 6 router. Demonstrates denial-of-service and…
 rbowes-r7/refreshing-soap-exploit
A PoC exploit for CVE-2022-41622 - a CSRF in F5 BIG-IP control plane that leads to remote root
 evillm/cve-2024-45590-poc
Proof-of-concept exploit for CVE-2024-45590, demonstrating unauthenticated remote code execution in a WordPress plugin via arbitrary file upload.…
 l-urk/cve-2024-6387
Proof of concept python script for regreSSHion exploit.
 coolman6942o/-exploit-cve-2023-36025
Windows SmartScreen Security Feature Bypass Vulnerability
 boompig/cve-2016-6662
Exploit code for MySQL remote root code execution and privilege escalation (CVE-2016-6662), including Python and C implementations.
 biitts/poc-ingressnightmare-cve-2025-1974
Builds a shell.so reverse shell payload for CVE-2025-1974 (IngressNightmare) using Alpine Linux in Docker, with hardcoded IP and port configuration.
 ch4os1/cve-2024-4157-ssrf-rce-reverse-shell
Chaining Havoc C2 SSRF with RCE to get reverse shell on Havoc C2 Server.
 polo35/cve-2020-0022
CVE-2020-0022 vulnerability exploitation on Bouygues BBox Miami (Android TV 8.0 - ARM32 Cortex A9)
 lorentzenman/payday
Payload generator that uses Metasploit and Veil. Takes IP address as input and calls Veil. Use msfvenom to create payloads and writes resource…
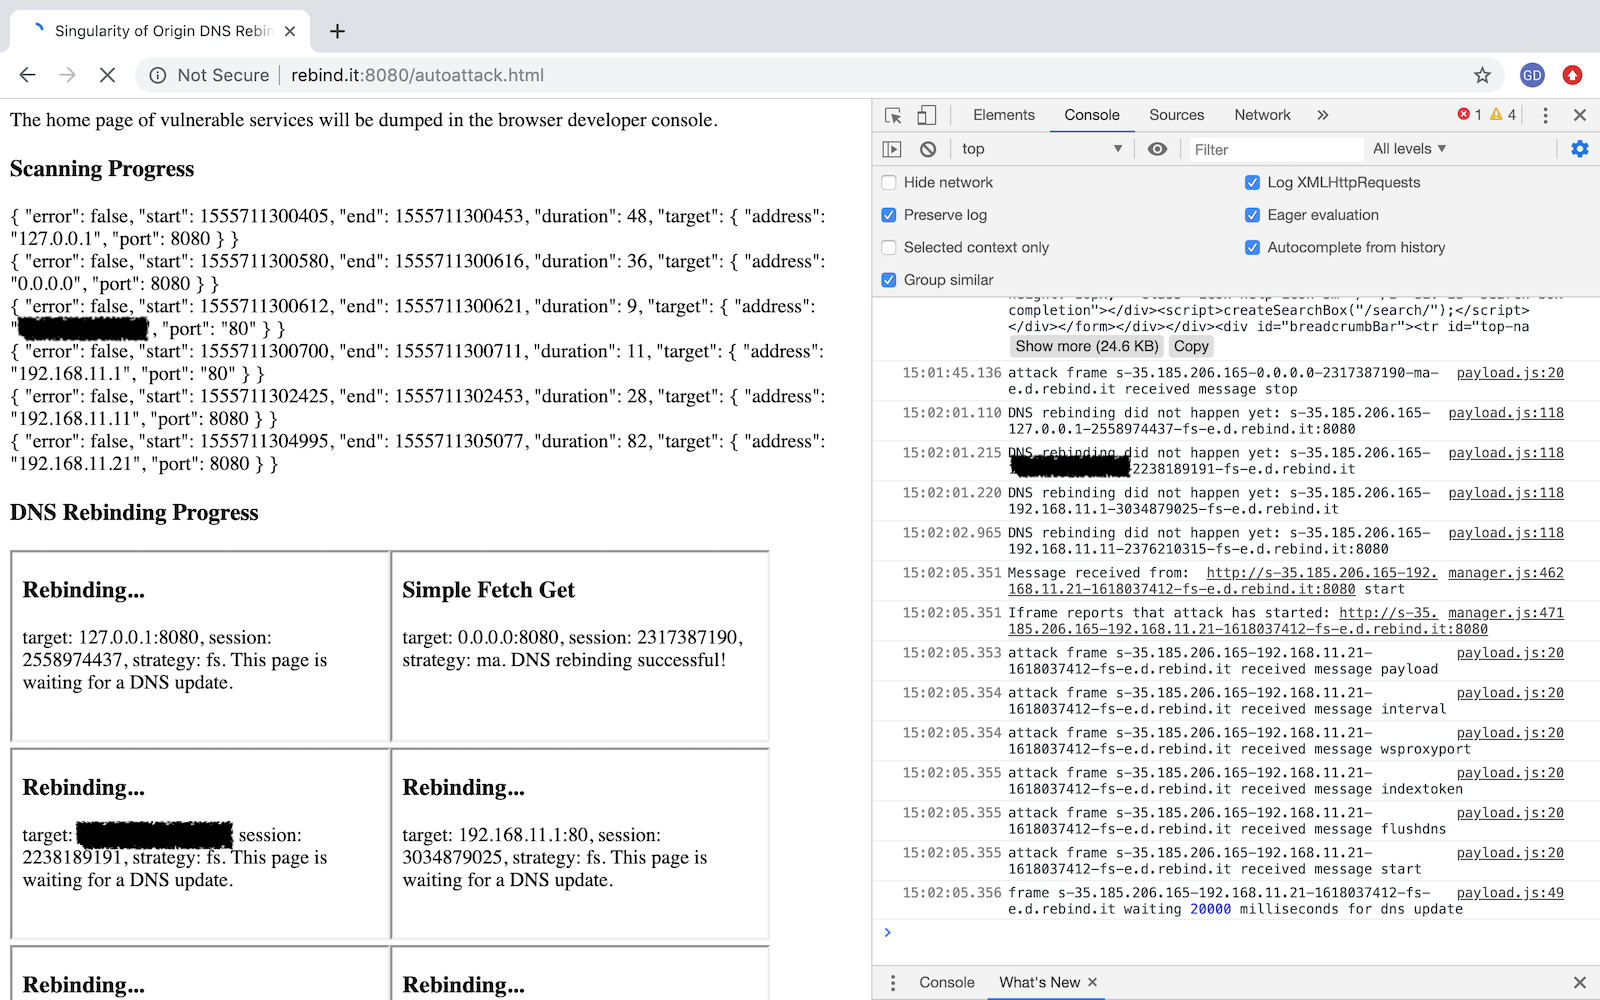 nccgroup/singularity
A DNS rebinding attack framework.
 elevenpaths/siemframework
Modular Python3 attack framework for automating exploitation of SIEM platforms (Splunk, Graylog, OSSIM, QRadar, McAfee) via credential theft, payload…
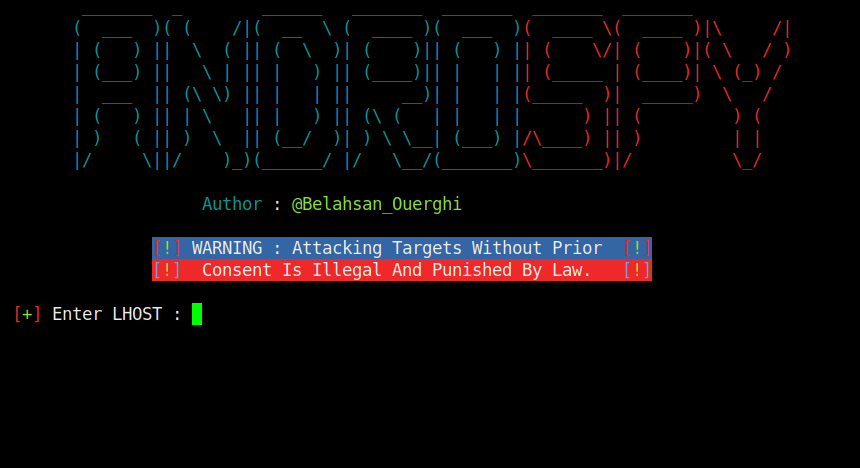 cyb0r9/androspy
Automated Android backdoor generator with crypter, IP poisoning, and Metasploit payload integration for penetration testing and red team operations.
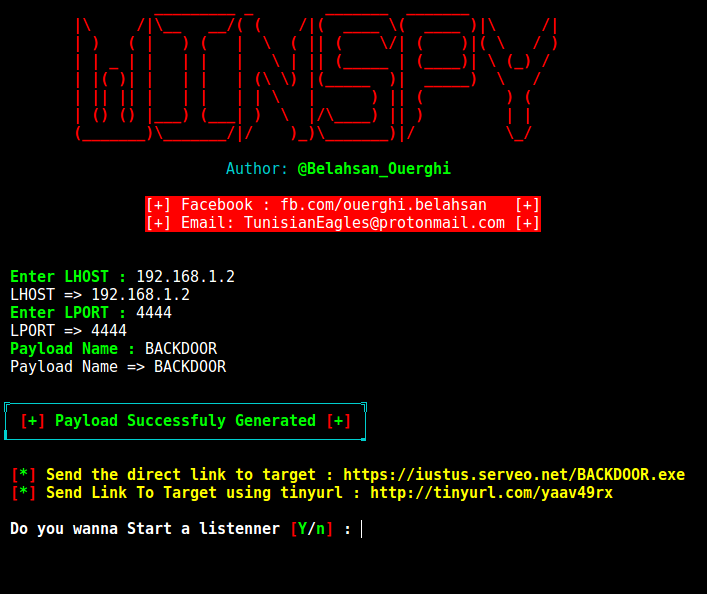 cyb0r9/winspy
Generates Windows reverse shell backdoors with automatic IP poisoning, leveraging Metasploit for payload creation and Apache for delivery in…