
CVE-2026-102425
 murrez/cve-2026-102425
Python PoC for CVE-2026-102425: unauthenticated RCE in Joomla Balbooa Forms (com_baforms) via field shortcode injection in post-submission PHP…
exploitationpayload-developmentpenetration-testing+5
murrez/cve-2026-102425Python PoC for CVE-2026-102425: unauthenticated RCE in Joomla Balbooa Forms (com_baforms) via field shortcode injection in post-submission PHP…
 murrez/cve-2026-100721
Python PoC for CVE-2026-100721: detects and exploits vm2 <3.12.2 NodeVM external allowlist bypass, achieving sandbox escape and host RCE via local…
 murrez/cve-2026-18143
Python PoC that checks and exploits CVE-2026-18143, an unauthenticated arbitrary file upload in Addify Request a Quote for WooCommerce ≤ 2.9.2 via…
 winrarzipsexploit/cve-2026-48908
Python exploit suite for CVE-2026-48908, an unauthenticated ZIP upload RCE in Joomla SP Page Builder (<=6.6.1), with fingerprinting, batch mode, and…
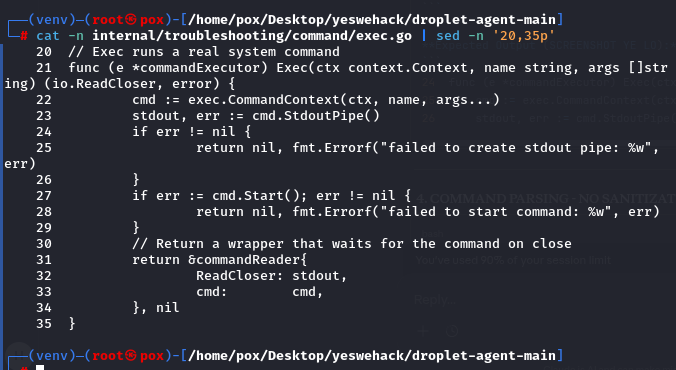 poxsky/cve-2026-24516-digitalocean-rce.
Technical analysis and PoC for CVE-2026-24516: Unauthenticated Root Remote Code Execution in DigitalOcean Droplet Agent (CVSS 10.0).
 zyphorixofficialmain-lab/cve-2026-87902
Python exploit for CVE-2026-87902, a WordPress Core LFI-to-RCE chain. Fingerprints versions, writes a PHP shell via pearcmd, and provides command…
 nxploited/cve-2026-91097-cve-2026-91106
HPLIP < 3.26.6 — Full admin takeover via PAPPL web interface (no auth). Related to CVE-2026-91097 through CVE-2026-91106 (CVSS 9.3)
 murrez/cve-2026-19658
Python 3 checker and exploit helper for CVE-2026-19658, a WordPress Give Tributes PHP object injection flaw, with FOFA target discovery and legacy…
 iicaicai/cve-2026-5524-poc
Python mass-exploit toolkit for CVE-2026-5524, an unauthenticated file upload RCE in the WordPress Divi Form Builder plugin, with webshell upload and…
 kamalx06/tornadorevc2
Modular post-exploitation framework managing reverse-shell sessions over TCP/TLS/mTLS with plugins for enumeration, in-memory execution, SOCKS5…
 ghostlyrootb2h/cve-2026-82222
Exploit framework for CVE-2026-82222, an unauthenticated RCE in GiveWP WordPress plugin. Supports mass scanning, auto-detection, multi-threading,…
 digitalsurgn/cve-2024-21546
Automated exploit toolkit and detection template for CVE-2024-21546, an unauthenticated RCE in UniSharp Laravel Filemanager, with WAF evasion and…
 null200ok/cve-2026-41940-tool
A comprehensive Python utility to **detect**, **scan in bulk**, and **exploit** the critical authentication bypass vulnerability (CVE-2026-41940) in…
 truekas/ls-poc
Proof-of-concept exploit for CVE-2026-30368, demonstrating authentication bypass in Lightspeed Classroom to control student devices via Ably channel.
 al4n4n/cve-2026-25253-research
Proof-of-concept exploit for CVE-2026-25253, demonstrating one-click RCE on OpenClaw via Cross-Site WebSocket Hijacking. Includes attacker server and…
 g0d150ne/xss2shell
Exploits WordPress pre-auth XSS (CVE-2026-64638) to achieve remote code execution, installing an AES-encrypted backdoor webshell with persistence,…
 jsecu/bof-pack-1
A care package of useful bofs for red team engagments
 0xdea/tactical-exploitation
Modern tactical exploitation toolkit.