
CVE-2022-25581
 wooluo/cve-2022-25581
Python exploit script for CVE-2022-25581 (ClassCMS 2.4 arbitrary file download) that automates login, CSRF token extraction, malicious zip upload…
educationexploitationpayload-development+3
wooluo/cve-2022-25581Python exploit script for CVE-2022-25581 (ClassCMS 2.4 arbitrary file download) that automates login, CSRF token extraction, malicious zip upload…
 mahajian/cve-2024-10793
Proof-of-concept exploit for CVE-2024-10793 targeting WordPress wp-security-audit-log plugin. Demonstrates account takeover, privileged user…
 mightysai1997/cve-2021-41773-l-
Proof-of-concept exploit for CVE-2021-41773, demonstrating path traversal and remote code execution on Apache HTTP Server 2.4.49 with a reverse shell…
 shivshantp/cve-2025-24813
Apache Tomcat PUT JSP RCE - CVE-2025-24813 - Exploit & PoC
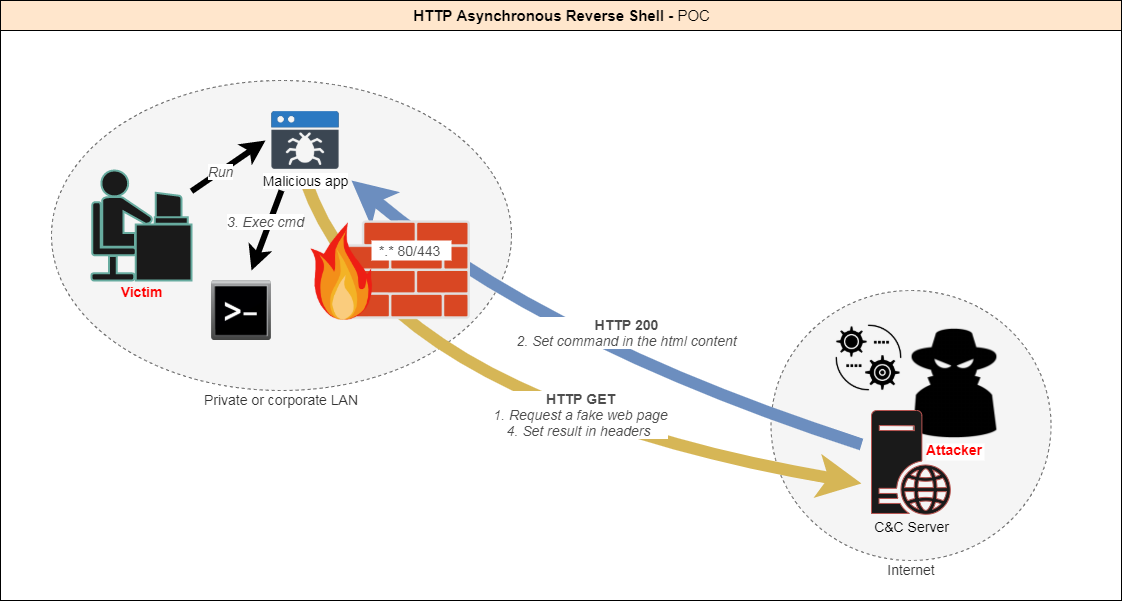 onsec-fr/http-asynchronous-reverse-shell
[POC] Asynchronous reverse shell using the HTTP protocol.