Nginx-chain-Rift-Poolslip

ASLR-independent nginx RCE chain PoC combining the PoolSlip heap over-read leak (CVE-2026-9256) with the rift overflow (CVE-2026-42945) to reach…

ASLR-independent nginx RCE chain PoC combining the PoolSlip heap over-read leak (CVE-2026-9256) with the rift overflow (CVE-2026-42945) to reach…

Modular Python exploitation framework with a Metasploit-style console, auto-registering Exploit and Auxiliary modules, tri-state checks, and multiple…

Python PoC exploiting CVE-2026-38526 in Krayin CRM <= 2.2.x: authenticated PHP webshell upload via /admin/tinymce/upload leading to remote code…

Python PoC exploiting CVE-2026-38526 in Krayin CRM <= 2.2.x: authenticates, uploads a PHP webshell via /admin/tinymce/upload, and executes commands…

PS5 exploit chain for firmware 7.00-13.60 combining a WebKit JSC info leak and typedarray corruption with an aio_multi_wait UAF race for kernel…

Proof-of-concept for CVE-2026-100310, a local privilege escalation in GNU libextractor ≤1.15 via the LIBEXTRACTOR_PREFIX untrusted search path, with…

A minimal PE mapper that loads DLLs straight from memory and calls into a clean plugin interface, no LoadLibrary needed.

UnrealIRCd 3.2.8.1 backdoor exploit — reverse shell via AB; trigger, built from scratch in Python using raw sockets. No Metasploit.

WordPress Core <= 7.1.1 unauthenticated LFI to RCE - validation lab, PoC, nuclei template (GHSA-7hp8-65ch-5whp)

Reproduction lab + URL-list scanner + PoC for CVE-2026-87902 / GHSA-7hp8-65ch-5whp — WordPress get_page_template() unauthenticated LFI to conditional…

Windows proof-of-concept exploit chain for CVE-2019-11707, a Firefox IonMonkey type confusion, combining browser RCE with sandbox escape to achieve…

From-scratch exploit development in Python. No Metasploit. No frameworks. Raw socket-level implementation of real CVEs against authorized lab targets.

fodhelper-based UAC bypass poc for CVE-2021-31956, registry keys to SYSTEM without a prompt. educational

CVE-2026-63030 & CVE-2026-60137 RCE chain proof-of-concept

Reproduction pack and PoC script for CVE-2026-87796, an unauthenticated arbitrary file upload RCE in Multi Uploader for Gravity Forms <= 1.1.9, with…

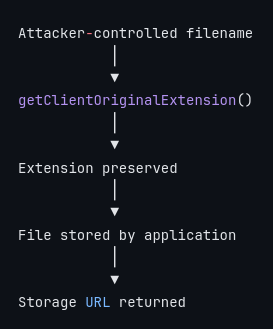
Authenticated Arbitrary File Upload leading to Remote Code Execution Technical analysis and controlled reproduction of CVE-2026-38526 in Webkul…

PoC and write-up for the HackTheBox "Nexus" privilege escalation: root-run Gitea template-sync service vulnerable to path traversal via forged Git…

JFrog Artifactory 预认证全链 RCE 复现项目(CVE-2026-42018 / CVE-2026-65616 / CVE-2026-65615):完整攻击链报告、7.146.7 Docker 复现交付物(EXP / 部署 / 基线验证 / payload 样本 / 恢复工具)