
redStack
 devzero-security/redstack
Terraform-deployed red team operator lab on AWS: Mythic, Sliver, and Adaptix C2 behind a production-style Apache redirector, with Kali/Windows hosts…
cloud-infrastructure-securitycommand-and-controleducation+8
316
devzero-security/redstackTerraform-deployed red team operator lab on AWS: Mythic, Sliver, and Adaptix C2 behind a production-style Apache redirector, with Kali/Windows hosts…
 trustedsec/meterssh
MeterSSH is a way to take shellcode, inject it into memory then tunnel whatever port you want to over SSH to mask any type of communications as a…
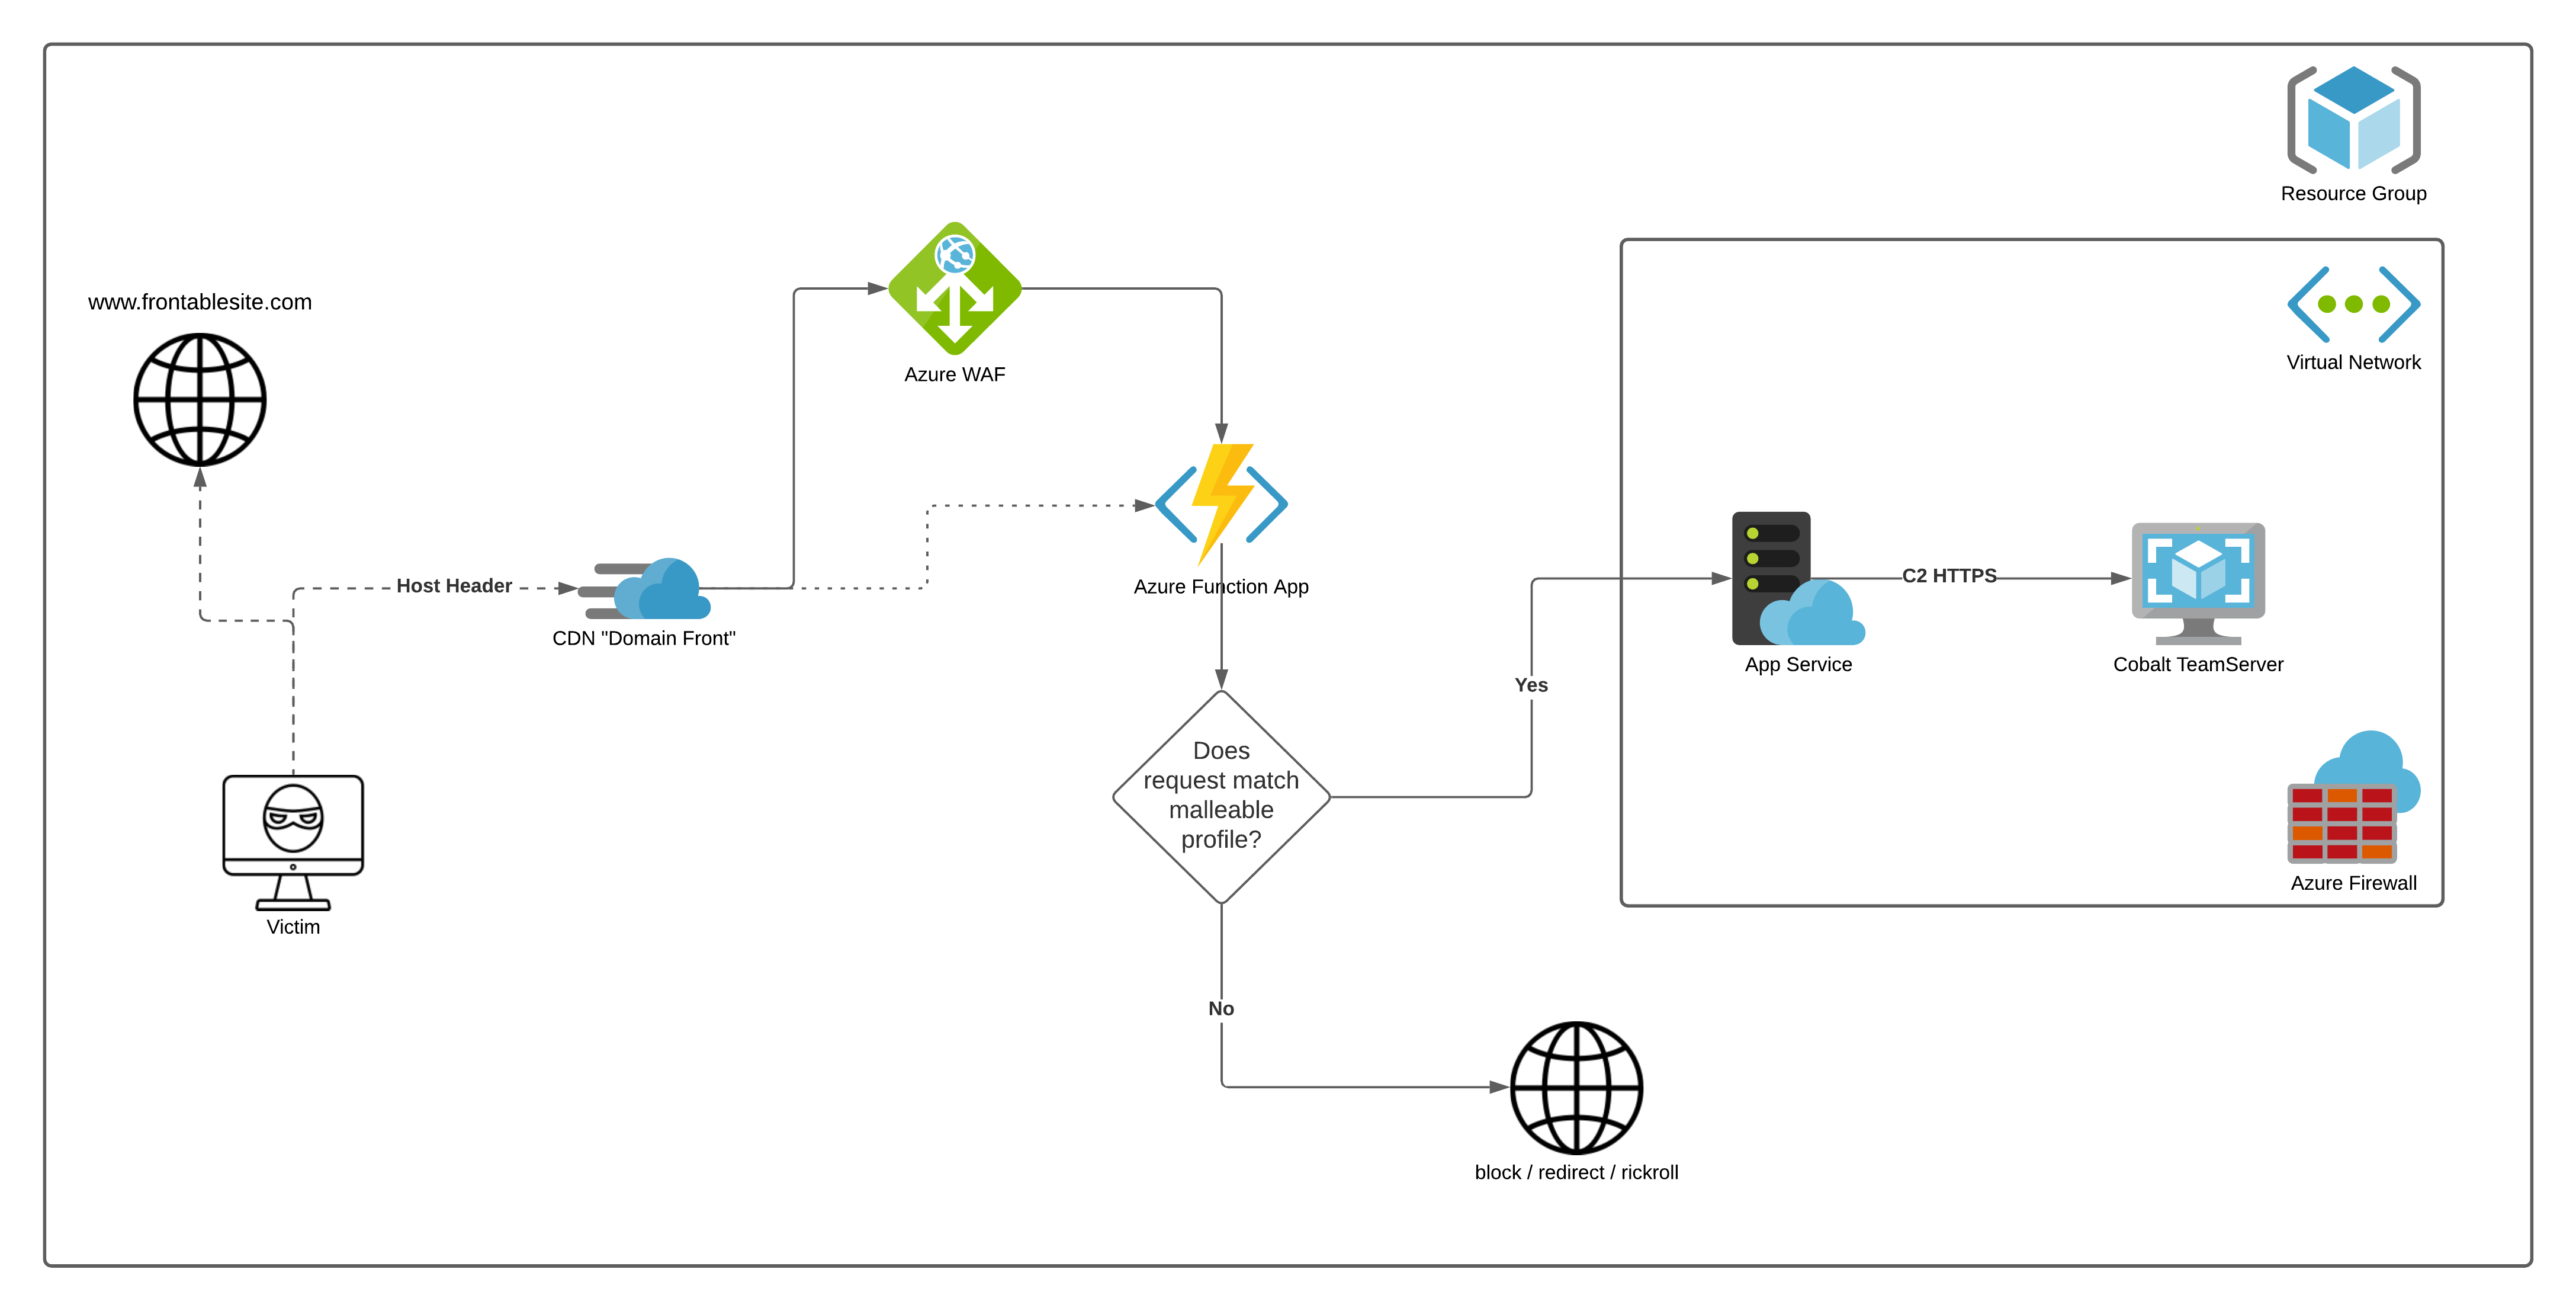 flangvik/azurec2relay
Azure Function that validates and relays Cobalt Strike beacon traffic using malleable C2 profiles, redirecting invalid requests to a decoy site and…
 0dinox/cve-2024-415770-ssrf-rce
Automated exploit for CVE-2024-415770: leverages SSRF to achieve RCE, registers an agent on the teamserver, opens a socket, and injects an SSH key…
 axedos/cve-2026-67401
Python proof-of-concept for CVE-2026-67401, an authenticated SQL injection in cPanel EmailTrack that allows arbitrary file write as root via SQLite…
 mrr0b0t19/cve-2024-6387-exploit-poc
Proof-of-concept exploit for CVE-2024-6387 targeting vulnerable OpenSSH servers via heap manipulation and race condition to achieve remote code…
 jxroot/zeropulse
🔒 Modern C2 Platform with Cloudflare Tunnel Integration | WinRM & SSH Remote Management | Real-time Terminal & Remote Desktop | Built with FastAPI &…
 l-urk/cve-2024-6387
Proof of concept python script for regreSSHion exploit.
 purpleozone/pe_cve-cve-2021-3156
Exploit for Ubuntu 20.04 using CVE-2021-3156 enhanced with post-exploitation scripts
 bishopfox/cve-2021-35211
Python exploit for Serv-U SSH vulnerability (CVE-2021-35211) with multiple payload modes: stage, exec, and download-execute, enabling shellcode…
 saku0512/cve-2026-48732-poc
Proof-of-concept demonstrating OS command injection in Warp's legacy SSH background command handling (CVE-2026-48732). Includes local simulation of…
 iveresk/cve-2022-40684
Proof-of-concept exploit for CVE-2022-40684 authentication bypass in Fortinet FortiOS, FortiProxy, and FortiSwitchManager. Injects SSH keys via…
 gill-singh-a/vsftp-2.3.4-remote-root-shell-exploit
A Simple Python Program that uses gets a Remote Root Shell on the Target Device by exploiting a Vulnerability (CVE-2011-2523) present in vsFTP 2.3.4
 vulncheck-oss/external-c2-experiments
Go external C2 module for go-exploit that catches reverse SSH shells, providing a server listener and payload client for integrating custom C2…
 symbolexe/cve-2024-6387
SSH Exploit for CVE-2024-6387 : RCE in OpenSSH's server, on glibc-based Linux systems
 zorvithonleo/exploit-cve-2014-4210-
Exploit for CVE-2014-4210 targeting WebLogic deserialization, with post-exploitation features including ransomware deployment, C2 integration, and…
 lu3ky13/alternative-approach-reverse-shell-callback-test-invokeai-rce
This repository contains alternative payload approaches for the InvokeAI RCE vulnerability (CVE-2024-12029) when SSH key injection fails. The…
 4lxprime/regresshive
rewrited SSH Exploit for CVE-2024-6387 (regreSSHion)