
nanodump
 fortra/nanodump
The swiss army knife of LSASS dumping
exploitationmemory-forensicspayload-development+4
fortra/nanodumpThe swiss army knife of LSASS dumping
 gabriellandau/edrsandblast-godfault
EDRSandblast-GodFault
 redteamsocietegenerale/dllirant
DLLirant is a tool to automatize the DLL Hijacking researches on a specified binary.
 carmaa/inception
Inception is a physical memory manipulation and hacking tool exploiting PCI-based DMA. The tool can attack over FireWire, Thunderbolt, ExpressCard,…
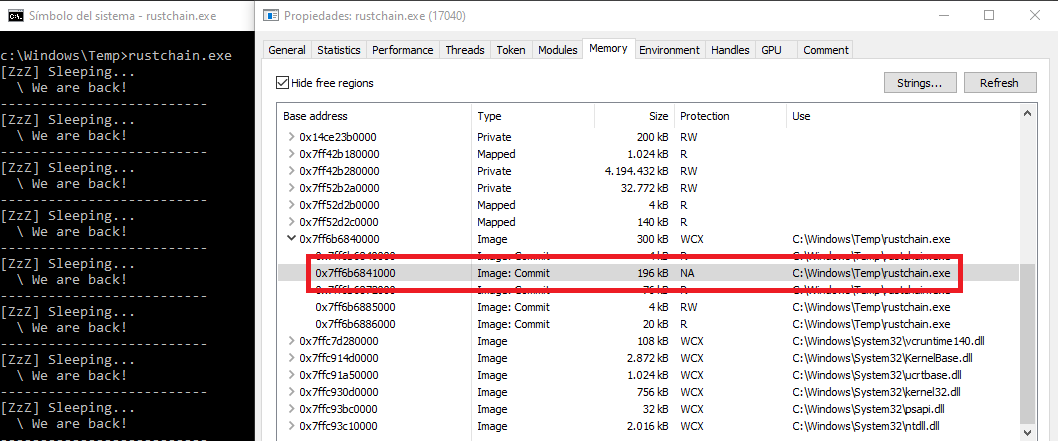 kudaes/rustchain
Hide memory artifacts using ROP and hardware breakpoints.
 naksyn/moduleshifting
Stealthier variation of Module Stomping and Module Overloading injection techniques that reduces memory IoCs. Implemented in Python ctypes
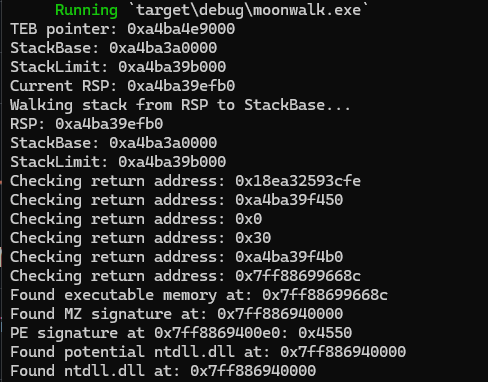 teach2breach/moonwalk
find dll base addresses without PEB WALK