

Heroinn
 b23r0/heroinn
A cross platform C2/post-exploitation framework.
command-and-controldata-exfiltrationlateral-movement+8
b23r0/heroinnA cross platform C2/post-exploitation framework.
 bishopfox/sliver
Adversary Emulation Framework
 s3n4t0r-0x0/bear-c2
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
 javascript-obfuscator/javascript-obfuscator
Obfuscates JavaScript and Node.js code with variable renaming, string encryption, control flow flattening, and anti-debugging to protect source code…
 jingmatrix/pixel-ksu-root
CVE research and exploits to help gaining roots for Pixel devices
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 mythicagents/xenon
A Mythic agent for Windows written in C
 lsposed/lspromise
Android complete exploit chain that enables privilege escalation from a local untrusted app to root/kernel, combination of CVE-2026-49881 and…
 its-a-feature/mythic
A collaborative, multi-platform, red teaming framework
 dagowda/notrdp
Havoc C2 plugin that creates a hidden Windows desktop, streams it to a browser viewer, and injects mouse/keyboard input for covert remote control.
 racoten/reflectivepluginloader
Minimal Windows x64 reflective PE mapper that loads DLLs from memory without LoadLibrary, resolves exports, and dispatches calls through a…
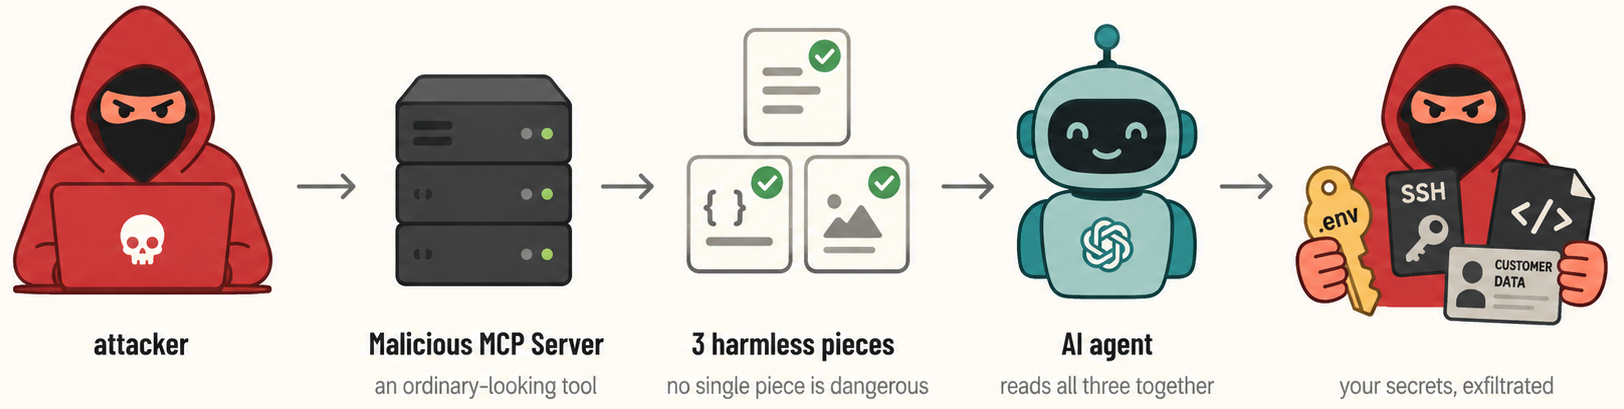 asset-group/ghostsplice
Ghostsplice repository: PoC for Cross-Channel Trust Fragmentation Attack
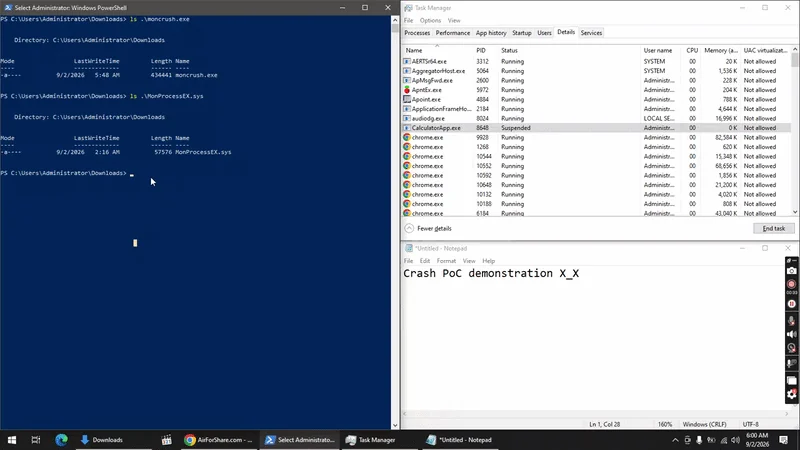 deathshotxd/0xm0ncrush
Kernel-mode process terminator using a signed BYOVD driver. Works on all Windows 10/11. No offsets, no PDB. Rust.
 fortra/impacket
Python library for low-level network protocol manipulation, featuring SMB, MSRPC, Kerberos, and WMI implementations with tools for authentication…
 0dayctf/reverse-shell-generator
Hosted Reverse Shell generator with a ton of functionality. -- (Great for CTFs)
 traitimtrongvag/android-imgui-template
A complete Android ImGui menu template project.
 a0yami/cve-2025-50505
Exploit for CVE-2025-50505 in Clash Verge Rev, demonstrating local privilege escalation and remote code execution via unauthenticated API, including…