
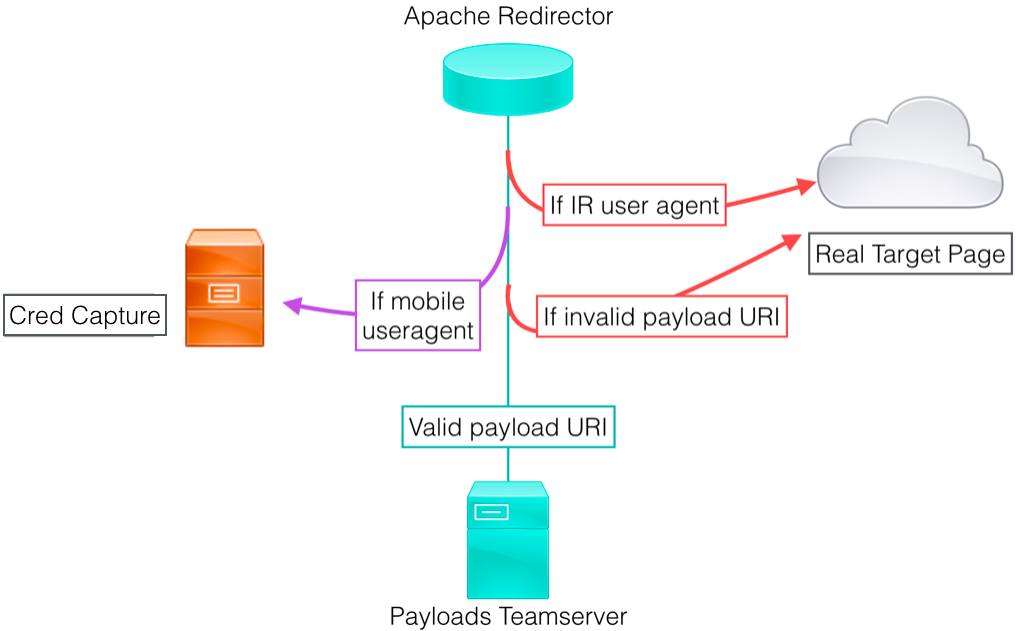
Red-Team-Infrastructure-Wiki
 bluscreenofjeff/red-team-infrastructure-wiki
Wiki to collect Red Team infrastructure hardening resources
cloud-infrastructure-securitycommand-and-controlcurated-resources+5
4.5k
bluscreenofjeff/red-team-infrastructure-wikiWiki to collect Red Team infrastructure hardening resources
 b23r0/heroinn
A cross platform C2/post-exploitation framework.
 grisuno/lazyown
Red team framework and multi-operator C2 platform with AI agents, malleable implants, rootkits, phishing engine, and 741 CLI commands covering the…
 bishopfox/sliver
Adversary Emulation Framework
 botesjuan/burp-suite-certified-practitioner-exam-study
Practical study notes and walkthroughs for PortSwigger Academy labs, covering web vulnerabilities, payloads, enumeration, and BSCP exam strategies.
 adityatelange/evil-winrm-py
Execute commands interactively on remote Windows machines using the WinRM protocol (just faster)
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
 yaklang/yakit
All-in-one penetration testing platform with MITM proxy, web fuzzer, reverse connection handler, and plugin system for automated security testing and…
 ccp-p/ghostlock-cve-2026-43499-4.19-k40
Android kernel LPE PoC for CVE-2026-43499, an rtmutex use-after-free in 4.19 Qualcomm kernels, adapted for Redmi K40 with LD_PRELOAD root payload.
 lyravoid/folkpatch
Root access to the kernel can be achieved simply by patching the Boot partition for reflashing. This solution is based on a non-parallel extended…
 user696/mrrat
:mouse: This is a cross-platform Python 2.x Remote Access Trojan (RAT)
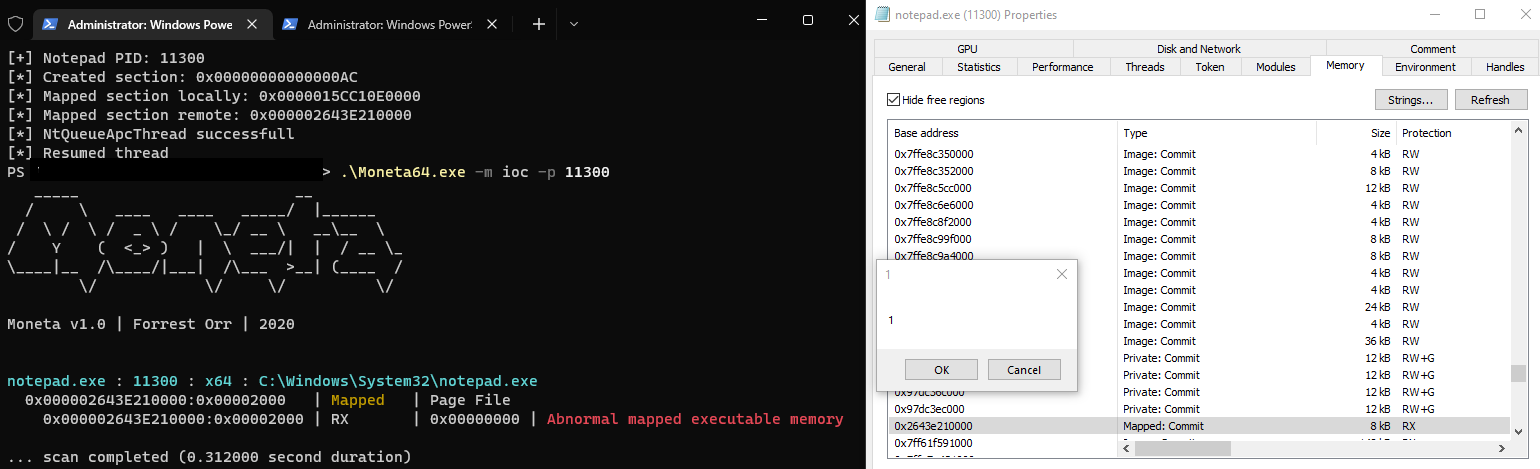 theflink/deepsleep
A variant of Gargoyle for x64 to hide memory artifacts using ROP only and PIC
 exploit-database/exploitdb
exploitdb // The official Exploit-Database repository
 mythicagents/xenon
A Mythic agent for Windows written in C
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 x3r0day/fud-c2-framework
A fileless reverse shell and C2 framework leveraging direct syscalls, proxy tunneling, and ChaCha20 encryption for AV evasion.
 ntfargo/relapse-exploit
PS5 exploit chain for firmware 7.00-13.60 combining a WebKit JSC info leak and typedarray corruption with an aio_multi_wait UAF race for kernel…
 mgeeky/stracciatella
OpSec-safe Powershell runspace from within C# (aka SharpPick) with AMSI, Constrained Language Mode and Script Block Logging disabled at startup