SmuggleMyPayload
Generates HTML smuggling pages that embed and reconstruct files client-side via JavaScript, with payload encoding, chunking, obfuscation, and…

Generates HTML smuggling pages that embed and reconstruct files client-side via JavaScript, with payload encoding, chunking, obfuscation, and…

Obfuscates PowerShell and JavaScript scripts using tree-sitter-based parsing with multiple configurable impostor profiles for stealth, size, and…

A DNS rebinding attack framework.

CVE-2026-39154, Stored XSS in CometChat JS SDK

This repository contains a POC of CVE-2025-55182, a critical (CVSS score 10.0) pre-authentication remote code execution vulnerability affecting React…

JavaScript for Automation (JXA) macOS agent

Proof-of-concept exploit for CVE-2026-27574, a critical code injection in OneUptime enabling remote code execution and environment variable leakage.

This repository contains a Proof of Concept (PoC) for CVE-2024-28397, a vulnerability in the js2py library allowing a sandbox escape to achieve…

CVE-2023-22621: SSTI to RCE by Exploiting Email Templates affecting Strapi Versions <=4.5.5

Python PoC and version scanner for CVE-2026-29053, an authenticated RCE in Ghost CMS below 6.19.1 via malicious Handlebars theme templates.

PoC for Arbitrary Code Execution in Notable

CVE-2024-4367 & CVE-2024-34342 Proof of Concept

Serverside Template Injection (SSTI) RCE - THM challenge "whiterose"

This vulnerability displays an XSS flaw in a WordPress popup plugin, allowing attackers to inject malicious JavaScript through a stored XSS

JavaScript exploit targeting CVE-2023-2033 for proof-of-concept testing and vulnerability validation in web applications.

Proof-of-concept exploit for CVE-2019-0752 targeting Internet Explorer 11 on Windows 10 x64. Uses JavaScript DOM manipulation and special address…

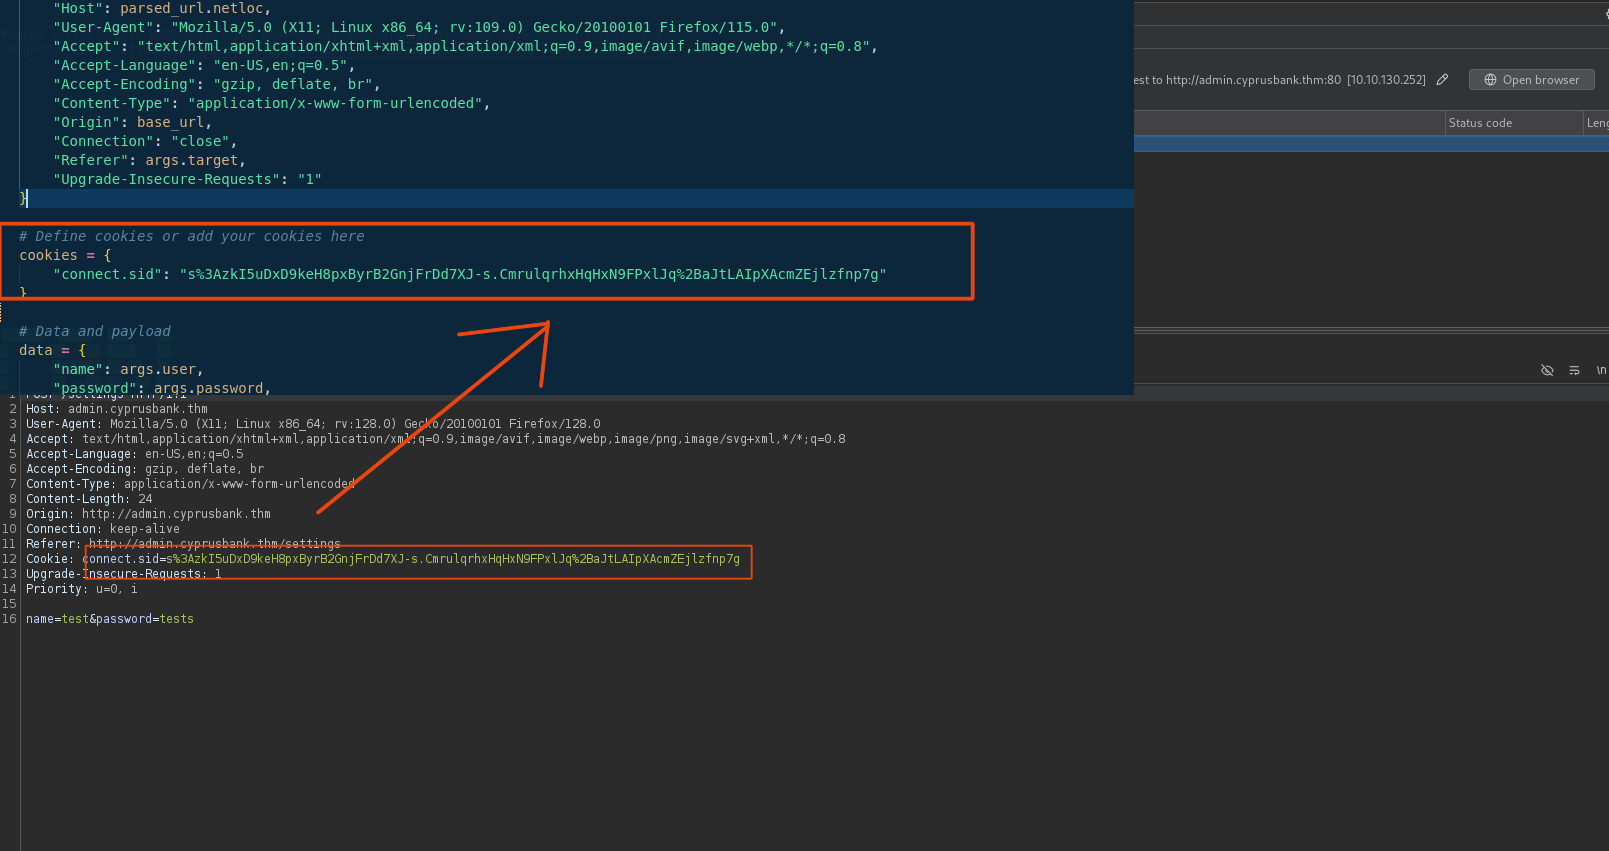
Educational demo of Node.js insecure deserialization (CVE-2017-5941) with cookie-based payload injection and reverse shell exploitation for security…