

metasploit-payloads
 rapid7/metasploit-payloads
Unified repository for different Metasploit Framework payloads
command-and-controlexploitationexploit-frameworks+9
2.1k
rapid7/metasploit-payloadsUnified repository for different Metasploit Framework payloads
 hypnguyen1209/log4j2-rce
Pre-auth RCE via FilteredObjectInputStream MarshalledObject bypass in Apache Log4j 2
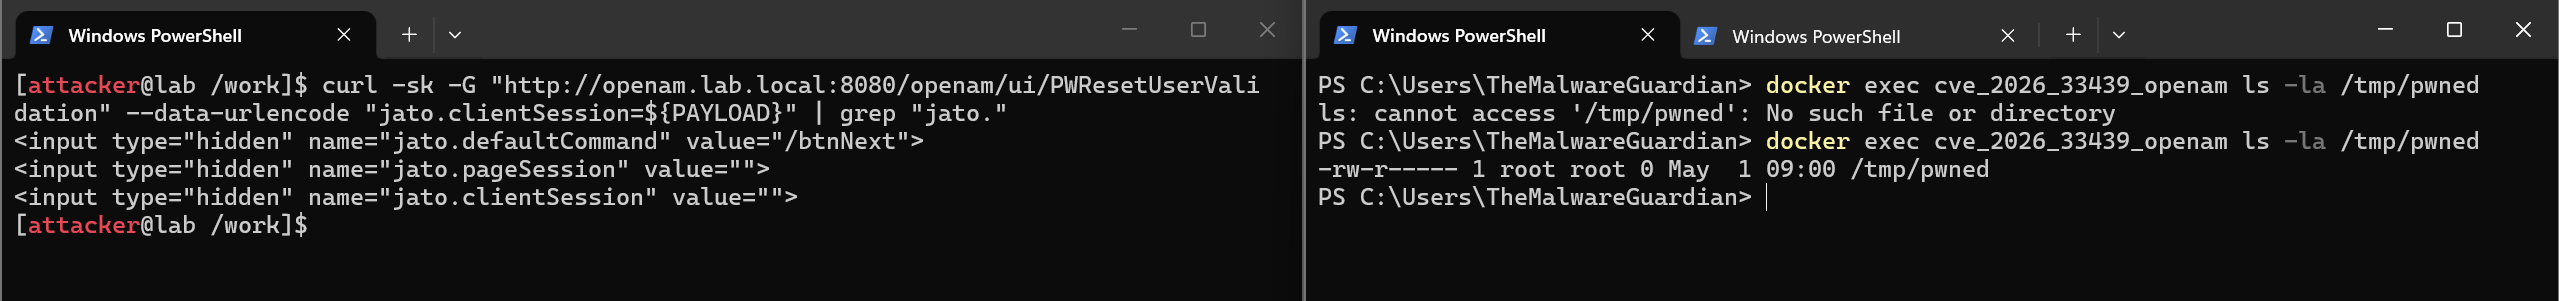 themalwareguardian/cve-2026-33439
First publicly shared exploit implementation for CVE-2026-33439 (OpenAM pre-auth RCE via jato.clientSession deserialization).
 fi3ro/cve-2015-5377
Java deserialization exploit targeting Elasticsearch 1.5.2 transport protocol (port 9300) using Groovy MethodClosure chain for remote code execution…
 joaovicdev/exploit-cve-2026-40901
Automated exploit for DataEase: 4-vulnerability chain (auth bypass, JDBC blocklist bypass, SQL injection, Java deserialization) achieving…
 ibonok/cve-2026-33439-poc
Exploit for OpenAM pre-auth RCE (CVE-2026-33439) using a Java deserialization gadget chain to execute commands and return output directly in the HTTP…
 llamaonsecurity/cve-2018-12533
Payload generator and proof-of-concept exploit for CVE-2018-12533 (Richfaces deserialization/EL injection) with Docker-based vulnerable environment…
 gokul-ramesh/spring4shell-poc-exploit
Demonstrable Proof of Concept Exploit for Spring4Shell Vulnerability (CVE-2022-22965)
 mbechler/marshalsec
Java deserialization vulnerability exploitation tool with payload generators for multiple marshallers (Jackson, XStream, SnakeYAML) and JNDI…
 gu-007/struts2-tool
Struts2 S2-045/S2-046 CVE-2017-5638 detection & exploitation tool
 jiahong-guan/log4j-shell-poc
A Proof-Of-Concept for the CVE-2021-44228 vulnerability.
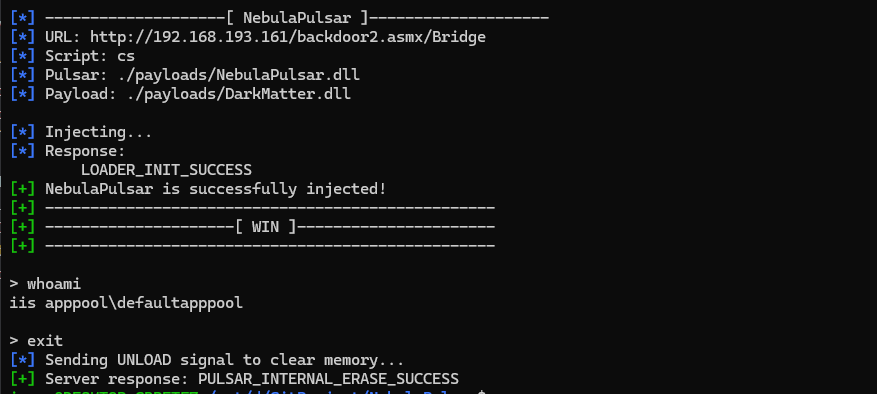 iss4cf0ng/nebulapulsar
NebulaPulsar is a proof-of-concept in-memory implant framework for Java (JSP) and ASP.NET (ASPX/ASHX/ASMX) webshells, originally developed as part of…
 gutierre0x80/cve-2026-59827
Technical analysis and proof of concept for CVE-2026-59827, a critical unsafe Java deserialization vulnerability in Metabase leading to remote code…
 schierlm/javapayload
JavaPayload is a collection of pure Java payloads to be used for post-exploitation from pure Java exploits or from common misconfigurations (like not…
 cornerpirate/java-stager
A PoC Java Stager which can download, compile, and execute a Java file in memory.
 jas502n/cve-2015-5254
ActiveMQ Deserialization RCE
 pimps/ysoserial-modified
That repository contains my updates to the well know java deserialization exploitation tool ysoserial.
 abbarhissarh/cve-2022-26133
CVE-2022-26133 Exploit