QuickAssist_UAC_Bypass

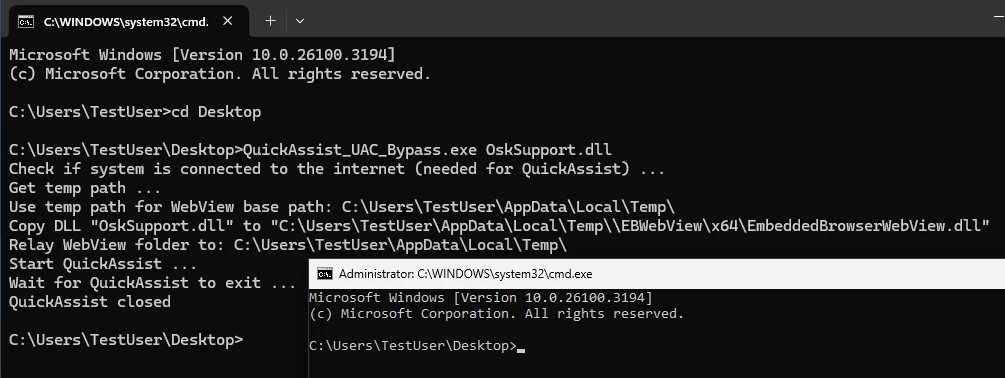
UAC bypass PoC abusing the UIAccess QuickAssist binary to load an attacker-controlled DLL via WebView2 BrowserExecutableFolder, then hijack elevated…

UAC bypass PoC abusing the UIAccess QuickAssist binary to load an attacker-controlled DLL via WebView2 BrowserExecutableFolder, then hijack elevated…

Shellcode implementation of Reflective DLL Injection. Convert DLLs to position independent shellcode

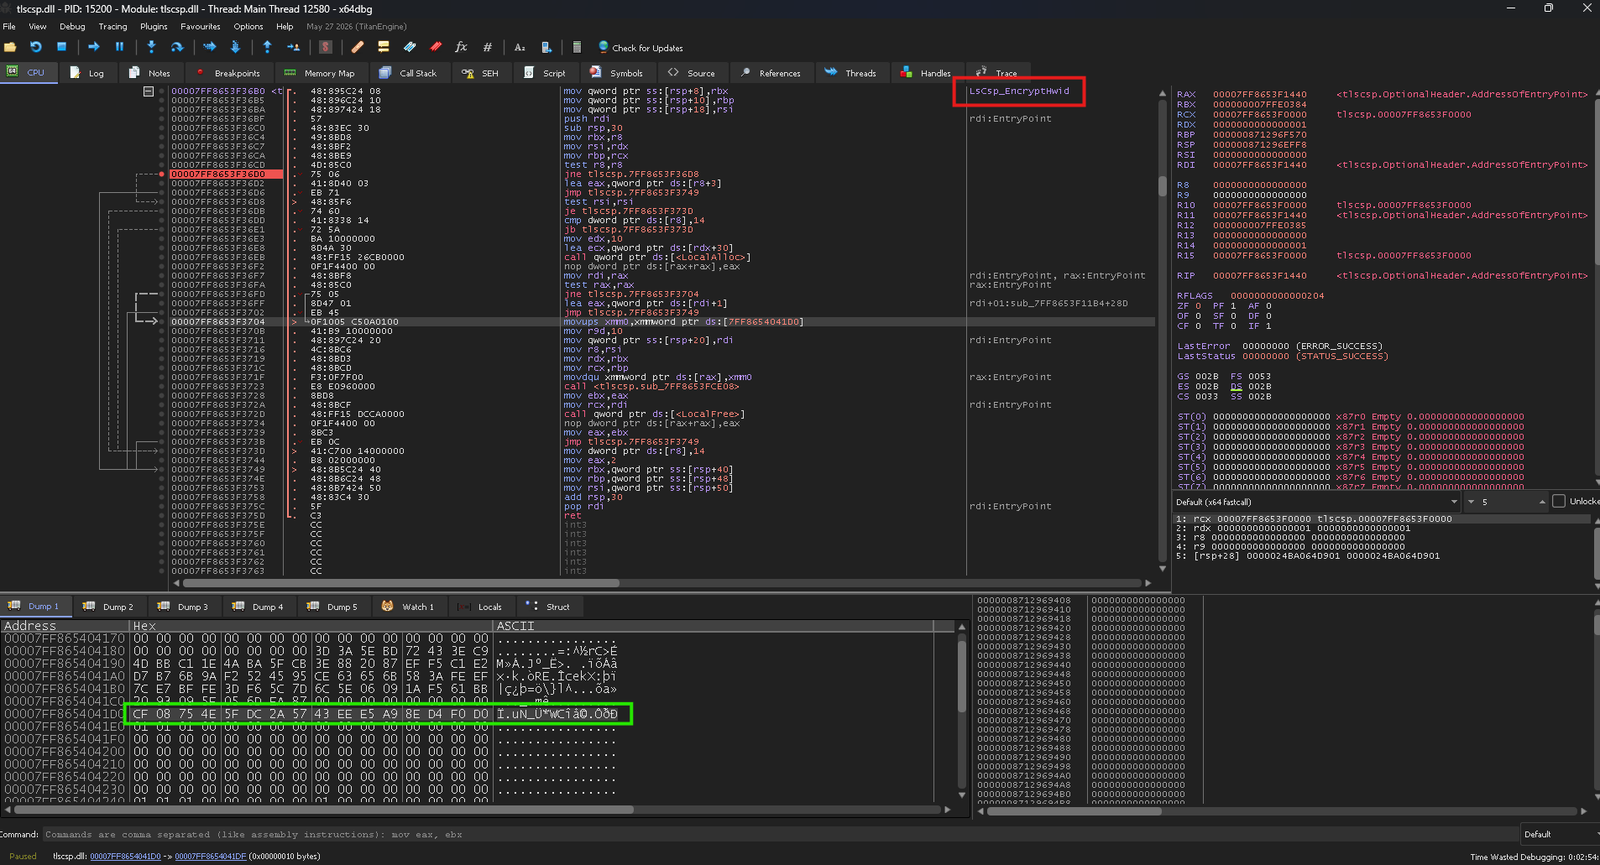
Abuses the Microsoft-signed tlscsp.dll LOLBin to run RC4 encrypt/decrypt via LsCsp_EncryptHwid, patching the hardcoded key in memory for BYOK…

EternalBlue suite remade in C/C++ which includes: MS17-010 Exploit, EternalBlue vulnerability detector, DoublePulsar detector and DoublePulsar…

SigFlip is a tool for patching authenticode signed PE files (exe, dll, sys ..etc) without invalidating or breaking the existing signature.

Polymorphic shellcode generator for in-memory execution of EXE, DLL, .NET, VBScript, and JScript with per-output and per-build randomization for…

C++ library to load DLLs directly from memory without touching disk, with exception handling support, enabling stealthy code execution and evasion of…

Rust-based DLL hijacking loader for MobaXterm (CVE-2026-6421) with persistence

CVE-2026-50343 InstallService StaticPluginMap EoP - standard user to SYSTEM

Windows Local Privilege Escalation via CdpSvc service (Writeable SYSTEM path Dll Hijacking)

Staged DLL injection proof-of-concept built in C using Win32 APIs — developed in an isolated lab environment for red team certification study (CRTO).

Stealthy DLL proxying implant for Microsoft Teams that injects AES-encrypted shellcode via unhooking techniques, providing persistent backdoor access…

Local PE injection technique using hardware breakpoints and vectored exception handling to manipulate DLL loading and execute arbitrary payloads, as…

Windows 10 DLL Injector via Driver utilizing VAD and hiding the loaded driver

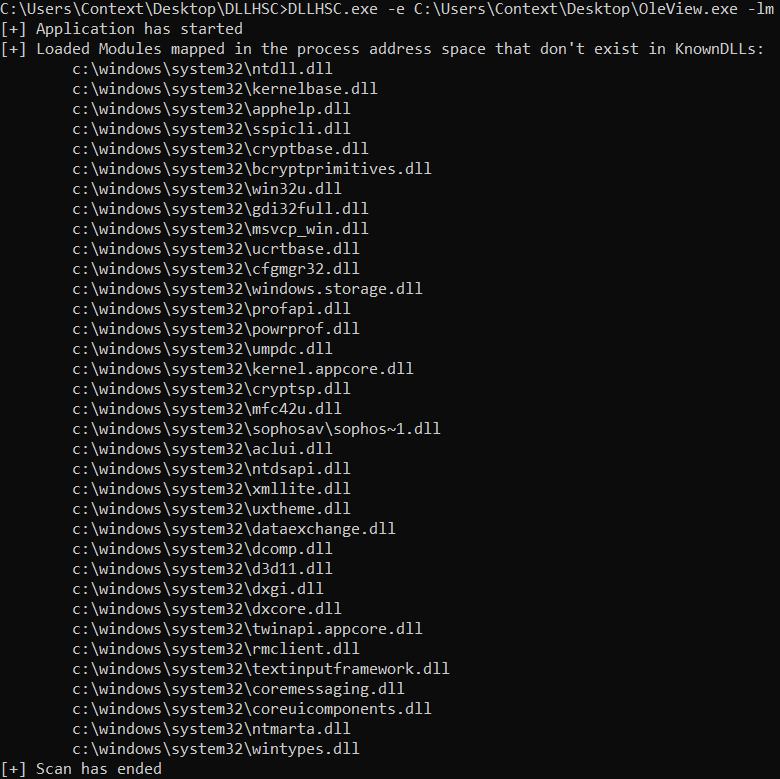
Automated scanner for discovering DLL search order hijacking candidates in Windows executables, featuring import table parsing, runtime module…

A collection of tools which integrate with Cobalt Strike (and possibly other C2 frameworks) through BOF and reflective DLL loading techniques.

Reflective DLL injection is a library injection technique in which the concept of reflective programming is employed to perform the loading of a…

DLL Injection and CVE-2010-3124