javascript-obfuscator

Obfuscates JavaScript and Node.js code with variable renaming, string encryption, control flow flattening, and anti-debugging to protect source code…

Obfuscates JavaScript and Node.js code with variable renaming, string encryption, control flow flattening, and anti-debugging to protect source code…

Havoc C2 plugin that creates a hidden Windows desktop, streams it to a browser viewer, and injects mouse/keyboard input for covert remote control.

Hosted Reverse Shell generator with a ton of functionality. -- (Great for CTFs)

Thefatrat a massive exploiting tool : Easy tool to generate backdoor and easy tool to post exploitation attack like browser attack and etc . This…

The Browser Exploitation Framework Project

Proof-of-concept exploit for CVE-2026-54088, a pre-authentication OS command injection in File Browser <=2.63.5. Demonstrates shell injection via…

A tool to transform Chromium browsers into a C2 Implant

JavaScript beacons and C2 to be used for XSS payload or post exploitation implants on webapp servers or desktop software to monitor users and…

PoC - Exploit Delivery via Steganography and Polyglots, CVE-2014-0282

A personal collection of Windows CVE I have turned in to exploit source, as well as a collection of payloads I've written to be used in conjunction…

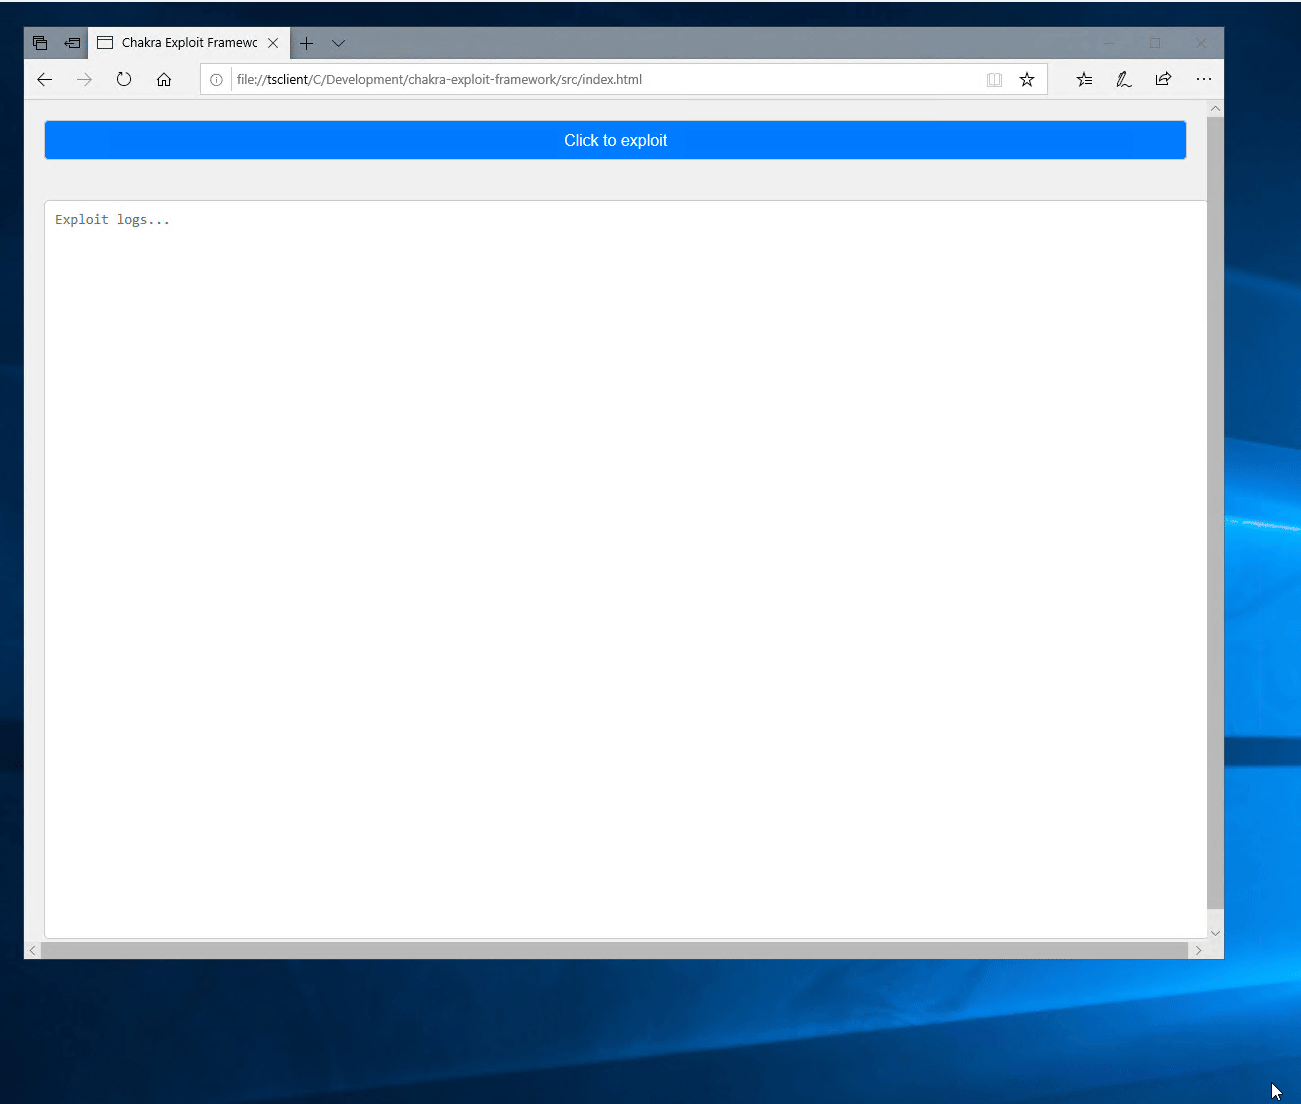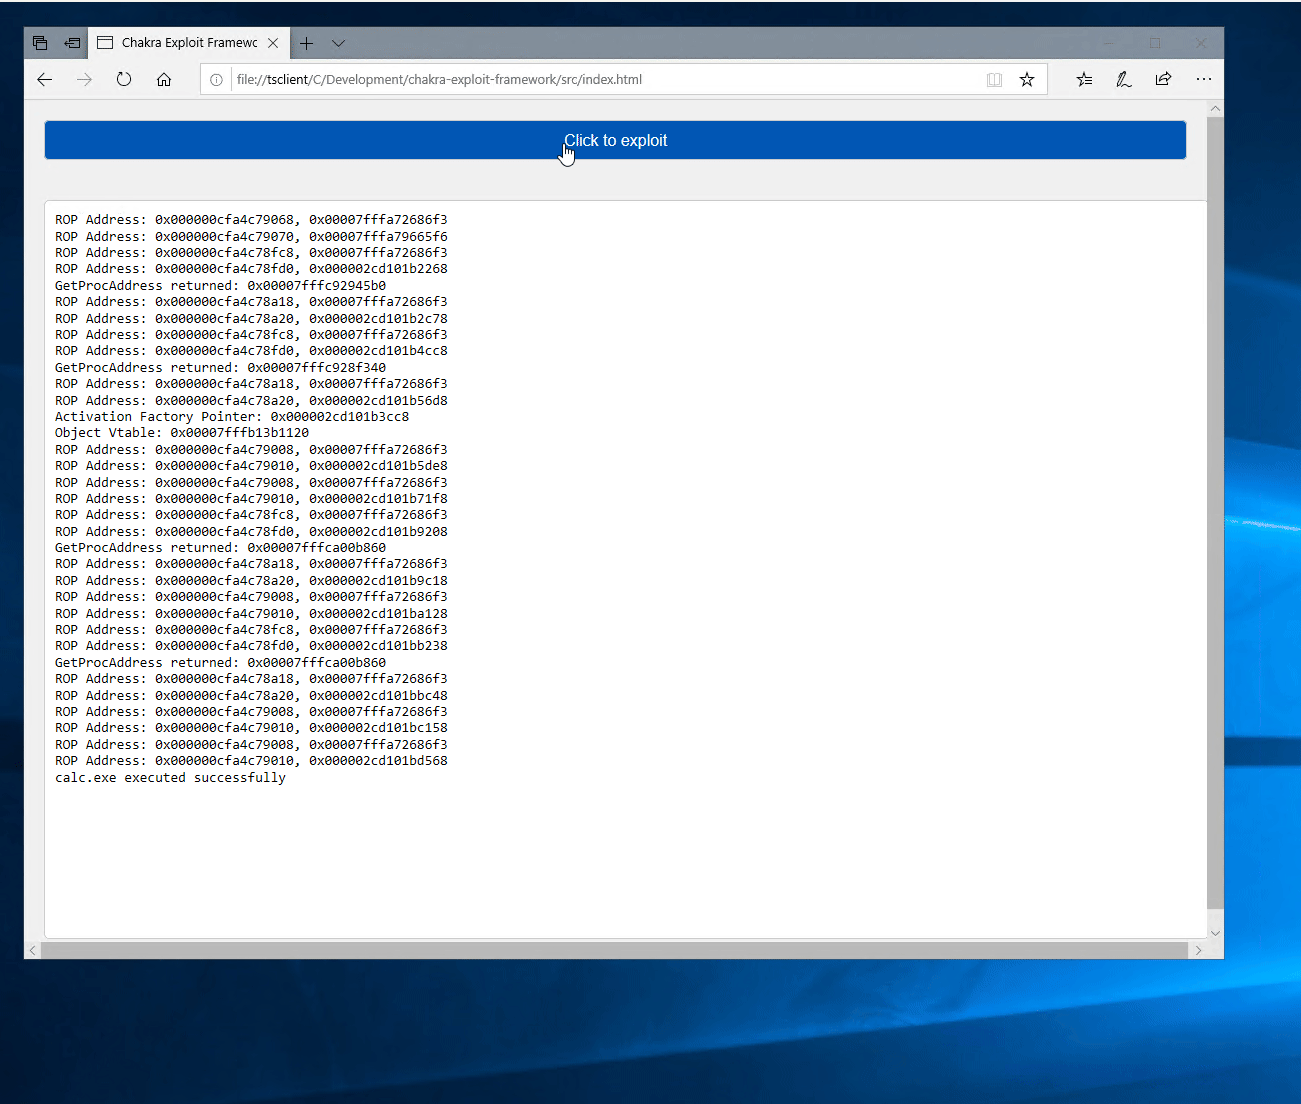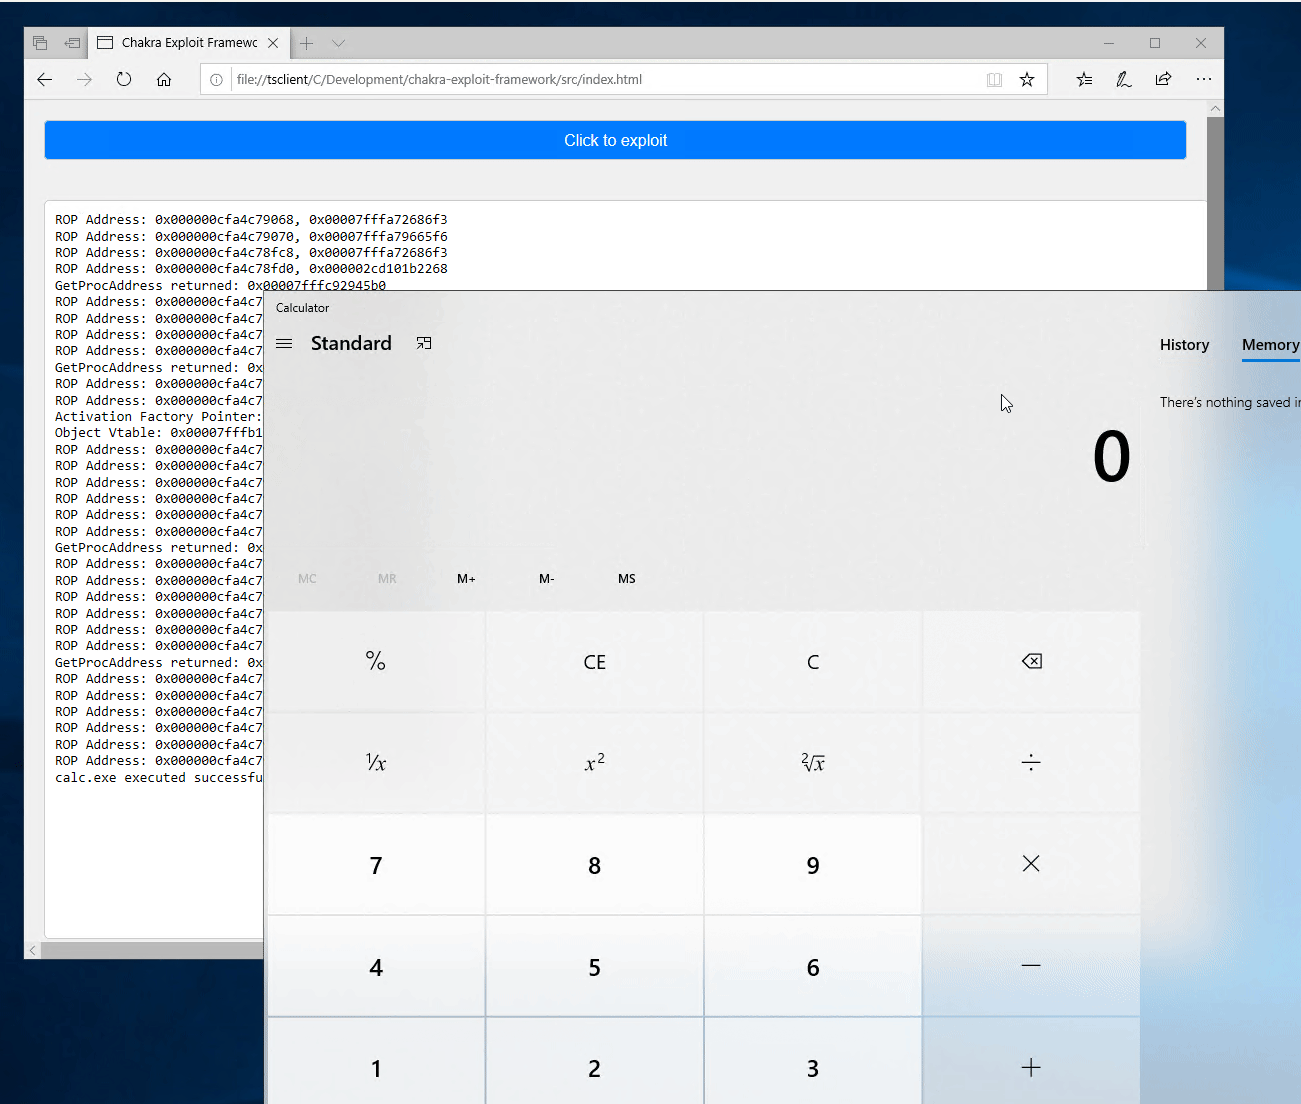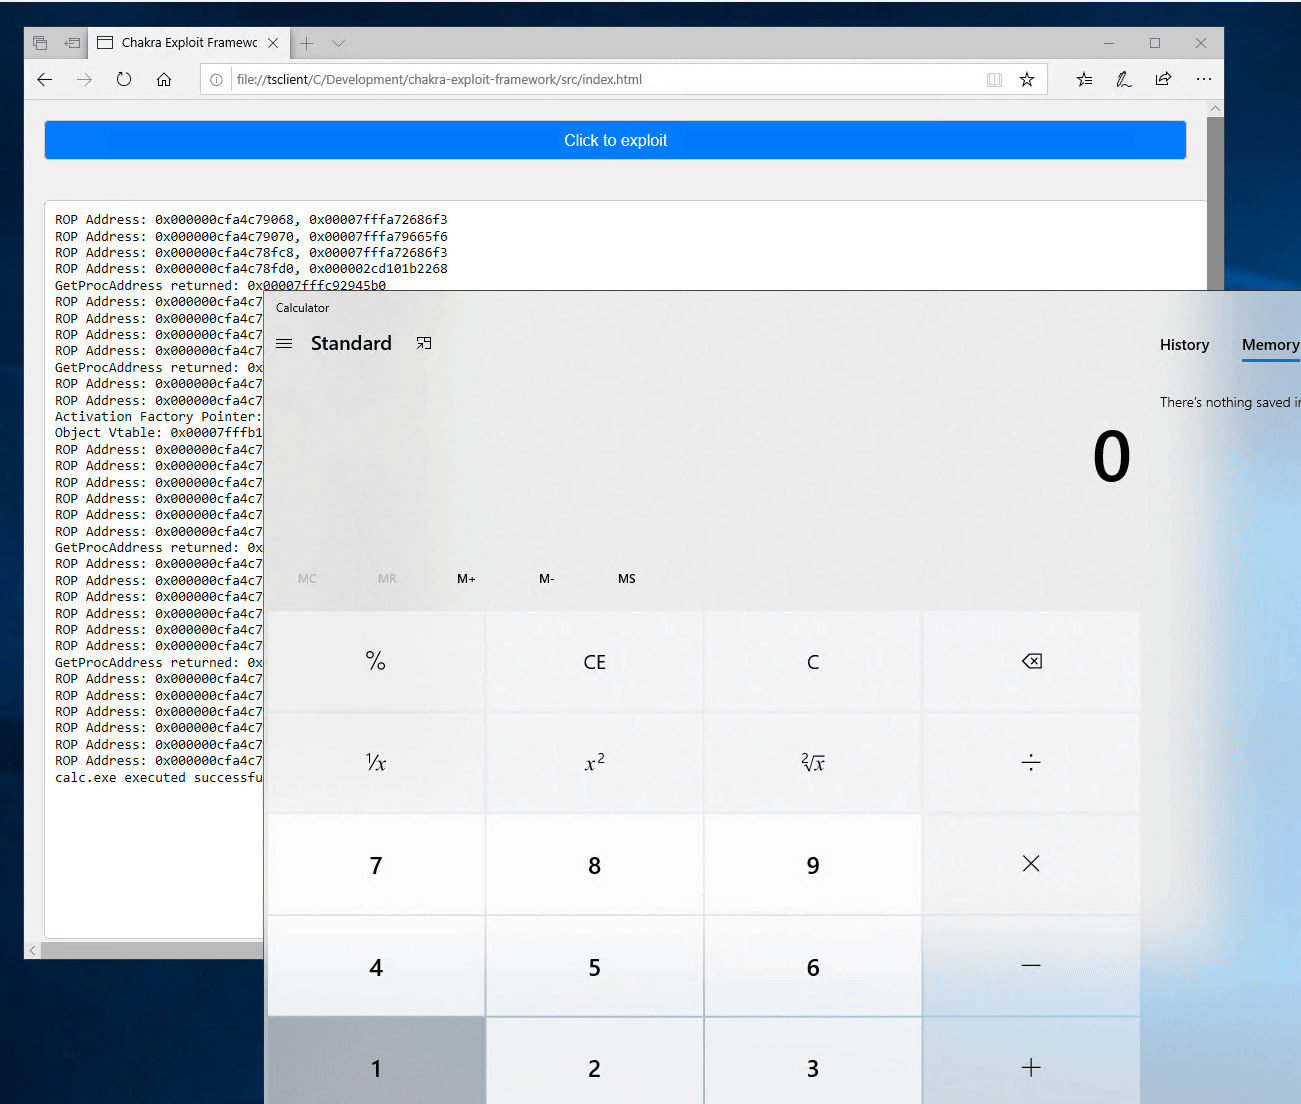
Browser exploitation framework for Chakra (Edge). Written as part of OSEE preparation. Demo bug: CVE-2019-0567

Browser-based CVE-2021-21220 exploit delivering a reverse shell via shellcode and a C2 implant for remote command execution on Windows targets.

My proof of concept for CVE-2019 Microsoft-Edge

Delivering PHP RCE (CVE-2024-4577) to the Local Network Servers

This Python script exploits a vulnerability (CVE-2024-21388) in Microsoft Edge, allowing silent installation of browser extensions with elevated…

This tool is a Proof of Concept (PoC) intended for security research and educational purposes only. Using this tool on systems without explicit…

Proof-of-concept exploit for CVE-2023-41993, a WebKit vulnerability in iOS 17.0 and macOS 14.0, demonstrating addrof/fakeobj primitives for browser…

Proof-of-concept exploit for CVE-2025-14174, a use-after-free in Chrome's V8 engine. Includes JavaScript PoC and HTML embed for identifying the…